HashiCorp Consul
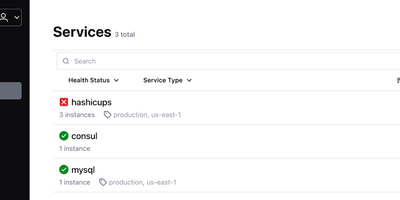
With nearly 30,000 GitHub stars and deployment across organizations including Criteo, Pandora, and Barclays, HashiCorp Consul is the industry-standard platform for service discovery, service mesh, and distributed configuration across dynamic multi-cloud and multi-datacenter infrastructure. Services register themselves and become discoverable via a built-in DNS interface on port 8600 or an HTTP API on port 8500, with health checks ensuring only healthy instances receive traffic through automatic catalog deregistration and service-level circuit breaking. The service mesh capabilities use Envoy sidecar proxies with Transparent Proxy mode to establish automatic mTLS encryption for all service-to-service communication, while identity-based intentions define fine-grained authorization rules controlling which services can communicate. The integrated API Gateway manages north-south traffic into the mesh with configurable routing rules, TLS termination, and header-based matching policies. Consul's distributed key-value store provides hierarchical configuration storage accessible via CLI, HTTP API, and the built-in web UI, with blocking queries enabling watch-based configuration updates without polling. Multi-datacenter federation connects Consul clusters across regions through WAN gossip and RPC forwarding, enabling cross-datacenter service discovery and failover with configurable prepared queries. The Raft consensus protocol provides strong consistency for the service catalog and KV store, with anti-entropy mechanisms ensuring agent state converges with the server catalog. Consul integrates natively with Kubernetes via Helm charts with automatic sidecar injection, Nomad for workload orchestration, Vault for secrets management, and Terraform for infrastructure provisioning. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. BUSL 1.1 licensed.
Nacos
Every microservice has to find the others and learn its own settings, and Nacos is the discovery and configuration platform that answers both needs from a single server. Producers register instances with names, addresses, weights, and metadata, and consumers look services up or subscribe to changes, so a fresh instance receives traffic without hand-edited load balancer rules. Health checks drop dead instances from discovery results, while weight controls in the console shift traffic gradually during a rollout or drain a node before maintenance. Configuration lives apart from code: publish properties and YAML under a Data ID and Group, split environments with namespaces, and subscribed clients apply changes within seconds. History keeps every published version, so a typo is recoverable: rollback republishes an earlier value, and listener queries show which clients picked the change up. Gray releases push a new value to a chosen slice of instances first, so a risky flag reaches a fraction of the fleet before the rest. The registry covers AI building blocks too: MCP servers register their tools, prompts and skills carry versions and visibility, and agents publish discovery cards that gateways look up like any service. Spring Cloud, Dubbo, and Kubernetes workloads plug in through SDKs for Java, Go, Python, and other languages; run one standalone node for development or a Raft-backed cluster for production. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
SaltStack
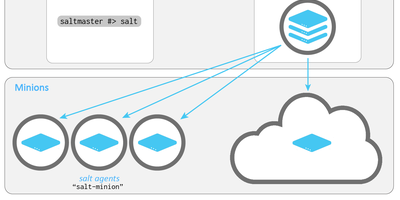
Type one command on the Salt master and ten thousand machines answer, because Salt publishes jobs to minions that subscribe, check whether the job targets them, and execute it in parallel before reporting results back. Configuration management describes the desired end state in YAML state files: which packages, files, services, and users should exist, and highstate runs converge every targeted minion toward that description with dependency ordering. Targeting goes far beyond hostnames, since grains describe each minion's operating system, hardware, and roles, and Pillar delivers per-minion secrets and settings rendered only for the machines that should receive them. Beacons watch services, load, disks, logins, and file changes on minions and emit events onto the bus, while reactors bind those events to prepared responses, so a failed service can restart itself and an administrator gets notified with the evidence attached. Orchestration runners coordinate multi-machine procedures in sequence, such as draining a load balancer pool, patching it, and returning it to service, and the master exposes HTTP APIs and pluggable returners that stream job results into your databases and dashboards. Machines that cannot run an agent are reached through Salt SSH, and Salt Resources target appliances and API endpoints that should be managed without a minion at all. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Dopbase
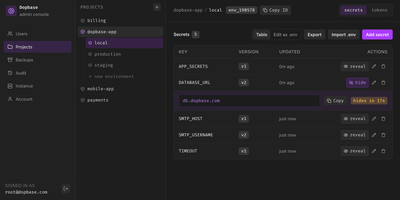
Dopbase keeps your application secrets out of scattered .env files and stores them, encrypted one by one, in a single self-hosted server you run as one file. You organize everything by project and environment, so the payment service has its own development, staging, and production values, and the same key can hold a different encrypted value in each place. Every secret is an individual record that can be updated, revealed, versioned, or rolled back without touching the others, and reading metadata never exposes a value. When an application starts, one command asks the server for an environment and injects exactly those values into the process, removing its own token before the child process runs. People sign in to the Admin UI with roles for root, admins, members, and even AI agents that can read metadata but change nothing. CI jobs and servers use runner tokens scoped to a single environment, so a staging credential can never read production. You can import and export .env files, edit secrets as a table or as raw env text, connect single sign-on through providers like Keycloak, and read an audit history of checks, reveals, and changes. Full-instance backups and the master key stay under your control on your own disk. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Semaphore
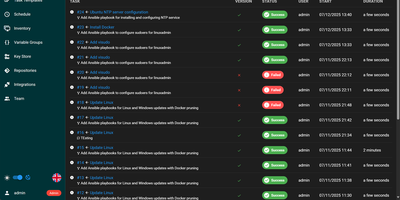
With nearly 14,000 GitHub stars and over 200 releases, Semaphore UI has established itself as the lightweight yet powerful alternative to enterprise automation platforms like Ansible AWX and Jenkins. Unlike AWX's heavyweight Kubernetes-dependent architecture, Semaphore ships as a single Go binary with zero external runtime dependencies — install it, run setup, and you have a production-ready automation server in minutes. The platform natively orchestrates Ansible playbooks, Terraform and OpenTofu infrastructure code, Terragrunt configurations, PowerShell scripts, Bash commands, and Python automation, all from a clean Vue.js web interface that displays task history, execution logs, and scheduling status at a glance. Semaphore supports concurrent task execution across multiple servers using distributed project runners, enabling horizontal scaling of automation workloads without complex clustering. The built-in inventory management system handles both static and dynamic inventory sources, while four-level RBAC (Owner, Manager, Task Runner, Guest) provides granular access control for team environments. Notifications flow to Slack, Microsoft Teams, Telegram, email, Rocket.Chat, and Gotify, keeping operators informed of failed tasks and deployment status. Integration with HashiCorp Vault secures sensitive credentials, and the comprehensive REST API with built-in Swagger documentation enables programmatic automation. Deploy via Docker Compose, Helm chart for Kubernetes, or native packages for Debian, Ubuntu, and RHEL-based distributions. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
DCM
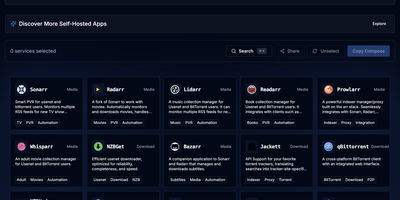
DCM is a visual builder that eliminates docker-compose copy-paste anxiety for home server enthusiasts. The TypeScript and Next.js web interface on port 7576 presents a curated catalog of popular self-hosted applications organized into categories: media management with Jellyfin, Plex, Sonarr, Radarr, and Prowlarr; dashboards like Homarr and Heimdall; databases including PostgreSQL, MariaDB, MongoDB, and Redis; monitoring stacks with Grafana and Prometheus; download clients like qBittorrent and NZBGet; security tools including Vaultwarden; storage solutions like Nextcloud; and home automation via Home Assistant. Select any combination of containers and DCM generates both compose.yaml and .env files with correct volume mounts, environment variables, PUID/PGID ownership, network modes, and port mappings — ready to paste into your terminal. Automatic port conflict detection identifies clashing services and reassigns ports before you ever hit a deployment error. The Template Gallery ships predefined multi-container stacks for common setups: media servers, development environments, database clusters, and monitoring solutions — some incorporating ten or more services in a single template. Built as a static Next.js export served from a 62 MB multi-arch Docker image supporting amd64, arm64, and arm/v7, DCM runs on everything from rack servers to Raspberry Pis. Share generated configurations via URL or download them locally. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
AWX
AWX transforms Ansible from a command-line tool into a centralized automation hub with a web UI, REST API, and distributed task engine for managing playbooks, inventories, and credentials at enterprise scale. The React-based dashboard provides real-time visibility into job status, inventory health, and execution history while Django REST Framework powers programmatic control over every automation resource. Job templates combine Ansible playbooks, inventories, and credentials into reusable units that chain together in workflow templates using directed acyclic graph orchestration with conditional branching on success, failure, or always-run logic and configurable convergence gates. The RBAC system built on django-ansible-base provides granular permission control over organizations, teams, projects, inventories, and credentials at object-level granularity. Dynamic inventory sources pull host data from AWS EC2, Google Cloud, Microsoft Azure, VMware vCenter, and Red Hat Satellite, while credential management securely stores SSH keys, cloud tokens, and vault passwords with HashiCorp Vault and CyberArk integration for external secret retrieval. Notifications deliver alerts via Slack, email, PagerDuty, Mattermost, IRC, and webhooks, while activity streams log every action for compliance auditing. The Receptor mesh network distributes job execution across isolated container-based execution environments with capacity-aware scheduling and hop-node routing for network-segmented infrastructures. Upstream of Red Hat Ansible Automation Platform. Deploys via Docker Compose with PostgreSQL and Redis or via the AWX Operator on Kubernetes. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
etcd
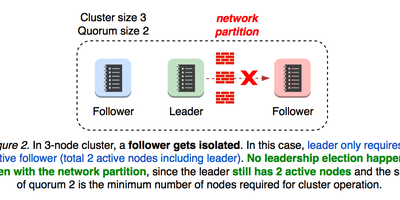
With over 52,000 GitHub stars and its role as the foundation of every Kubernetes cluster worldwide, etcd is the distributed key-value store that handles the most critical data in modern infrastructure — cluster state, configuration, service discovery, and distributed coordination. Built in Go and graduated from the CNCF, etcd uses the Raft consensus algorithm to maintain a strongly-consistent, highly-available replicated log across a cluster of machines, gracefully handling leader elections during network partitions and tolerating machine failure including the leader node. The gRPC API provides atomic key-value operations including put, get, delete, and transactions with multi-key compare-and-swap semantics, enabling distributed locking, leader election, and configuration management without external coordination. Watch operations stream real-time change notifications for specific keys or key ranges, powering reactive architectures that respond immediately to configuration updates. Version 3.7 introduces RangeStream for streaming large result sets in chunks, keys-only range requests for faster metadata queries, and bootstraps entirely from v3store after eliminating the legacy v2 store dependency. Automatic TLS encryption with optional client certificate authentication secures all cluster communication, while role-based access control restricts key access per user. The embedded bbolt B+ tree storage engine provides consistent reads and writes with configurable compaction policies. Benchmarked at 10,000 writes per second per instance with linearizable reads, etcd supports clusters of 3, 5, or 7 members for fault tolerance. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Uyuni
Four hundred servers need a security patch, they run five different Linux distributions, and a spreadsheet says which ones were done. Uyuni replaces that spreadsheet: one server inventories your fleet, mirrors the software channels each machine subscribes to, and shows exactly which patches and errata apply where. Administrators register clients manually, by bootstrap script, or automatically through activation keys, then group them into systems sets so an action aimed at a group lands on staging first and production on schedule. Patch management creates and applies errata with CVE context, and CVE audits check systems against vulnerability data so you can prove a fix landed instead of believing it did. Configuration channels push files, directories, and symbolic links rendered with Jinja templates through the built-in Salt master, which also runs remote commands and orchestration across tens of thousands of clients. The Content Lifecycle Manager promotes package sets from development through testing to production channels, so every environment consumes tested content in order. Provisioning reinstalls or network-boots machines through PXE with AutoYaST, Kickstart, or cloud-init profiles, proxies cache content for branch offices, and built-in Prometheus and Grafana monitoring watches the management server itself. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL-2.0 licensed.
Foreman
Foreman is the control room for a server fleet, taking machines from blank hardware or an empty VM to configured, monitored hosts through one web interface. Create a host entry and it network-boots by PXE or UEFI HTTP, or starts from a discovery image that phones home its hardware inventory so unknown machines can be claimed and built by rule. Installation runs from templates for Kickstart, Preseed, AutoYaST, Agama, and cloud-init, while host groups bundle the operating system, partition layout, and parameters that make every build of a role identical. The same console provisions onto bare metal, libvirt, VMware, oVirt, Amazon EC2, Google Compute Engine, and OpenStack, because each provider plugs in as a compute resource with its own images and networks. After installation, Puppet classes and parameters, Ansible roles with recurring runs, or Salt states keep configuration enforced, and the reports and facts those tools send back fill dashboards showing which hosts are current, which drifted, and which are erroring. Smart Proxy services carry DHCP, DNS, TFTP, and configuration enforcement into each subnet or datacenter segment, remote execution runs jobs across the fleet, and the Katello plugin adds content and patch management on top. Hammer gives the whole API a command-line face, and role-based access with LDAP or FreeIPA sign-in keeps large teams in their lanes. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL-3.0 licensed.