Coolify VPS
The open-source PaaS with 55,000+ GitHub stars and the largest one-click service catalog in its class — Coolify gives you the Vercel push-to-deploy workflow on a dedicated server you control. Connect a GitHub, GitLab, Bitbucket, or Gitea repository and every push builds and deploys automatically via Nixpacks, a Dockerfile, or Docker Compose, with Traefik or Caddy reverse proxying, automatic Let's Encrypt certificates, and per-branch preview deployments with their own URLs. Databases — PostgreSQL, MySQL, MariaDB, MongoDB, Redis — provision in a few clicks, and a catalog of 280+ one-click service templates covers WordPress, n8n, Grafana, MinIO, Plausible, Ollama, and more. One dashboard manages the entire server, with Docker Swarm available for clustering multiple nodes. Backups go to any S3-compatible storage with one-click restore, and a full API supports CI/CD integration. All configuration lives on your own server, so resources keep running even if you stop using Coolify — no vendor lock-in by design. Running on a dedicated VPS with guaranteed CPU, RAM, and SSD, full root access via SSH and browser console. Apache 2.0 licensed.
Dokploy VPS
Your own Heroku or Vercel on a dedicated server — Dokploy is the open-source PaaS that replaces cloud platform subscriptions with a single dashboard you control. Point it at a Git repository or a Docker image, and it builds and deploys the application using Dockerfiles, Nixpacks, or Heroku/Paketo buildpacks. Traefik handles reverse proxying, routing, load balancing, automatic Let's Encrypt SSL, and HTTP/3. Databases — MySQL, PostgreSQL, MongoDB, MariaDB, libsql, and Redis — provision from the UI with automated backups to any S3-compatible destination. Complex multi-service applications deploy through native Docker Compose support, and multi-node scaling uses Docker Swarm. The web dashboard covers environment variables, volumes, resource limits, real-time CPU/memory/network monitoring, and deployment logs, with a CLI and REST API for automation. Deploy notifications go to Slack, Discord, Telegram, or email. One-click templates install common open-source tools, and a single control plane can manage deployments across multiple remote servers. Because everything is standard Docker, there is no lock-in: Dockerfiles, Compose files, and data volumes work anywhere else Docker runs. The push-to-deploy workflow of a $20/seat cloud PaaS, running on a dedicated VPS with guaranteed CPU, RAM, SSD, and full root access — no per-app, per-environment, or per-seat fees regardless of how many applications you deploy. 26,000+ GitHub stars.
Supabase
With over 107,000 GitHub stars and adoption by teams at Mozilla, 1Password, Peerlist, and thousands of startups, Supabase has become the most widely deployed open-source Firebase alternative — built entirely on PostgreSQL rather than a proprietary NoSQL store. Every project provisions a dedicated Postgres database with 40+ preinstalled extensions, auto-generating REST APIs via PostgREST, GraphQL via pg_graphql, and real-time change streams via an Elixir-based WebSocket engine that supports database change listeners, user presence tracking, and arbitrary broadcast messaging. Authentication covers email and password, phone OTP, magic links, and 20+ social providers including Google, GitHub, Apple, Azure, and SAML SSO, all enforced through Postgres Row Level Security policies that run inside the database itself. S3-compatible object storage delivers files through a CDN spanning 285+ cities with on-the-fly image transformations powered by imgproxy. Edge Functions run globally distributed TypeScript on the Deno runtime with Node.js compatibility and access to over two million NPM packages. The pgvector extension stores, indexes, and queries vector embeddings for AI-powered semantic search and retrieval-augmented generation workflows. Supabase Studio provides a browser-based dashboard with a table editor, SQL editor, schema visualizer, and log explorer. Official client SDKs ship for JavaScript, Python, Flutter, Swift, Kotlin, C#, Go, and Ruby. The self-hosted Docker Compose stack runs fourteen coordinated services including Kong API gateway, Supavisor connection pooler, and Logflare analytics. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
AKB
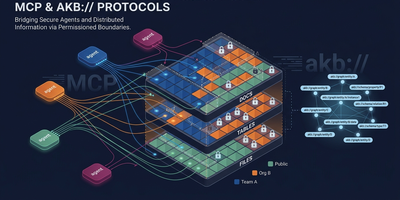
Achieving 98.4% Recall@5 on LongMemEval-S without a reranker, AKB is the agent-native knowledge infrastructure giving Claude Code, Cursor, Windsurf, and any MCP-aware agent persistent organizational memory — a drop-in replacement for Confluence or Notion where AI agents read and write directly rather than scraping human-formatted pages. Documents are stored as Markdown with YAML frontmatter in Git bare repositories (full version history, branching, diff), while PostgreSQL 16 serves as source of truth for chunk text, metadata, and BM25 vocabulary, with dense embeddings handled by a pluggable vector store (pgvector default, Qdrant optional, or managed Seahorse). Agents interact through 20+ MCP tools — akb_put, akb_search, akb_browse, akb_relations, akb_sql, akb_edit, akb_history — performing hybrid dense plus BM25 search fused via Reciprocal Rank Fusion in one call. The URI graph (depends_on, related_to, implements relations) lets agents traverse knowledge connections without external graph databases. Multi-tenant vault isolation is enforced at the PostgreSQL ACL level with per-user roles and SET LOCAL ROLE for SQL sandboxing. Event fanout streams structured events to Redis Streams for external consumers (synthesis bots, digest agents, audit trails), and a hash-chained append-only audit log integrates with enterprise SIEMs. Ships with agent plugins for Claude Code and Codex (session capture, wiki ingest, lifecycle hooks), Kubernetes kustomize manifests, and Open Knowledge Format export. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. BSL 1.1 licensed (free under 100 seats, auto-converts to Apache 2.0 after four years).
Mail-in-a-Box
Mail-in-a-Box turns a single Ubuntu server into a fully functional email system with one setup command, installing and configuring Postfix for SMTP, Dovecot for IMAP, Roundcube for webmail, and Z-Push for Exchange ActiveSync push notifications in an automated sequence that would take days to replicate manually. The DNS server auto-configures the full suite of email authentication records: SPF, DKIM, DMARC, DNSSEC with DANE TLSA, MTA-STS, and SSHFP. Getting all of these right is what separates email that lands in inboxes from email that lands in spam, and most manual installations never achieve the complete set. Nextcloud integration adds CardDAV contact sync and CalDAV calendar sharing across devices. Let's Encrypt certificates provision and renew automatically for every hosted domain. The web control panel manages users, aliases, custom DNS records, and automated backups, protected by TOTP two-factor authentication. Daily health checks verify that services run correctly, ports remain open, TLS certificates stay valid, and DNS records resolve properly, alerting you before delivery problems develop. Multiple domains and users operate from one installation with internationalized domain name support. Built-in HTTPS static site hosting uses the TLS infrastructure already in place. Runs on a dedicated RepoCloud VPS with guaranteed resources, root SSH, and browser serial console for complete email sovereignty. CC0 public domain licensed.
Knowhere
With 2,600+ GitHub stars since its May 2026 open-source launch, Knowhere solves the last-mile problem of document intelligence for AI systems — transforming complex unstructured PDFs, reports, and multi-page documents into structured JSON chunks that LLMs can consume without hallucination. The platform processes documents through an AI-native parsing pipeline that handles 20+ page documents with deep hierarchies, intricate tables, and multimodal content including images with OCR, achieving 95% precision in information extraction while reducing token costs by 50% compared to raw document ingestion. The knowledge tree architecture maintains historical context across multiple documents, enabling cross-document graph navigation for agentic retrieval that goes beyond simple chunk-based RAG. Built on Python 3.11+ with MinerU as the default PDF parser, the backend API runs alongside async workers that process document ingestion, graph construction, and embedding generation. The self-hosted Docker Compose stack packages the API server, processing workers, and Next.js dashboard for managing API keys, webhooks, and document-processing jobs, backed by PostgreSQL and Redis. Both Python and Node.js SDKs provide programmatic access for integration into existing AI pipelines and agent frameworks. LLM providers include DeepSeek and Alibaba Cloud DashScope with configurable key rotation for rate-limit management. Deploy on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
InsForge
With 12,600 GitHub stars and 52 releases in under a year of development, InsForge is the fastest-growing open-source backend platform purpose-built for AI coding agents — giving Claude, Cursor, and any MCP-compatible tool direct access to database, authentication, storage, compute, and AI model infrastructure through a single self-hosted stack. The native MCP server exposes every InsForge operation as callable tools, letting coding agents autonomously create database tables, manage user authentication, upload files, deploy edge functions, and ship complete full-stack applications without human intervention. The Model Gateway provides an OpenAI-compatible API that routes requests across multiple LLM providers (OpenAI, Anthropic, Google, and open-source models) with unified billing, rate limiting, and fallback logic. PostgreSQL with pgvector handles both relational data and vector embeddings for RAG pipelines, while S3-compatible storage manages file uploads and static assets. Edge Functions run serverless TypeScript code on Deno with sub-millisecond cold starts for API endpoints, webhooks, and scheduled tasks. The authentication system provides user management, OAuth2 flows, sessions, and magic links with JWT token handling built in. Site Deployment builds and serves frontend applications with automatic SSL and custom domain configuration. The CLI paired with Agent Skills enables terminal-based workflows where agents invoke InsForge operations directly from the command line. Deploy via Docker with PostgreSQL as the only required external dependency. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Backstage
Adopted by over 3,400 companies and backed by 34,000 GitHub stars, Backstage is the open-source developer portal framework created by Spotify and now hosted by the Cloud Native Computing Foundation. The centralized Software Catalog registers every service, library, data pipeline, website, and ML model in your organization using YAML metadata files stored alongside code in GitHub, GitHub Enterprise, or GitLab, tracking ownership, lifecycle status, and dependency relationships across your entire ecosystem. Software Templates provide self-service infrastructure provisioning where developers fill out a form and Backstage automatically scaffolds new repositories, CI/CD pipelines, and cloud resources following your organization's standardized best practices. TechDocs renders Markdown documentation directly alongside the services it describes using a docs-like-code approach powered by MkDocs, with the TechDocs Addon Framework for extending the reading experience. The Search Platform indexes content across the catalog, TechDocs, Confluence, and Stack Overflow through configurable search backends. Kubernetes monitoring built specifically for service owners rather than cluster admins displays pod health, logs, and deployment status across any cloud provider or managed Kubernetes service. The plugin ecosystem includes over 230 open-source integrations covering CI/CD systems like GitHub Actions and GitLab Pipelines, monitoring platforms like Datadog and Grafana, cloud providers including AWS and Azure, plus specialized plugins for security scanning, cost management, API documentation, PagerDuty incident management, and Lighthouse website auditing. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Neon
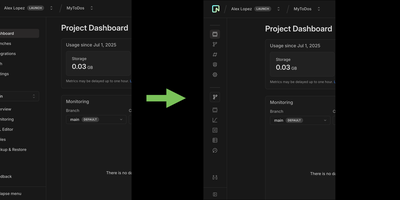
Neon reimagines PostgreSQL with a serverless architecture that decouples storage from compute, enabling instant copy-on-write database branching, autoscaling under load, and scale-to-zero when idle with sub-second cold starts. The lakebase architecture distributes durability across three layers: stateless compute nodes running unmodified PostgreSQL, safekeepers providing Paxos-based WAL quorum replication, and a pageserver that materializes pages on demand while offloading immutable history to S3-compatible object storage via MinIO or AWS S3. Copy-on-write branching creates full database clones as metadata operations without duplicating data, enabling developers to spin up isolated test environments, run parallel CI/CD pipelines, or recover from data loss through point-in-time restore across the configurable history window. Autoscaling dynamically adjusts CPU and memory based on live traffic without manual capacity planning, while scale-to-zero ensures costs drop to storage-only during idle periods. Neon maintains 100% PostgreSQL compatibility with broad extension support including PostGIS, pg_cron, pgvector, pg_stat_statements, and hundreds more, so existing applications connect with standard PostgreSQL drivers and ORMs unchanged. The API-first control plane enables programmatic provisioning, branch management, and multi-tenant fleet operations for platform builders and AI agent integrations. Acquired by Databricks in May 2025 and backed by over 22,800 GitHub stars. Deploys via Docker Compose with pageserver, safekeepers, storage broker, and compute nodes backed by MinIO object storage. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
UptimeKuma
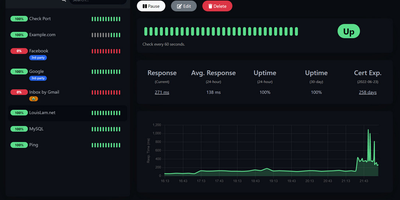
Sixty-thousand-plus GitHub stars make Uptime Kuma the most popular self-hosted monitoring tool - MIT-licensed, Node.js, and the standard replacement for UptimeRobot, Pingdom, and Freshping. It watches a dozen monitor types: HTTP(S) endpoints with keyword and JSON-query content validation, TCP ports, ICMP ping, DNS records, WebSockets, Docker containers via the socket, Steam game servers, MQTT brokers, gRPC services, and push-based heartbeats for cron jobs and internal workers. Checks run at intervals as tight as 20 seconds - versus UptimeRobot's 5-minute free tier - with unlimited monitors and unlimited data retention. When something fails, alerts fan out through 90+ notification channels: Slack, Discord, Telegram, email with LiquidJS templating, PagerDuty, OpsGenie, ntfy, Gotify, Matrix, and dozens more via native providers plus the Apprise library. Unlimited public or password-protected status pages - mappable to specific domains and organized into monitor groups - communicate health to customers, with maintenance windows that suppress alerts during planned work. The reactive dashboard graphs response times, tracks SSL certificate expiry with advance warnings, supports proxies and 2FA, and ships in dozens of languages. One Docker container with a SQLite volume covers an entire infrastructure.
xyOps
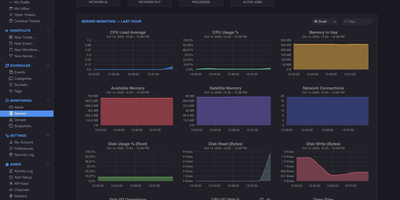
With 4,500+ GitHub stars and version 1.0.92 released August 2026, xyOps delivers a complete operations platform that unifies workflow automation, job scheduling, server monitoring, alerting, and incident response in one self-hosted system. The platform uses a distributed architecture where a central conductor coordinates lightweight xySat satellite agents running on Linux, macOS, or Windows worker nodes via persistent WebSocket connections. The visual workflow builder lets you chain events, triggers, actions, and monitors into multi-step pipelines with conditional logic, fan-out/fan-in parallelism, multiplex controllers for fleet-wide execution, and configurable resource limits. QuickMon provides per-second CPU, memory, disk, and network visibility streamed live to the web UI, while user-defined monitor plugins sample metrics every minute with time-series storage at hourly, daily, monthly, and yearly resolutions. Alert triggers evaluate expressions against live data and fire notifications via email, webhook, or custom actions, with full server snapshots attached showing every running process, network connection, and resource utilization at the moment of detection. Failed jobs and alerts automatically create tickets with linked logs, metrics history, and context for end-to-end incident tracking. The plugin marketplace supports extensions written in any language, and the Docker plugin enables container-based job execution. Deploy via Docker with persistent volumes on port 5522 for the web UI and 5523 for API access, running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. BSD-3-Clause licensed.
DragonflyDB
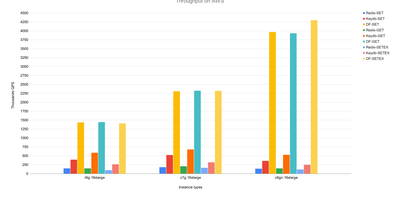
With over 30,000 GitHub stars and benchmarks showing 25x the throughput of single-threaded Redis, DragonflyDB is a modern in-memory data store that eliminates the need for complex Redis Cluster deployments by fully utilizing every CPU core on a single machine. Its shared-nothing, thread-per-core architecture written in C++ supports over 200 Redis commands and 13 Memcached commands, making it a true drop-in replacement that requires zero application code changes. A single DragonflyDB instance scales vertically from 8GB to 768GB of RAM across up to 64 cores, replacing entire Redis Cluster topologies with one process while maintaining full compatibility with Strings, Hashes, Lists, Sets, Sorted Sets, Streams, JSON, and Bloom Filters. The novel dashtable data structure and cache eviction algorithm achieve higher hit rates than LRU and LFU with zero memory overhead per entry. Forkless point-in-time snapshotting eliminates the memory spikes associated with Redis BGSAVE, while automatic backup scheduling via cron syntax supports both local disk and AWS S3 cloud storage. Primary-replica replication follows the Redis replication protocol up to version 6.2, and Prometheus-compatible metrics at the default port enable Grafana monitoring dashboards out of the box. DragonflyDB also exposes an HTTP admin interface on its main TCP port for operational monitoring. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. BSL 1.1 licensed.
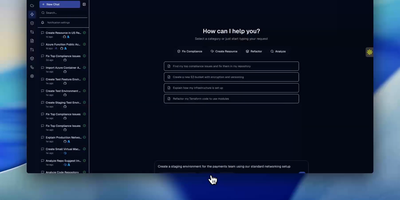
Opengeni
Enterprises requiring production-grade governance for long-running autonomous AI operations can rely on OpenGeni, a self-hosted orchestration platform with human-in-the-loop approvals, Connected Machine execution, and comprehensive audit replays. Operators can configure durable multi-turn workflows that execute continuously toward specified goals without premature termination, automatically pausing when human verification, structured multiple-choice decisions, or critical credential approvals are required. Teams can assign execution workloads across ephemeral cloud sandboxes or route them straight to enrolled Connected Machines to run commands directly against local code repositories without exposing inbound network ports. The integrated web console lets developers inspect live Server-Sent Event activity streams, replay complete turn histories from audit logs, inspect generated artifacts, and cancel or steer in-flight agent tasks on demand. Platform administrators can enforce fine-grained access policies through GitHub App repository bindings, broker temporary role-scoped secrets, and maintain a shared organizational knowledge base where agents propose findings for human review before vector indexing. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
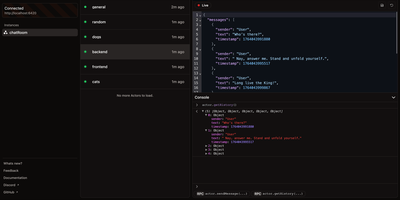
Rivet
Stateful serverless actors that run indefinitely, sleep when idle, and persist state across restarts without external database round trips. Rivet provides a vendor-neutral alternative to Cloudflare Durable Objects, delivering long-running processes with co-located in-memory state and per-actor SQLite databases on any infrastructure you choose. The Rust engine comprises four packages: Pegboard for actor orchestration, Gasoline for durable execution, Guard for traffic routing via Envoy, and Epoxy implementing multi-region KV storage through EPaxos consensus. Each actor maintains instant-access in-memory state plus a dedicated SQLite database for relational queries, backed by RocksDB on single nodes or PostgreSQL with NATS pub/sub for multi-node clusters. RivetKit SDKs in TypeScript, Rust, and Python support built-in WebSocket connections, task queues, scheduling, and CRDT-based real-time collaboration. The v2.3 rewrite moved the core runtime from JavaScript to native Rust via WebAssembly, eliminating main-thread blocking across Node.js, Bun, Deno, and Cloudflare Workers. A built-in dashboard provides actor inspection with real-time Prometheus metrics. Deploys as a single Docker container on port 6420 with optional PostgreSQL for persistence. Available on RepoCloud with a dedicated VPS under the Apache 2.0 license.
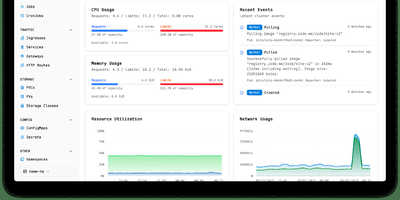
Kite
With nearly 3,000 GitHub stars and 14 releases since its June 2025 launch, Kite delivers a lightweight Kubernetes dashboard that replaces the fragmented workflow of switching between kubectl, Lens, and separate monitoring tools with a unified multi-cluster management platform. The dashboard automatically discovers clusters from kubeconfig files and supports independent Prometheus configurations per cluster, providing real-time CPU, memory, and network charts alongside live pod log streaming with filtering and search. A built-in web terminal opens shells directly into pods and nodes without kubectl port-forward, while the Monaco-based YAML editor offers syntax highlighting and validation for in-place resource editing. The integrated AI agent, powered by OpenAI or Anthropic models via native Go SDK integrations, translates natural language into precise client-go API calls — querying cluster health, analyzing pod logs, scaling deployments, patching resources, and cleaning up failed jobs — all operating strictly within the logged-in user's RBAC permissions. Enterprise governance includes OAuth 2.0 single sign-on, multi-factor authentication, FIDO2 passkeys, granular role-based access control with per-namespace permissions, and comprehensive audit logging. Helm chart management enables browsing, installing, and upgrading releases directly from the UI, while the Docker registry integration provides quick image tag selection. Deploy via a single Docker container with SQLite or use the official OCI Helm chart with PostgreSQL or MySQL for production. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
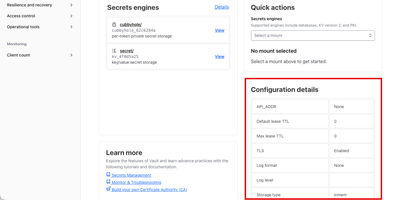
HashiCorp Vault
With over 36,000 GitHub stars and adoption by organizations including Adobe, Shopify, and Roblox, HashiCorp Vault is the industry-standard platform for secrets management, encryption services, and privileged access control across hybrid and multi-cloud infrastructure. The key/value secrets engine stores arbitrary secrets with full versioning, soft-delete, and metadata tracking, while dynamic secrets engines generate on-demand, short-lived credentials for AWS, Azure, GCP, databases including PostgreSQL, MySQL, MongoDB, and MSSQL, and SSH access with automatic revocation after configurable lease periods. The PKI secrets engine dynamically issues X.509 certificates on demand with automatic rotation and ACME protocol support, eliminating manual certificate management workflows entirely. Encryption as a service through the transit secrets engine lets applications encrypt, decrypt, sign, verify, and generate HMACs without managing cryptographic keys directly, supporting AES-GCM-256, ChaCha20-Poly1305, RSA-2048/4096, ECDSA-P256/P384, and ED25519 algorithms. Authentication integrates with LDAP, OIDC/OAuth2, SAML, AppRole for machine-to-machine access, Kubernetes service accounts, AWS IAM, Azure Active Directory, and GitHub tokens. Fine-grained ACL policies use path-based rules with glob patterns and sentinel policies for programmatic enforcement. The integrated Raft storage backend provides high-availability clustering without external dependencies, while alternative backends include Consul, S3, DynamoDB, PostgreSQL, and MySQL. The built-in web UI provides a visual interface for browsing secrets, managing policies, configuring auth methods, and monitoring cluster health. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. BSL 1.1 licensed.
Netdata
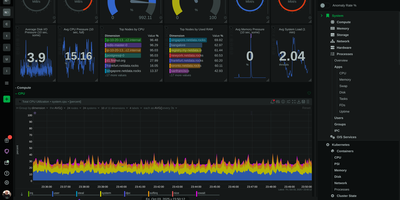
Trusted by millions of engineers and deployed on over 80,000 GitHub stars worth of community confidence, Netdata delivers true real-time monitoring at per-second granularity — 10-60x faster than Prometheus, Datadog, or any conventional monitoring stack that averages away the transient anomalies lasting 2-10 seconds where most production incidents originate. A single installation command deploys the agent with zero configuration, automatically discovering every running process, container, systemd service, network connection, disk, and application on the host within seconds. Unsupervised machine learning trains multiple models per metric directly at the edge, detecting anomalies without thresholds, baselines, or manual tuning. The distributed Parent-Child architecture scales horizontally from a single Raspberry Pi to fleets exceeding 100,000 nodes while maintaining sub-2-second visualization latency and storing metrics at approximately 0.5 bytes per sample through tiered compression. Native network monitoring provides live topology maps, NetFlow and sFlow analytics, SNMP device polling across 200+ profiles, and trap handling — capabilities that typically require a separate NPM product. Hundreds of pre-configured alerts cover systems and applications out of the box, with AI-powered root cause analysis surfacing correlated metrics through natural language via MCP-compatible AI assistants. The agent supports Linux, macOS, FreeBSD, Kubernetes, and Docker with eBPF-based kernel observability requiring no application instrumentation. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL v3+ licensed.
Pulse
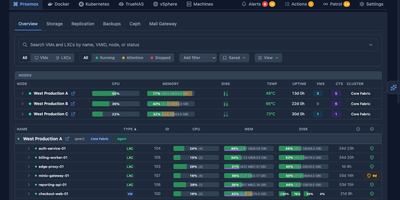
Pulse monitors your entire heterogeneous infrastructure from one screen: Proxmox VE, Proxmox Backup Server, Proxmox Mail Gateway, Docker, Podman, Docker Swarm, Kubernetes, TrueNAS SCALE/CORE, VMware vSphere, and standalone Linux/Windows/macOS machines. The Go binary embeds a SolidJS/TypeScript frontend, delivering WebSocket-driven dashboards with sub-second metric updates on port 7655. A unified agent auto-detects Docker, Podman, Kubernetes, and Proxmox on each host without manual configuration and self-updates silently, while Proxmox nodes need only API credentials with zero agent installation. Smart alerts use adaptive hysteresis-based thresholds to prevent notification floods, pushing to Discord, Slack, Telegram, Teams, email, ntfy.sh, Gotify, and generic webhooks with per-resource overrides. The standout feature is Pulse Patrol: scheduled AI health checks running every ten minutes to seven days using OpenAI, Anthropic, Gemini, or local Ollama models. Patrol catches silent backup failures, capacity creep, restart loops, unhealthy containers, and clock drift that dashboards miss when nobody is watching. Platform-specific views render Proxmox nodes, Ceph clusters, Docker Compose projects, Kubernetes workloads, TrueNAS pools, and vSphere VMs in familiar layouts. OIDC, SSO, and SAML authentication with credential encryption at rest secures access. 6,500+ stars and 441 releases since February 2025. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.