Categories
Self-Hosted Developer Tools Configuration Management Secrets Management DevOps Tools Security Tools Environment VariablesStars
Forks
Watchers
Developer links
Dopbase
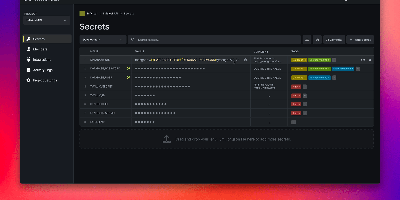
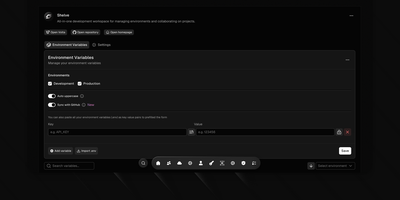
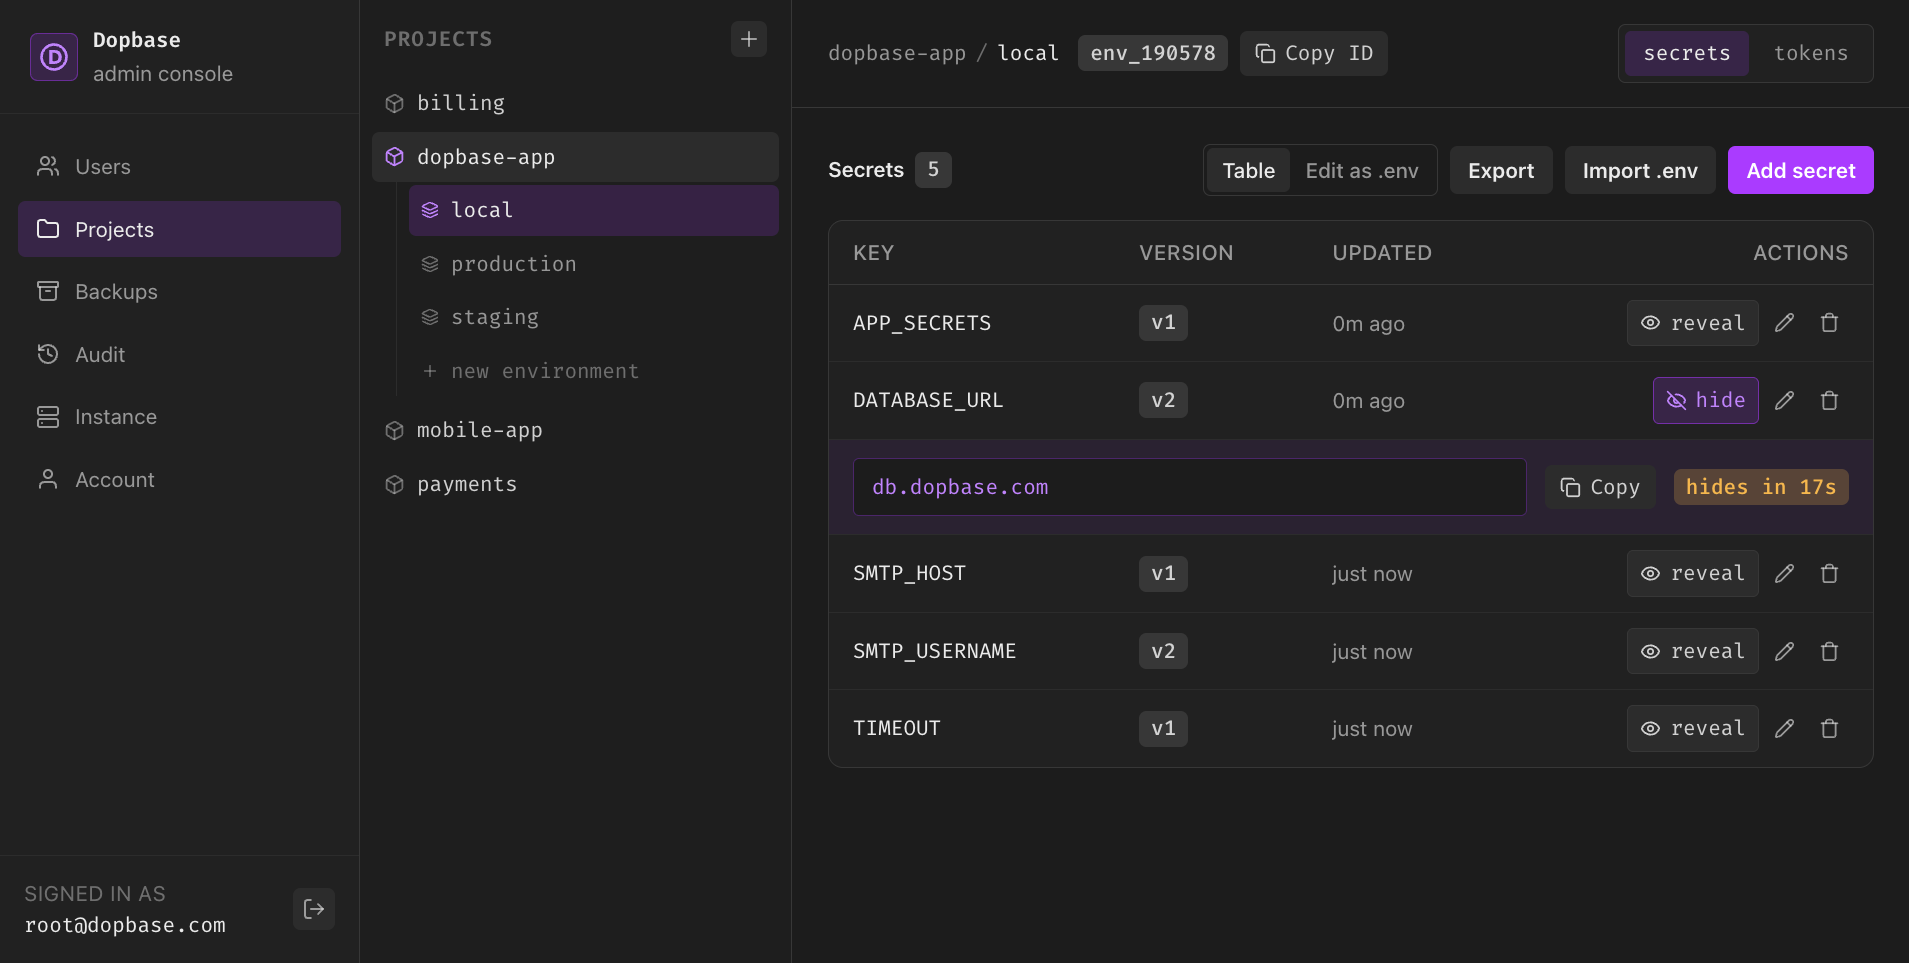
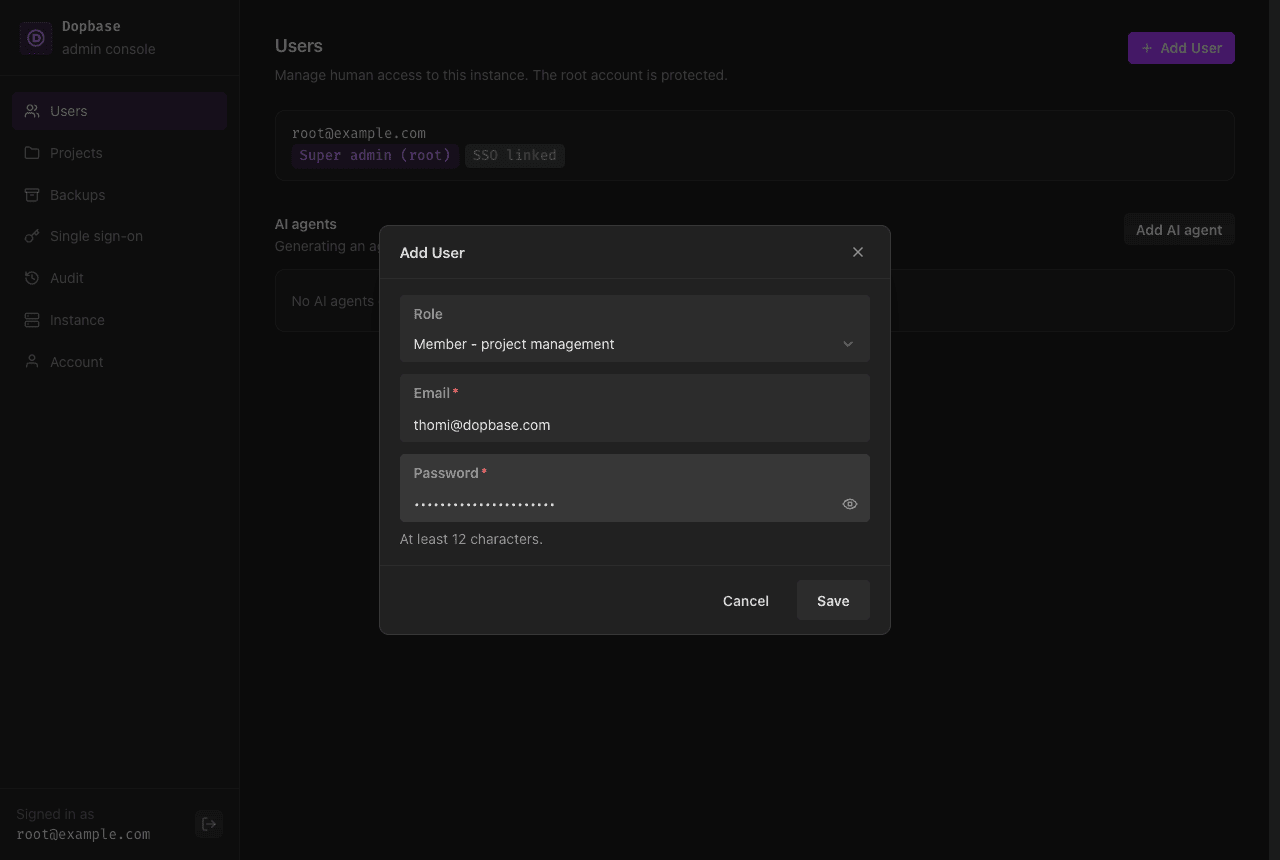
Dopbase keeps your application secrets out of scattered .env files and stores them, encrypted one by one, in a single self-hosted server you run as one file. You organize everything by project and environment, so the payment service has its own development, staging, and production values, and the same key can hold a different encrypted value in each place. Every secret is an individual record that can be updated, revealed, versioned, or rolled back without touching the others, and reading metadata never exposes a value. When an application starts, one command asks the server for an environment and injects exactly those values into the process, removing its own token before the child process runs. People sign in to the Admin UI with roles for root, admins, members, and even AI agents that can read metadata but change nothing. CI jobs and servers use runner tokens scoped to a single environment, so a staging credential can never read production. You can import and export .env files, edit secrets as a table or as raw env text, connect single sign-on through providers like Keycloak, and read an audit history of checks, reveals, and changes. Full-instance backups and the master key stay under your control on your own disk. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Benefits
- One File, Whole Vault
- The server, Admin UI, REST API, and SQLite storage ship in a single executable, so a complete secrets manager deploys by copying one file and starting it on your own host.
- Secrets Individually Encrypted
- Each secret is its own encrypted, versioned record rather than one opaque .env blob, so a single value can be updated, revealed under permission, audited, or rolled back alone.
- Scoped Runner Tokens
- CI jobs and servers authenticate with tokens scoped to exactly one environment, and the run command strips its own token before starting your process, shrinking what a leak can reach.
- Roles Including AI Agents
- Root, admin, and member roles cover people, while a dedicated AI agent role can read project and secret metadata without managing anything, matching how automated tooling actually works.
Features
- Projects And Environments
- Organize secrets by project and environment with immutable IDs, readable references like payment-service/staging, per-environment encrypted values, and .env import, export, and raw text editing.
- Process Injection With Run
- The run command fetches one environment from the server and starts your application with those values injected, preferring the same values locally that deployment uses in production.
- Admin UI And REST API
- Manage users, projects, backups, audit history, and instance settings in the embedded Admin UI, automate through the REST API, or enable the optional Swagger UI and OpenAPI document.
- Single Sign-On
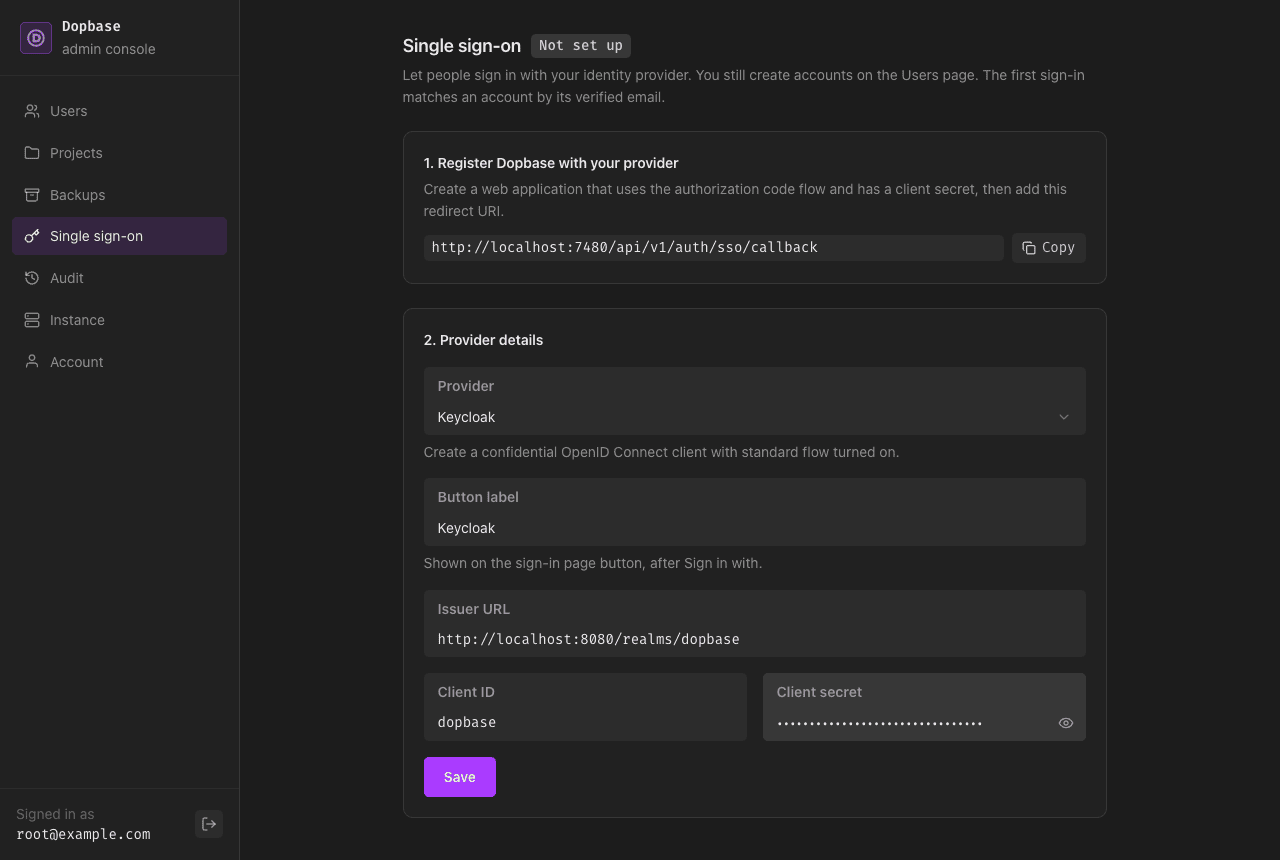
- Connect OpenID Connect providers such as Keycloak with a tested sign-in flow, matching accounts by verified email while local password accounts continue to work beside SSO.
- Audit And Version History
- Every check, merge, reveal, and change lands in a filtered audit history, secret versions are kept per record, and reveals are explicit, permission-controlled, and confirmed interactively in the CLI.