OpenBot
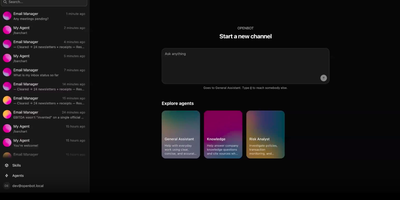
Open source GrokBot, built by the team behind the AG-UI protocol. OpenBot is the open-source enterprise agent platform that gives every AI coworker its own sandboxed computer — a real Chromium browser with its own login sessions, a private filesystem, and only the MCP tools you explicitly grant. The centralized gateway evaluates CEL policy rules against tool name, intent, bot identity, page URL, element attributes, and file paths before any action executes, writing an immutable audit row for every call and outcome. Any agent that speaks AG-UI — LangGraph, Mastra, CrewAI, Pydantic AI, Google ADK, or hand-written endpoints — registers as a Bot and receives its own channel with persistent conversation history. The take-the-wheel system lets humans assume control when an agent encounters login walls or two-factor prompts, recording control transfers as structured audit events. Knowledge documents from Google Drive and OneDrive carry source-based permissions where deny principals always win and ambiguous mappings refuse retrieval entirely. The React and Vite frontend provides live screen viewing of each agent's browser, channel-based chat, admin settings, and component galleries. The Hono API server on port 3001 handles authentication, role-based access, tenant packaging, and credential management backed by PostgreSQL with pgvector. Deploy via Docker Compose with the included supervisor that manages per-bot computer containers. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
NanoClaw
NanoClaw delivers a radically simple alternative to OpenClaw — a single Node.js process and a handful of files that provide the same core functionality with true container-level security isolation. Agents execute inside Docker containers on Linux or Apple Containers on macOS, where even root access inside the sandbox cannot reach the host filesystem. The platform natively runs Claude Code via Anthropic's official Claude Agent SDK, with drop-in alternatives including OpenAI Codex, OpenRouter via OpenCode, Google, DeepSeek, and local open-weight models via Ollama — configurable per agent group. Multi-channel messaging connects WhatsApp, Telegram, Discord, Slack, Microsoft Teams, iMessage, Matrix, Google Chat, Webex, Linear, GitHub, WeChat, and email via Resend, installed on demand through skill commands. Each agent group receives its own CLAUDE.md memory file, isolated filesystem, container sandbox, and session state — a prompt injection in one group cannot exfiltrate data from another. The OneCLI Agent Vault handles credentials so agents never hold raw API keys, while approval-gated self-modification allows agents to request new packages or MCP servers that administrators must authorize. Scheduled tasks run recurring jobs inside containers with message delivery back to users. The setup script handles dependencies, authentication, and container configuration through Claude Code conversation. Deploy on any Docker-capable Linux server. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Dockhand
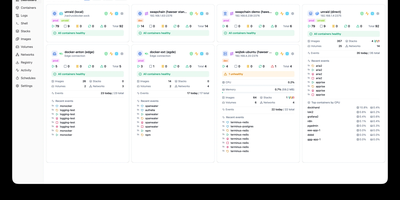
Dockhand is a Docker management platforms, offering a modern alternative to Portainer with free OIDC SSO and vulnerability scanning that competitors gate behind paid tiers. Real-time container management provides start, stop, restart, and remove operations with live resource monitoring across CPU, memory, and network usage on a dashboard with real-time metrics. The visual Docker Compose editor enables stack creation and modification with syntax highlighting, while Git integration deploys stacks directly from repositories with webhooks and auto-sync for GitOps workflows. Vulnerability scanning powered by Grype and Trivy analyzes container images against CVE databases, with configurable auto-update scheduling that can trigger updates based on vulnerability severity criteria. The Hawser Go agent enables management of remote Docker hosts in Standard mode for LAN environments or Edge mode using outbound WebSocket connections for hosts behind NAT, firewalls, or dynamic IPs without exposing inbound ports. Interactive terminal sessions provide shell access into running containers, while the file browser enables uploading, downloading, and editing files directly within containers. Image management includes registry browsing, pull operations, and layer inspection alongside network and volume administration. The security-focused architecture builds its own OS layer from scratch using Wolfi packages via apko with every package explicitly declared. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. BSL 1.1 licensed, converting to Apache 2.0 in 2029.
Ory Hydra
Ory Hydra is an OpenID Certified OAuth 2.0 and OpenID Connect provider that plugs into any existing user database or authentication system through a headless consent and login bridge, letting you own your authorization infrastructure without rebuilding identity management from scratch. The Go binary ships at under 15MB with zero system dependencies and exposes two distinct API surfaces: a public endpoint on port 4444 handling authorization code flows, token exchanges, PKCE challenges, device authorization grants per RFC 8628, and OpenID Connect discovery, plus an admin endpoint on port 4445 managing client registration, token introspection, consent session lifecycle, and JWKS rotation. Access tokens can be issued as opaque reference tokens or signed JWTs for stateless validation at resource servers, while refresh token rotation, token revocation per RFC 7009, and pairwise subject identifiers provide granular security controls. Persistent storage spans PostgreSQL, MySQL, and CockroachDB with automatic schema migrations, and the architecture supports horizontal scaling behind load balancers with shared database state. Dynamic client registration per RFC 7591 enables automated provisioning, and the OAuth 2.0 Threat Model security considerations are implemented as default behaviors rather than optional add-ons. Trusted by OpenAI and other internet-scale platforms. Helm charts and Docker Compose quickstarts provide production-ready deployment paths alongside the broader Ory ecosystem including Kratos for identity management, Oathkeeper for zero-trust API proxying, and Keto for fine-grained permissions. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Mira
The fastest tool on the public Martian Code Review Bench at 77 seconds per PR with competitive F1 scores — while every higher-scoring competitor takes 5 to 14 times longer — Mira is the fully open-source AI code reviewer that ships the entire feature surface other tools gate behind per-seat subscriptions: indexed PR reviews with full-repo context, streaming walkthroughs posted within seconds, inline vulnerability scanning from hourly OSV.dev polls, org-wide package inventory answering "which repos use [email protected]?" in one query, interactive dependency graphs with blast-radius SVG rendering via ReactFlow, a learning loop that synthesizes rules from rejected comments and human review patterns on merged PRs, and cost telemetry showing actual spend per repo and per model. Unlike CodeRabbit, Greptile, and GitHub Copilot code review which are SaaS-only with per-seat pricing, Mira runs as a single Docker image on your infrastructure with your LLM key through OpenRouter (fronting Anthropic, OpenAI, Google Gemini, DeepSeek) or direct to Ollama and vLLM for fully air-gapped deployments. The engine indexes Python, TypeScript, Go, Rust, Java, C/C++, C#, Swift, Kotlin, Scala, and PHP with per-file symbol extraction, enabling multi-file reasoning across diffs rather than isolated line-by-line review. Integrates with GitHub, GitLab, and Forgejo via webhook with full feature parity. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Fleet
Fleet lets IT and security teams query every device in their organization like a SQL database, using osquery to surface installed software, running processes, configurations, and vulnerabilities within seconds across macOS, Windows, Linux, iOS, Android, and ChromeOS. The Go-based server exposes a web console and REST API for centralized device management, with MDM capabilities built on nanoMDM for Apple device enrollment, configuration profiles, and remote lock or wipe. Vulnerability management cross-references installed software inventories against NVD and OVAL CVE databases, automatically flagging known vulnerabilities with severity scores and remediation guidance. Software deployment handles OS updates using Apple Declarative Device Management, Windows Update, and custom installer packages distributed through S3-compatible storage. A GitOps workflow enables infrastructure-as-code management where device policies, osquery queries, and configuration profiles live as YAML files in Git repositories, with CI/CD pipelines pushing changes through the fleetctl CLI. The fleetd agent bundle includes osquery for telemetry, Orbit for version management, and Fleet Desktop providing end users a menu bar status indicator. Integrations connect to Snowflake, Splunk, Elastic, Jira, Zendesk, Vanta, and GitHub Actions for automated compliance reporting. CIS benchmark policies verify security baselines across operating systems. Deployment requires MySQL for persistence and Redis for caching, running as Docker containers or on Kubernetes. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
OpenSearch
OpenSearch is a search and analytics platforms, powering full-text search, log analytics, observability, and AI-powered vector retrieval at petabyte scale. The distributed engine provides BM25 full-text search alongside k-NN vector search using NMSLIB, Faiss, and Lucene libraries, enabling semantic search, hybrid search combining keyword and vector scoring through normalization processors, neural sparse search, and retrieval-augmented generation workflows with built-in ML Commons for model hosting. OpenSearch Dashboards delivers interactive visualization with Discover for log exploration, custom dashboards, alerting, anomaly detection using Random Cut Forest algorithms, and Security Analytics with detection rules mapped to MITRE ATT&CK. Native Prometheus integration with full PromQL support unifies metrics alongside logs and traces in a single observability interface, while Data Prepper handles telemetry ingestion from OpenTelemetry collectors, Fluent Bit, and Logstash-compatible pipelines. SQL and Piped Processing Language queries with a visual PPL builder enable analysts to query data without learning the native DSL. Index State Management automates index lifecycle with rollover, shrink, and delete policies, while cross-cluster replication and searchable snapshots on S3-compatible storage provide disaster recovery. Scoped API keys, field-level security, document-level security, and audit logging deliver enterprise-grade access control. Docker Compose deploys multi-node clusters alongside the Kubernetes operator for orchestrated production environments. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
PentaGI
Autonomous red team execution without manual script coordination is what PentaGI delivers through a multi-agent penetration testing platform engineered for automated security assessments. Security engineers configure testing scopes, target IP ranges, domain lists, and rules of engagement through an interactive web console with real-time execution graphs. Autonomous agent personas break down high-level assessment goals into discrete tactical phases, orchestrating network port discovery, service banner fingerprinting, web application crawling, and CVE verification. Specialized agents query integrated Graphiti knowledge graphs and local vulnerability repositories to synthesize attack paths, validate exploitability, and confirm finding veracity before issuing alerts. Operators monitor live agent terminal streams, inspect sandboxed tool executions, and adjust active LLM provider routes across OpenAI, Anthropic, or local Ollama endpoints. The template editor allows red teams to compose reusable testing playbooks with customizable security prompt chains, safety constraints, and automated remediation reporting. Audit logs capture full command histories, raw tool outputs, and LLM reasoning steps to generate compliance-ready technical documentation. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Open Code Review
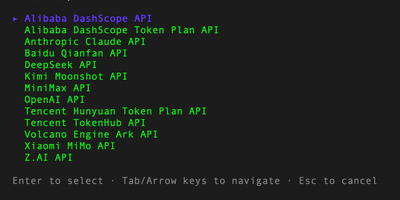
Originated as Alibaba Group's official internal AI code review assistant serving tens of thousands of developers and identifying millions of code defects over two years before open-sourcing in May 2026 — now at 21,000+ GitHub stars — Open Code Review is the production-hardened platform that proves enterprise-grade code review can be fully open-source under Apache 2.0. The hybrid architecture separates deterministic engineering pipelines (file selection, diff parsing, rule matching for NPE, thread-safety, XSS, and SQL injection across 10+ languages) from LLM-powered agent reasoning with tool-use capabilities including FileRead, CodeSearch, and cross-file context inspection, consuming approximately one-ninth the tokens of general-purpose coding agents while delivering line-level precise comments with severity and confidence scoring. The bundled web dashboard (port 4173) provides review management, findings triage, result browsing, and direct GitHub posting without external dependencies, while the session viewer (port 5483) renders full LLM request/response traces for debugging and auditing. Integration spans GitHub Actions, GitLab CI, GitFlic CI, and Gerrit with delegation mode enabling Claude Code, Cursor, and other AI agents to leverage OCR's engineering logic alongside their own LLM reasoning. Supports OpenAI, Anthropic, Google Gemini, DeepSeek via built-in providers plus Ollama and vLLM for air-gapped deployments. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Bitwarden
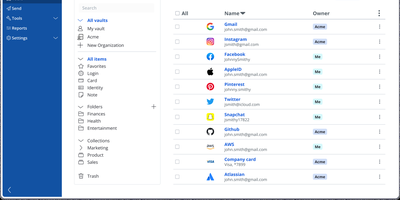
Backed by nearly 20,000 GitHub stars and ranked number one in G2's Enterprise User Satisfaction for eleven consecutive quarters, Bitwarden is the open-source password manager trusted by millions worldwide. The zero-knowledge encryption architecture ensures all vault data — passwords, passkeys, credit cards, identities, secure notes, and file attachments — is encrypted exclusively on client devices using AES-256 with PBKDF2-SHA256 or Argon2id key derivation and RSA-2048 for organization key exchange. Cross-platform clients span a web vault, browser extensions for Chrome, Firefox, Safari, Edge, Opera, Vivaldi, and Brave, native desktop apps for Windows, macOS, and Linux, mobile apps for iOS and Android, and a CLI for scripting. Bitwarden Send enables time-limited, password-protected sharing of text and files, while the built-in TOTP authenticator generates two-factor codes alongside stored credentials. Enterprise deployments integrate with identity providers through SAML 2.0 and OpenID Connect SSO, automate provisioning via SCIM or Directory Connector supporting LDAP, Active Directory, Azure AD, Okta, and OneLogin, and enforce security policies with custom roles and granular permissions. Emergency access allows designated contacts to request vault view or takeover through configurable waiting periods with cryptographic key exchange. The Secrets Manager stores API keys, tokens, and infrastructure credentials with native GitHub Actions, GitLab CI/CD, Ansible, and Terraform integrations. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
SearXNG
Up to 280 search services - Google, Bing, DuckDuckGo, Brave, Qwant, Startpage - aggregated without tracking or profiling: SearXNG is a privacy-respecting metasearch engine (AGPL-3.0, successor to Searx). Your instance queries the upstream engines on your behalf: your IP address, cookies, and search history never reach them, tracker parameters are stripped from result URLs, and an optional image proxy fetches thumbnails server-side so result pages leak nothing. It can even route outbound queries through Tor for full anonymity. Search is organized into categories - general, images, videos, news, maps, music, IT, science, files - with bang shortcuts for targeting specific engines, and every source can be enabled, disabled, or weighted per category in settings.yml. A plugin system adds calculators, hash tools, tracker removal, and unit conversions inline, and preferences (themes, safe search, languages, engine selection) persist in cookies rather than server-side accounts. The real argument for running your own instance rather than trusting a public one is control: you decide the logging policy (none), the engine mix, rate limiting, and who gets access - making it the default search backend for browsers, families, and teams that want Google-quality results without the profile.
SuperTokens
Powering authentication for over 15,000 GitHub stargazers and production deployments across startups and enterprises alike, SuperTokens delivers the complete login infrastructure that Auth0, Firebase Auth, and AWS Cognito charge premium prices for — entirely open source under Apache 2.0 with no per-user limits. The Java-based core service runs as a lightweight HTTP microservice that connects to PostgreSQL or MySQL and handles email-password login, passwordless magic links and OTP via email or SMS, social OAuth with Google, GitHub, Facebook, Apple, and any custom OIDC provider, phone-password authentication, and time-based one-time password multi-factor authentication. Session management uses rotating refresh tokens with anti-CSRF and anti-session-fixation protections, verifying tokens locally in your backend SDK without network round-trips to the core. Frontend SDKs for React, React Native, Angular, Vue, and vanilla JavaScript provide pre-built UI components for login, signup, email verification, and password reset flows, all customizable through an override system that lets you add pre- and post-API logic, custom hooks, and user event handlers. The built-in user management dashboard enables administrators to view users, reset passwords, revoke sessions, modify roles, and manage email verification status. Multi-tenancy and organization support powers B2B SaaS applications with tenant-level authentication configuration and Enterprise SSO via SAML and OIDC. Migration tools support bulk importing millions of existing password hashes, TOTP secrets, and role mappings. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Cerbos
Cerbos decouples authorization logic from application code entirely, evaluating human-readable YAML policies in under one millisecond through a stateless Policy Decision Point that requires no application state synchronization or cross-network fan-out. Its custom decision engine benchmarks up to 17x faster than OPA-based alternatives. Access control policies use conditions expressed in Google's Common Expression Language, supporting role-based, attribute-based, and policy-based access control patterns including derived roles, scoped policies, and permissions-aware data filtering that pushes authorization predicates directly into database queries. The PDP exposes both gRPC and HTTP APIs with SDKs for JavaScript, Python, Go, Java, .NET, Rust, PHP, and Ruby, making integration a single function call regardless of tech stack. GitOps-native workflows treat policies as code with Git versioning, CI validation through GitHub Actions, coverage reports, breaking-change detection, and audit logs of every authorization decision for ISO27001, SOC2, and HIPAA compliance. Deployment flexibility spans Kubernetes sidecars, standalone services, systemd daemons, AWS Lambda functions, and WebAssembly-embedded PDPs that run authorization logic directly in browsers, serverless architectures, and edge devices. The Admin API manages policy lifecycle operations programmatically, while the built-in Playground and REPL provide interactive testing environments for policy authoring and debugging. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Xalgorix
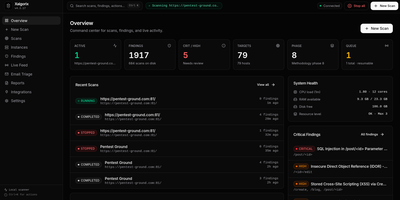
Xalgorix delivers AI-driven penetration testing that proves vulnerabilities exist rather than guessing, pairing an autonomous LLM agent with an independent exploit verifier that re-exploits every finding before it reaches your report. The 22-phase methodology mirrors how a skilled human pentester works through an engagement, covering reconnaissance, subdomain enumeration, port scanning, web crawling, parameter fuzzing, SQL injection testing, XSS detection, authentication bypass, API testing, and more. Select all phases or pick specific ones per target. The platform ships with 85+ offensive security tools preinstalled (nmap, nuclei, httpx, subfinder, katana, ffuf, gobuster, sqlmap, masscan, dalfox, feroxbuster) plus 14 built-in agent tools for browser automation, terminal execution, and note-taking. Connect your own LLM provider (OpenAI, Anthropic, DeepSeek, Gemini, Groq, Ollama, or MiniMax) so no scan data or target information leaves your infrastructure. The web dashboard on port 9137 provides live WebSocket telemetry showing tool calls, agent reasoning, and findings as scans progress. A findings index with CVSS scoring and severity filters organizes results, and branded PDF reports include your company name and logo. Wildcard and multi-target scans handle red team attack-surface mapping, while source-code scanning audits repositories directly without requiring a deployed target. A REST API enables scripted scans and SIEM pipeline integration, and webhooks push notifications to Discord or Telegram. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
CTFd
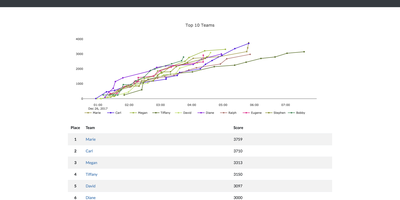
Starred by over 6,500 users on GitHub and trusted by organizations including Toyota, CTFd has been the leading open-source platform for hosting cybersecurity competitions since 2015, providing everything needed to run professional Capture The Flag events through a clean web-based administration panel without touching a database query. The framework supports both individual and team-based competitions with automatic tie resolution, configurable score freezing, and scoregraphs comparing the top teams with detailed progress tracking. Challenge creation offers static and regex-based flags, dynamic scoring that adjusts point values based on solve count, unlockable hints purchasable with points, file attachments uploaded to local storage or Amazon S3-compatible backends, and challenge attempt limits with automatic bruteforce protection. Version 3.8 introduced challenge logic fields controlling flag submission behavior with any, all, and team modes, integrated dynamic scoring into the standard challenge type, participant ratings and reviews on challenges, and admin-stored challenge solutions viewable after competition. The Markdown-based content management system enables custom pages for rules, FAQs, and resources, while SMTP and Mailgun integration handles email confirmation and password recovery. The plugin architecture supports custom challenge types, flag validators, and scoring algorithms, while the theme system provides complete visual customization. Import and export functionality preserves entire competition configurations for archival and reuse across events. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.

CubeSandbox
CubeSandbox gives every AI agent its own hardware-isolated MicroVM with a dedicated Linux kernel — not a shared-kernel container but a true KVM virtual machine — booting in under 60ms with less than 5MB of memory overhead per instance, enabling thousands of concurrent sandboxes on a single server via kernel sharing and Copy-on-Write memory. The Rust-built CubeProxy exposes an E2B SDK-compatible REST API on Axum, so existing E2B Cloud applications switch by changing one environment variable with zero client code changes. CubeMaster orchestrates cluster-level scheduling in Go while Cubelet manages node-local sandbox lifecycles including create, run, pause, resume, snapshot, and destroy operations. CubeVS, the eBPF-powered network layer, enforces per-sandbox isolation with LPM trie-based egress policies entirely in kernel space — no userspace context switches — while CubeEgress provides an L7 security proxy with per-domain, per-path, and per-method allowlists plus automatic credential injection that keeps secrets invisible to sandbox code. Hundred-millisecond-granularity snapshots enable checkpoint, rollback, and parallel fork from any saved state. The volume framework supports E2B-compatible pluggable storage with independent lifecycle and cross-sandbox sharing. Production deployment uses Terraform on Tencent Cloud or Helm charts on Kubernetes, K3s, or TKE, with full ARM64 support alongside x86_64 and AutoPause/AutoResume for cost optimization. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Element
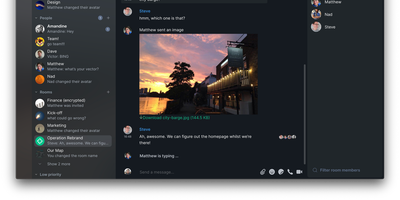
Matrix's flagship client, built by the protocol's creators: Element brings the decentralized open standard for real-time communication to web, desktop, iOS, and Android. Paired with a Matrix homeserver, it delivers Slack-quality team messaging where you own every message, file, encryption key, and byte of metadata. End-to-end encryption is on by default, built on Olm and Megolm - the Double Ratchet algorithm family Signal popularized, extended for large-room scalability and publicly audited by NCC Group. Messages encrypt per-device with cross-signed device verification, so even a compromised server yields nothing readable. Federation is the defining capability: like email, users on different homeservers converse seamlessly, and 30+ bridges connect Matrix rooms to Slack, Discord, WhatsApp, and Telegram, so moving to sovereign infrastructure doesn't sever contact with anyone. Rooms support threads, reactions, file sharing, and voice and video calls via Element Call. The result is digital sovereignty chosen by governments and enterprises across Europe: your data sits on your server in your jurisdiction, portable to any other Matrix host because the protocol is an open standard. Apache-2.0 licensed, with no per-user fees at any scale.
Mailcow
With over 13,000 GitHub stars and active monthly releases, Mailcow delivers a production-ready mail server infrastructure through Docker Compose orchestration of twelve integrated containers. The stack pairs Postfix as the MTA handling SMTP traffic with Dovecot for IMAP and POP3 retrieval featuring the Flatcurve full-text search engine, while Rspamd provides machine-learning-powered spam filtering with Bayesian classification, DKIM signing, and ARC support. ClamAV scans attachments for malware including Office document macro analysis via Olefy, and SOGo serves as a responsive webmail client with CalDAV, CardDAV, and Microsoft ActiveSync synchronization. The admin panel manages multiple domains, per-user spam score thresholds, quarantine review, black and whitelists, temporary spam aliases, mailbox quotas, and TLS enforcement policies for both inbound and outbound messages. Security features include two-factor authentication via TOTP, WebAuthn, and Yubikey OTP, a Fail2ban-like Netfilter integration for brute-force protection, and automatic SPF, DKIM, and DMARC configuration. The ACME container handles Let's Encrypt certificate generation with DNS-01 challenge support, while Postfix TLS-Pol provides MTA-STS and DANE/TLSA resolution for encrypted transport. Built-in imapsync enables periodic migration from remote mailboxes, and the REST API allows programmatic management of all server resources. MariaDB stores user data, Redis caches configuration and sessions, and Unbound provides local DNSSEC-validating DNS resolution. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL-3.0 licensed.