Openship
Point Openship at a GitHub repo, local folder, or prebuilt artifact and it detects your stack, builds a Docker container, provisions databases, configures domains with automatic Let's Encrypt TLS, and routes traffic through an OpenResty edge layer on ports 80 and 443. Already past 10,000 stars since launching in March 2026, it turns any Linux VPS into a managed application host. Language support covers Node.js, Python, Go, Rust, PHP, Ruby, Java, .NET, Docker, and monorepo projects with push-to-deploy CI/CD, pull request preview environments on unique subdomains, staging/production flows, and one-click rollbacks. Integrated backend services include managed Postgres, MySQL, MongoDB, Redis, persistent volumes, WebSocket proxying, object storage, and worker processes, all provisioned from the dashboard without compose files. A built-in SMTP server handles transactional email with automatic DKIM, SPF, and DMARC configuration, eliminating external email services. The edge layer serves HTTP/3 with Brotli compression, configurable cache rules, and instant purging. Real-time monitoring streams build logs, container metrics, visitor geography, and per-status-code analytics at 1.4 microsecond overhead with zero database writes. Scheduled backups cover databases and volumes with one-click restore and export. Three interfaces (web dashboard, desktop app for macOS/Windows/Linux, and the openship CLI) drive the same API, plus a Model Context Protocol endpoint for AI integration. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Coolify VPS
The open-source PaaS with 55,000+ GitHub stars and the largest one-click service catalog in its class — Coolify gives you the Vercel push-to-deploy workflow on a dedicated server you control. Connect a GitHub, GitLab, Bitbucket, or Gitea repository and every push builds and deploys automatically via Nixpacks, a Dockerfile, or Docker Compose, with Traefik or Caddy reverse proxying, automatic Let's Encrypt certificates, and per-branch preview deployments with their own URLs. Databases — PostgreSQL, MySQL, MariaDB, MongoDB, Redis — provision in a few clicks, and a catalog of 280+ one-click service templates covers WordPress, n8n, Grafana, MinIO, Plausible, Ollama, and more. One dashboard manages the entire server, with Docker Swarm available for clustering multiple nodes. Backups go to any S3-compatible storage with one-click restore, and a full API supports CI/CD integration. All configuration lives on your own server, so resources keep running even if you stop using Coolify — no vendor lock-in by design. Running on a dedicated VPS with guaranteed CPU, RAM, and SSD, full root access via SSH and browser console. Apache 2.0 licensed.
Dokploy VPS
Your own Heroku or Vercel on a dedicated server — Dokploy is the open-source PaaS that replaces cloud platform subscriptions with a single dashboard you control. Point it at a Git repository or a Docker image, and it builds and deploys the application using Dockerfiles, Nixpacks, or Heroku/Paketo buildpacks. Traefik handles reverse proxying, routing, load balancing, automatic Let's Encrypt SSL, and HTTP/3. Databases — MySQL, PostgreSQL, MongoDB, MariaDB, libsql, and Redis — provision from the UI with automated backups to any S3-compatible destination. Complex multi-service applications deploy through native Docker Compose support, and multi-node scaling uses Docker Swarm. The web dashboard covers environment variables, volumes, resource limits, real-time CPU/memory/network monitoring, and deployment logs, with a CLI and REST API for automation. Deploy notifications go to Slack, Discord, Telegram, or email. One-click templates install common open-source tools, and a single control plane can manage deployments across multiple remote servers. Because everything is standard Docker, there is no lock-in: Dockerfiles, Compose files, and data volumes work anywhere else Docker runs. The push-to-deploy workflow of a $20/seat cloud PaaS, running on a dedicated VPS with guaranteed CPU, RAM, SSD, and full root access — no per-app, per-environment, or per-seat fees regardless of how many applications you deploy. 26,000+ GitHub stars.
Temps
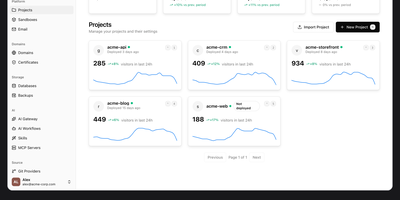
Consolidate application hosting, web analytics, error tracking, and performance monitoring into Temps, an open-source developer platform that replaces disparate SaaS subscriptions with a single compiled Rust binary. Engineering teams deploy full-stack web applications, background daemons, and microservices directly from Git repositories with automated TLS certificate provisioning powered by an embedded Cloudflare Pingora reverse proxy. The centralized web console unifies real-time visitor analytics, conversion funnels, and rrweb-powered session replay recordings without third-party tracking scripts. Integrated error monitoring ingests runtime exceptions with full stack traces and source map resolution, while continuous health checks evaluate container CPU utilization, memory thresholds, and network throughput across custom alerting rules. Developers manage infrastructure through an extensive command line interface containing over 440 operations across 69 command groups, or deploy drop-in skill files that allow AI coding assistants like Claude Code and Codex to provision preview environments autonomously. The platform also provides serverless key-value storage, S3-compatible blob buckets, and native transactional email routing with custom DKIM validation. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Levelrail
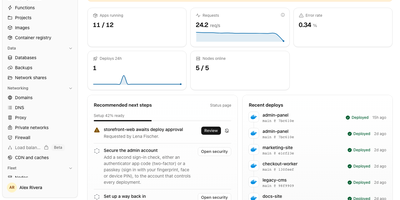
Push to git, watch the deploy go live over HTTPS, and roll back in one click, all on servers you own: Levelrail is a self-hosted platform for running apps and databases without Kubernetes. Deploys start from GitHub, GitLab, Bitbucket, or Gitea webhooks and build from a Dockerfile, Compose file, image, or framework preset such as Next.js, Go, React, or Spring Boot, with preview environments per pull request, canary and blue-green rollouts, approvals, and freezes. Embedded Caddy gives every app a domain with HTTPS: self-signed by default, Let's Encrypt with one toggle, a free sslip.io address when no domain exists, or your own uploaded certificate. Provision Postgres, MySQL, MariaDB, MongoDB, Redis, ClickHouse, and more with scheduled backups that are re-downloaded and verified, Postgres point-in-time recovery, and password rotation. Metrics with deploy markers, searchable live logs, alerts, and a public status page need no separate monitoring stack. Roughly 360 one-click templates and a Cmd+K search across apps, databases, and nodes speed up daily work. Extra servers enroll with a one-time token and a reverse-dialed agent that needs no inbound ports. Sign in with passkeys, TOTP, OAuth from 20 providers, or OIDC, then scope access with IAM policies, encrypted secrets, and a tamper-evident audit log. A CLI, HTTP API, and MCP server let scripts and coding agents deploy and roll back. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
OpenLLM
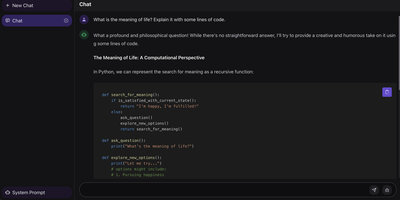
OpenLLM serves any large language model as an OpenAI-compatible API endpoint from a single CLI command, handling model download, backend selection, quantization, and port binding automatically. It supports the full spectrum of popular models including Llama 3.3, Qwen2.5, DeepSeek, Mistral, and Phi3, choosing between vLLM and PyTorch inference backends based on hardware capabilities. When vLLM is available, continuous batching with PagedAttention achieves up to 23x throughput improvement over naive serving, while GPTQ and bitsandbytes quantization reduces memory requirements for GPU-constrained deployments. The server exposes a RESTful API on port 3000 with full OpenAI client library compatibility, enabling drop-in replacement for commercial providers in any application using the standard chat completions format. A built-in web chat UI at the /chat endpoint provides immediate interactive testing without external clients. Custom model repositories allow teams to maintain private catalogs of fine-tuned models alongside the default repository that tracks the latest releases. Deployment workflows generate production-ready Docker images automatically, with Kubernetes manifest support for orchestrated scaling. Native integration with LangChain and LlamaIndex supports RAG pipelines, Transformers Agents enables tool-calling workflows, and HuggingFace Hub handles model discovery. Server-Sent Events enable real-time token streaming across all API endpoints. Backed by BentoML's production ML infrastructure. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Zeabur
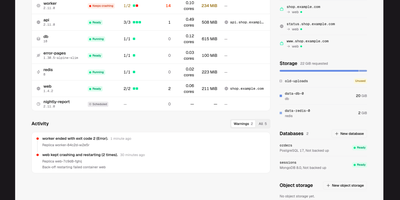
Zeabur is a self-hosted web platform that deploys and runs your services on your own Kubernetes cluster, presenting the cluster as simple projects and services instead of raw manifests. Every change starts as a readable plan listing the exact fields it will write and who owns them today, and nothing is applied until you confirm it. When something breaks, Zeabur says so in plain words and points at the fix: a worker that restarted fourteen times gets a button straight to the logs from the run before the restart. You deploy from Git repositories, from an uploaded folder or ZIP archive, or directly in the dashboard, then follow live logs, open a terminal inside a container, and watch CPU and memory move over time. Projects are namespaces and all state lives in Kubernetes objects, so there is no Zeabur database to back up, and uninstalling the platform leaves your Deployments, Services, and Ingresses running untouched. Companion pieces add passkey sign-in for kubectl with tokens that expire in minutes, image builds from Git through a BuildKit operator, and a catalog of cluster components and app templates. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Uncloud
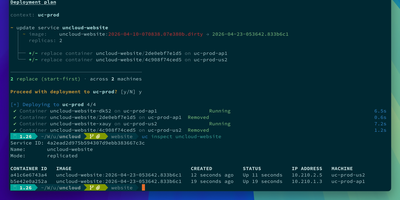
Scatter a few cheap VPS boxes, a home server, and one bare metal machine across three different providers, and Uncloud still treats them as a single place to run your applications. You describe services in ordinary Docker Compose files, deploy them with the uc command line tool, and publish any container port as a public HTTPS endpoint in a single command. Every machine joins an encrypted WireGuard mesh with its own container IP addresses, so services on different continents reach each other directly without VPN configuration or exposed ports. A built-in DNS server resolves service names to container IPs, and the integrated Caddy reverse proxy provisions and renews Let's Encrypt certificates automatically, sharing them across the cluster. Rolling updates replace containers with zero downtime, persistent Docker volumes keep stateful services safe, and the Unregistry integration pushes image layers straight to your machines when no registry is available. There is no control plane to babysit: each machine keeps a synchronised copy of the cluster state, and SSH access to any single node is enough to manage the whole fleet. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Dockge
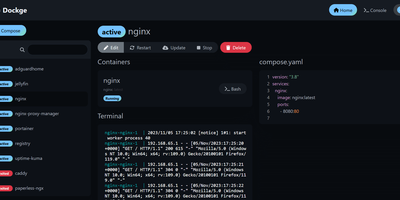
Created by the developer behind Uptime Kuma and carrying over 23,000 GitHub stars, Dockge brings the same clean, reactive design philosophy to Docker Compose stack management with a web interface that makes Portainer's compose handling feel like editing YAML in a terminal over SSH. The interactive editor provides syntax highlighting, inline validation, and a live preview of your compose.yaml files while keeping every stack stored as a standard file on disk in /opt/stacks by default, meaning you can seamlessly switch between the web UI and the docker compose CLI without lock-in or proprietary database formats. Real-time WebSocket updates stream pull progress, container start/stop transitions, and build output directly to the browser with no polling delays. The built-in web terminal opens a shell session inside any running container for quick debugging, while the docker-run-to-compose converter transforms single-container run commands into proper compose.yaml definitions with one click. Multi-agent support introduced in version 1.4.0 connects multiple Docker hosts to a single Dockge dashboard, enabling centralized management of stacks distributed across different servers. Image update detection shows which stacks have newer versions available, and one-click updates pull the latest images and recreate containers without manual intervention. The stack is a single Docker container running on Node.js with Socket.IO for reactivity and stores no external database. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Argo CD
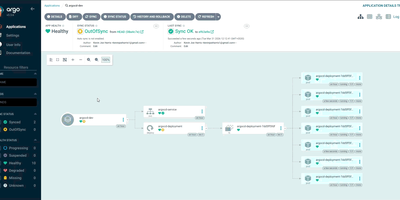
A CNCF Graduated project with over 23,700 GitHub stars and adoption by organizations including Intuit, Adobe, Capital One, and Red Hat, Argo CD has become the industry standard for GitOps-based Kubernetes deployments since its creation at Intuit in 2018, treating Git repositories as the single source of truth for application configurations and automatically reconciling live cluster state with declared desired state. The platform supports Helm charts including Helm 4, Kustomize overlays, Jsonnet, and plain Kubernetes YAML manifests, rendering templates and applying resources through configurable sync policies with automated or manual reconciliation, pruning of orphaned resources, and self-healing that reverts unauthorized cluster changes. ApplicationSets enable templated generation of applications across multiple clusters, environments, and Git repositories using generators for pull requests, Git directories, cluster lists, and merge strategies. The web UI provides a real-time application topology view with resource health status, sync state indicators, log streaming, and a network view supporting Gateway API and Ingress visualization. Version 3.5 introduced mTLS for internal component communication, graduated user impersonation and source hydrator to beta, added native ApplicationSet management with preview applications in the UI, and delivered source integrity validation. Multi-cluster management deploys applications across development, staging, and production environments from a single Argo CD instance with RBAC, SSO via OIDC and SAML, and audit logging. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Dokku
With over 32,000 GitHub stars and a decade of production use since 2013, Dokku is the original self-hosted Heroku alternative — a Docker-powered PaaS that turns any single Ubuntu server into a full application platform with a simple git push. Deploy applications written in Node.js, Python, Ruby, Go, Java, PHP, Scala, and Clojure using Heroku-compatible buildpacks, Cloud Native Buildpacks via pack-cli, standard Dockerfiles, or pre-built Docker images, with automatic language and framework detection handling the rest. Every deployment runs through zero-downtime checks that health-test new containers before routing traffic via the built-in Nginx reverse proxy, which handles virtual host configuration, WebSocket proxying, and HTTP/2 support automatically. The official plugin ecosystem provides managed datastores including PostgreSQL, MySQL, MariaDB, MongoDB, Redis, RabbitMQ, and Elasticsearch, each provisioned with a single CLI command and linked to apps via environment variables. Automated TLS certificates arrive through the Let's Encrypt plugin with auto-renewal, while persistent storage volumes, cron job scheduling, user ACL management, and process scaling round out the platform capabilities. The entire system is CLI-driven — no web dashboard — keeping resource overhead minimal enough to run multiple applications on a $5/month VPS. Dokku also supports Lambda function builds, custom builder plugins, and app.json-based healthcheck configuration for advanced deployment workflows. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Nixopus
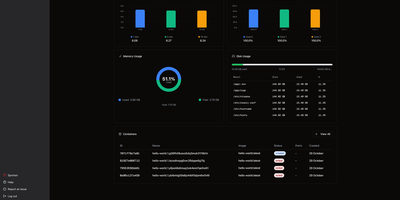
Tell an AI agent to deploy your app and watch it actually happen. Nixopus connects to your GitHub repo, analyzes the codebase to detect your framework, generates the right Docker configuration, resolves dependency conflicts, and ships the whole thing to your server with HTTPS enabled. When something breaks, the agent reads the logs, creates a pull request with a fix, and redeploys without waking you up. The chat interface lets you deploy, add custom domains, check logs, roll back, and troubleshoot in plain English from the web dashboard or directly from your VS Code or Cursor editor. Extensions bring one-click installs for 100+ self-hostable apps like Appwrite, Excalidraw, and Ollama, each showing you exactly what it runs on your server before installation. Connect multiple servers and monitor CPU, memory, disk, and running containers across your entire fleet from a single dashboard with draggable widget layouts. The built-in terminal opens SSH sessions right in the browser with split-pane support, so you can watch logs in one pane while running commands in another. Framework detection covers Next.js, Django, Rails, Go, FastAPI, and anything else that fits a container image. Every deployment gets automatic TLS via Caddy with Let's Encrypt certificates provisioned and renewed silently. Previous container images are retained so rollbacks skip the rebuild step entirely. Deploy on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
OpenRun
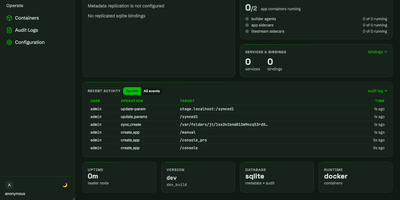
OpenRun replaces the patchwork of CI/CD pipelines, reverse proxies, and identity providers that teams typically assemble when deploying internal tools, offering declarative GitOps-based deployment of web applications to Docker, Podman, or Kubernetes from a single self-hosted Go binary. Point it at a Git repository and it builds containers from AppSpec templates, routes requests by domain or URL path, provisions TLS certificates automatically, and scales idle applications to zero when unused. Blue-green staged deployments promote new versions through development, staging, and production environments with atomic rollback across multiple apps simultaneously. Every deployed application inherits SSO authentication through OAuth, OpenID Connect, or SAML providers alongside role-based access control, all configured once at the platform level rather than per app. Service bindings provision isolated PostgreSQL, MySQL, SQLite, or Redis credentials for each application, while Litestream integration replicates SQLite databases to S3 for automatic disaster recovery. The management console provides a web interface for monitoring containers, reviewing audit logs, configuring syncs, and managing server operations. AppSpec templates handle Streamlit, Gradio, FastAPI, Flask, and FastHTML projects out of the box, deploying existing Python applications without requiring custom Dockerfiles. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Komodo
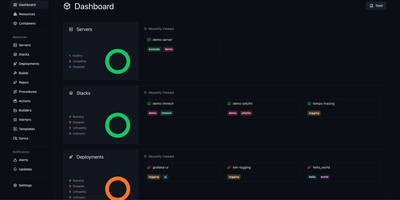
Komodo puts every server, container, and deployment pipeline behind a single dashboard where you build, ship, and monitor Docker workloads across unlimited hosts. Lightweight stateless agents install on each connected server and report CPU, memory, and disk metrics back to the Rust-powered core, giving you real-time visibility without heavyweight monitoring stacks. Docker Compose stacks deploy directly from the UI or link to Git repositories with webhook-triggered automatic redeploys on push. A built-in CI pipeline compiles versioned Docker images from source, with optional AWS spot instances for burst build capacity. For orchestration at scale, Docker Swarm management handles node configuration, service deployment, and multi-node stack orchestration from the same control plane. Browser terminal sessions open persistent named shells on servers and inside containers, complete with shared team access and scriptable Actions that chain executions into multi-stage procedures. Infrastructure-as-code support defines all resources declaratively in TOML files within a Git repository, keeping production state version-controlled and auditable. Granular role-based access control with user groups, per-resource permissions, and OAuth through GitHub and Google keeps teams operating within defined boundaries. A full OpenAPI specification, dedicated CLI, and typesafe client libraries for Rust and TypeScript make programmatic integration straightforward. With 12,000+ stars and active development, the community continues expanding multi-architecture builds and Swarm tooling.
Kubero
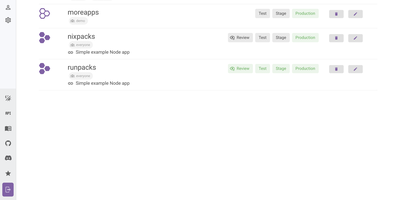
With over 4,300 GitHub stars and a v3 release adding built-in user management, team views, and multi-language support, Kubero has established itself as the most feature-complete open-source Heroku alternative running natively on Kubernetes. The platform operates as a Kubernetes operator with two containers — kubero-ui and the operator — storing all state in etcd without an external database. Developers push code via Git integration with GitHub, GitLab, Bitea, or Gitea, and Kubero automatically builds using Buildpacks, Nixpacks, Runpacks, or Dockerfiles, then deploys to the configured domain with SSL via cert-manager. CI/CD pipelines support up to four staging environments — review, test, staging, and production — with per-stage environment variable isolation and ephemeral review apps that spin up on pull request open and tear down on close. The template catalog includes over 170 pre-configured applications like WordPress, Grafana, and PostgreSQL deployable in one click, while managed add-ons provide highly available PostgreSQL, Redis, MySQL, Kafka, CouchDB, Elasticsearch, and MongoDB alongside your applications. Security features include Trivy vulnerability scanning, GitHub and OAuth2 single sign-on, basic auth, and a role-based permission system with API tokens. The NestJS backend with Vue.js and Vuetify frontend provides application metrics, real-time logs, a built-in web console for container access, scheduled cronjob management, and deployment notifications via Discord, Slack, or webhooks. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL-3.0 licensed.
Stormkit
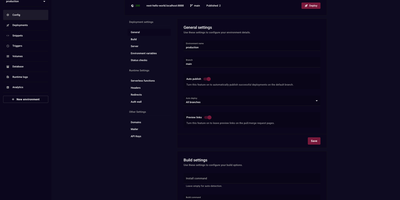
Stormkit delivers a self-hostable PaaS that eliminates vendor lock-in while providing Vercel-class deployment workflows. The Go backend handles build orchestration, hosting, and background job processing while the React frontend provides a complete management dashboard for applications, environments, and team collaboration. Git integration with GitHub, GitLab, and Bitbucket enables push-to-deploy workflows where every commit triggers automated builds with preview links posted directly to pull requests. Serverless functions use filesystem-based routing — each TypeScript or Node.js file in the API directory becomes an endpoint automatically, deploying to AWS Lambda with configurable timeouts. PostgreSQL database schemas ship with automatic migrations, isolated credentials per environment, and secure environment variable injection preventing credential leakage between staging and production. Custom domains provision TLS certificates automatically through Let's Encrypt with support for custom certificates and headers. The environment system creates isolated deployment contexts for production, staging, and development with independent variables, domain bindings, and auto-publish rules per branch. Privacy-respecting server-side analytics track visitors, referrers, and top paths without client cookies or third-party scripts. Role-based access control manages team permissions across applications. Docker Compose deployment provisions the full stack including the API server, hosting service, build runner, and worker server. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
QuickStack
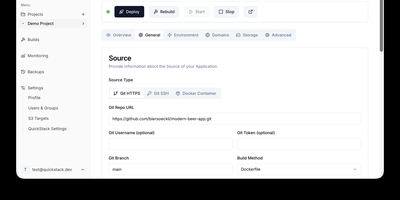
QuickStack transforms your standalone Linux server or cluster into a self-hosted platform-as-a-service that automatically compiles, deploys, and monitors full-stack applications and relational databases without vendor lock-in. Developers can trigger instant deployments directly from public or private Git repositories, upload custom Dockerfiles, or pull container images straight from private registries with automated webhook synchronization. The built-in application catalog enables one-click provisioning of production databases including PostgreSQL, MySQL, MariaDB, MongoDB, and Redis with preconfigured internal network isolation. Administrators can route traffic across custom domains with automated Let's Encrypt SSL certificate issuance, inspect real-time CPU and memory telemetry, stream container runtime logs, and launch in-browser web terminals. Teams can configure granular role-based access controls with single sign-on authentication, establish zero-trust ingress and egress network security policies, and orchestrate automated volume snapshots directly to S3 object storage. When infrastructure requirements expand, operators can attach additional worker nodes using lightweight join tokens to distribute workloads seamlessly across high-availability compute pools. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GNU GPL v3.0 licensed.
CapRover
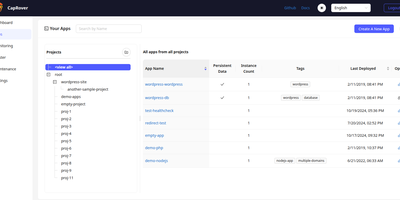
With over 15,000 GitHub stars and nearly nine years of active development, CapRover is the self-hosted PaaS that replaces Heroku's pricing with your own infrastructure while keeping the deploy-and-forget simplicity. The web dashboard manages application lifecycle from deploy through scaling — configure custom domains, environment variables, persistent volumes, instance counts, and nginx templates without touching config files or SSH. The CLI tool enables scriptable deployments with a single command from your terminal or CI/CD pipeline, while webhook-based deployment triggers automated builds from Git pushes. The one-click app marketplace provides over 100 pre-configured services including WordPress, Ghost, PostgreSQL, MySQL, MongoDB, Redis, Grafana, Portainer, and dozens more, each deployed as a Docker container with volumes and environment variables preconfigured. Automatic HTTPS provisions and renews Let's Encrypt certificates for every custom domain with one-click HTTP-to-HTTPS redirects. Under the hood, Docker Swarm orchestrates containers across multiple nodes for horizontal scaling and load balancing, while nginx handles routing with fully customizable EJS-generated configuration templates per application. Deployment supports four methods: CLI push, tarball upload through the web UI, Docker image reference, and Git repository connection. The build system supports Dockerfiles, captain-definition files with build packs, and direct Docker image pulls. NetData integration provides real-time server monitoring dashboards. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.