Xalgorix
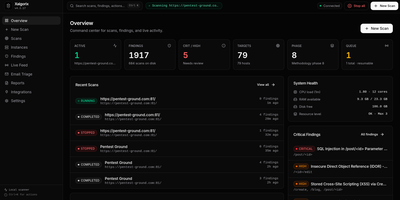
Xalgorix delivers AI-driven penetration testing that proves vulnerabilities exist rather than guessing, pairing an autonomous LLM agent with an independent exploit verifier that re-exploits every finding before it reaches your report. The 22-phase methodology mirrors how a skilled human pentester works through an engagement, covering reconnaissance, subdomain enumeration, port scanning, web crawling, parameter fuzzing, SQL injection testing, XSS detection, authentication bypass, API testing, and more. Select all phases or pick specific ones per target. The platform ships with 85+ offensive security tools preinstalled (nmap, nuclei, httpx, subfinder, katana, ffuf, gobuster, sqlmap, masscan, dalfox, feroxbuster) plus 14 built-in agent tools for browser automation, terminal execution, and note-taking. Connect your own LLM provider (OpenAI, Anthropic, DeepSeek, Gemini, Groq, Ollama, or MiniMax) so no scan data or target information leaves your infrastructure. The web dashboard on port 9137 provides live WebSocket telemetry showing tool calls, agent reasoning, and findings as scans progress. A findings index with CVSS scoring and severity filters organizes results, and branded PDF reports include your company name and logo. Wildcard and multi-target scans handle red team attack-surface mapping, while source-code scanning audits repositories directly without requiring a deployed target. A REST API enables scripted scans and SIEM pipeline integration, and webhooks push notifications to Discord or Telegram. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
ZTNET
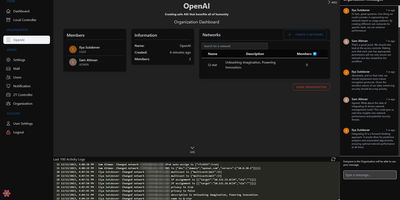
ZTNET provides a polished web dashboard for running your own ZeroTier network controller, covering network creation, member authorization, IP assignment, flow rule editing, and real-time node monitoring entirely from the browser. The organization system supports multi-tenant deployments where teams manage separate network pools with role-based permissions and customizable email notification templates for events like member joins, departures, IP changes, and authorization updates. Each network view displays connected members with their ZeroTier addresses, assigned IPs, last-seen timestamps, physical endpoints, and protocol versions in a clean tabular layout. The admin panel provides platform-wide user management, SMTP configuration for transactional emails, and system-level settings. Built on the T3 stack with Next.js, Prisma ORM, tRPC, TypeScript, and Tailwind CSS with DaisyUI components, the application supports both PostgreSQL and SQLite for persistence and communicates directly with the ZeroTier controller daemon through its native API. Dark and light themes adapt to user preference, and responsive layouts make network management practical from any device. Docker Compose bundles the web application alongside the ZeroTier controller service. Over 100,000 Docker pulls confirm steady community adoption. GPL-3.0 licensed.
Z-Wave JS UI
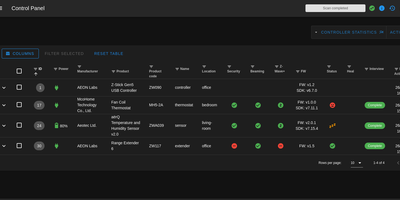
Managing dozens of smart locks, dimmers, thermostats, and sensors across a Z-Wave mesh often leaves homeowners blind to routing hops, sleepy battery devices, and firmware bugs; Z-Wave JS UI solves this by delivering a comprehensive browser control panel and MQTT gateway for your USB or network Z-Wave controller. Provision new devices with SmartStart QR scanning or S2 authenticated inclusion, inspect every Command Class parameter, and push over-the-air manufacturer firmware updates straight to switches and sensors. Interactive network topology graphs map live routing neighbors, link quality, and background RSSI signal strength, while built-in health checks and an integrated Zniffer packet analyzer pinpoint RF interference before automations fail. Operators can configure direct node-to-node association groups and multicast broadcast groups so wall switches trigger lights even when the central hub is offline. Scheduled Non-Volatile Memory controller backups and pre-inclusion restore points protect your mesh against hardware failure, and the configurable MQTT Discovery and WebSocket server bridges every entity seamlessly into Home Assistant, OpenHAB, Domoticz, Jeedom, and ioBroker. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
DumbAssets
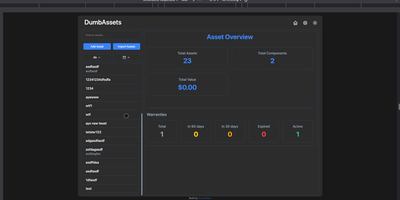
DumbAssets delivers a deliberately simple physical asset tracker that does exactly one thing well — keeping tabs on everything you own, from server racks down to individual HDDs, with hierarchical component nesting that mirrors real-world organization. The Node.js backend stores all data in JSON files within a single /data directory, making backups trivial with one folder copy while the PWA-enabled frontend provides responsive access from any device with light and dark theme persistence. Assets track model numbers, serial numbers, purchase dates, warranty expiration dates, and custom descriptions while sub-components nest infinitely — attach a Dell R730 to your server rack, then attach individual drives, CPUs, and NICs to that server with separate warranty and maintenance schedules for each. The Apprise notification engine fires configurable alerts for warranty expirations and maintenance events with direct links back to the specific asset in the web interface. Photo uploads attach visual records to any asset, receipt storage keeps purchase documentation alongside the item it covers, and a flexible tagging system enables cross-cutting organization beyond the hierarchy. PIN authentication with brute-force protection secures the interface, while search covers names, models, serials, and descriptions with sorting by warranty status, tags, components, or alphabetical order. Deploy with a single Docker command mapping port 3000 and one data volume. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL v3 licensed.
Journiv
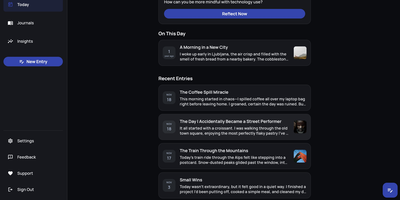
A Day One alternative that keeps your most personal writing on your own server: Journiv is journaling purpose-built for self-hosters. The FastAPI backend runs on SQLite by default with optional PostgreSQL, Redis, and Celery for background work, behind a clean, minimal web UI. Unlike general note-taking apps, it ships the features journaling actually needs: customizable moods and mood groups, activity tracking, goals with automated progress from logged activities, and daily writing prompts filterable by category and difficulty so a blank page never stalls you. Quick Log captures a moment in seconds and expands into a full entry later; "On This Day" resurfaces entries from past weeks, months, and years. Multiple journals separate work, gratitude, and personal writing, with tags and full-text search across everything, plus media uploads with automatic thumbnails and an Immich integration for linking photo-library memories. Analytics chart mood trends and writing patterns over time. Data portability is taken seriously: native import of Day One exports, JSON/Markdown/HTML export, and a standalone HTML viewer that opens your archive in any browser with no server running. OIDC single sign-on works with Authentik or Keycloak, and multi-arch images cover amd64 and arm64.
Distr
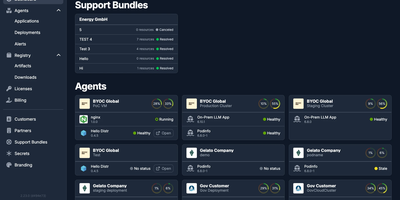
Shipping commercial software to customer-managed infrastructure demands a reliable distribution hub, and Distr provides that control plane for vendors who sell into VPCs, on-prem data centers, and air-gapped networks. Vendors define Docker Compose, Docker Swarm, or Helm applications with versions and configuration templates, then roll releases out to every customer deployment from a single vendor portal. Prebuilt deployment controllers installed in customer environments apply updates and report status, container logs, live host metrics, and alerts back, so support teams can diagnose problems without touching anyone's infrastructure. Customers get a white-labeled portal with your branding, install instructions, registry credentials, version management, and customer-initiated support bundles. A built-in OCI registry distributes Docker images, Helm charts, Zarf packages, and other artifacts with per-customer tag access, pull-through caching, and download analytics showing which customer pulls which version. Entitlements control which application versions each customer may deploy, and Ed25519-signed JWT license keys let your own software verify usage limits offline, which keeps licensing working in air-gapped sites. An OpenTofu controller provisions and reconciles BYOC cloud infrastructure, while a REST API and SDK automate onboarding, releases, and entitlements from CI pipelines. Role-based access control manages permissions across vendor and customer organizations, while the Kubernetes compatibility matrix and vulnerability scanning help validate releases before they ship. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
OnGrid
When an alert fires, OnGrid investigates it for you: an AI operations agent that correlates metrics, logs, traces, and topology, then names the root cause in plain language. A coordinator agent hands each question to specialist SRE, network, or database sub-agents, and the incident investigator walks the service graph for blast radius, queries Prometheus, Loki, and Tempo, and pins the cause to a line of source code before posting its report back to chat. Lightweight edge agents on every host dial out over a single tunnel, so no inbound ports are opened, and operators can reach any machine through an audited browser shell. The agent works through more than 26 read-only inspection tools in a sandbox, while anything that changes production waits behind an approval gate. Ask questions or receive reports in Slack, Telegram, Larksuite, DingTalk, or WeCom, and run it on Anthropic, OpenAI, GLM, DeepSeek, Gemini, Kimi, or any OpenAI-compatible endpoint. A workflow builder turns triggers, agents, tools, and notifications into repeatable automations, and a knowledge vault indexes runbooks, incident history, and repositories for search. Enroll Kubernetes clusters to inspect workloads and manage upgrades, or discover network neighbors, verify them over SNMP, and map them into the topology. Role-based access separates admins, users, and viewers. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Gerrit Code Review
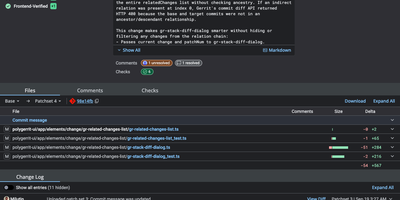
Unlike pull-request forges, Gerrit reviews every Git change as a series of patchsets, and nothing merges until the required approvals are in. Developers upload with a plain git push to a refs/for ref, adding push options for topics, hashtags, work-in-progress, or private changes. Each change gets a page listing reviewers, CCs, an attention set that flags who must act next, and submit requirements driven by labels such as Code-Review and Verified, with a quick approve button for the last missing vote. Side-by-side diffs with syntax highlighting take inline comments written in Markdown, saved as drafts and published together. A Checks tab shows CI runs reported by plugins, and integrations reach Jenkins, GitHub Actions, Zuul, and webhooks. Access rights attach to groups and branch patterns, including regular expressions, and inherit from parent projects and All-Projects. Sign-in works with LDAP, OAuth, OpenID, or HTTP single sign-on, and SAML through a plugin. A query language filters changes by status, owner, reviewer, label, file path, and reviewer count. Projects pick a submit strategy: merge if necessary, fast forward only, rebase if necessary, rebase always, merge always, or cherry pick. A REST API, SSH commands, and a plugin system extend the server, and an optional Review Agent chat panel can summarize a change once an AI provider plugin is installed. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Websurfx
Websurfx aggregates results from multiple search engines into one private, ad-free interface that never tracks your queries. Written in Rust, the backend provides memory safety against buffer overflows and data races at the language level while handling concurrent requests across upstream providers like DuckDuckGo and Searx. A built-in re-ranking algorithm scores and merges results by relevance, producing a unified page that draws from many sources while appearing as one coherent search. Safe-search filtering operates across four levels from unrestricted to complete content blocking, with regex-based filter lists for parental controls in schools and organizations. Upstream requests route through configurable proxy chains or Tor, preventing search providers from correlating your queries with a specific IP address. Four Docker image variants target different caching strategies: hybrid Redis plus in-memory for maximum throughput, Redis-only, in-memory-only, or zero-persistence for environments where cached queries must never touch disk. The Lua configuration file controls engine selection, request timeouts, rate limiting thresholds, and production-mode delays that throttle upstream traffic to prevent abuse. Quick-result widgets handle calculations, currency conversions, and unit transformations inline without external redirects. Image search capabilities serve visual discovery for designers and researchers who need media results without surveillance. Runs on a RepoCloud VPS with dedicated resources and full root access. AGPL-3.0 licensed.
Agentic SOC Platform
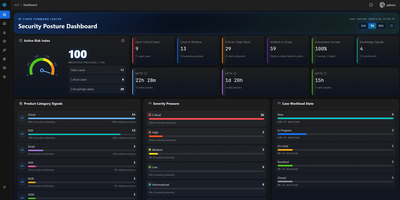
Agentic SOC Platform compresses hours of manual security analysis into seconds by deploying specialized AI agents that autonomously triage, investigate, and enrich security alerts. The Python/Django backend processes SIEM webhooks through Redis Streams into a modular pipeline where LangGraph-orchestrated agents extract IOCs, correlate signals, and generate Cases with severity, confidence, impact, priority, and structured verdicts. The built-in SIRP provides full case management with Alerts, Artifacts, Enrichments, Tickets, and a Knowledge base that accumulates institutional memory for both human analysts and LLM agents. Native Splunk and Elasticsearch/Kibana integrations deliver unified log search through a standardized interface so agents and analysts share identical security context. The playbook engine combines traditional SOAR automation with AI-powered investigation — launching threat hunting agents, knowledge extraction, threat intelligence enrichment, and CMDB lookups from a single orchestration layer. MCP Plugin support exposes ASP capabilities to Claude Code, Codex, and OpenCode, enabling external AI agents to operate cases, search logs, query threat intelligence, and write custom modules directly. Python Modules adapt new alert sources while Playbooks orchestrate LLM analysis and automated response actions, scaling the platform with your security scenarios. Deploy via Docker Compose with all data staying inside your network. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Swetrix
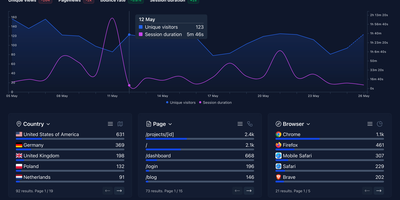
Traffic analytics, real-user performance monitoring, and client-side error tracking - normally three tools - in one cookieless, privacy-first dashboard: Swetrix. The Community Edition ships the same core engine as the cloud product - a NestJS API with ClickHouse for high-volume event storage, MySQL for relational data, and Redis for caching, fronted by a React dashboard and a ~5 KB tracking script with official packages for 20+ frameworks including Next.js, WordPress, and Shopify. Traffic analytics cover pageviews, referrers, UTM campaigns, geolocation, sessions with page flows, funnels, and custom events - all anonymized server-side with no cookies, no cross-device tracking, and no consent banner required for GDPR compliance. Performance monitoring records real-user metrics per pageview: TTFB, DNS and TLS timing, and render times, so regressions surface in the same place as traffic. Error tracking captures unhandled JavaScript exceptions automatically with formatted stack traces, filename/line metadata, affected browsers and pages, first/last-seen timestamps, and a resolve workflow - replacing a separate error monitoring subscription for many teams. Alerts fire to email, Slack, Telegram, Discord, or webhooks on traffic spikes, new errors, and custom events. If Plausible covers your traffic questions but you also want to know why the site broke, Swetrix answers both.
Vvveb
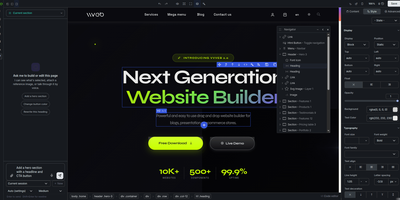
Vvveb, an open-source CMS with a drag-and-drop page builder and a built-in store, runs a blog, a portfolio, and a webshop from one dashboard, with every page edited visually on a true WYSIWYG canvas. Reusable blocks, page revisions, a code editor, and an optional AI assistant plugin sit alongside media management, custom fields, custom posts, and custom products that shape content well beyond plain pages. The store handles one-page checkout, subscriptions, digital downloads, vouchers, coupons, product options, attributes, variants, reviews, and Q&A across multiple payment methods and currencies. Content can be published in several languages, the admin interface switches with language packs, many sites or subdomains share one installation, and action-level permissions are assigned to each user role. A bundled SEO plugin generates sitemaps, robots.txt, Open Graph tags, hreflang links, and schema markup, and hybrid headless mode serves the same content to any frontend through GraphQL and REST endpoints. A randomized admin login URL, two-factor authentication, brute-force defenses, and a built-in integrity check guard the dashboard, and manual or automatic backups plus import and export tools cover recovery and migration. Any HTML template converts into a theme in minutes, a demo importer loads sample content for a fast start, and plugins and themes install with one click from the admin dashboard. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
HomeGallery
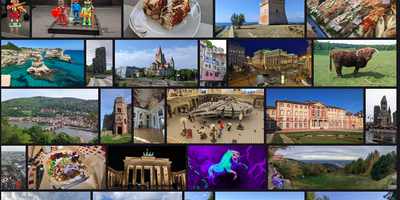
HomeGallery turns the photo and video folders on your server into a mobile-friendly web gallery. Your files and folder structure stay exactly as they are. Point it at camera files, phone files, or offline drives, and previews and metadata are extracted once. Scroll one endless stream, newest first. Open any image for its file name, dimensions, capture date, source paths, camera settings, street address, tags, and detected objects. Swipe between photos, then pinch or double-tap to zoom. The Map view clusters photos by place, with counts. The plant button lists similar images, so one sunset finds every other sunset. Face search finds the same person in other photos. A search box accepts expressions like tags in (vacation, family), type:video year in [2015:2020] order by duration, or not exists(geo). In Edit mode, select many photos at once and type comma-separated tags; a minus prefix removes one. Videos are transcoded for playback. Renamed or moved files keep their previews. An archive disk can stay unplugged once indexing is done. Optional logins limit each user to a query filter. Install it as a PWA for a lightweight mobile app. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Peekaping
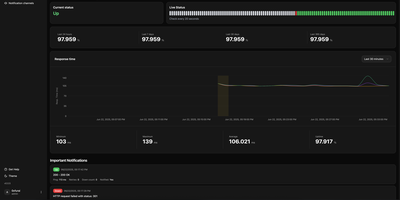
Keep users ahead of outages by consolidating infrastructure monitoring into Peekaping, a unified uptime monitoring and incident communication platform that alerts engineering teams to network and application failures before customers experience disruptions. Users can configure automated synthetic checks across HTTP endpoints, database engines, message queues, and container runtimes to verify response latency, payload integrity, and SSL certificate expiration. When performance thresholds degrade or connections drop, the platform broadcasts structured incident notices across twenty-two notification channels including Slack, Discord, Telegram, PagerDuty, and custom webhooks. Visual dashboards display live heartbeat timelines, historical latency percentiles, and rolling availability scores for each monitored endpoint. System administrators can assemble custom public status pages with custom domains, branded color schemes, and component grouping to inform external stakeholders during planned maintenance or unforeseen service degradations. Teams can schedule recurring maintenance windows to pause alert notifications during routine deployments and generate API tokens to automate monitor creation directly from CI/CD deployment pipelines. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
LeafWiki
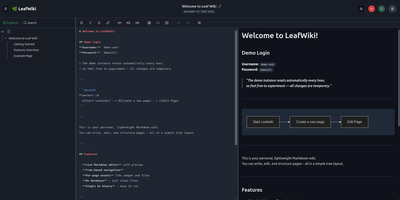
Engineering teams and technical writers maintain operational runbooks, system documentation, and knowledge bases using LeafWiki, an open-source self-hosted wiki that stores page contents directly as human-readable Markdown files on the local filesystem. Authors can compose documentation through a dual-pane editor equipped with live HTML preview, keyboard navigation, autocomplete for internal links, and native rendering for Mermaid diagrams, KaTeX mathematical formulas, and collapsible callout containers. The navigational tree organizes complex documentation into explicit directory hierarchies and custom drag-and-drop page sequences tracked in lightweight configuration files rather than arbitrary alphabetical lists. An integrated SQLite engine indexes page content and custom taxonomy tags for fast full-text searches, automatic incoming backlink tracking, and automated broken link detection. System operators can deploy the single-binary application without external database servers or runtime dependencies, backing up the entire repository by copying the data directory. Administrators can provision granular user roles, configure reverse proxy header authentication for single sign-on gateways, and manage read-only API access keys for automated documentation scripts and continuous integration pipelines. Public viewers can browse technical notes without authentication or switch between dark and light high-contrast themes. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Artifact Keeper
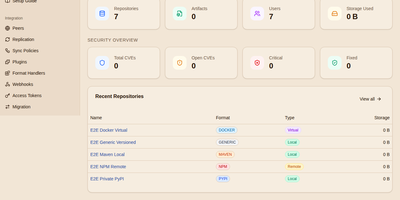
Artifact Keeper serves as a self-hosted universal software artifact repository that consolidates container images, application libraries, and infrastructure bundles under a unified management control plane. Software development teams can publish and resolve dependencies using their existing build tools, including Docker, Helm, npm, PyPI, Maven, Cargo, NuGet, and Terraform without installing proprietary client plugins. Remote repositories act as transparent pull-through caching proxies for public upstreams like Docker Hub and PyPI, accelerating internal CI/CD build speeds while insulating production pipelines from external registry outages. Virtual repositories combine multiple local, remote, and third-party endpoints into single URLs, resolving packages across prioritized internal teams and public registries automatically. Automated security scanners evaluate incoming packages for Common Vulnerabilities and Exposures using Trivy and Grype engines, assigning letter grades and enforcing quarantine policies to block vulnerable binaries before production release. Administrators can sign package metadata with cryptographic GPG keys, configure peer mesh replication across geographic regions, and manage team permissions using OpenID Connect, SAML, and granular access tokens. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
PigeonPod
To listen to your favorite YouTube channels, video playlists, and Bilibili creators during a commute without keeping a browser tab open, PigeonPod converts video subscriptions into private, standard podcast RSS feeds for any podcast player. Paste a channel URL, playlist link, or single video address to preview uploads and generate a protected feed for Apple Podcasts, Overcast, Pocket Casts, or AntennaPod. You can select audio-only or video output, customize bitrates and formats, and generate Podcasting 2.0 chapter markers for topic scrubbing. Scheduled background sync jobs fetch new releases automatically while on-demand history backfill queues older catalog episodes in bulk. Per-feed keyword rules, duration thresholds, and retention limits keep storage clean by filtering out shorts or marathon livestreams. Upload YouTube or Bilibili cookies for member-only streams, route traffic through custom proxies, and update the yt-dlp engine directly inside the web dashboard. A built-in web player, one-click public episode share pages, and OPML export let you stream in the browser or migrate subscriptions. Media files store on local disk or S3-compatible buckets such as Cloudflare R2 and MinIO, accompanied by YouTube API quota monitors and failure alerts. Multi-user role permissions support shared accounts across eight interface languages. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL-3.0 licensed.
Tracely
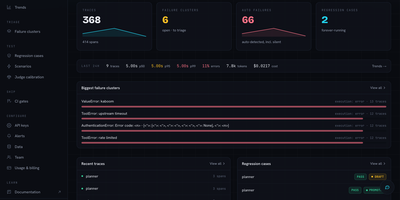
When an AI agent breaks in production, Tracely freezes that exact run into a replayable regression test and blocks the pull request that would ship the bug again. Span soup hides the failure. OTLP/HTTP traces group into conversation threads, and a waterfall marks the failing span in red with its input and output. Nobody knows if an answer was good. Evaluators sit as columns on the trace table, mixing model-free checks with LLM judges at conversation, run, or span level. Thirty-one broken runs, one issue. Clustering turns them into a single counted issue and can suggest the evaluator that would have caught it. A fix nobody can prove. One click promotes a failing trace into a hermetic case with recorded fixtures and a fail-to-pass contract, and scenarios send a red-team model after an adversarial goal. Model bills on every CI run. The suite replays offline with no API keys and no model spend, and tracely gate posts a commit status, comments on the pull request, and blocks regressions. No warning when it breaks again. Alert flows drawn on a canvas react to failed gates, broken conversations, unseen failure modes, or rising failure rates by messaging Slack, sending email, calling a webhook, or prompting an LLM. Coding agents can read traces and write evaluators through an MCP endpoint. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.