
Stars
Forks
Watchers
Developer links
Xalgorix
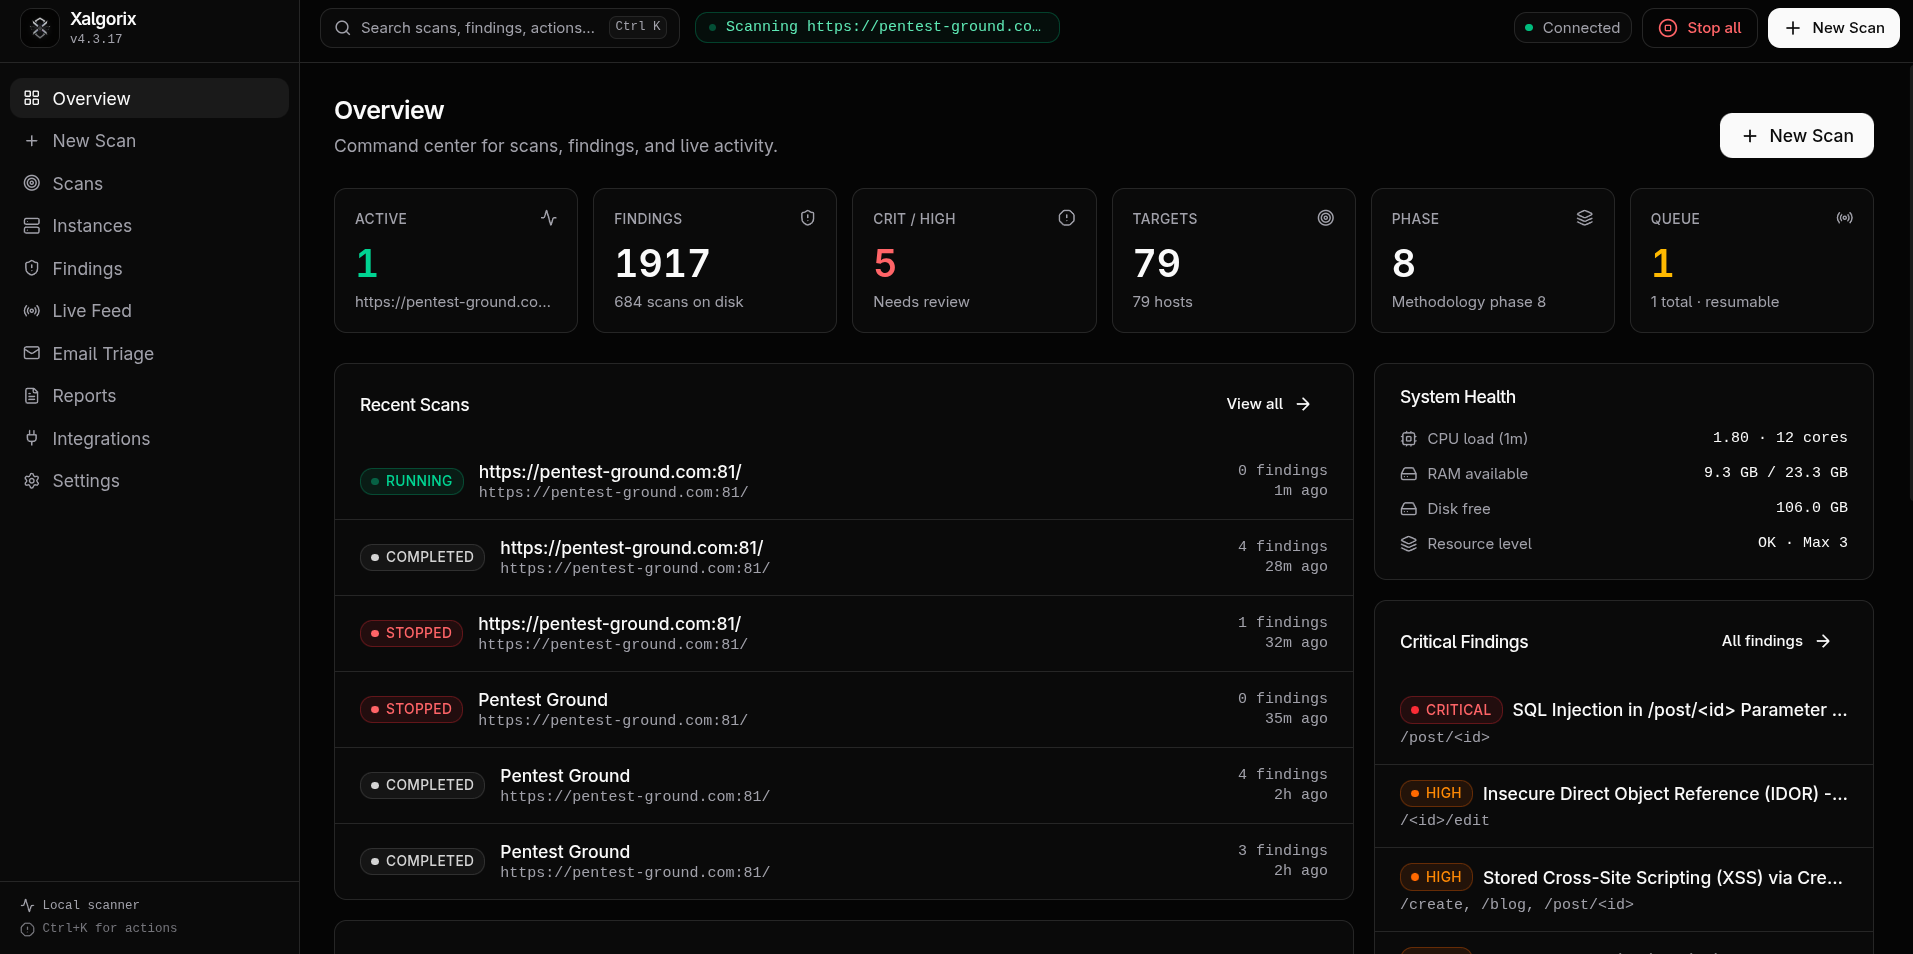
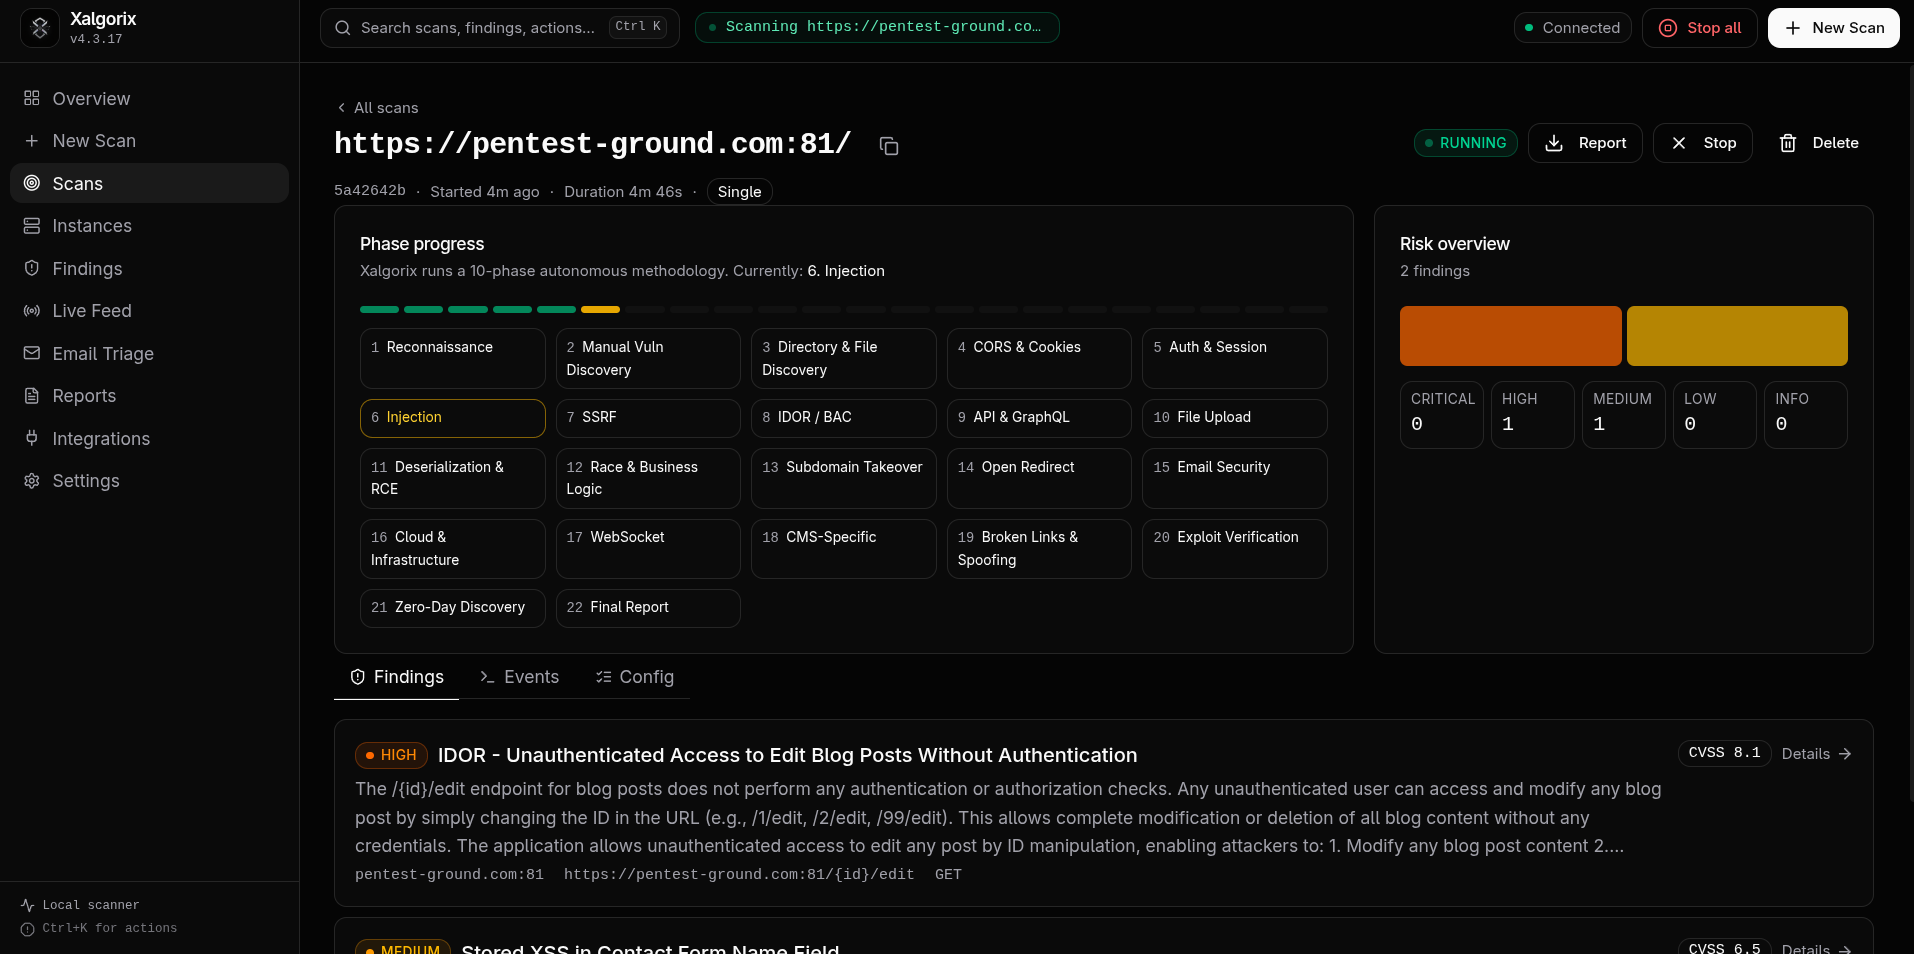
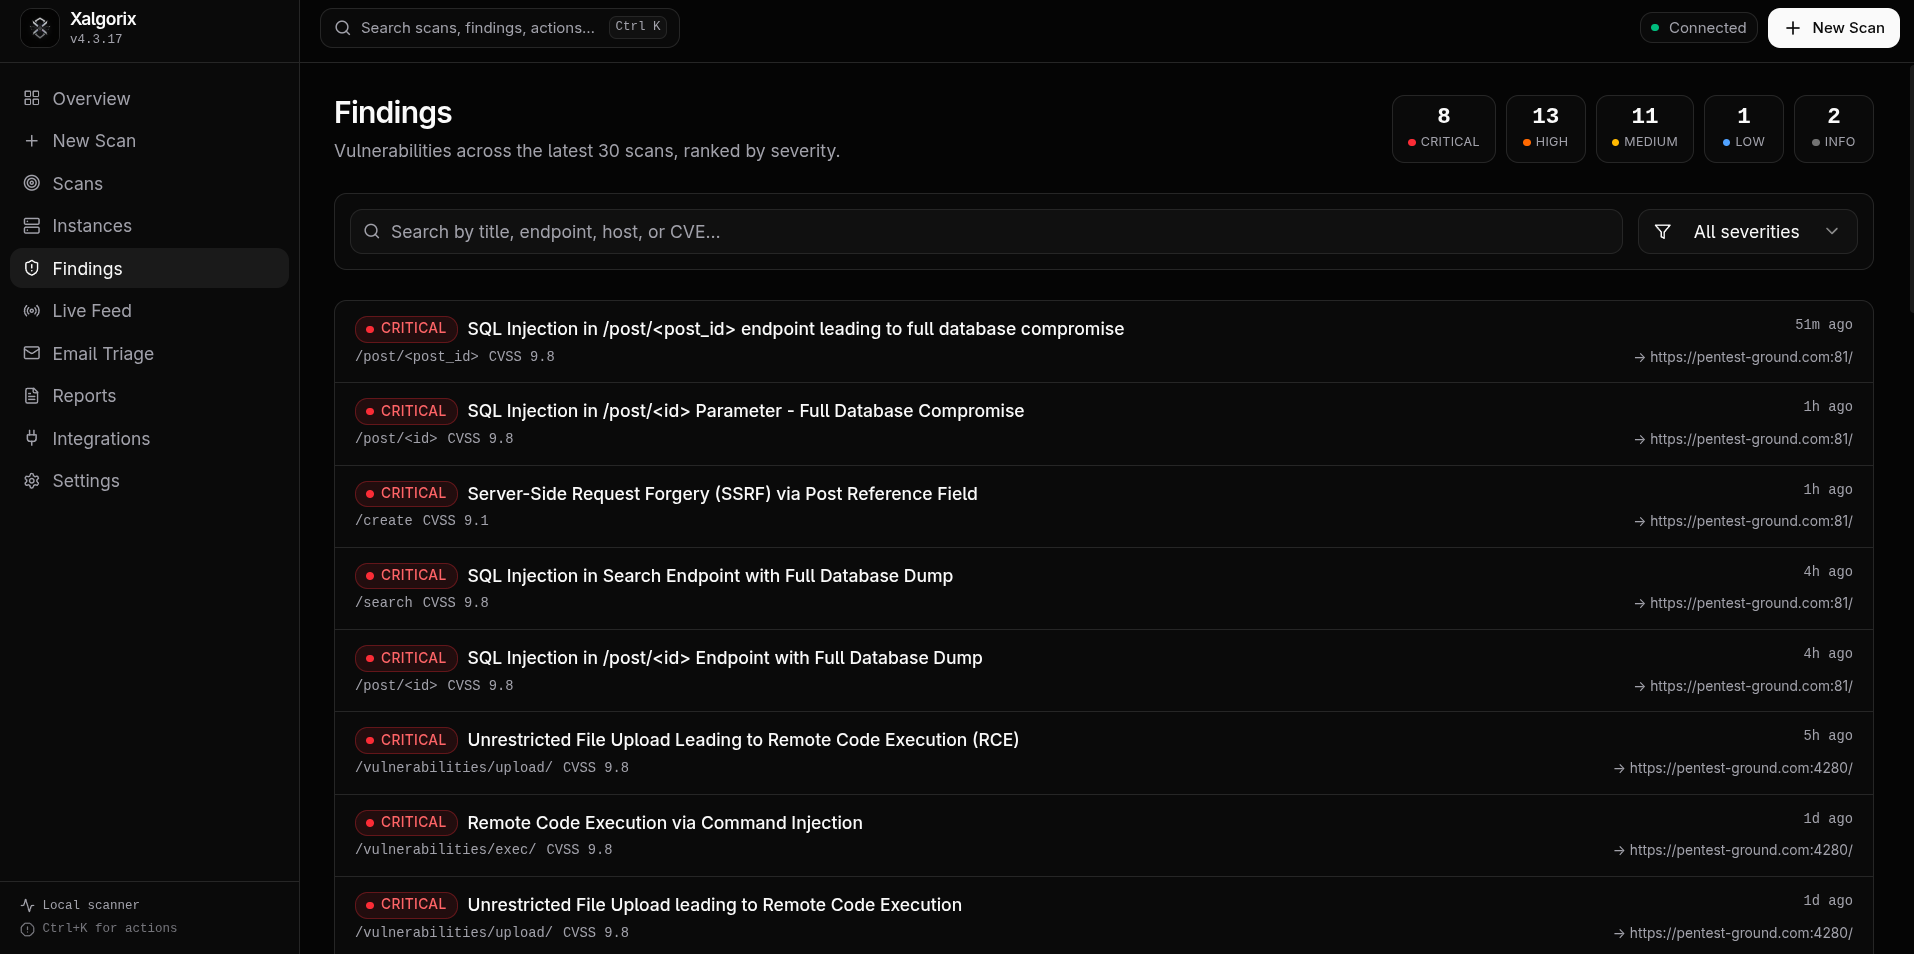
Xalgorix delivers AI-driven penetration testing that proves vulnerabilities exist rather than guessing, pairing an autonomous LLM agent with an independent exploit verifier that re-exploits every finding before it reaches your report. The 22-phase methodology mirrors how a skilled human pentester works through an engagement, covering reconnaissance, subdomain enumeration, port scanning, web crawling, parameter fuzzing, SQL injection testing, XSS detection, authentication bypass, API testing, and more. Select all phases or pick specific ones per target. The platform ships with 85+ offensive security tools preinstalled (nmap, nuclei, httpx, subfinder, katana, ffuf, gobuster, sqlmap, masscan, dalfox, feroxbuster) plus 14 built-in agent tools for browser automation, terminal execution, and note-taking. Connect your own LLM provider (OpenAI, Anthropic, DeepSeek, Gemini, Groq, Ollama, or MiniMax) so no scan data or target information leaves your infrastructure. The web dashboard on port 9137 provides live WebSocket telemetry showing tool calls, agent reasoning, and findings as scans progress. A findings index with CVSS scoring and severity filters organizes results, and branded PDF reports include your company name and logo. Wildcard and multi-target scans handle red team attack-surface mapping, while source-code scanning audits repositories directly without requiring a deployed target. A REST API enables scripted scans and SIEM pipeline integration, and webhooks push notifications to Discord or Telegram. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Benefits
- Proven Exploits, Not Theoretical Alerts
- An independent verifier re-exploits every finding after the primary agent discovers it, confirming that vulnerabilities are genuinely exploitable before they appear in your report. No more false-positive triage.
- 22-Phase Methodology Like a Human
- From reconnaissance and subdomain enumeration through SQL injection, XSS, authentication bypass, and API testing, the full engagement mirrors professional pentester workflows with selectable phases per scan.
- 85+ Security Tools Preinstalled
- Ships with nmap, nuclei, httpx, subfinder, katana, ffuf, gobuster, sqlmap, masscan, dalfox, and feroxbuster ready to run. Missing tools auto-install at runtime when enabled.
- Complete Data Sovereignty
- Bring your own LLM provider from OpenAI, Anthropic, DeepSeek, Gemini, Groq, Ollama, or MiniMax. No scan data, API keys, or target information ever leaves your infrastructure.
Features
- Live WebSocket Telemetry
- The dashboard streams tool calls, agent reasoning steps, findings, and errors in real time as scans progress through the 22-phase methodology.
- Branded PDF Reports
- Generate professional reports with your company name, logo, and target details. Findings include CVSS scoring, severity classification, and exploitation proof.
- Source-Code Scanning
- Audit repositories directly without a deployed target. Provision mode builds and runs applications locally before pentesting the live instance.
- REST API for Automation
- Script scans, query findings, download reports, and build SIEM pipelines through the documented REST API served on the dashboard port.
- Multi-Target Attack Surface
- Wildcard and multi-target scan modes map attack surfaces across domains and subdomains for red team engagements and bug bounty programs.