OpenBot
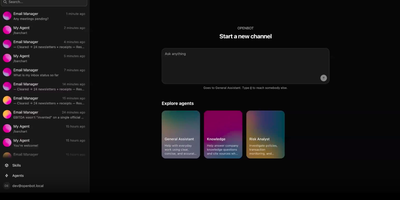
Open source GrokBot, built by the team behind the AG-UI protocol. OpenBot is the open-source enterprise agent platform that gives every AI coworker its own sandboxed computer — a real Chromium browser with its own login sessions, a private filesystem, and only the MCP tools you explicitly grant. The centralized gateway evaluates CEL policy rules against tool name, intent, bot identity, page URL, element attributes, and file paths before any action executes, writing an immutable audit row for every call and outcome. Any agent that speaks AG-UI — LangGraph, Mastra, CrewAI, Pydantic AI, Google ADK, or hand-written endpoints — registers as a Bot and receives its own channel with persistent conversation history. The take-the-wheel system lets humans assume control when an agent encounters login walls or two-factor prompts, recording control transfers as structured audit events. Knowledge documents from Google Drive and OneDrive carry source-based permissions where deny principals always win and ambiguous mappings refuse retrieval entirely. The React and Vite frontend provides live screen viewing of each agent's browser, channel-based chat, admin settings, and component galleries. The Hono API server on port 3001 handles authentication, role-based access, tenant packaging, and credential management backed by PostgreSQL with pgvector. Deploy via Docker Compose with the included supervisor that manages per-bot computer containers. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Onyx
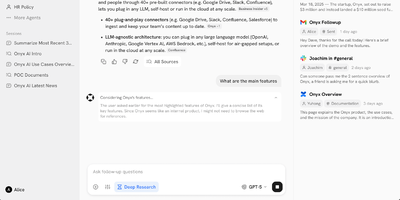
Formerly known as Danswer and now backed by over 31,000 GitHub stars with 253 releases, Onyx delivers a production-ready AI platform that turns any LLM into a context-aware enterprise assistant connected to your organization's actual knowledge. The agentic RAG pipeline combines BM-25 keyword search with prefix-aware embedding models in a hybrid index, then deploys AI agents to retrieve, verify, and synthesize answers with source citations from over 40 connected workplace tools including Google Drive, Confluence, Slack, Notion, Jira, SharePoint, GitHub, and Linear. Custom AI assistants with configurable prompts, backing knowledge sets, and document-level access control enable specialized agents for engineering, sales, support, and research workflows. The platform supports every major LLM provider — Anthropic Claude, OpenAI, Google Gemini, plus self-hosted options via Ollama, LiteLLM, and vLLM for fully air-gapped deployments. Beyond chat, Onyx provides web search with Serper, Google PSE, Brave, and SearXNG integration, an in-house web crawler, code execution, file creation, and multi-step deep research with report generation. Enterprise features include SSO via Google OAuth, OIDC, or SAML with SCIM provisioning, role-based access control, usage analytics by team and agent, query history auditing, PII removal through custom code hooks, and full whitelabeling. Deploy via Docker Compose on any infrastructure. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed (Community Edition).
Archestra
Archestra delivers the enterprise AI infrastructure layer that organizations need when managing multiple LLM providers, MCP servers, and AI agents across teams becomes unmanageable. The LLM gateway routes requests across Anthropic, OpenAI, Azure, Bedrock, and DeepSeek with virtual API keys, per-team cost limits, and dynamic model routing — giving every developer one token for Claude Code, Cursor, or Codex while finance tracks spend per department. The MCP gateway authenticates tool calls with OAuth 2.1 and On-Behalf-Of tokens so each tool executes as the calling user, not a shared service account, eliminating credential sprawl. The private MCP registry lets teams publish custom tool servers with approval flows promoting servers from dev through staging to production, each environment maintaining its own credentials and network egress policies. The Kubernetes operator manages MCP server lifecycle — deploying containers, scaling, health-checking, and routing gateway traffic to local servers automatically. The agent runtime supports scheduled triggers, email and webhook invocations, sub-agent delegation, reusable skills, and sandboxed code execution with a K8s-native filesystem. Deterministic guardrails including Dual-LLM verification and Lethal Trifecta protections prevent dangerous tool calls before execution. Built-in OpenTelemetry traces and Prometheus metrics provide full observability without additional tooling. Docker deployment exposes the Admin UI on port 3000 and API on port 9000 with a single command. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
QM
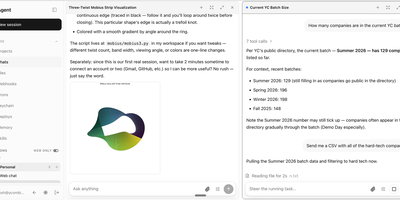
QM is Y Combinator's internal multiplayer agent infrastructure that shifts AI agents from personal assistants to shared company operating layer. The headless TypeScript core runs on Node.js with Fastify handling HTTP, Slack integration via Bolt, and a web UI built with Vite and Lit. PostgreSQL stores sessions, memory, queue state, and audit logs. Every person and every Slack channel gets an isolated sandbox with its own durable file system, installed tools that persist across runs, private memory, keychain view, permissions, and background crons. The harness-agnostic architecture routes agent tasks through Pi, OpenCode, Codex, or Claude Code without vendor lock-in, with production implementations swapping via a single wiring file. Three org-level security postures gate execution: Strict requires human approval for every tool call, Auto applies automated content screening, and Dangerous removes all pauses. Skills are scope-owned and shareable by grant, with admin-gated promotion to the entire organization and skill packs importable from Git repositories. The web apps feature lets agents spin up custom internal applications published to specific users. The qm CLI bootstraps operator-owned deployment directories with digest-pinned release images, infrastructure rendering, secret management, and live verification checks for Docker, Fly.io, or AWS ECS Fargate targets. On RepoCloud, deploy QM on a dedicated VPS with PostgreSQL persistence, Docker socket access, root SSH access, and complete control over your multiplayer agent infrastructure, all under the MIT license.
WeKnora
WeKnora turns scattered corporate documents into a searchable, reasoning-capable knowledge asset that your team can query in plain language and receive cited, sourced answers. Upload PDFs, Word files, web pages, Feishu wikis, Notion databases, Yuque docs, GitLab repositories, or RSS feeds into structured knowledge bases, and three distinct modes make the content actionable: RAG Quick Q&A retrieves relevant chunks and generates answers with source citations; the ReAct Agent autonomously orchestrates multi-step reasoning across knowledge retrieval, MCP tool calls, web search, and sandboxed code execution to produce comprehensive research reports; and Wiki Mode deploys LLM agents to distill raw documents into an interlinked markdown knowledge base with an interactive knowledge graph, revision history, and one-click rollback. Connect 20+ LLM providers including OpenAI, DeepSeek, Qwen, Claude, and local Ollama models without vendor lock-in, and choose from seven vector database backends (Qdrant, Milvus, Weaviate, and more) for embedding storage. Enterprise features include four-tier RBAC with per-resource ownership and per-workspace audit logs, AES-256-GCM credential encryption, scoped API keys, Langfuse observability tracing for every agent loop and tool call, and a runtime task-queue dashboard for worker-pool governance. Cross-session long-term memory preserves conversational context across interactions. The Agent Skills catalog lets teams install and share sandboxed scripts executed in Docker or E2B containers. A Chrome Extension captures web content directly into knowledge bases. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
OpenCloud
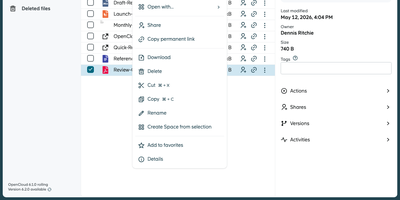
Organizations seeking complete data sovereignty over their documents, spreadsheets, and shared project folders can deploy OpenCloud as a self-hosted workspace for file sync, sharing, and real-time collaboration across web, desktop, iOS, and Android clients. Teams organize departmental assets inside dedicated Spaces where files belong to the project rather than individual user accounts, ensuring continuity when personnel change and enabling delegated space managers to assign granular read, edit, or upload permissions. Through built-in WOPI integration with Collabora Online, multiple colleagues can co-edit Microsoft Office and OpenDocument files simultaneously in the browser with automatic conflict locking and version history recovery. External partners and clients can access files via password-protected public links with custom expiration dates or upload deliverables into write-only File Drop folders without seeing existing directory contents. Cross-organization collaboration works seamlessly over the Open Cloud Mesh federation protocol, while full-text and tag-based search locates documents across personal and shared drives in seconds. Client devices synchronize changes in real time with support for virtual files on demand, resumable chunked uploads, and offline mobile access with camera document scanning. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Cloudflare OS
With over 7,700 GitHub stars and thousands of Cloudflare employees using it daily across every function, Cloudflare OS delivers an open-source AI workspace where every employee gets a personal agent grounded in company context, systems, and skills — not a generic chatbot but a programmable workspace that builds real applications, automates workflows, and connects to internal tools through governed access. The Code Mode agent writes and immediately executes code snippets to perform arbitrary tasks, build full-stack Gadgets with client code, server code, APIs, and durable SQLite state, debug errors, and test results within isolated sandboxes. Gadgets are private application instances running in separate sandboxes — each document, spreadsheet, or tool is its own secure runtime that cannot leak data even to attackers with access to other Gadgets. Blueprints enable sharing application code as templates that others instantiate with independent state, credentials, and resources. Gatekeepers provide security governance giving system owners precise control over what agents can see, change, and when human approval is required before actions execute. Built on Cloudflare Workers using Durable Objects for workspace persistence, Dynamic Workers for Gadget execution, and Facets for access management. Zero Trust security via Cloudflare Access verifies every user and request before granting access. Real-time collaboration lets colleagues use shared Gadgets. Deploy to your own Cloudflare account or self-host on workerd, the open-source Workers runtime, on your own servers. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Snipe-IT
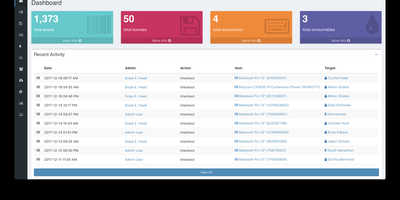
Trusted by thousands of organizations worldwide with over 14,700 GitHub stars, Snipe-IT has been the gold standard in open-source IT asset management since 2013. Built on Laravel 12 with PHP 8.2+, it provides a comprehensive web-based platform for tracking every physical and digital asset in your organization — from laptops and servers to software licenses, accessories, consumables, and components. The check-in/check-out system assigns assets to users with full audit trails, digital signature acceptance, and automated email notifications for checkouts, approaching deadlines, expiring warranties, and low inventory. License management handles multi-seat software with seat-by-seat tracking, compliance monitoring, and expiration alerts. Custom fields let you capture organization-specific metadata, while the advanced search engine supports logical operators including and/or conditions, exact matching with is:value, fuzzy exclusions with not:value, and null checks. SCIM 2.0 integration synchronizes users, groups, locations, companies, and managers from identity providers like Azure Entra ID and Okta. Enterprise authentication supports LDAP, Active Directory, Google Secure LDAP, and SAML 2.0 single sign-on. The reporting dashboard generates custom asset reports with saved templates, depreciation schedules, and audit logs. QR code labels enable instant mobile asset lookup via barcode scanners. The full-featured JSON REST API powers custom integrations, with community-built SDKs, MCP servers, and third-party mobile apps including SnipeMate and Snipe-Scan. Deploy via Docker Compose with MariaDB 11 in minutes. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Owncloud
The project that proved organizations could have Dropbox-style convenience with complete data ownership: ownCloud is the original open-source file sync and share platform - the codebase Nextcloud later forked from. This deployment runs the classic ownCloud Server (PHP over PostgreSQL or MariaDB, with Redis caching), the battle-tested edition trusted across enterprises, universities, and public institutions worldwide. The core loop: store files on your server, sync them via desktop clients for Windows, macOS, and Linux plus iOS and Android apps, and access everything through the web interface or standard WebDAV. Sharing is granular - internal users and groups, external recipients via public links with passwords and expiration dates, and federated sharing that connects separate ownCloud instances into one network. Security controls include file firewall rules, multi-factor authentication, encryption, and detailed audit-friendly lifecycle management with versioning and trash-bin recovery. An app marketplace extends the platform, and Web Office integrations bring collaborative document editing through Collabora Online, OnlyOffice, or Microsoft Office Online directly into your files. LDAP and Active Directory integration slots it into existing identity infrastructure. For teams that need a proven, self-hosted alternative to Dropbox or Google Drive - where compliance demands knowing exactly which disk your data sits on - ownCloud remains a foundational choice.
Casibase
Casibase lets organizations build AI-powered knowledge bases that answer questions from their own documents, connecting to 30+ model providers through a unified admin interface with RAG retrieval and multi-agent orchestration via MCP and A2A protocols. The platform plugs into OpenAI GPT-4o, Anthropic Claude, Meta Llama, Google Gemini, DeepSeek, Ollama local models, HuggingFace, Azure OpenAI, and additional providers, while embedding APIs from OpenAI Ada and Baidu handle vector representation of ingested documents. Document ingestion parses TXT, Markdown, DOCX, PDF, CSV, XLSX, and PPTX files with intelligent chunking strategies for optimal retrieval accuracy. The built-in chat interface provides real-time AI conversations with manual session handover for human agent escalation, and comprehensive chat session logging enables audit trails for compliance. Enterprise identity management integrates Casdoor for Single Sign-On supporting GitHub, Google, WeChat, and OIDC providers with fine-grained access control via the Casbin permission engine. The multi-tenant architecture supports isolated knowledge bases per organization with role-based user management and configurable storage, model, and embedding providers per tenant. The React frontend with Ant Design v5 provides a polished admin dashboard for managing providers, knowledge stores, chat sessions, and user access, while the Go backend with Beego framework handles API logic with MySQL or MariaDB persistence. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Kortix
Kortix Suna is an AI management system where autonomous agents run on isolated Linux sandbox computers, producing finished deliverables that humans review through a change request workflow before anything merges. With 20,000+ stars, it positions itself against Claude Cowork and ChatGPT Work by storing every agent persona, skill, memory artifact, and connector in a git repository: versioned, diffable, and shared across an organization. Each session launches a dedicated sandbox with full terminal access, Playwright-controlled Chromium, writable filesystem, and internet connectivity. Over 3,000 app connectors are available through MCP, OpenAPI, GraphQL, and raw HTTP, with credentials brokered server-side so tokens never enter the sandbox. Skills (reusable markdown-plus-script packages encoding company workflows) load automatically into every session, compounding institutional knowledge over time. Bring-your-own-key model routing through LiteLLM connects to OpenAI, Anthropic, Google, Mistral, or local models without vendor lock-in. The deployment runs as a single Docker Compose stack bundling the Next.js frontend, FastAPI backend, Supabase, Redis, and Caddy with automatic TLS certificates. Enterprise features include SAML/OIDC SSO, SCIM provisioning, RBAC, and audit logging. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Elastic License 2.0.
Astron Agent
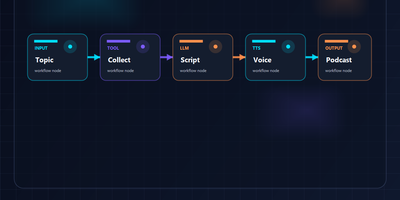
Recognized by the CNCF Landscape in the AI Agent – Workflow Orchestration category alongside Dify and Temporal, Astron Agent is iFLYTEK's fully open-source platform for building, deploying, and managing enterprise multi-agent systems — backed by 8,900+ GitHub stars and the production infrastructure behind one of China's largest AI companies. Unlike pip-install frameworks such as LangGraph, CrewAI, or AutoGen, Astron Agent ships as a complete microservices platform spanning 10+ services across Java, Python, Go, and TypeScript: a ReactFlow-based visual workflow builder for low-code agent orchestration, native integration with the Model Context Protocol (MCP) for tool calling, a built-in model management layer supporting iFLYTEK Spark, OpenAI, Anthropic, and on-premises MaaS deployments, and a multi-tenant Go authentication service powered by Casdoor. The standout differentiator is native RPA integration via the companion astron-rpa project (7,200+ stars), providing 300+ pre-built automation capabilities spanning browser, Office document, and enterprise system interaction — enabling agents to execute physical UI actions rather than only API calls. Infrastructure includes PostgreSQL for multi-tenant data isolation, MySQL for application metadata, Kafka for event streaming, Redis for caching, and MinIO for object storage, all orchestrated through Docker Compose with explicit health checks and dependency chains or production Kubernetes Helm charts. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Utopia
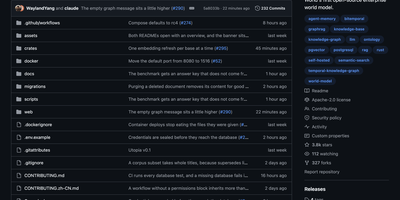
The first open-source substrate for enterprise knowledge engineering that learns passively and governs itself. The Rust-built backend paired with PostgreSQL and pgvector delivers a bitemporal knowledge graph where every fact carries two timelines: when it held in the real world and when the system came to believe it — enabling full audit trail replay of how understanding evolved. Document ingestion handles PDF, DOCX, PPTX, XLSX, CSV, Markdown, HTML, and plain text with legacy encoding detection, while scheduled syncing pulls from web pages, RSS feeds, GitHub, Jira, Notion, WebDAV, and S3-compatible buckets. Search fuses Tantivy full-text indexing with pgvector semantic vectors using Reciprocal Rank Fusion, streaming answers with inline citations that link directly to source passages. The built-in agent harness drives agentic RAG through conversation — searching documents, walking the knowledge graph at any historical date, and querying mounted databases via Ontology2SQL which achieves state-of-the-art results on BIRD Mini-Dev benchmarks. Five ontology packs ship inside the binary (schema.org, W3C Org, PROV-O, FOAF, IOF Core) with forward-chaining reasoning for transitivity, symmetry, inverses, and relation hierarchy. Entity resolution operates in three stages: exact name matching, embedding similarity, then model-based judgment with every merge reversible. Any OpenAI-compatible endpoint works including DeepSeek, Qwen, Ollama, and vLLM for fully air-gapped deployment. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
XWiki
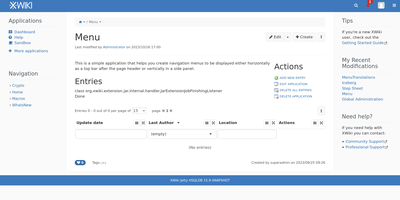
With over 140,000 code commits, 1,200+ GitHub stars, and continuous development since 2004 spanning more than two decades of active maintenance through version 18.6.0 released in July 2026, XWiki operates as a second-generation wiki platform that goes beyond static pages by enabling teams to build custom collaborative applications directly inside wiki pages using structured data forms and in-page scripting. The Java backend runs on Apache Tomcat with PostgreSQL, MySQL, or Oracle database storage, serving a responsive web interface with a WYSIWYG editor featuring real-time collaborative editing, link and macro editors, user mentions, inline comments, annotations, and complete version history with diff comparison. The App Within Minutes extension lets non-developers create custom data-driven applications using drag-and-drop form builders that generate filterable live tables for structured data browsing without writing code. Over 900 extensions from the built-in Extension Manager add functionality including blogs, task trackers, forums, diagram editors, and Confluence migration tools. Enterprise integration features include LDAP and Active Directory authentication, SAML and OIDC single sign-on, fine-grained per-page and per-space permissions with nested page hierarchies, and multi-wiki support for hosting multiple independent wikis from a single installation. The RESTful API provides programmatic access to pages, spaces, objects, attachments, and properties with XML and JSON representations. Office document import converts Word and Excel files directly into wiki pages while PDF export generates formatted documents from wiki content. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. LGPL-2.1 licensed.
Zitadel
Securing a SaaS product, running B2B onboarding, or replacing Auth0 and Keycloak with a stack they own - teams needing more than basic auth reach for ZITADEL, an open-source identity and access management platform built in Go. Its multi-tenancy model is the differentiator: a strict Instance, Organization, Project hierarchy isolates data and scopes policy at each level, with identity brokering (pre-built templates for Google, GitHub, Microsoft, Apple, plus generic OIDC, OAuth, SAML, and LDAP), domain discovery that routes users to the right organization by email domain, and delegated management so customers administer their own users and roles. Authentication covers OpenID Connect (certified, including device authorization and token exchange), SAML 2.0 as both IdP and SP, SCIM, FIDO2 passkeys for phishing-resistant passwordless login, and MFA via OTP, email, SMS, and U2F; machine-to-machine flows support JWT profile, PATs, and client credentials. The architecture is event-sourced - every mutation is an immutable event, yielding a complete audit trail - with relational projections for queries and no external session store, so it scales horizontally. API-first with gRPC and REST, extensible via Actions webhooks, and the same codebase self-hosted (Docker Compose or Helm on PostgreSQL) as in the cloud.
PipesHub
Unify fragmented corporate knowledge across chat channels, documents, and cloud drives with PipesHub, an open-source workplace context platform providing permission-aware search and verifiable answers for teams and autonomous agents. Employees can query enterprise knowledge bases through a conversational interface that retrieves relevant information across Google Workspace, Microsoft 365, Slack, Confluence, Jira, and GitHub while strictly respecting individual user access permissions. Knowledge workers can verify every answer through clickable citation blocks that trace claims directly back to source documents, spreadsheet rows, or chat messages. Teams can assemble custom AI agents visually using a drag-and-drop builder, combining retrieval collections with interactive toolsets to automate multi-step operations like drafting customer responses or creating issue tickets. Autonomous agents connect via Model Context Protocol to inspect shared company knowledge and perform external actions across connected SaaS tools. Organizations can index scanned PDFs, slide decks, markdown pages, and spreadsheets with OCR and document parsing, maintaining synchronized records through automated schedules. Administrators can inspect synchronized records, monitor query history, and manage connector credentials across all integrated business applications. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache License 2.0 licensed.
MateClaw
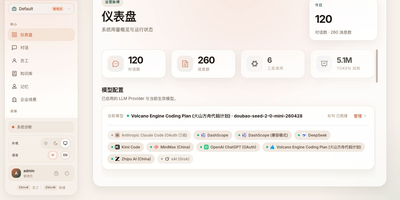
MateClaw delivers a multi-agent AI platform where digital employees run as persistent team members with roles, goals, and accumulated skills rather than stateless chat completions. The Spring Boot backend on Spring AI Alibaba provides ReAct iterative reasoning and Plan-and-Execute decomposition on a StateGraph runtime, with parallel delegation between employees and dynamic context pruning for multi-step tasks. Five career templates ship ready (Product Researcher, Customer Support, Knowledge Curator, Data Analyst, Executive Assistant) while custom employees inherit configurable backstories, pixel-art avatars, and dedicated tool bindings. The MCP integration supports stdio, SSE, and Streamable HTTP transports with per-employee tool isolation preventing capability bleed between agents. ACP bridges bring Claude Code, Codex, and other coding agents in as first-class employees. Workflow orchestration composes multiple employees and system actions into publishable linear DSL processes with seven step modes: sequential, fan_out, collect, conditional, await_approval, dispatch_channel, and write_memory. The trigger system wires cron schedules, webhooks, channel messages, employee lifecycle events, content matches, and workflow completions to automated flows. The Admin Runtime Console provides real-time visibility into running employees with token usage tracking and one-click force-recycle. Spring Boot Actuator monitoring, full audit trail, and per-channel error isolation deliver production-grade reliability. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
TeamPass
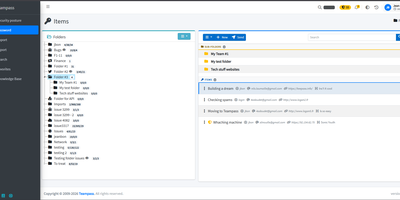
TeamPass is a dedicated on-premise password manager built specifically for teams that need collaborative credential sharing with fine-grained access controls. Role-based access control defines user permissions through hierarchical folder trees where each folder and item can be independently set to write, read, or no access against assigned roles, enabling organizations to segment credentials across departments without exposing sensitive data. Passwords are encrypted in the database using Defuse PHP Encryption with per-installation unique saltkeys, while two-factor authentication supports configurable RFC 6238 TOTP profiles with custom digits, period, and algorithm settings alongside Duo Security and Yubico hardware key integration. LDAP and Active Directory native integration enables enterprise SSO with automatic user provisioning. The Security Posture Dashboard surfaces weak, reused, breached, overdue, no-expiry, widely-shared, and unreadable credentials through indicator cards that filter and deep-link directly to items. Secure Send creates expiring, view-count-limited one-time links optionally protected by recipient passphrases for sharing credentials with external users. Import from Bitwarden, LastPass, 1Password, and KeePassXC through a unified source selector, with export to encrypted offline files. Email notifications, password expiration policies, custom fields, and attachment support round out item management. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL-3.0 licensed.