Agentic Security
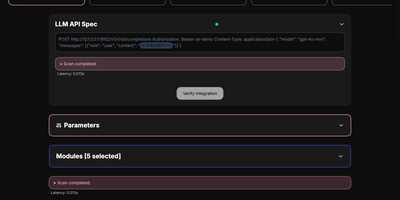
Find out how easily your chatbot can be talked into misbehaving before a stranger on the internet does. Agentic Security points a library of attack prompts at any LLM endpoint you can describe in a few lines of HTTP, then reports which attack families got through. Paste a request template with a marker where the attack goes, press Verify Integration to confirm the endpoint answers, and start the scan. Pick from jailbreak corpora on Hugging Face, obfuscation mutations like Base64, ROT13, mirrored words, and scrambled text, or drop your own CSV of prompts into a folder. Presets cover OpenAI, DeepSeek, Groq, Gemini, Claude, Azure, and custom APIs. Set a token budget, switch on concurrency, and watch a per-module table of failure rates and estimated cost fill in live. Download failed prompts as a CSV, export the full log, or generate a config and run the same scan as a CI gate with failure thresholds. Re-run the same scan after every model or system prompt change to spot regressions early. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Xalgorix
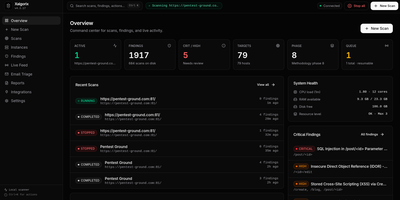
Xalgorix delivers AI-driven penetration testing that proves vulnerabilities exist rather than guessing, pairing an autonomous LLM agent with an independent exploit verifier that re-exploits every finding before it reaches your report. The 22-phase methodology mirrors how a skilled human pentester works through an engagement, covering reconnaissance, subdomain enumeration, port scanning, web crawling, parameter fuzzing, SQL injection testing, XSS detection, authentication bypass, API testing, and more. Select all phases or pick specific ones per target. The platform ships with 85+ offensive security tools preinstalled (nmap, nuclei, httpx, subfinder, katana, ffuf, gobuster, sqlmap, masscan, dalfox, feroxbuster) plus 14 built-in agent tools for browser automation, terminal execution, and note-taking. Connect your own LLM provider (OpenAI, Anthropic, DeepSeek, Gemini, Groq, Ollama, or MiniMax) so no scan data or target information leaves your infrastructure. The web dashboard on port 9137 provides live WebSocket telemetry showing tool calls, agent reasoning, and findings as scans progress. A findings index with CVSS scoring and severity filters organizes results, and branded PDF reports include your company name and logo. Wildcard and multi-target scans handle red team attack-surface mapping, while source-code scanning audits repositories directly without requiring a deployed target. A REST API enables scripted scans and SIEM pipeline integration, and webhooks push notifications to Discord or Telegram. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.