Shuffle
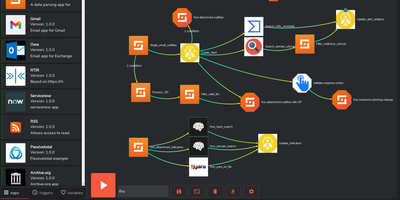
Security teams drown in alerts that all demand the same twelve manual steps. Shuffle is an open-source security orchestration, automation, and response platform that turns those steps into visual workflows: an alert arrives from the SIEM, Shuffle enriches it against threat intelligence, opens the ticket, isolates the host, and messages the analyst, without anyone copying values between browser tabs. Analysts assemble workflows on a canvas from more than two thousand pre-built app integrations covering email, EDR, firewalls, ticketing, chat, and cloud services, and any tool with an OpenAPI description can be converted into a new app automatically, exported again, and reused outside Shuffle. Webhooks, schedules, and pipeline triggers start executions; custom Python covers the odd cases; conditional branches and sub-workflows keep one big playbook from becoming spaghetti. Multi-tenancy with sub-organisations, roles, single sign-on, and MFA fits managed security providers running one deployment for many customers, and execution workers can run on premises closer to the systems they touch. Community members publish workflows and apps to a marketplace, so a phishing triage playbook that works for one SOC can be running in another by lunchtime. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Agentic SOC Platform
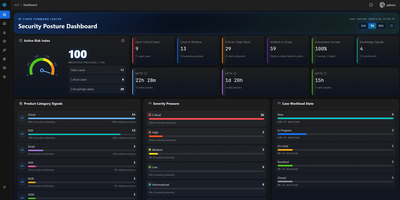
Agentic SOC Platform compresses hours of manual security analysis into seconds by deploying specialized AI agents that autonomously triage, investigate, and enrich security alerts. The Python/Django backend processes SIEM webhooks through Redis Streams into a modular pipeline where LangGraph-orchestrated agents extract IOCs, correlate signals, and generate Cases with severity, confidence, impact, priority, and structured verdicts. The built-in SIRP provides full case management with Alerts, Artifacts, Enrichments, Tickets, and a Knowledge base that accumulates institutional memory for both human analysts and LLM agents. Native Splunk and Elasticsearch/Kibana integrations deliver unified log search through a standardized interface so agents and analysts share identical security context. The playbook engine combines traditional SOAR automation with AI-powered investigation — launching threat hunting agents, knowledge extraction, threat intelligence enrichment, and CMDB lookups from a single orchestration layer. MCP Plugin support exposes ASP capabilities to Claude Code, Codex, and OpenCode, enabling external AI agents to operate cases, search logs, query threat intelligence, and write custom modules directly. Python Modules adapt new alert sources while Playbooks orchestrate LLM analysis and automated response actions, scaling the platform with your security scenarios. Deploy via Docker Compose with all data staying inside your network. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.