VictoriaLogs
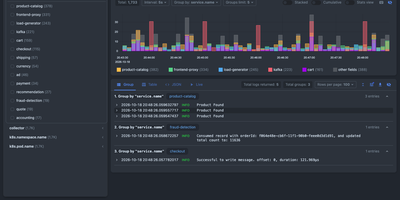
Instead of running an Elasticsearch or Loki cluster, VictoriaLogs stores and searches your logs from a single zero-config server. Ship from Filebeat, Fluent Bit, Fluentd, Logstash, Vector, Promtail, Telegraf, the OpenTelemetry Collector, or the Datadog Agent. Syslog, journald, and Splunk endpoints work too. Query with LogsQL: word, phrase, and prefix filters combine with pipes that extract fields from raw lines and compute stats, top values, and facets. See results as a table, grouped by stream, as raw JSON, or as a live tail. Chart them in Grafana, or work from a terminal with vlogscli and pipe output into grep, less, or jq. Events with hundreds of fields are supported. So are high-cardinality fields like trace_id and user_id. Late, out-of-order backfills are accepted. During an incident, stream_context pulls the lines around any match. Tenants are keyed by AccountID and ProjectID headers. vmalert evaluates LogsQL queries as alerting and recording rules. CEF messages sent over Syslog are parsed automatically for SIEM work. Retention defaults to 7 days and can be capped by disk space. Per-day partitions snapshot and copy out with rsync or rclone. Cluster mode splits ingestion, querying, and storage across nodes for logs that outgrow one server. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Deploy