
Pipelock
Your AI coding agent has your API keys in its environment and unrestricted network access, which means one prompt injection away from sending those secrets anywhere. Pipelock closes that gap by sitting as a proxy between your agents and every outbound connection, scanning the actual content of HTTP, WebSocket, MCP, and Agent-to-Agent traffic before it leaves your server. An 11-layer scanner pipeline checks every request against 62 credential patterns covering AWS, GCP, Azure, GitHub, OpenAI, Anthropic, SSH keys, and database URLs, then inspects every response for prompt injection using 29 detection patterns with six-pass normalization that catches base64-encoded, leetspeak, and whitespace-obfuscated payloads. The MCP proxy wraps any Model Context Protocol server (stdio, HTTP, or WebSocket) with bidirectional scanning that detects tool description poisoning and mid-session rug-pull changes via SHA-256 fingerprinting. Every scanning decision produces a cryptographically signed action receipt that third parties can verify offline without trusting the agent or the vendor. The Operator Console provides a web dashboard for reviewing evidence scorecards, receipt timelines, agent sessions, enforcement decisions, and fleet posture at a glance. Cross-request taint tracking catches slow-drip exfiltration attempts that spread a secret across multiple calls. Canary tokens plant synthetic secrets that trip alerts the moment an agent tries to exfiltrate them. Pre-built Prometheus metrics and a Grafana dashboard provide real-time visibility into traffic volumes and block rates. Deploy on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
DodoGuard
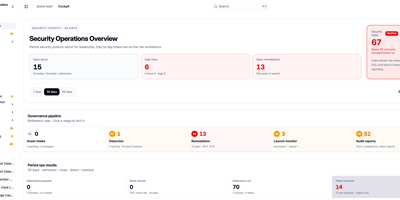
Before an AI agent meets real users, put it through a security checkup it cannot sweet-talk. DodoGuard is a web console and command line where teams register their agents, run evaluation and red-team tasks against them, and decide if each one is cleared for launch. The overview page shows a security index, open risks, remediation counts, and a pipeline that runs from asset intake through detection and remediation to launch monitoring and audit reports. An asset ledger lists every managed agent with its platform, environment, and risk level. A guided wizard creates assessment tasks that pick a test library for prompt injection, instruction leakage, tool misuse, and output risks, then runs black-box conversations against the agent. Evaluation configs cover prompts, providers, variable cases, and several assertion types, with OpenAI, Anthropic, Azure, Bedrock, Ollama, and any OpenAI-compatible endpoint supported. Findings land in a closed-loop board where owners confirm, fix, retest, and close each risk, and finished tasks export as reports for release evidence. Docker Compose with SQLite brings up the web UI on port 3000, and the same engine runs in continuous integration. Security teams use it for launch gates, platform owners use it for regression checks after prompt changes, and auditors use it for evidence. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.