Tinyauth
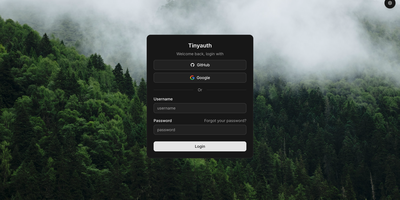
To protect self-hosted web services behind a unified single sign-on portal without deploying complex enterprise identity suites, Tinyauth acts as an OpenID Certified authentication server and reverse proxy middleware. Homelab operators and infrastructure teams place it in front of internal dashboards, media servers, and administrative tools routed through Traefik, Caddy, Nginx, Nginx Proxy Manager, or LinuxServer SWAG. Users can sign in with local bcrypt-hashed credentials, scan QR codes to enroll time-based one-time password authenticators for two-factor verification, or authenticate through external OAuth providers like GitHub, Google, and Pocket ID. Organizations running centralized directories can bind Tinyauth directly to an LDAP server such as LLDAP or OpenLDAP and automatically synchronize group memberships for role-based authorization. Fine-grained access control rules configured via dynamic Docker container labels or environment variables let administrators whitelist or block specific usernames, OAuth email regex patterns, OIDC groups, client IP CIDR ranges, and URL path prefixes per subdomain. For applications that support native federated login, the built-in OpenID Connect 1.0 discovery endpoint, authorization code flow, and userinfo API allow seamless single sign-on with optional consent skipping for trusted clients. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Authelia
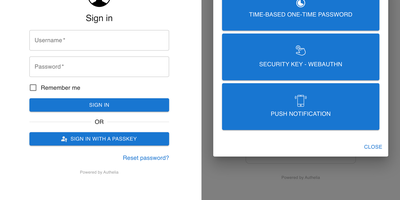
Authelia is the leading open-source SSO and multi-factor authentication server for self-hosted infrastructure. The Go backend compiles to a single binary or Docker container image, serving a TypeScript React web portal that handles first-factor username and password login, second-factor authentication via TOTP, WebAuthn FIDO2 security keys, passwordless passkeys, and Duo mobile push notifications, and an OpenID Connect 1.0 and OAuth 2.0 identity provider with device code flow, JWE encrypted ID tokens, custom claims policies, and network-scoped authorization criteria. The forward authentication model integrates with Nginx auth_request, Traefik ForwardAuth, HAProxy, Caddy, Envoy, SWAG, and Skipper reverse proxies, injecting Remote-User, Remote-Groups, and Remote-Email headers into authorized requests. Granular access control rules match subject, groups, request URI, HTTP method, and network to enforce one-factor and two-factor policies per route. The user backend supports LDAP with attribute mapping, connection pooling, and bind mode, or YAML file-based authentication with Argon2id hashed passwords. Session state stores in Redis for high availability across clustered deployments, while persistent data lives in SQLite, MySQL and MariaDB, or PostgreSQL. Brute force protection locks accounts after configurable failed attempts, and email-based identity verification handles password resets and device registration. Dark, light, and OLED themes with i18n localization customize the portal appearance. On RepoCloud, deploy Authelia on a dedicated VPS with Docker, root SSH access, and complete control over your authentication infrastructure, all under the Apache-2.0 license.
Authentik
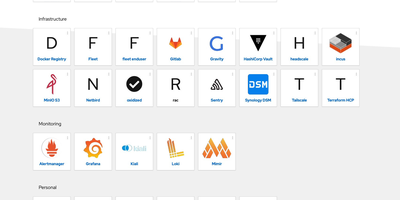
With over 24,000 GitHub stars and a rapidly growing community of self-hosters, authentik delivers enterprise-grade identity management that replaces commercial solutions like Okta and Auth0 with a fully self-hosted platform requiring no per-user licensing fees. The platform serves as a unified identity provider supporting SAML 2.0, OAuth 2.0 and OpenID Connect, LDAP for legacy application compatibility, SCIM 2.0 for automated user provisioning, and RADIUS for network device authentication. The visual flow designer enables administrators to create custom authentication workflows combining password verification, multi-factor authentication with TOTP, WebAuthn, and SMS codes, email verification, captcha challenges, and conditional logic based on user attributes or device context. The forward-auth and reverse proxy integration works seamlessly with Traefik, Nginx, Caddy, and Envoy to protect applications that lack built-in authentication. User enrollment flows support self-registration with configurable approval workflows, invitation links, and automatic group assignment. The LDAP outpost exposes user and group data to legacy applications requiring LDAP bind authentication, while the SCIM provider automates user lifecycle management with downstream applications. Multi-tenancy support through brands allows a single authentik instance to serve multiple organizations with independent domains, branding, and authentication policies. The admin interface provides comprehensive user management, group hierarchy, application catalog, event logging with GeoIP enrichment, and system health monitoring. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Licensed under a source-available license with an open-source community edition.