Stars
Forks
Watchers
Developer links
Tinyauth
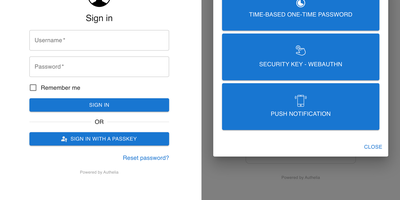
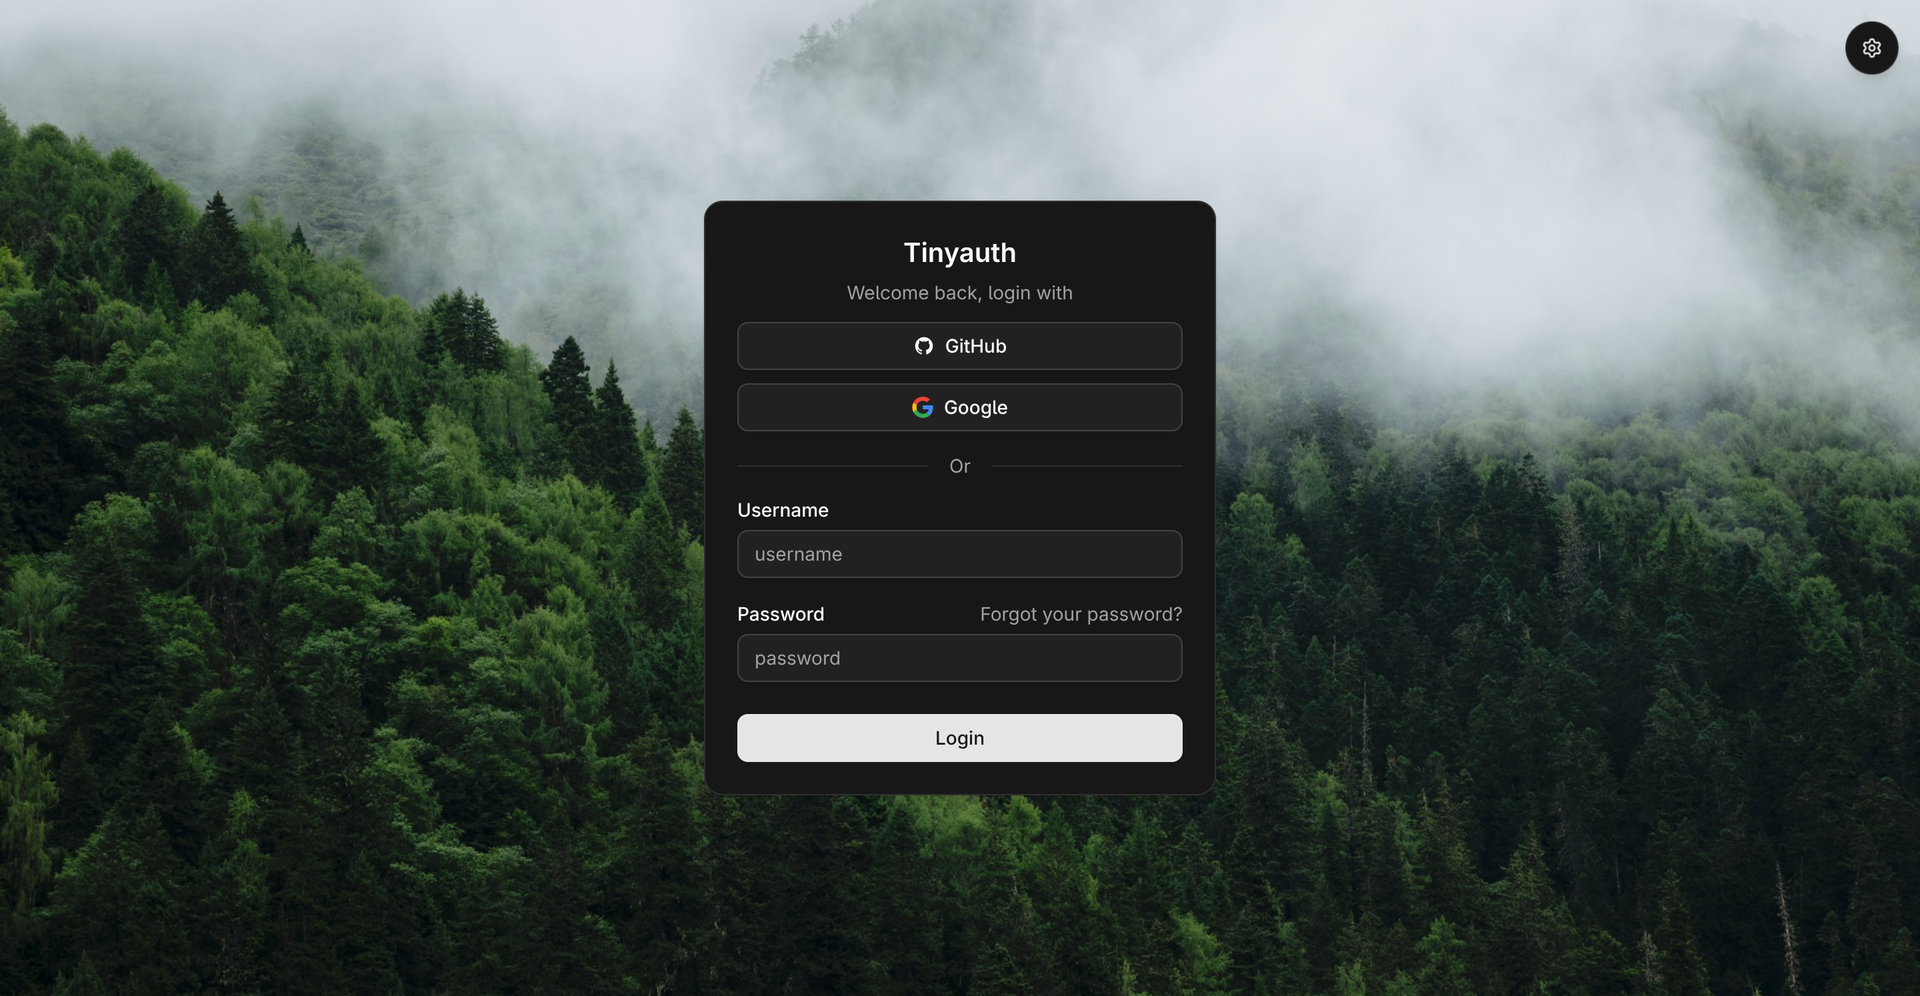
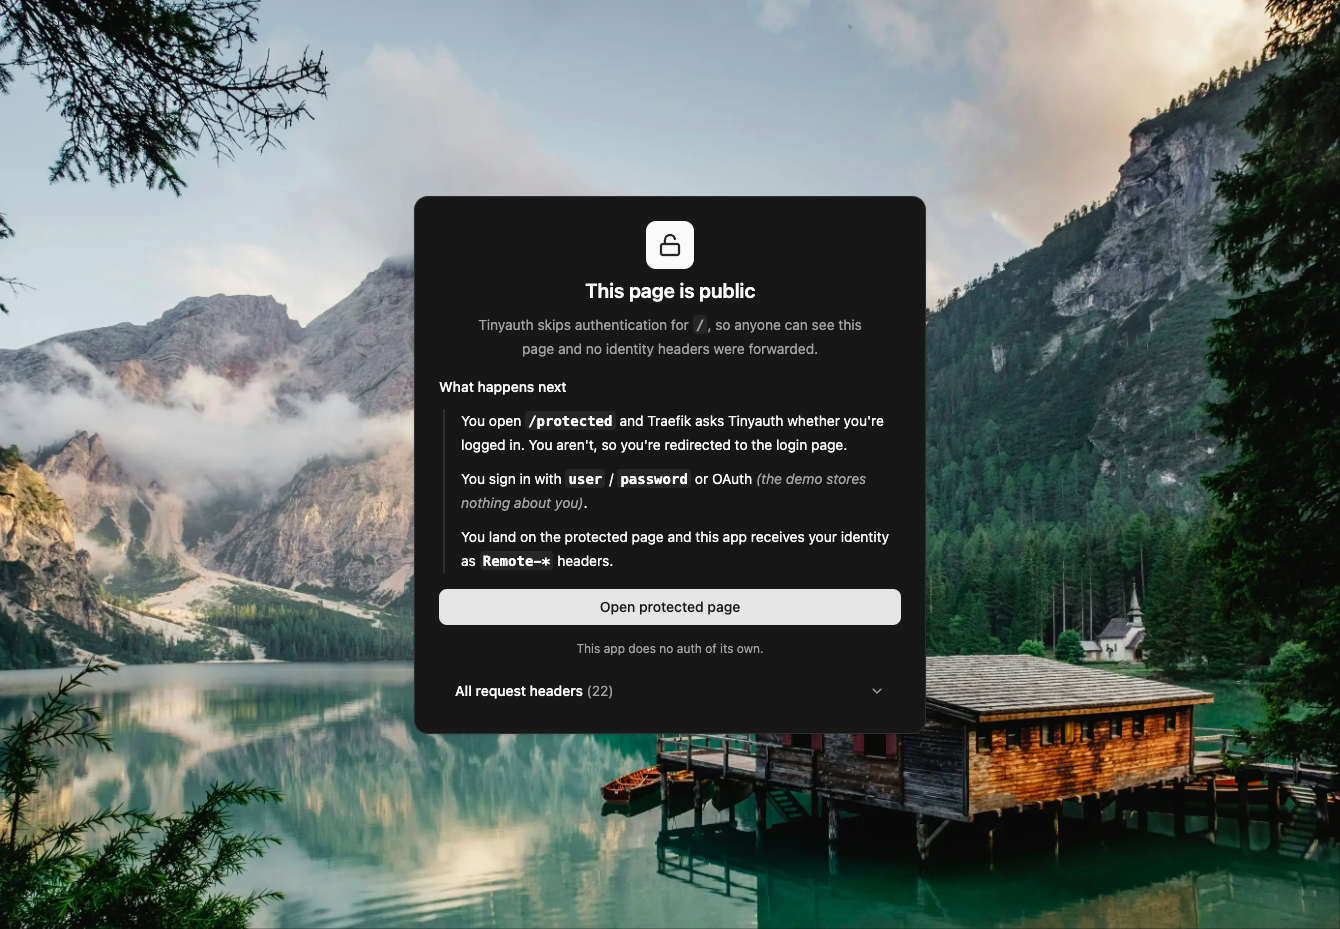
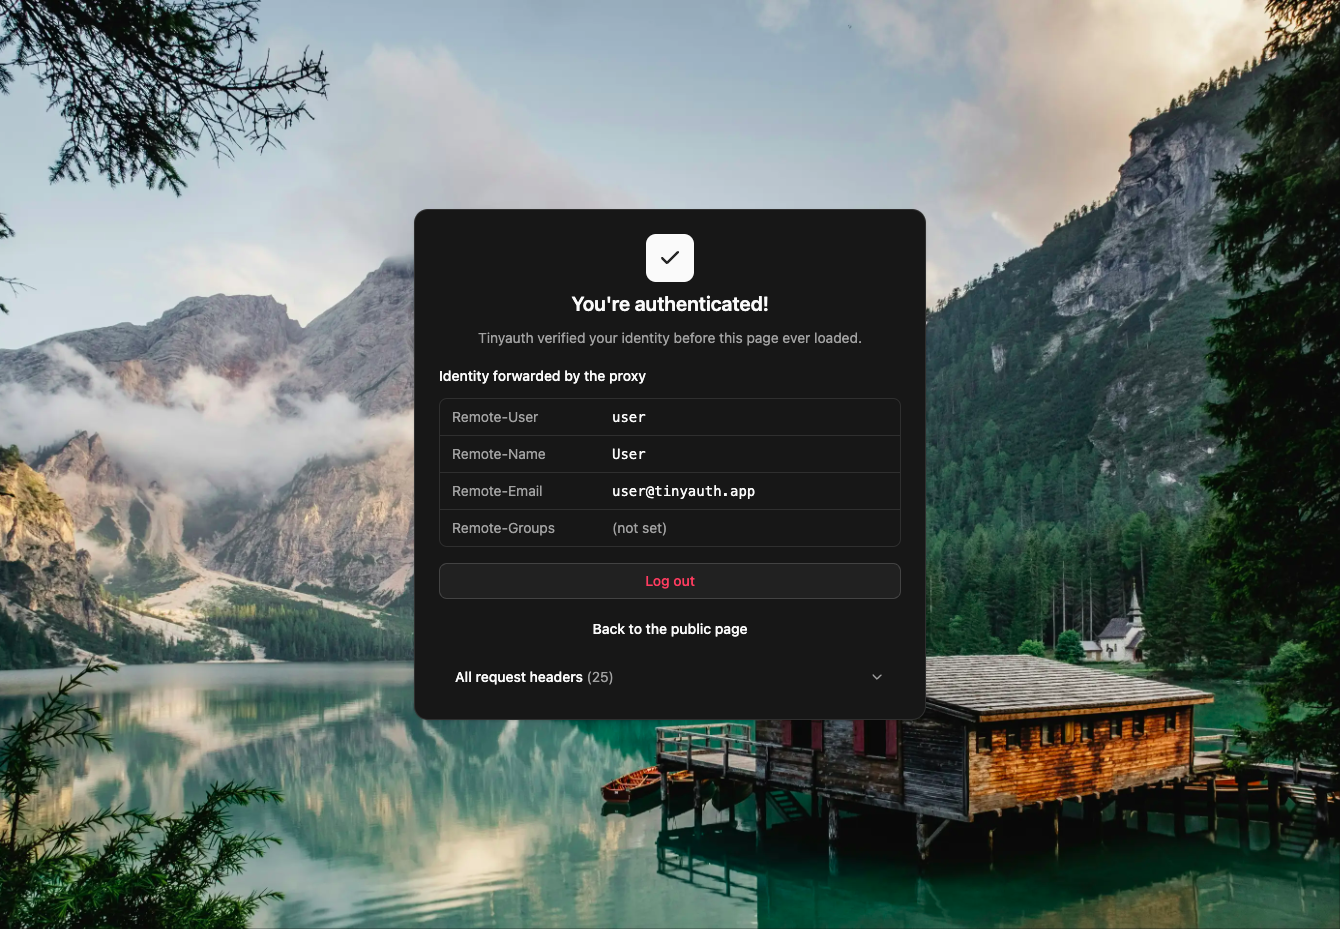
To protect self-hosted web services behind a unified single sign-on portal without deploying complex enterprise identity suites, Tinyauth acts as an OpenID Certified authentication server and reverse proxy middleware. Homelab operators and infrastructure teams place it in front of internal dashboards, media servers, and administrative tools routed through Traefik, Caddy, Nginx, Nginx Proxy Manager, or LinuxServer SWAG. Users can sign in with local bcrypt-hashed credentials, scan QR codes to enroll time-based one-time password authenticators for two-factor verification, or authenticate through external OAuth providers like GitHub, Google, and Pocket ID. Organizations running centralized directories can bind Tinyauth directly to an LDAP server such as LLDAP or OpenLDAP and automatically synchronize group memberships for role-based authorization. Fine-grained access control rules configured via dynamic Docker container labels or environment variables let administrators whitelist or block specific usernames, OAuth email regex patterns, OIDC groups, client IP CIDR ranges, and URL path prefixes per subdomain. For applications that support native federated login, the built-in OpenID Connect 1.0 discovery endpoint, authorization code flow, and userinfo API allow seamless single sign-on with optional consent skipping for trusted clients. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Benefits
- Universal Reverse Proxy Forward Auth
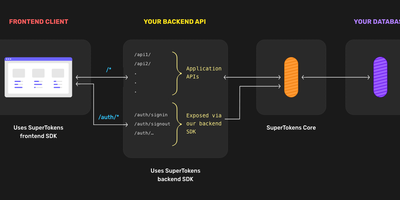
- Integrates with Traefik, Caddy, Nginx, Nginx Proxy Manager, and SWAG through dedicated forward-authentication endpoints while injecting authenticated remote-user, remote-email, and remote-groups HTTP headers into upstream requests.
- Certified OpenID Connect Identity Provider
- Complies with the OpenID Connect Core 1.0 specification and exposes automatic discovery at /.well-known/openid-configuration, authorization code and refresh token grants, and userinfo endpoints for downstream applications.
- Dynamic Docker Label Access Controls
- Evaluates per-application access control rules at runtime directly from Docker container labels, allowing administrators to restrict subdomains by username lists, OAuth email regexes, LDAP groups, or IP CIDRs.
- Multi-Factor and Directory Authentication
- Combines local bcrypt password accounts and interactive TOTP two-factor authentication with external OAuth 2.0 providers and cached LDAP group queries for flexible identity verification across self-hosted stacks.
Features
- OpenID Connect 1.0 Server
- Provides OpenID Certified Basic OP endpoints including /authorize, /api/oidc/token, /api/oidc/userinfo, and automatic discovery for native OIDC client integration.
- Docker Label ACL Engine
- Parses tinyauth.apps container labels dynamically to enforce user allowlists, OAuth email whitelists, IP subnet bypasses, and regex path restrictions.
- LDAP Directory and Group Sync
- Authenticates users against LDAP directories using observer bind credentials and caches groupOfUniqueNames memberships with configurable TTL intervals for group ACLs.
- TOTP Two-Factor Verification
- Generates interactive TOTP secrets with terminal QR codes for authenticator apps and validates six-digit time-based one-time passwords during login.
- Upstream Header and Auth Injection
- Forwards custom HTTP response headers and injects HTTP Basic Authentication credentials on behalf of authenticated users to legacy backend services.