Rauthy
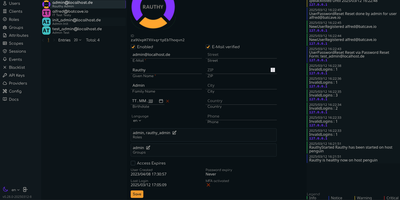
Every self-hosted app asking for its own password is a liability you keep re-creating. Rauthy is a lightweight single sign-on identity provider that gives your whole homelab or organization one secure login through OpenID Connect and OAuth 2, with passkeys at the center instead of passwords. Accounts can be fully passwordless: an email address plus a FIDO2 passkey with user verification, or a password backed by a security key, with magic links and upstream login providers also supported. The admin UI manages users, clients, roles, groups, sessions, API keys, blacklists, and per-client login branding with custom logos and colors, and events stream to email, Matrix, or Slack when something deserves attention. Login endpoints defend themselves with brute-force and credential-stuffing detection, automatic IP blacklisting, rate limiting, and optional geolocation blocking. Beyond web apps, a PAM and NSS module extends the same identities to Linux workstations and SSH logins with ephemeral passwords or public keys, and the OAuth device flow covers headless and IoT devices. It runs as a single efficient service on embedded Hiqlite or Postgres, clusters for high availability, needs only tens of megabytes of memory, and has passed an independent security audit. Dynamic client registration, SCIM provisioning, and DPoP tokens cover modern decentralized login flows. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Issuerd
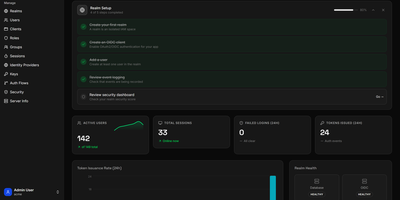
One login for every internal tool, without handing your users another password to forget: Issuerd is a Keycloak-compatible identity provider that runs single sign-on for your whole stack from a single binary. Administrators manage realms, users, groups, clients, roles, client scopes, and protocol mappers in an embedded admin console, while end users get their own account console for passwords, passkeys, and two-factor settings. Authentication flows cover MFA, social login, and themable, localized login pages with per-realm language and email templates, so each audience sees a sign-in that looks like your product. Federation connects Samba AD, OpenLDAP, and Active Directory with user and group sync, password validation and write-through, plus Kerberos and SPNEGO for desktop single sign-on. For modern clients it implements DPoP token binding so stolen access tokens are useless without the holder's key, CIBA for approvals that happen on a second device, and token exchange patterns aimed at AI agents calling downstream services. Declarative YAML provisioning, a full management API, OpenAPI export, Prometheus metrics, and health probes round out day-two operations, and nodes scale horizontally behind any load balancer with no sticky sessions. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Pocket ID
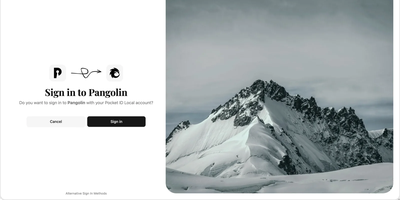
Backed by over 8,700 GitHub stars and OpenID Connect certification, Pocket ID delivers what enterprise identity platforms like Keycloak provide but without the configuration complexity — a passkey-only OIDC provider purpose-built for homelabs and small deployments. The core design decision is radical simplicity: no passwords exist in the system, only WebAuthn-based passkeys using hardware security keys, TouchID, FaceID, or device PINs, making phishing attacks structurally impossible rather than merely discouraged. The Go backend built on the Gin framework serves a compiled SvelteKit frontend as static assets, running as a single Docker container with SQLite as the default database and optional PostgreSQL for larger deployments. User management supports manual creation, signup links, and open registration, with group-based access control that restricts which OIDC clients each group can access and attaches custom claims for downstream role mapping. LDAP synchronization pulls users and groups from OpenLDAP or Active Directory, while SCIM support enables automated provisioning from compatible identity sources. Federated client credentials handle machine-to-machine authentication for service-to-service communication patterns. The audit system logs every authentication event with GeoIP enrichment, sends email notifications for sign-ins from unknown devices, and provides one-time login codes for accessing accounts from devices without passkey support. TLS with HTTP/2 is built in, PKCE adds code exchange protection, and OpenTelemetry provides tracing and metrics integration. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. BSD 2-Clause licensed.
Casdoor
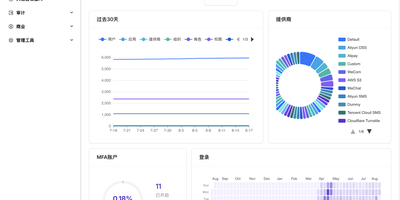
With 13,800+ GitHub stars and active releases through 2026, Casdoor is the open-source identity platform that ships OAuth 2.0, OIDC, SAML 2.0, CAS, LDAP, SCIM 2.0, WebAuthn passkeys, TOTP multi-factor authentication, and Face ID biometric login in a single Go binary with a React web console — covering every authentication protocol your organization will ever need. Social login connects 50+ identity providers including Google, GitHub, Microsoft Azure AD, Facebook, WeChat, DingTalk, Apple, Twitter, and LinkedIn without custom code. The AI-first architecture includes a Model Context Protocol gateway for AI agent authentication and Agent-to-Agent protocol support for securing LLM-powered workflows. Built-in Casbin integration delivers authorization primitives beyond basic RBAC: attribute-based access control, relationship-based access control, and custom policy models through a unified engine. The organization-scoped multi-tenancy model isolates users, applications, and identity providers per tenant with customizable login pages, branding, and SMTP configuration. SCIM 2.0 endpoints automate user provisioning from HR systems and Active Directory. Official SDKs for Go, Java, Node.js, Python, and PHP accelerate application integration. The RESTful API exposes every resource for programmatic management. Comprehensive audit logs record authentication events and administrative actions. Deploy via Docker Compose with MySQL or PostgreSQL, the all-in-one SQLite Docker image for quick trials, or the official Kubernetes Helm chart for production clusters. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Ory Hydra
Ory Hydra is an OpenID Certified OAuth 2.0 and OpenID Connect provider that plugs into any existing user database or authentication system through a headless consent and login bridge, letting you own your authorization infrastructure without rebuilding identity management from scratch. The Go binary ships at under 15MB with zero system dependencies and exposes two distinct API surfaces: a public endpoint on port 4444 handling authorization code flows, token exchanges, PKCE challenges, device authorization grants per RFC 8628, and OpenID Connect discovery, plus an admin endpoint on port 4445 managing client registration, token introspection, consent session lifecycle, and JWKS rotation. Access tokens can be issued as opaque reference tokens or signed JWTs for stateless validation at resource servers, while refresh token rotation, token revocation per RFC 7009, and pairwise subject identifiers provide granular security controls. Persistent storage spans PostgreSQL, MySQL, and CockroachDB with automatic schema migrations, and the architecture supports horizontal scaling behind load balancers with shared database state. Dynamic client registration per RFC 7591 enables automated provisioning, and the OAuth 2.0 Threat Model security considerations are implemented as default behaviors rather than optional add-ons. Trusted by OpenAI and other internet-scale platforms. Helm charts and Docker Compose quickstarts provide production-ready deployment paths alongside the broader Ory ecosystem including Kratos for identity management, Oathkeeper for zero-trust API proxying, and Keto for fine-grained permissions. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.