Categories
Self-Hosted Security Authentication Single Sign-On Identity Provider OpenID Connect PasskeysStars
Forks
Watchers
Developer links
Rauthy
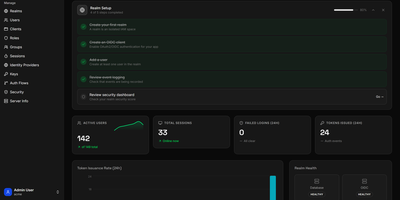
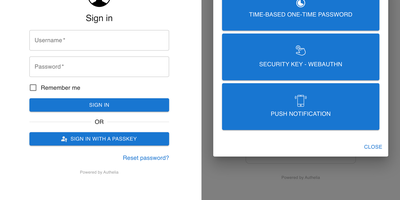
Every self-hosted app asking for its own password is a liability you keep re-creating. Rauthy is a lightweight single sign-on identity provider that gives your whole homelab or organization one secure login through OpenID Connect and OAuth 2, with passkeys at the center instead of passwords. Accounts can be fully passwordless: an email address plus a FIDO2 passkey with user verification, or a password backed by a security key, with magic links and upstream login providers also supported. The admin UI manages users, clients, roles, groups, sessions, API keys, blacklists, and per-client login branding with custom logos and colors, and events stream to email, Matrix, or Slack when something deserves attention. Login endpoints defend themselves with brute-force and credential-stuffing detection, automatic IP blacklisting, rate limiting, and optional geolocation blocking. Beyond web apps, a PAM and NSS module extends the same identities to Linux workstations and SSH logins with ephemeral passwords or public keys, and the OAuth device flow covers headless and IoT devices. It runs as a single efficient service on embedded Hiqlite or Postgres, clusters for high availability, needs only tens of megabytes of memory, and has passed an independent security audit. Dynamic client registration, SCIM provisioning, and DPoP tokens cover modern decentralized login flows. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Benefits
- One Login For Everything
- A single OpenID Connect provider serves every self-hosted application, replacing scattered per-app passwords with one identity, one session policy, and one place to disable access instantly.
- Passkeys Instead Of Passwords
- Passwordless accounts using email plus FIDO2 passkeys with user verification, or passwords backed by security keys, remove the weakest credential from most of your services entirely.
- Security That Fights Back
- Brute-force and credential-stuffing detection, automatic IP blacklisting with expiry, login rate limiting, and optional geolocation blocking defend the front door without extra appliances or services.
- Featherweight To Operate
- A single service on embedded Hiqlite runs a full identity provider in tens of megabytes of memory, even on a Raspberry Pi, and clusters for high availability when needed.
Features
- Admin And Account UIs
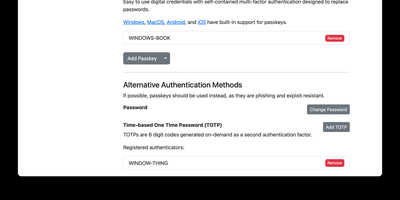
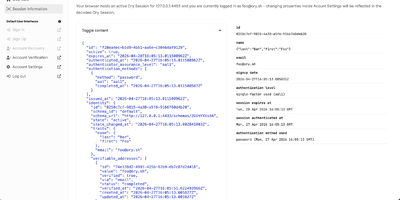
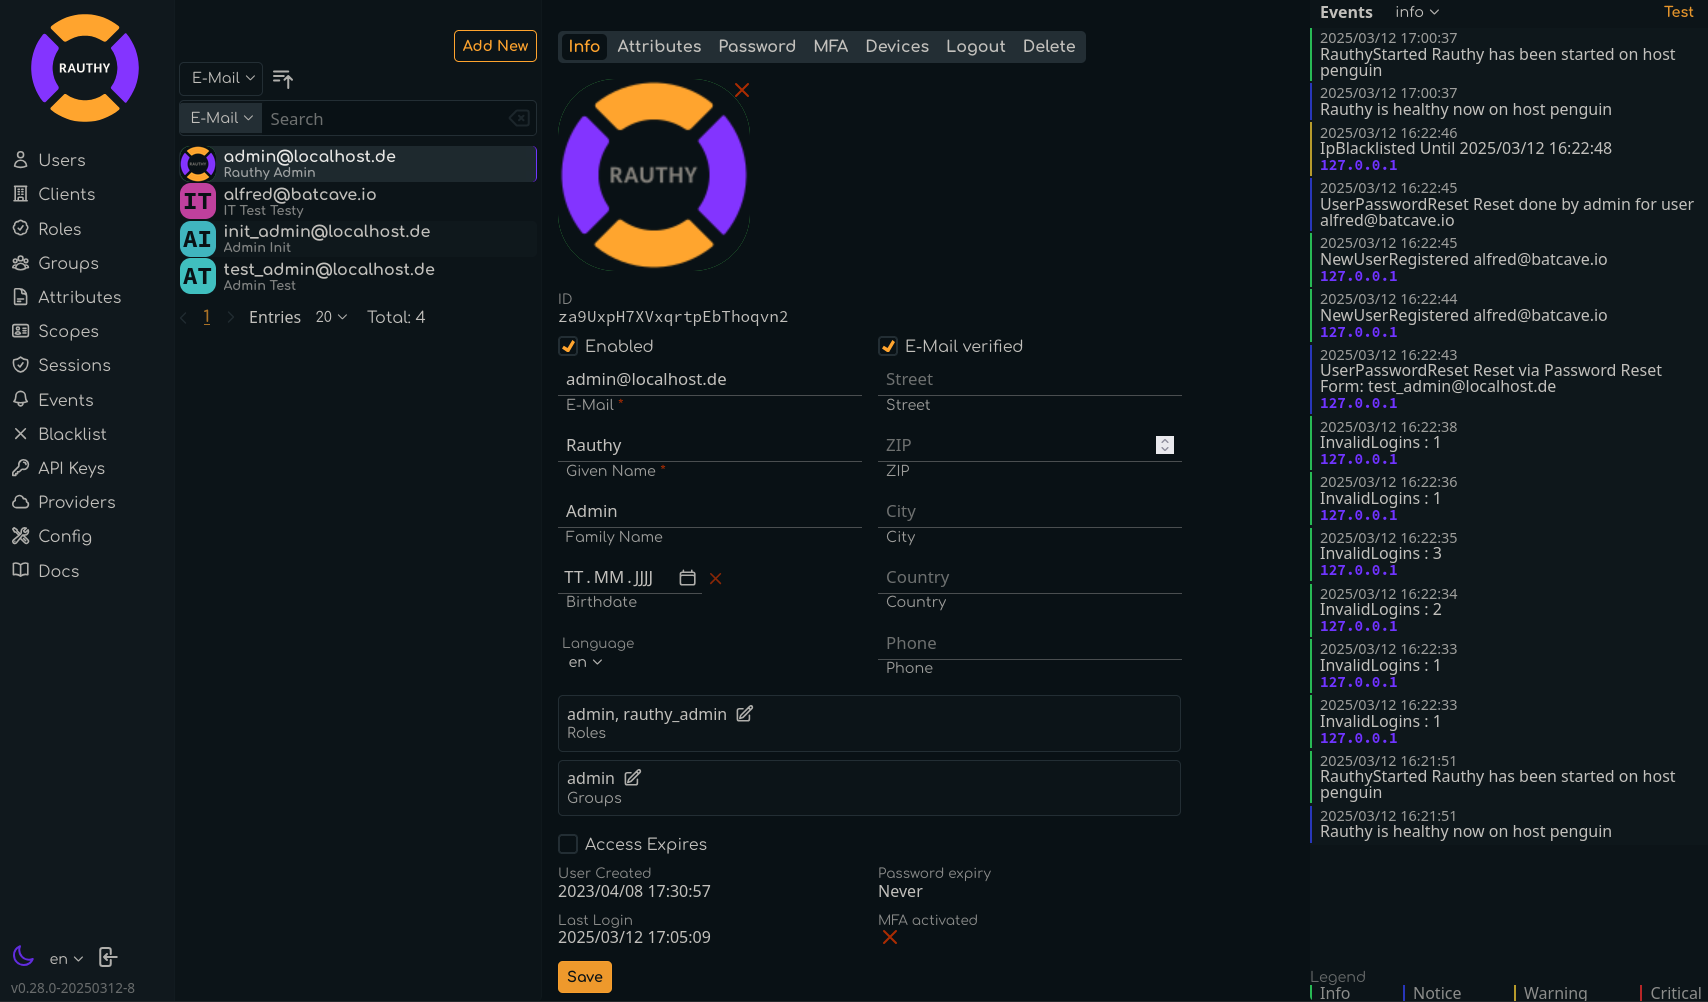
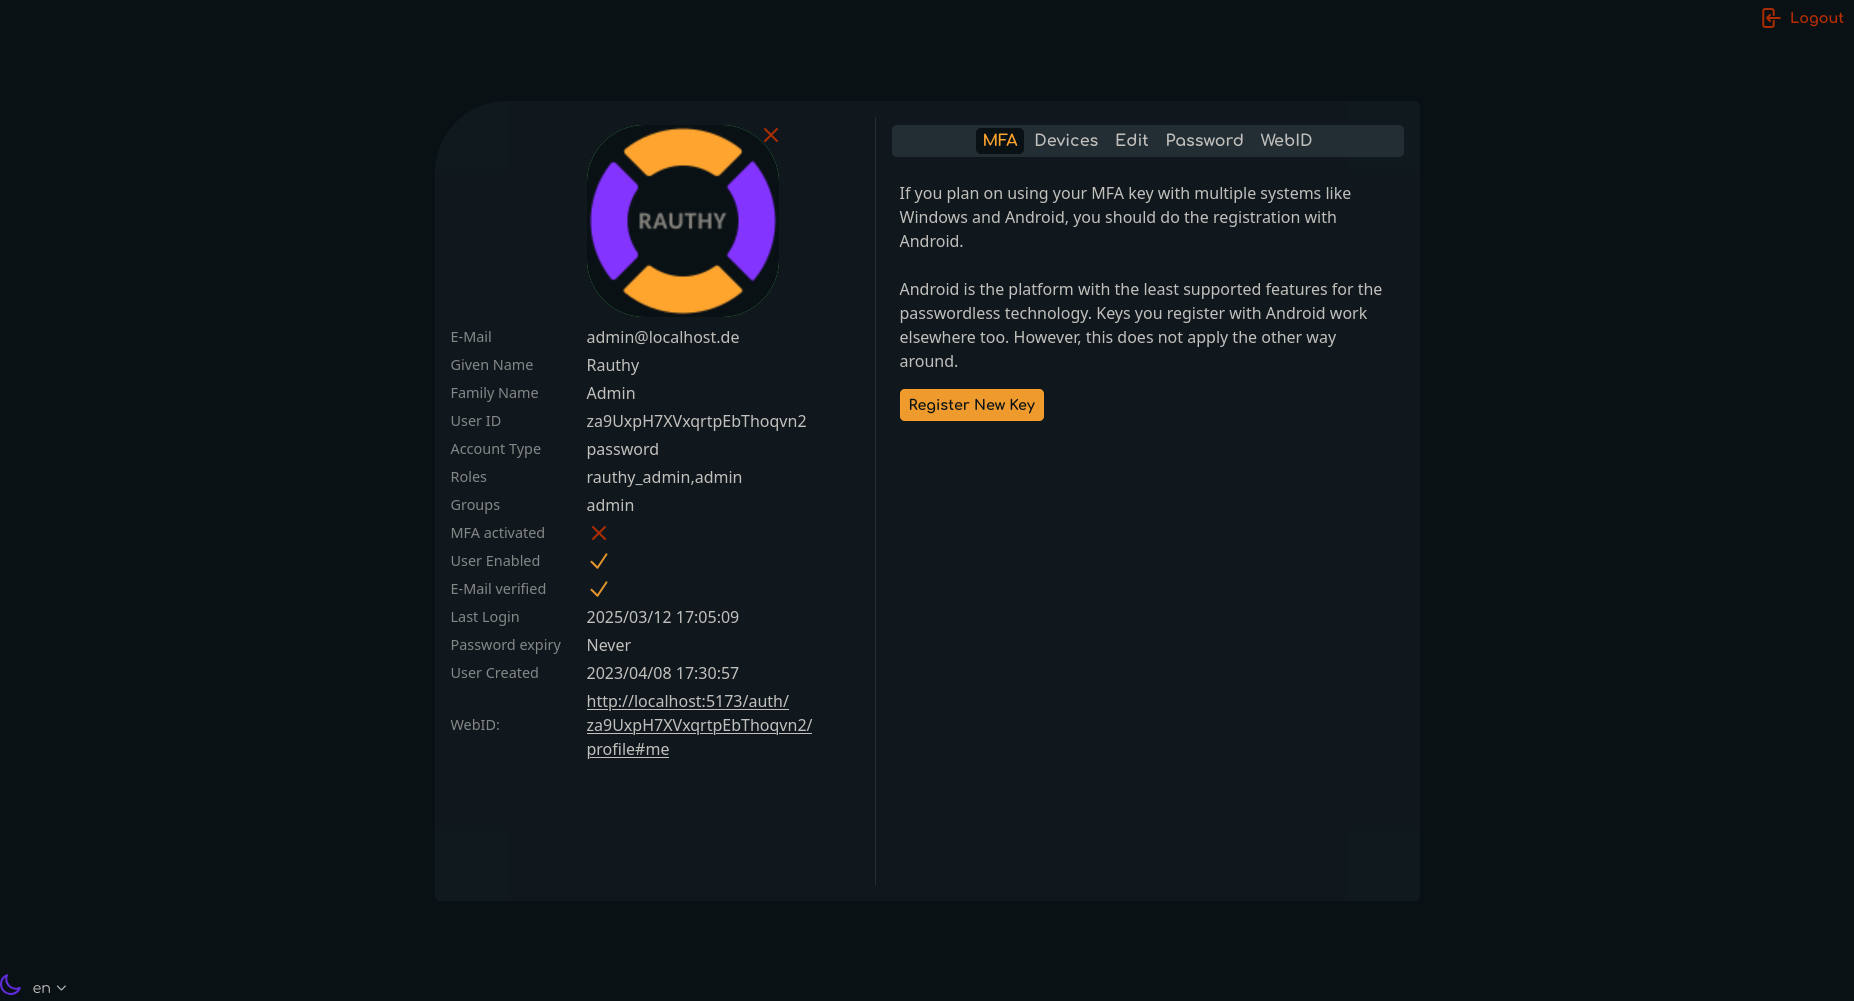
- The admin console manages users, clients, roles, groups, sessions, API keys, and blacklists, and each user gets a self-service dashboard for passwords, passkeys, and account data.
- Per-Client Login Branding
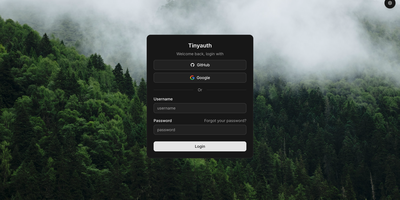
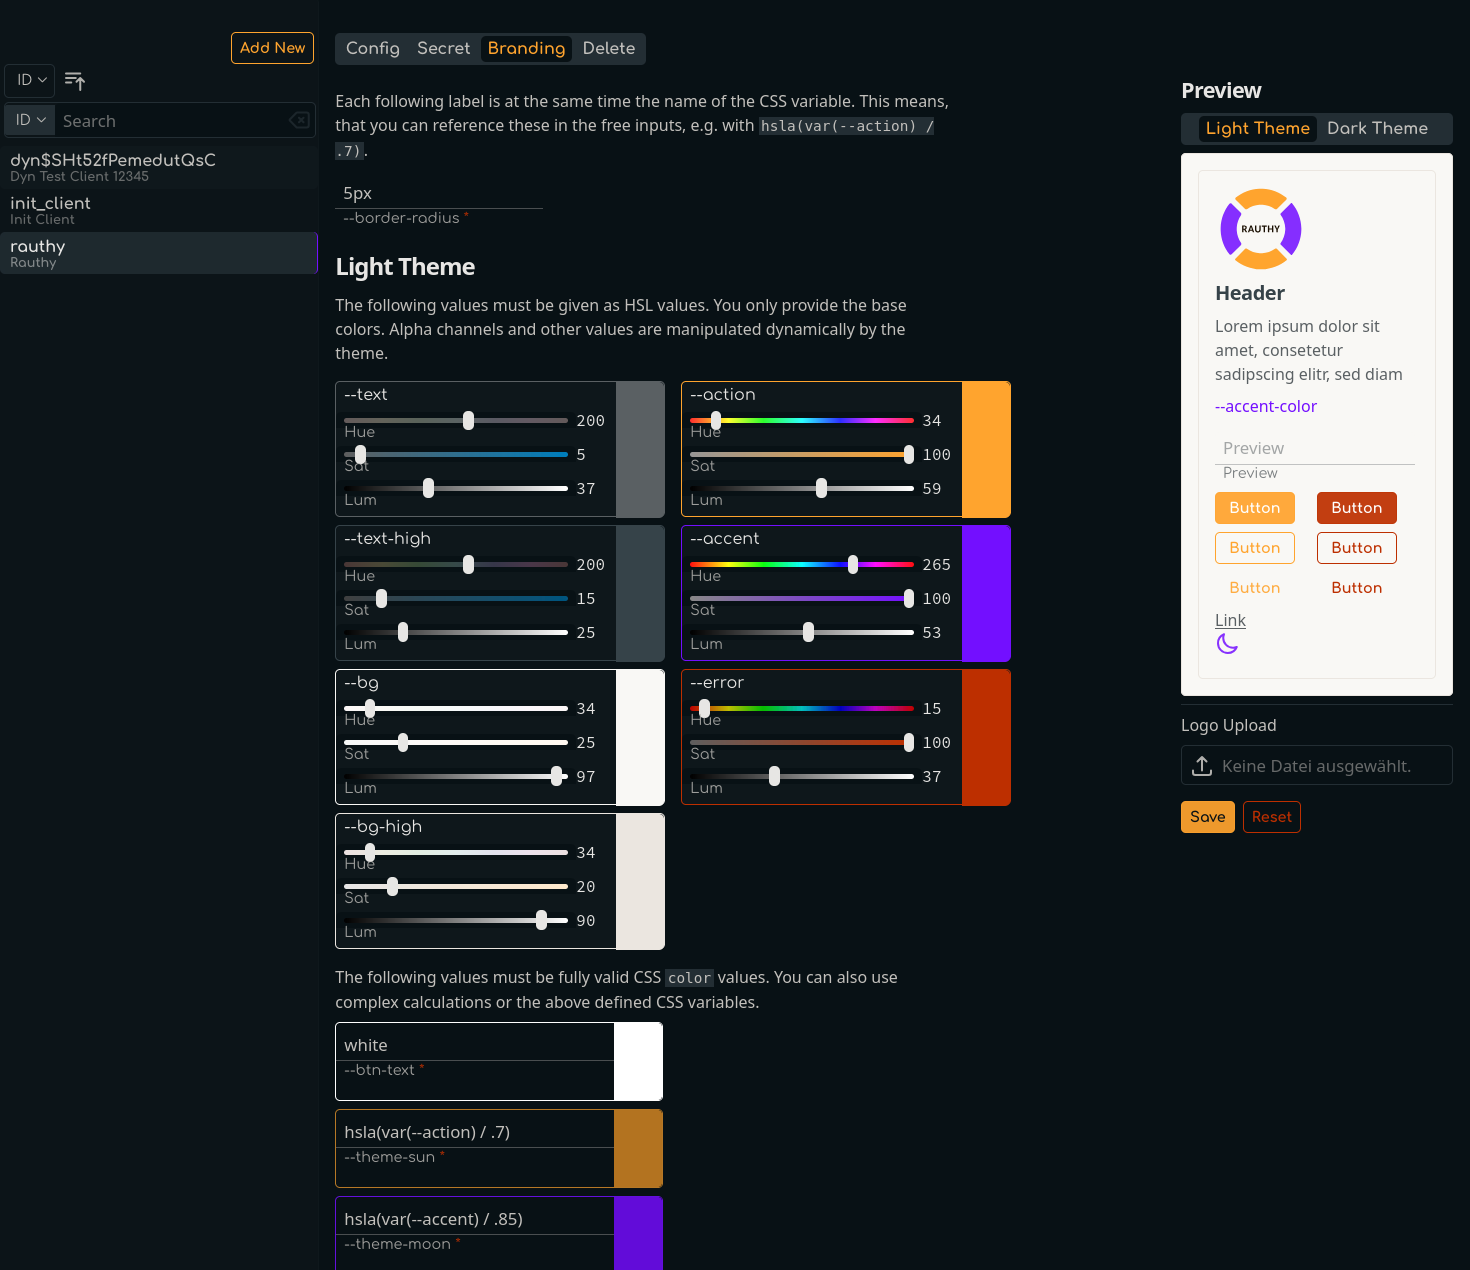
- Every client application can present its own themed login page with custom colors, logo, and favicon, and all end-user pages translate server-side into multiple languages.
- Linux PAM Integration
- Companion PAM and NSS modules extend identities to workstations and SSH with MFA, ephemeral auto-expiring passwords, or public keys, managed centrally without local account files.
- Modern Protocol Coverage
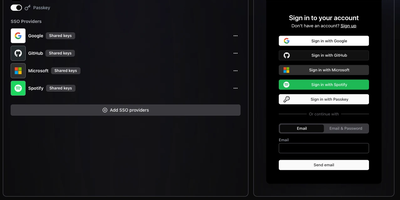
- Dynamic client registration, device authorization for headless devices, SCIM v2 provisioning, DPoP tokens, upstream providers, and backchannel logout cover contemporary federation requirements.