Xalgorix
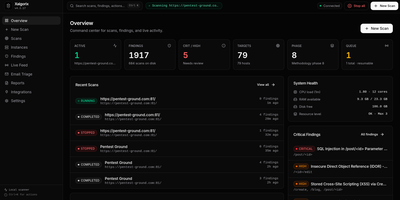
Xalgorix delivers AI-driven penetration testing that proves vulnerabilities exist rather than guessing, pairing an autonomous LLM agent with an independent exploit verifier that re-exploits every finding before it reaches your report. The 22-phase methodology mirrors how a skilled human pentester works through an engagement, covering reconnaissance, subdomain enumeration, port scanning, web crawling, parameter fuzzing, SQL injection testing, XSS detection, authentication bypass, API testing, and more. Select all phases or pick specific ones per target. The platform ships with 85+ offensive security tools preinstalled (nmap, nuclei, httpx, subfinder, katana, ffuf, gobuster, sqlmap, masscan, dalfox, feroxbuster) plus 14 built-in agent tools for browser automation, terminal execution, and note-taking. Connect your own LLM provider (OpenAI, Anthropic, DeepSeek, Gemini, Groq, Ollama, or MiniMax) so no scan data or target information leaves your infrastructure. The web dashboard on port 9137 provides live WebSocket telemetry showing tool calls, agent reasoning, and findings as scans progress. A findings index with CVSS scoring and severity filters organizes results, and branded PDF reports include your company name and logo. Wildcard and multi-target scans handle red team attack-surface mapping, while source-code scanning audits repositories directly without requiring a deployed target. A REST API enables scripted scans and SIEM pipeline integration, and webhooks push notifications to Discord or Telegram. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Watchtower
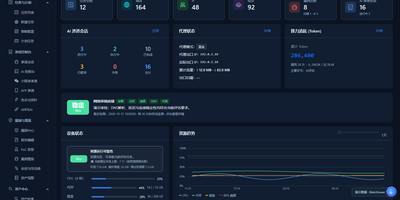
Watchtower puts AI-driven security assessments into one web console, where sessions probe your attack surface while every request, finding, and piece of evidence is captured as it happens. The AI session console follows the attack surface, session progress, tool calls, and findings as an assessment runs, so you can watch an engagement unfold instead of reading a log afterwards. A built-in proxy workflow records HTTP and HTTPS traffic history with highlighted patterns, and any captured request can be sent to the Repeater for editing, replay, and response comparison. Mobile work is covered too: connect phones over USB or wireless, capture app traffic separately from accessibility control, and import WeChat mini-program packages to configure an assessment session. A public vulnerability intelligence library can be searched by component, severity, and source and kept synchronized locally, giving assessments current context without sending your targets anywhere. Findings are managed by source, severity, and status, each linked back to its supporting evidence, and the report editor assembles them with a live preview, impact notes, and remediation guidance. The dashboard tracks assets, tasks, AI sessions, token usage, and runtime resources, and task admission is budgeted against physical memory so heavy scans do not starve the host. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL-3.0 licensed.