CrowdSec
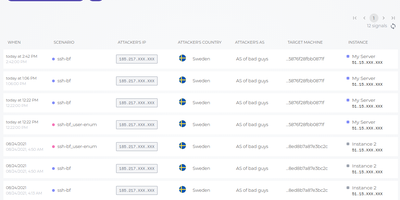
With over 14,000 GitHub stars and a growing global network of security deployments, CrowdSec turns every attack on any participating server into protection for the entire community. The security engine operates as a combined IDS/IPS and WAF, analyzing log sources from Nginx, Apache, SSH, WordPress, and over 50 other services to detect brute force attacks, port scans, web vulnerability exploitation, and credential stuffing in real time. When one server detects a new threat, the attacker's IP is shared through the community blocklist, proactively protecting thousands of other installations before the attacker can reach them. The built-in WAF powered by Coraza v3 inspects HTTP requests at the application layer, validates against OpenAPI schemas, and applies custom rules with flexible AND/OR condition mixing for precise threat detection. Bot detection serves challenge pages with client fingerprinting to distinguish legitimate traffic from automated scrapers and scanners. Remediation components block malicious IPs at multiple infrastructure layers including iptables, nftables, Nginx, HAProxy, Cloudflare, and AWS Security Groups through the detect-here-remedy-there architecture. The scenario-based detection system ships with default rules for common attack patterns and supports custom scenarios written in YAML with an expressive filter language. A centralized console provides real-time visualization of alerts, threat intelligence analysis, and management of multiple distributed security engines. GDPR compliant by design, all log analysis happens locally and raw logs never leave your infrastructure. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Nginx-Love
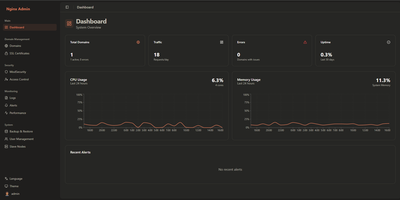
Hand-editing nginx configuration files to run a firewall is nobody's idea of a good afternoon, and Nginx-Love turns that chore into a dashboard. You manage domains, load balancing upstreams, and HTTPS backends through forms instead of config syntax, and the platform writes and reloads the underlying configuration for you. A ModSecurity firewall with the OWASP Core Rule Set inspects traffic to your sites, and you tune its rules from the interface rather than a text editor. Certificates arrive two ways: automated through Let's Encrypt, or uploaded manually when you bring your own. A Bot Manager fingerprints visitors with JA4 signals so you can welcome good crawlers, challenge suspicious automation, and block hostile bots by policy. Access lists filter by IP address, geography, and user agent, and multi-user roles let administrators, moderators, and viewers each see the controls appropriate to their job. Monitoring watches performance and attack patterns, sending alerts by email or Telegram when something needs attention. Configuration exports back up your setup, restores bring it back, and multi-node sync keeps a cluster of servers enforcing the same policy. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.