Categories
Reverse Proxy Web Application Firewall SSL Management Server Security Nginx Management Bot ManagementStars
Forks
Watchers
Developer links
Nginx-Love
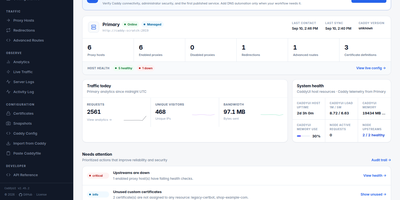
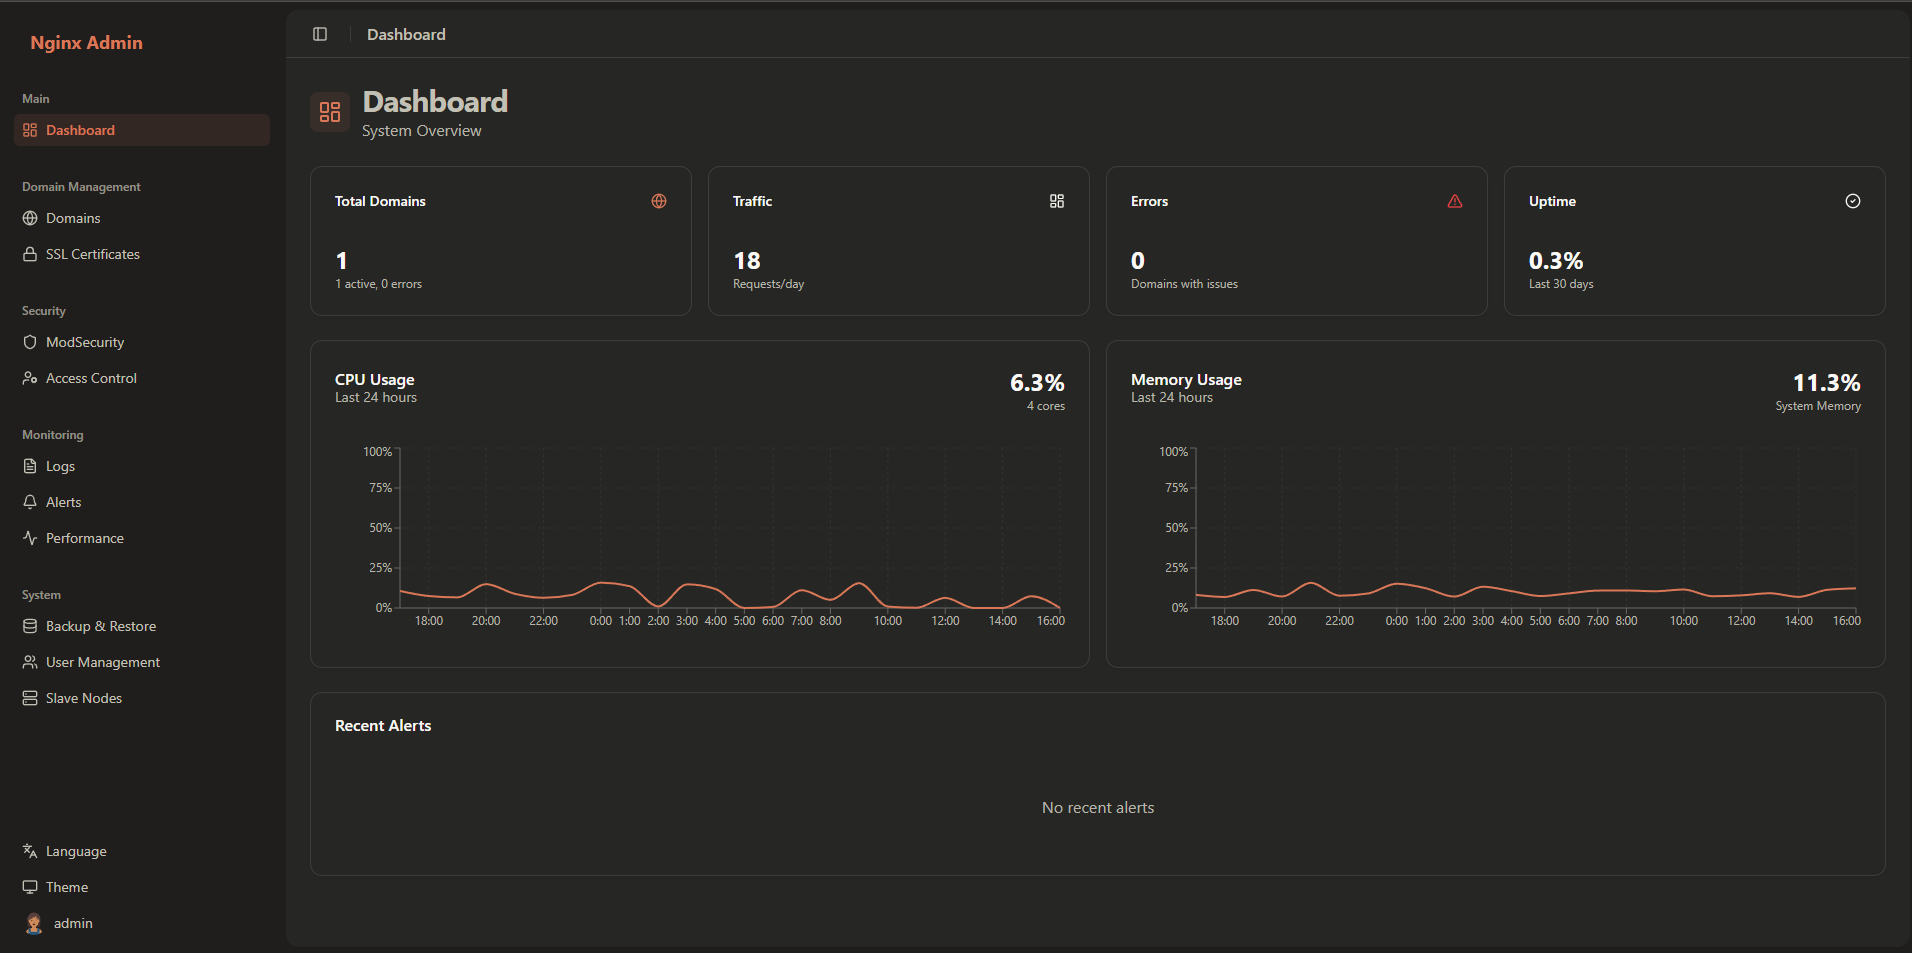
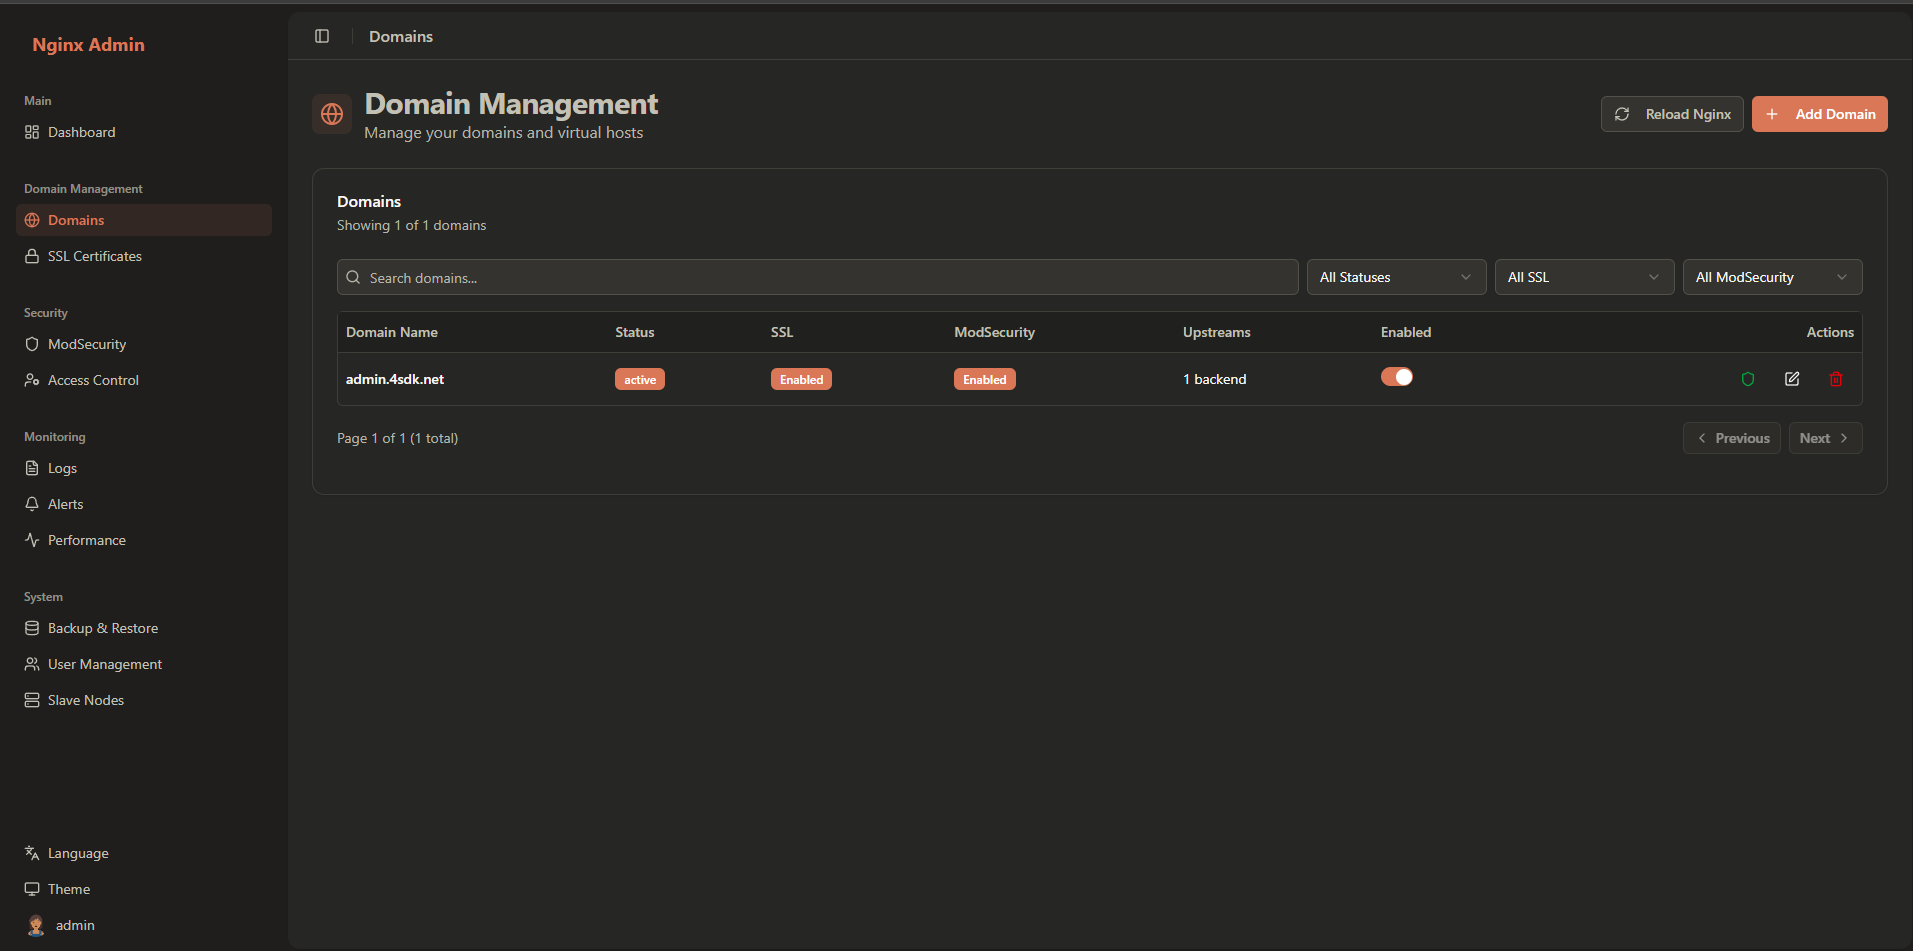
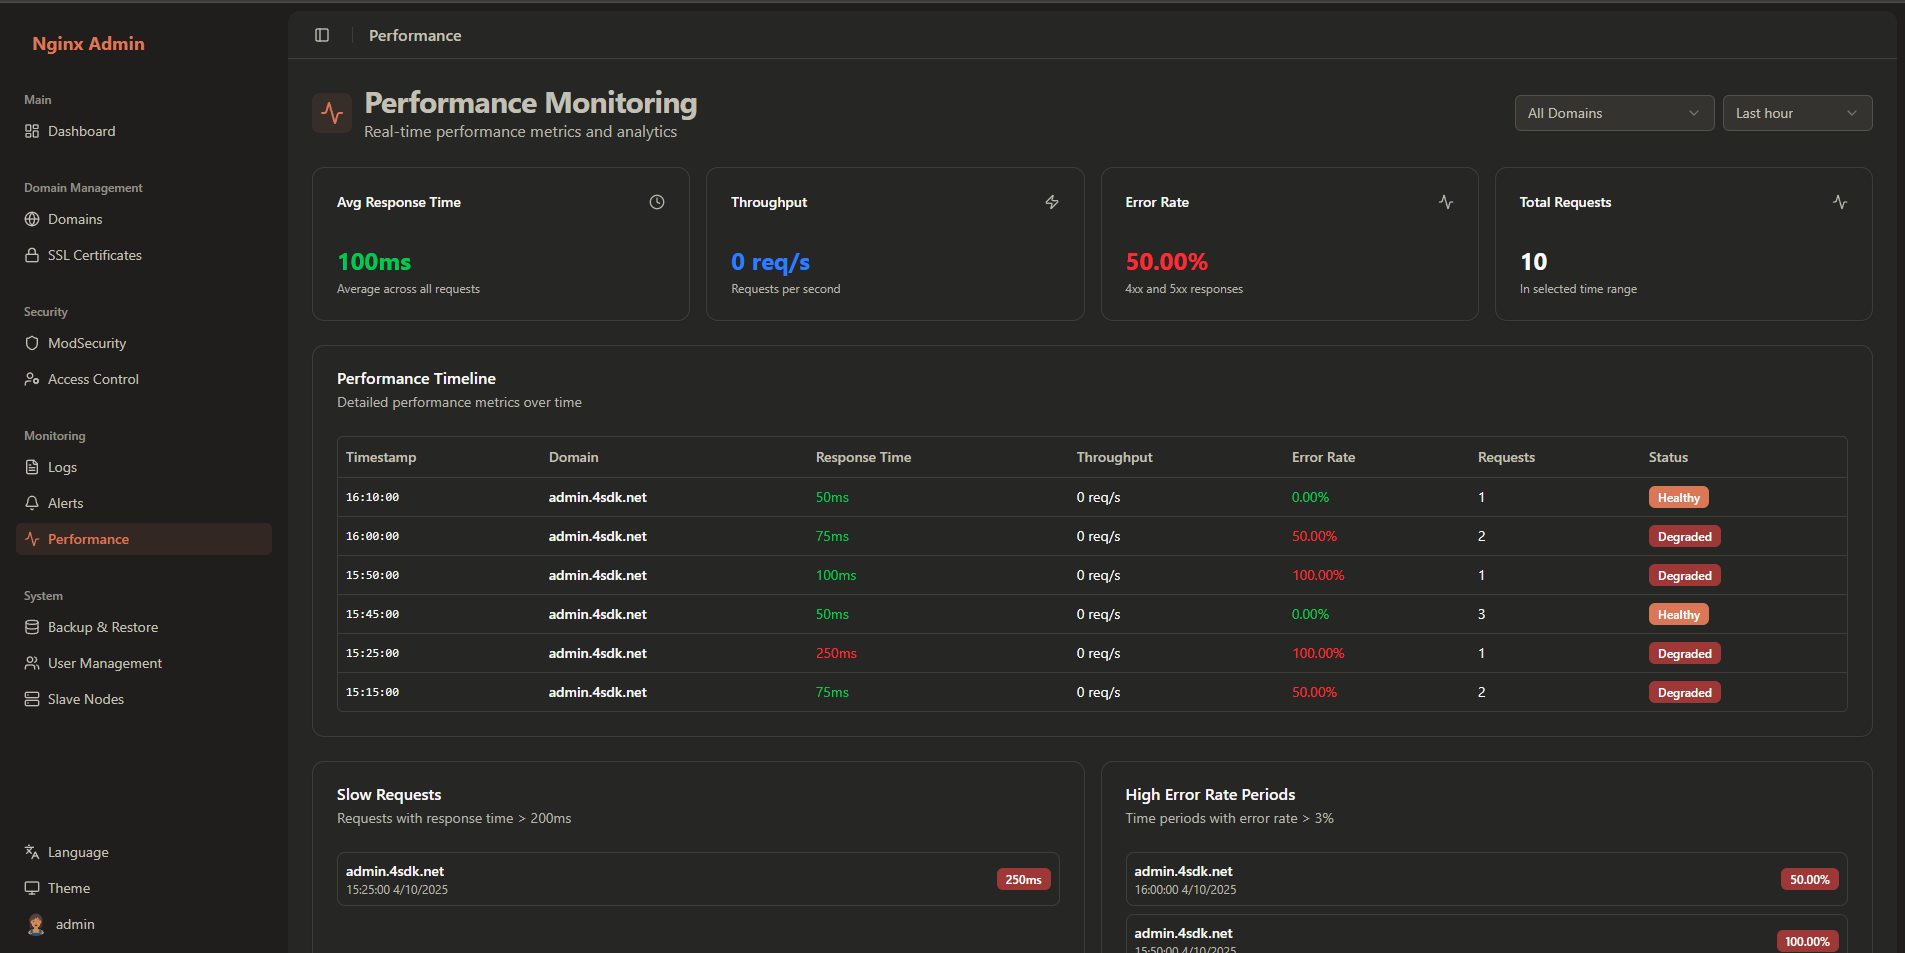
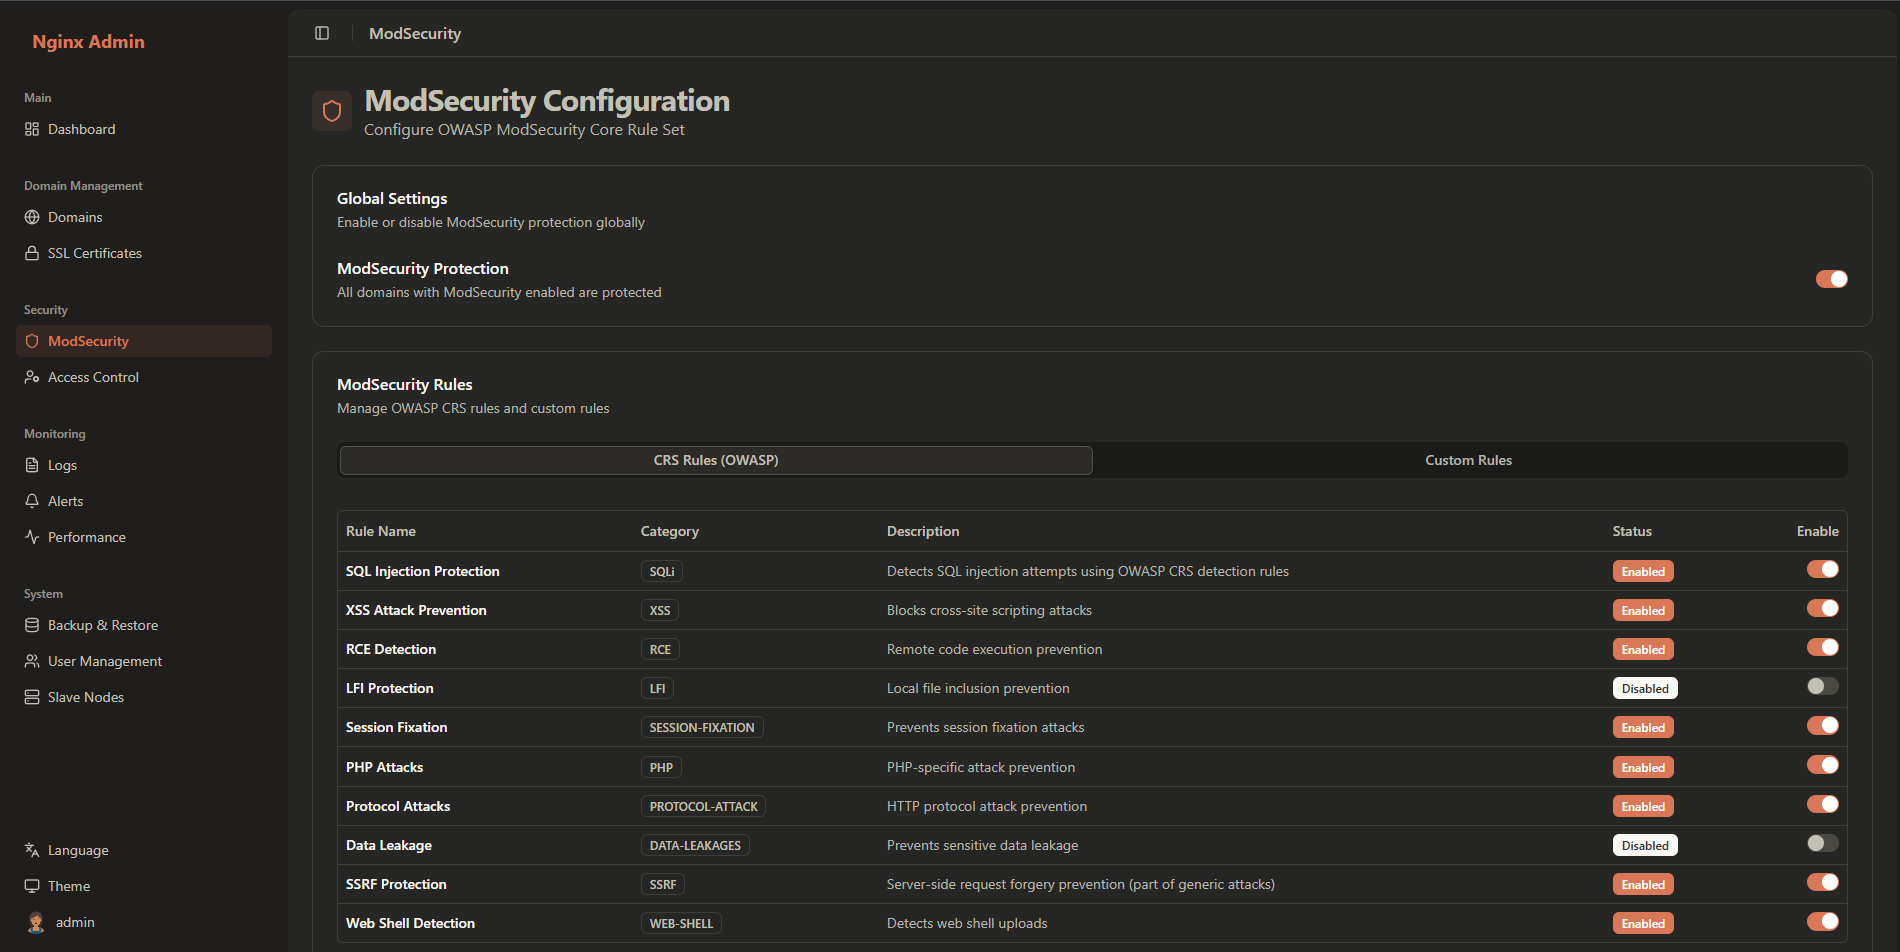
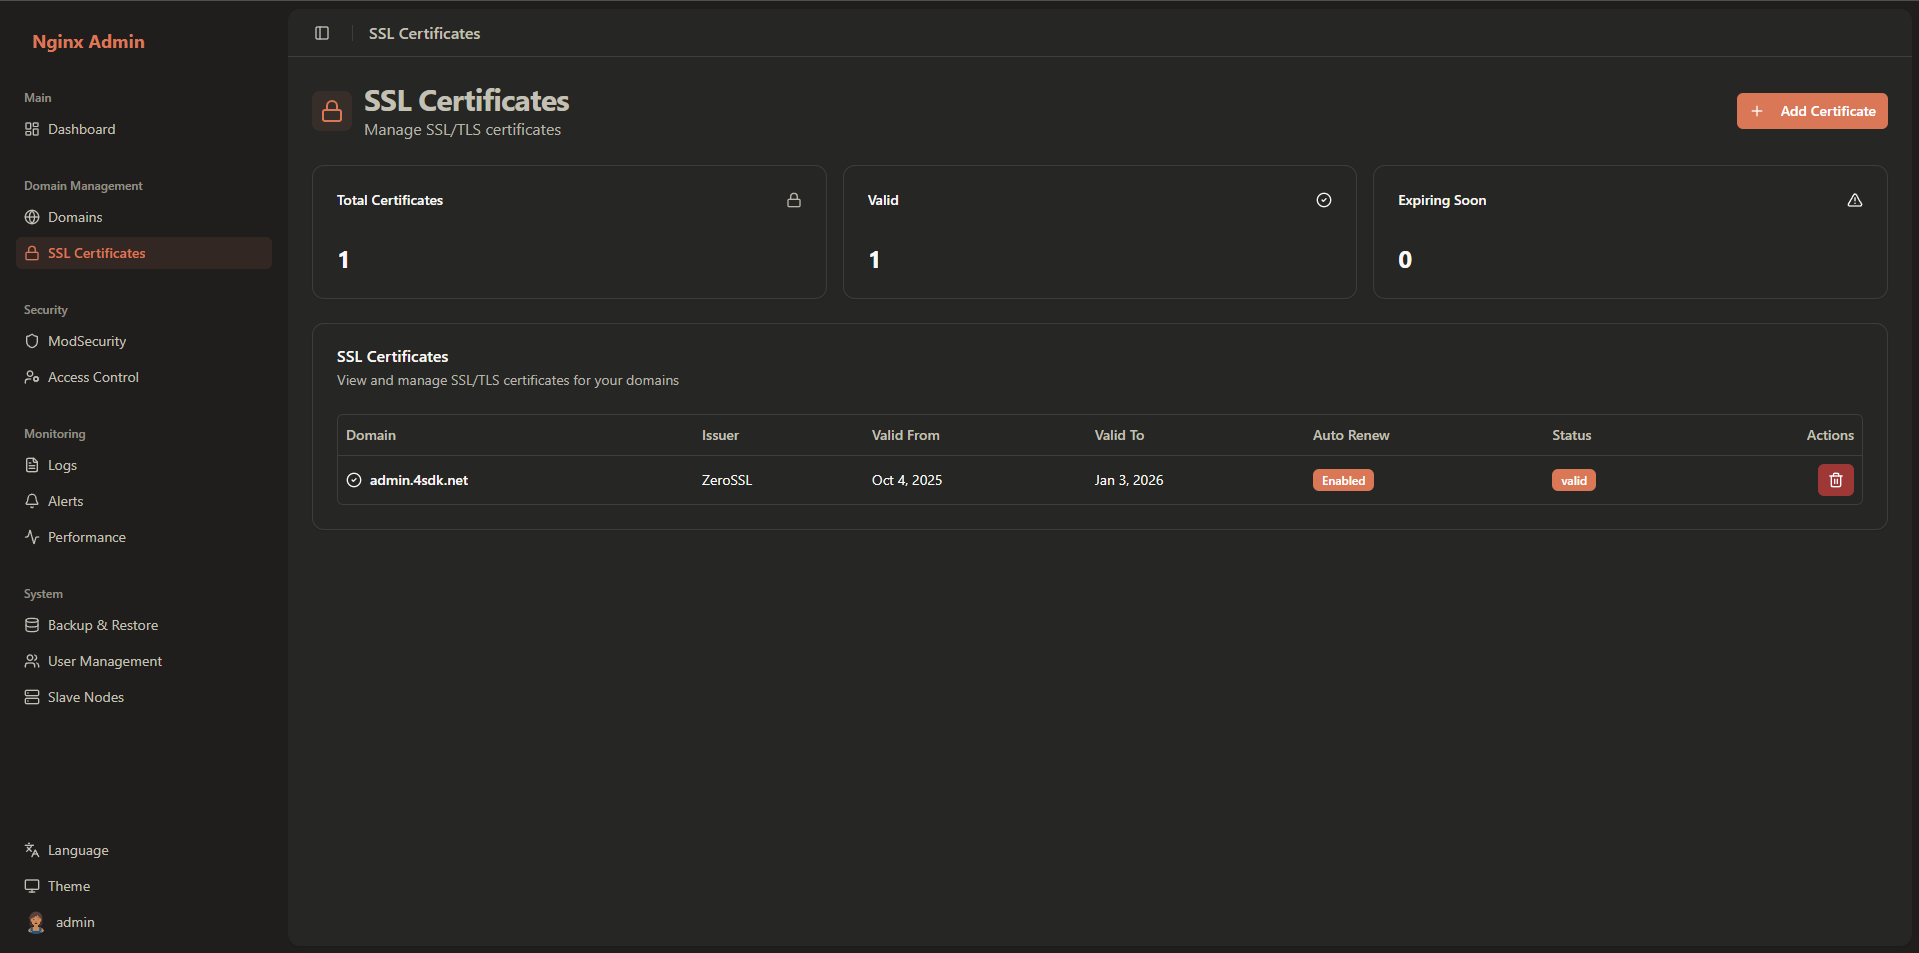
Hand-editing nginx configuration files to run a firewall is nobody's idea of a good afternoon, and Nginx-Love turns that chore into a dashboard. You manage domains, load balancing upstreams, and HTTPS backends through forms instead of config syntax, and the platform writes and reloads the underlying configuration for you. A ModSecurity firewall with the OWASP Core Rule Set inspects traffic to your sites, and you tune its rules from the interface rather than a text editor. Certificates arrive two ways: automated through Let's Encrypt, or uploaded manually when you bring your own. A Bot Manager fingerprints visitors with JA4 signals so you can welcome good crawlers, challenge suspicious automation, and block hostile bots by policy. Access lists filter by IP address, geography, and user agent, and multi-user roles let administrators, moderators, and viewers each see the controls appropriate to their job. Monitoring watches performance and attack patterns, sending alerts by email or Telegram when something needs attention. Configuration exports back up your setup, restores bring it back, and multi-node sync keeps a cluster of servers enforcing the same policy. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Benefits
- Firewall Without Config Files
- ModSecurity with the OWASP Core Rule Set guards your domains, tuned from the dashboard. You get a real web application firewall without hand-writing a single nginx directive.
- Bots Judged By Fingerprint
- JA4 fingerprinting in the Bot Manager distinguishes good crawlers from hostile automation. Policies welcome, challenge, or block by fingerprint instead of easily spoofed user-agent strings alone.
- Certificates On Autopilot
- Let's Encrypt issuance and renewal run automatically, and manual upload covers certificates you bring yourself. Domains, upstreams, and HTTPS backends are managed as forms, not files.
- Clusters Stay In Sync
- Export and restore configurations, and sync policy across multiple nodes. Alerts by email or Telegram flag attacks and performance issues while role-based access limits who changes what.
Features
- ModSecurity WAF Rules
- OWASP Core Rule Set plus custom rules inspect traffic on ports 80 and 443. Tune protections per domain from the interface while logs show what was blocked and why.
- JA4 Bot Manager
- Fingerprint-based bot detection builds policies from JA4 signals in your logs. Analytics break down bot traffic so allow, challenge, and block decisions rest on evidence.
- Domains And Load Balancing
- Manage domains with upstream health checks and HTTPS backends. The platform generates and reloads nginx configuration, replacing manual edits and reload commands entirely.
- Access Control Lists
- Filter visitors by IP address, GeoIP location, and user agent. Combine lists with bot policies for layered control over who reaches each protected domain.
- Monitoring And Alerts
- Real-time performance metrics and attack monitoring with email and Telegram notifications. Admin, moderator, and viewer roles govern access, and backups export your whole setup.