Pomerium
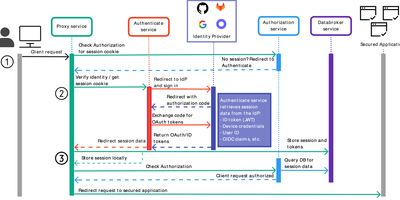
Pomerium puts every internal application behind a single identity-aware proxy, so engineers reach dashboards, admin panels, and databases through their browser with no VPN client and no network-level trust. Sign-in flows through your existing identity provider, including Google, Okta, Azure AD, GitHub, GitLab, and any OpenID Connect service, with sessions verified continuously rather than once at login. Each route carries its own policy: restrict the finance tool to the finance group, require a specific email domain for the admin console, or allow read-only paths more broadly. Authorized requests pass identity headers the application can trust, and every access decision is logged for audit. TCP routes extend the same sign-in and policy checks to SSH, PostgreSQL, MySQL, and RDP connections through a small client or a browser-based terminal. In Kubernetes, Pomerium doubles as an ingress controller, applying the same policies to services as annotations on ingress resources. Mutual TLS between the proxy and backends, encrypted sessions, and short-lived credentials replace shared passwords and flat networks. Teams roll it out as one all-in-one binary or split the proxy, authorize, authenticate, and cache services across machines as traffic grows. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Deploy