Categories
self-hosted security kubernetes zero-trust reverse-proxy access-control identity-aware-proxyStars
Forks
Watchers
Developer links
Pomerium
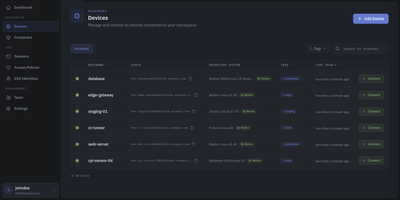
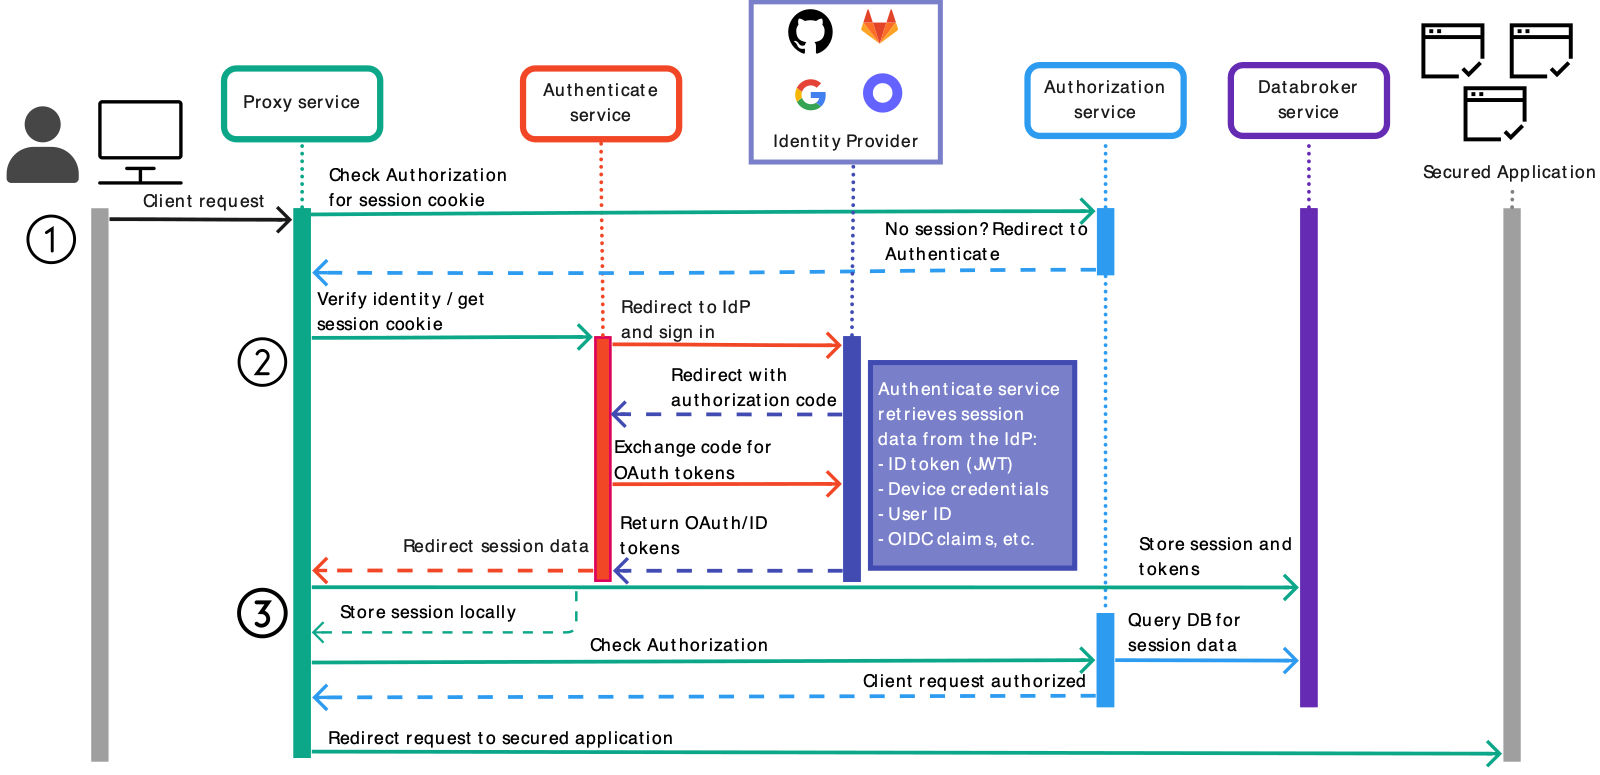
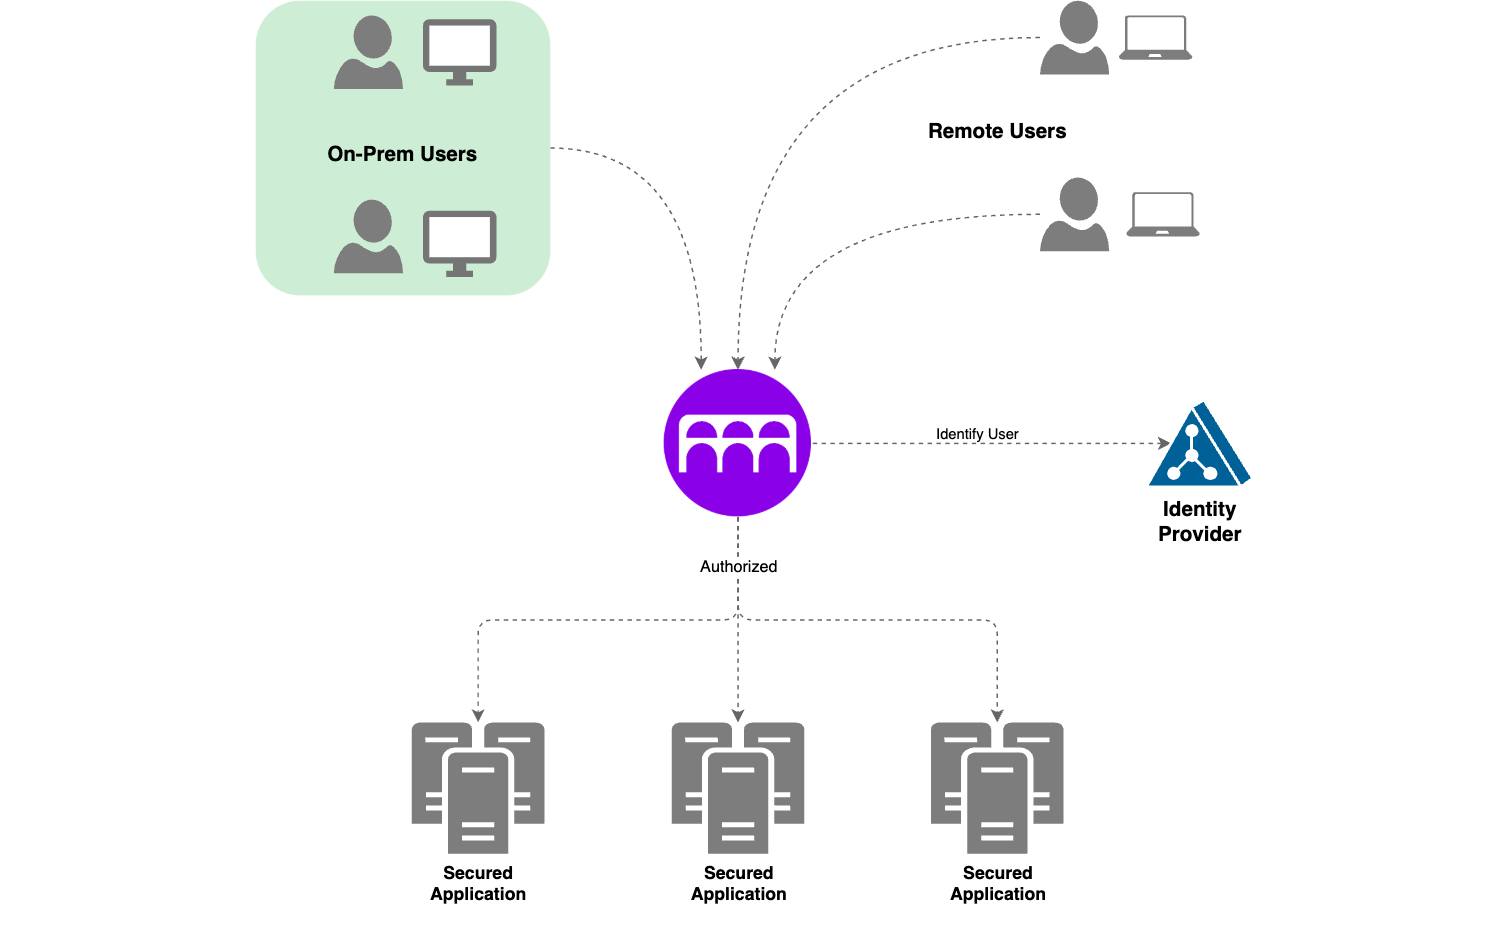
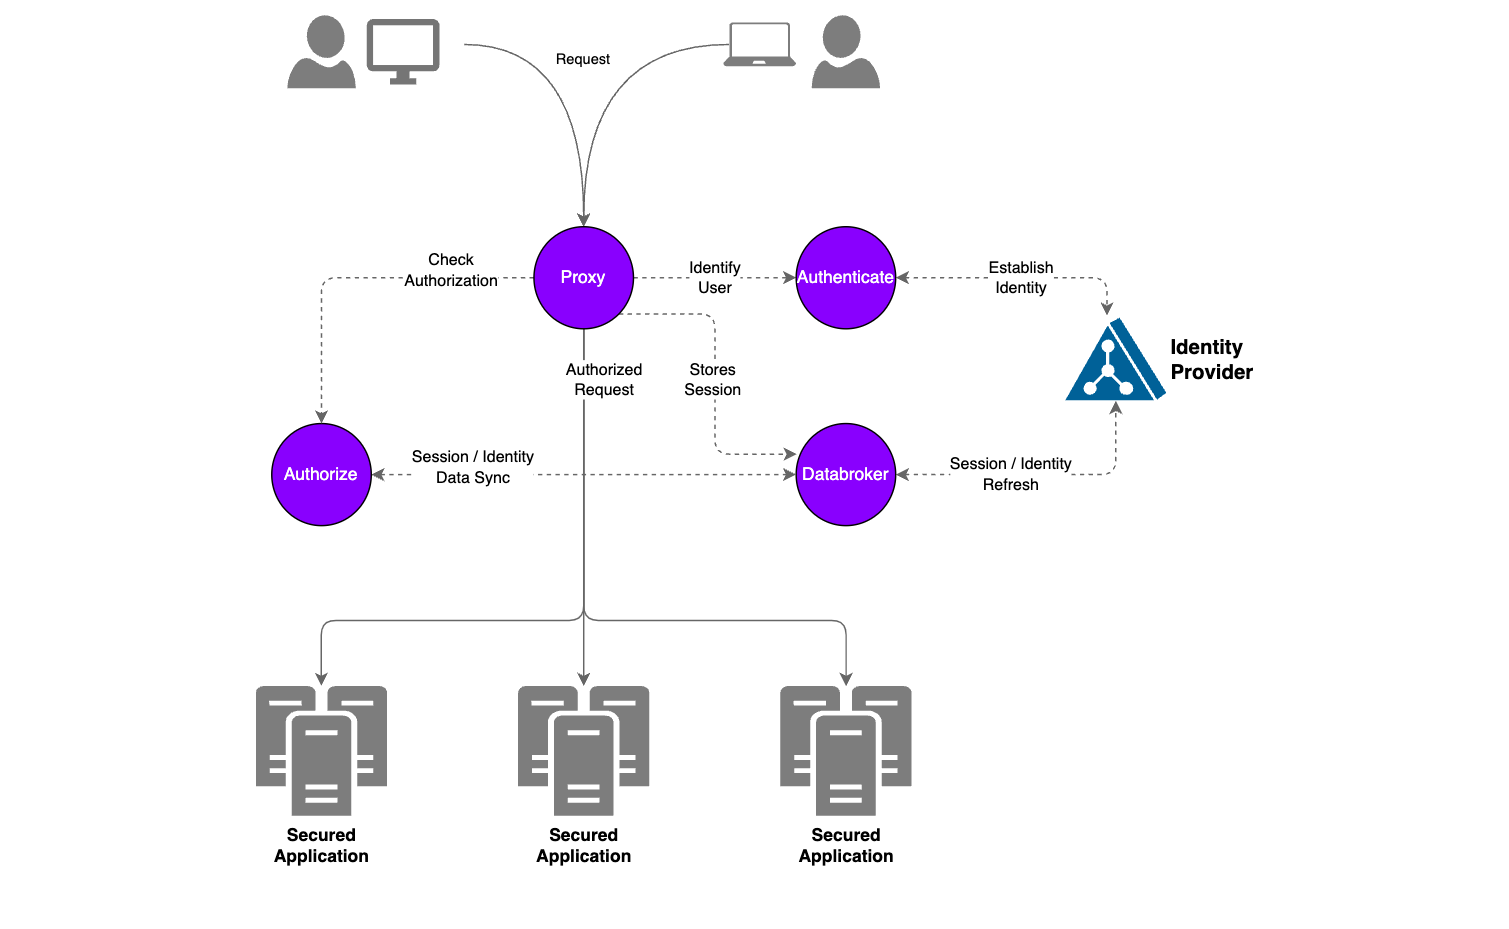
Pomerium puts every internal application behind a single identity-aware proxy, so engineers reach dashboards, admin panels, and databases through their browser with no VPN client and no network-level trust. Sign-in flows through your existing identity provider, including Google, Okta, Azure AD, GitHub, GitLab, and any OpenID Connect service, with sessions verified continuously rather than once at login. Each route carries its own policy: restrict the finance tool to the finance group, require a specific email domain for the admin console, or allow read-only paths more broadly. Authorized requests pass identity headers the application can trust, and every access decision is logged for audit. TCP routes extend the same sign-in and policy checks to SSH, PostgreSQL, MySQL, and RDP connections through a small client or a browser-based terminal. In Kubernetes, Pomerium doubles as an ingress controller, applying the same policies to services as annotations on ingress resources. Mutual TLS between the proxy and backends, encrypted sessions, and short-lived credentials replace shared passwords and flat networks. Teams roll it out as one all-in-one binary or split the proxy, authorize, authenticate, and cache services across machines as traffic grows. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Benefits
- VPN Free Internal Access
- Users open internal applications in a browser after signing in through your identity provider, so there is no VPN client to install, no tunnel to babysit, and no flat network.
- Policy Per Application Route
- Each route enforces its own rules about which users, groups, and domains may connect, evaluated on every request with identity and context instead of network location.
- One Front Door For Everything
- Web apps, SSH servers, and databases all sit behind the same sign-in and policy layer, giving one audit trail and one access model across the whole estate.
- Built For Kubernetes Too
- The same proxy runs as a Kubernetes ingress controller, so cluster services get identity-aware access through ingress annotations without a second tool to learn or operate.
Features
- Identity Provider Integration
- Connects to Google, Okta, Microsoft, GitHub, GitLab, OneLogin, and generic OpenID Connect providers, with directory sync for group based policies and user attributes.
- Per-Route Authorization Policies
- A policy language controls access by user, group, domain, path, and request attributes, decided by the authorize service on every single request.
- TCP And SSH Proxying
- TCP routes carry SSH, PostgreSQL, MySQL, Redis, and RDP through the proxy with the same authentication and policy checks as web traffic.
- Kubernetes Ingress Controller
- Runs as an ingress controller that reads standard ingress resources, applying Pomerium authentication and authorization to services inside the cluster.
- Identity Headers And JWTs
- Signed JSON Web Tokens and identity headers tell upstream applications exactly who the verified user is, so apps can drop their own login logic.
- Audit Logging Everywhere
- Structured logs record every authentication and authorization decision with user, route, and outcome, ready to ship to your existing log tooling.