Vaultwarden
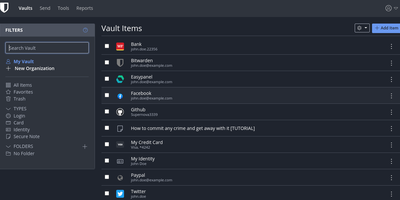
The Bitwarden server, reimplemented in Rust: Vaultwarden (formerly bitwarden_rs) is the unofficial lightweight edition. It speaks the same wire protocol as the official server, so every official Bitwarden client - browser extensions, iOS, Android, desktop, and the bw CLI - connects without modification, while the server itself runs as a single container against SQLite (or MySQL/MariaDB/PostgreSQL) instead of the official multi-container stack that wants gigabytes of RAM. Features Bitwarden gates behind paid tiers ship free: organizations with collections, groups, member roles, and policies; TOTP code storage; file attachments; Bitwarden Send; Emergency Access; event logs; and admin password reset. Two-factor options cover authenticator apps, email, FIDO2 WebAuthn, YubiKey, and Duo, and OIDC-based SSO landed natively in v1.35.0. Zero-knowledge encryption is unchanged - vault data is encrypted client-side and the master password never reaches the server. Attachments and Sends store on local disk or S3-compatible backends, an admin panel manages users and server settings, and backup is copying one data directory. Suited to individuals and teams up to roughly 50 users.
Passbolt
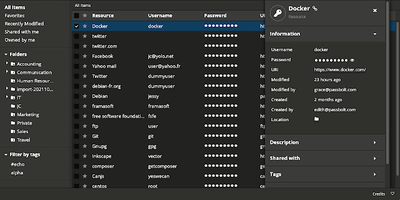
Security-conscious IT departments pick Passbolt for its cryptography: every user holds an OpenPGP key pair, and shared credentials are encrypted individually to each recipient's public key - real end-to-end encryption, not a vault password handed around. All crypto runs client-side in the mandatory browser extension (distributed and signed through the Chrome and Firefox stores, deliberately separating the crypto code from the server that stores ciphertext); private keys and passphrases never touch your instance, and the server admin cannot read a single secret. Authentication uses the challenge-based GpgAuth protocol, secrets are digitally signed to verify sender integrity, and metadata encryption extends protection to resource names and URLs. Day to day it behaves like a polished commercial manager: auto-fill and auto-save in forms, strong password generation, anti-phishing protection, TOTP storage, folder hierarchies shared per-user or per-group with fine-grained permissions and instant cryptographic revocation. Native iOS, Android, and desktop apps ship alongside a JSON API, CLI, and SDKs for CI/CD secret retrieval and rotation. The PHP server runs on MariaDB and is AGPL-licensed open source - including the paid tiers' codebase - with published security audits.
AliasVault
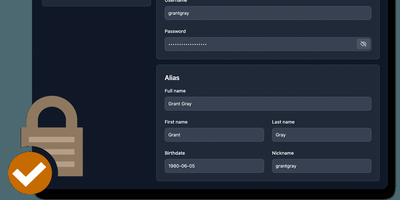
Sign up for a new service and you face a familiar choice: hand over your real email and get spam-listed forever, or generate a throwaway alias that dies when you close the tab. AliasVault eliminates that trade-off by combining a password manager with a built-in email server, so every website gets a unique identity (random email, generated name, strong password) and incoming emails land directly in your encrypted vault rather than your primary inbox. Creating a new alias takes one click: the system generates a random address on your configured domain, a fake identity with name and birthdate, and a cryptographically strong password, all stored in a zero-knowledge encrypted vault that even the server administrator cannot read. Browser extensions for Chrome, Firefox, Edge, Safari, and Brave detect login forms and autofill credentials or prompt you to create a new alias on the spot. Native iOS and Android apps with biometric unlock provide mobile access to your vault and integrate with the operating system's autofill framework. The built-in TOTP authenticator generates time-based one-time codes without needing a separate app. Import existing credentials from other password managers through standard export formats, and export your vault data at any time for full portability. Self-hosting via Docker with your own email domain gives you complete control over where alias mail is received and stored, with no third-party dependencies. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Bitwarden
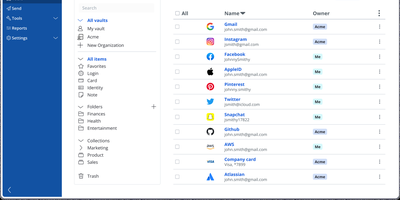
Backed by nearly 20,000 GitHub stars and ranked number one in G2's Enterprise User Satisfaction for eleven consecutive quarters, Bitwarden is the open-source password manager trusted by millions worldwide. The zero-knowledge encryption architecture ensures all vault data — passwords, passkeys, credit cards, identities, secure notes, and file attachments — is encrypted exclusively on client devices using AES-256 with PBKDF2-SHA256 or Argon2id key derivation and RSA-2048 for organization key exchange. Cross-platform clients span a web vault, browser extensions for Chrome, Firefox, Safari, Edge, Opera, Vivaldi, and Brave, native desktop apps for Windows, macOS, and Linux, mobile apps for iOS and Android, and a CLI for scripting. Bitwarden Send enables time-limited, password-protected sharing of text and files, while the built-in TOTP authenticator generates two-factor codes alongside stored credentials. Enterprise deployments integrate with identity providers through SAML 2.0 and OpenID Connect SSO, automate provisioning via SCIM or Directory Connector supporting LDAP, Active Directory, Azure AD, Okta, and OneLogin, and enforce security policies with custom roles and granular permissions. Emergency access allows designated contacts to request vault view or takeover through configurable waiting periods with cryptographic key exchange. The Secrets Manager stores API keys, tokens, and infrastructure credentials with native GitHub Actions, GitLab CI/CD, Ansible, and Terraform integrations. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
KeeWeb
Your KeePass vaults, opened from any browser: KeeWeb reads, edits, and creates standard KDBX files, so it works with the same databases as KeePass and KeePassXC without conversion or lock-in. Self-hosting the web app gives you a password manager reachable from any modern browser, including mobile, with no client installation and no third-party cloud in the loop. All KDBX cryptography runs client-side; the server just serves the static app. Open multiple vault files simultaneously and search them all from one box, with advanced options covering specific fields, password history, and regular expressions. Vaults load from local files, your own server (WebDAV), or Dropbox, Google Drive, and OneDrive, with automatic sync - and files are cached for offline use, so a dropped connection never locks you out; changes resync once you're back online. Day-to-day niceties include a configurable password generator, protected fields that stay masked and are held in memory more defensively, entry history, tags with easy input, drag-and-drop attachments, and per-entry icons with favicon fetching. The optional KeeWeb Connect extension (Chrome, Firefox, Edge, Safari) autofills credentials using the keepassxc-protocol. MIT-licensed with matching desktop apps for macOS, Windows, and Linux.
TeamPass
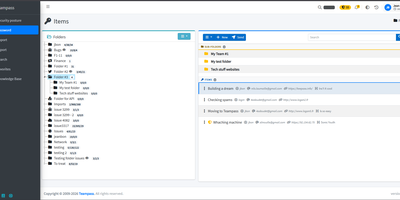
TeamPass is a dedicated on-premise password manager built specifically for teams that need collaborative credential sharing with fine-grained access controls. Role-based access control defines user permissions through hierarchical folder trees where each folder and item can be independently set to write, read, or no access against assigned roles, enabling organizations to segment credentials across departments without exposing sensitive data. Passwords are encrypted in the database using Defuse PHP Encryption with per-installation unique saltkeys, while two-factor authentication supports configurable RFC 6238 TOTP profiles with custom digits, period, and algorithm settings alongside Duo Security and Yubico hardware key integration. LDAP and Active Directory native integration enables enterprise SSO with automatic user provisioning. The Security Posture Dashboard surfaces weak, reused, breached, overdue, no-expiry, widely-shared, and unreadable credentials through indicator cards that filter and deep-link directly to items. Secure Send creates expiring, view-count-limited one-time links optionally protected by recipient passphrases for sharing credentials with external users. Import from Bitwarden, LastPass, 1Password, and KeePassXC through a unified source selector, with export to encrypted offline files. Email notifications, password expiration policies, custom fields, and attachment support round out item management. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL-3.0 licensed.