Cupdate
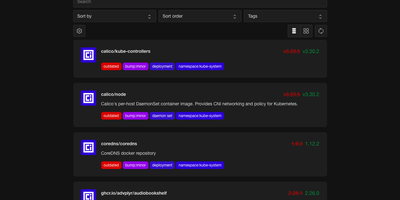
Cupdate keeps a watchful eye on every container image you run, reporting which ones are outdated or vulnerable while deliberately never touching the update button itself. Point it at a Kubernetes cluster, a Docker socket, or Podman hosts (local or remote, one or several) and it inventories every image in use with no configuration to write. Each image is matched against its registry to find the newest available version, and the dashboard shows the gap between what you deployed and what you could be running, with release notes inline so the decision to upgrade takes seconds instead of a changelog hunt. Vulnerability data is layered on top from four sources: Docker Scout for Docker Hub images, Clair for participating Quay images, GitHub Advisories for images tied to repositories, and osv.dev correlation for images shipping SBOMs. A dependency graph explains why each image exists in your stack by showing which workloads pull it, which ends the "can I delete this?" guessing game. Subscribe to the RSS feed to hear about new releases passively, query the REST API to drive scripts that update compose files or kustomizations, or surface outdated and vulnerable counts in a Homepage dashboard widget. Prometheus metrics and traces are available when you want the watcher itself watched. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Deploy