Prowler
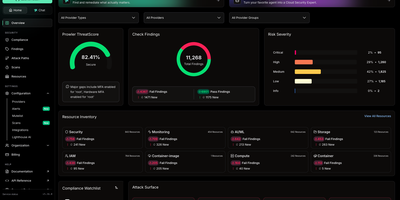
Point it at your cloud accounts and it returns a ranked list of what is misconfigured, mapped to the standards auditors ask about. Connect providers like AWS, Azure, Google Cloud, Kubernetes, Microsoft 365, and GitHub, launch a scan or schedule recurring ones, and read the results on an overview with a ThreatScore gauge, severity bars, and a resource inventory by category. The Findings page groups failed checks, expands each group into the affected resources, and lets teams mute noise, triage status, send groups to Jira, and create alerts that email or message people after each scan. Compliance pages score every framework from CIS and NIST to PCI DSS, SOC 2, HIPAA, GDPR, and ISO 27001, with a watchlist for the ones you care about and downloadable reports. Attack Paths draws a graph from IAM roles and policies to outcomes like code execution, using a Neo4j graph database filled by AWS scans. A built-in AI assistant answers questions about critical findings and compliance gaps with the model provider you configure. Organizations, roles, and API keys keep access tidy. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Deploy