Categories
Self-Hosted DevSecOps Compliance Vulnerability Management Security Posture Management AWS Security Cloud Security Kubernetes SecurityStars
Forks
Watchers
Developer links
Prowler
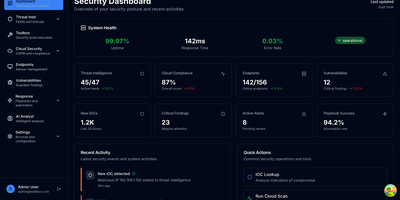
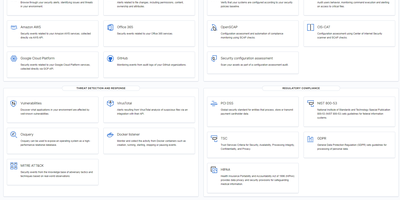
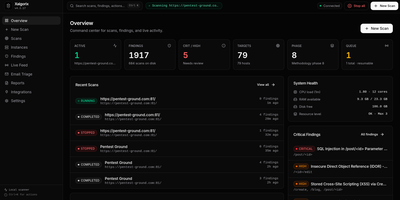
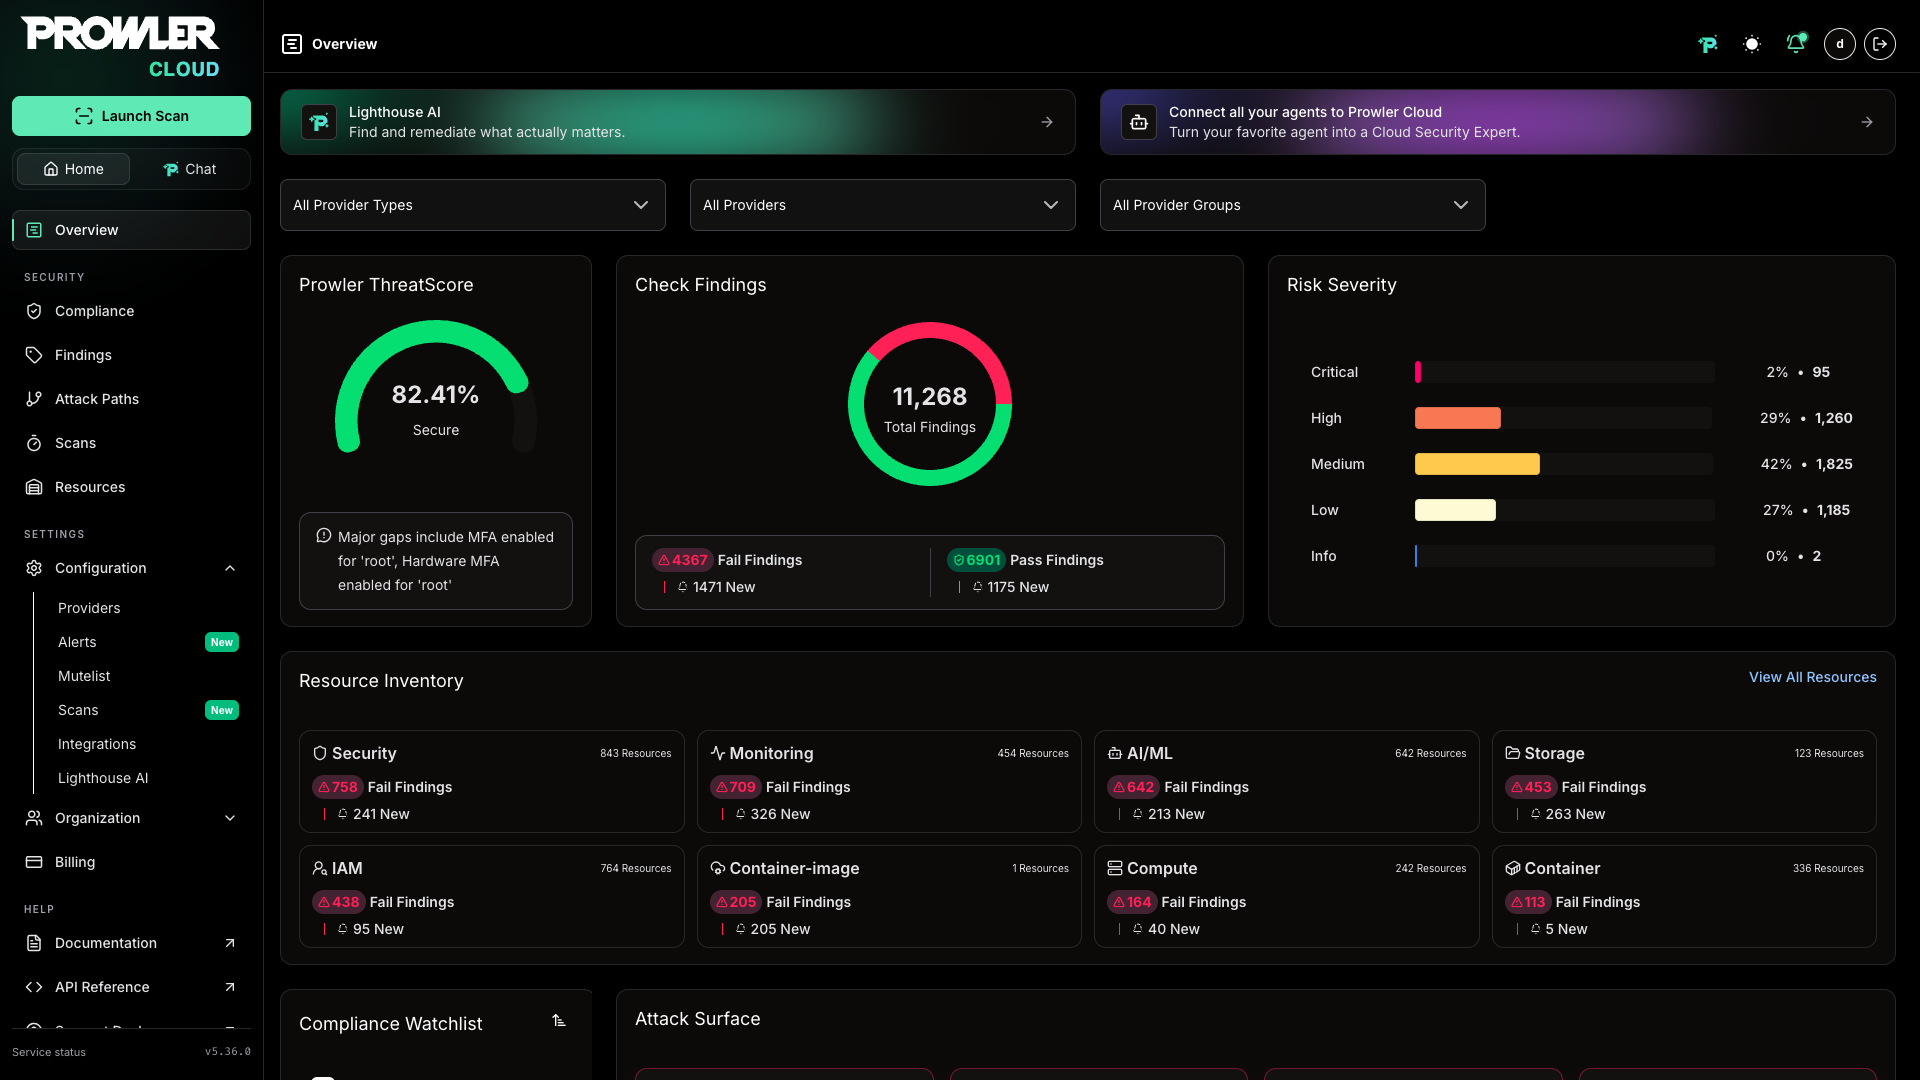
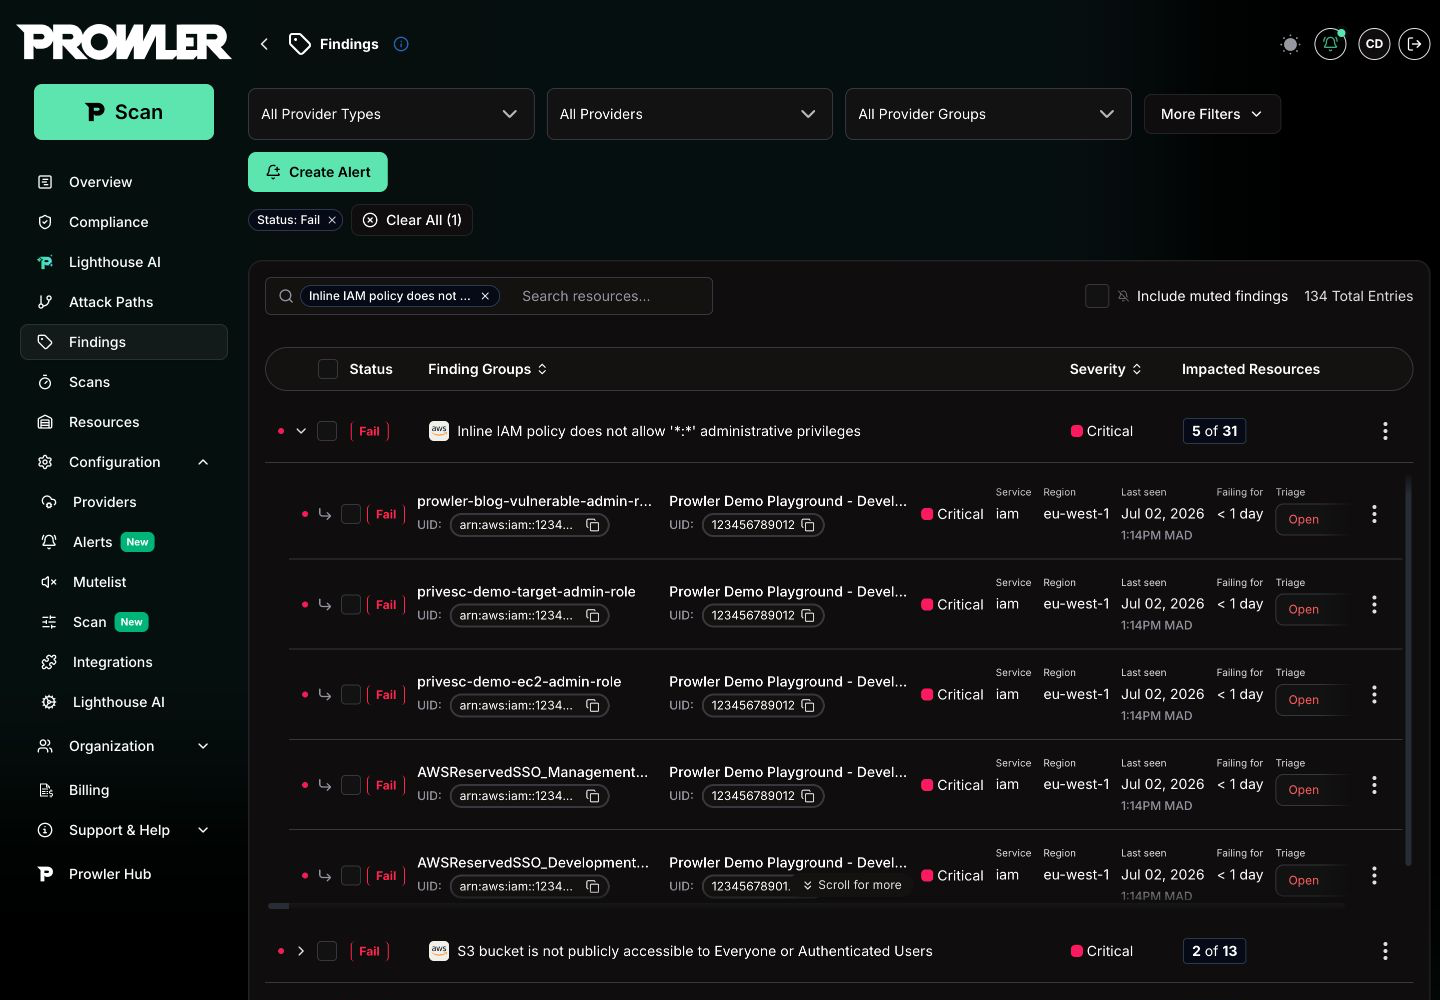
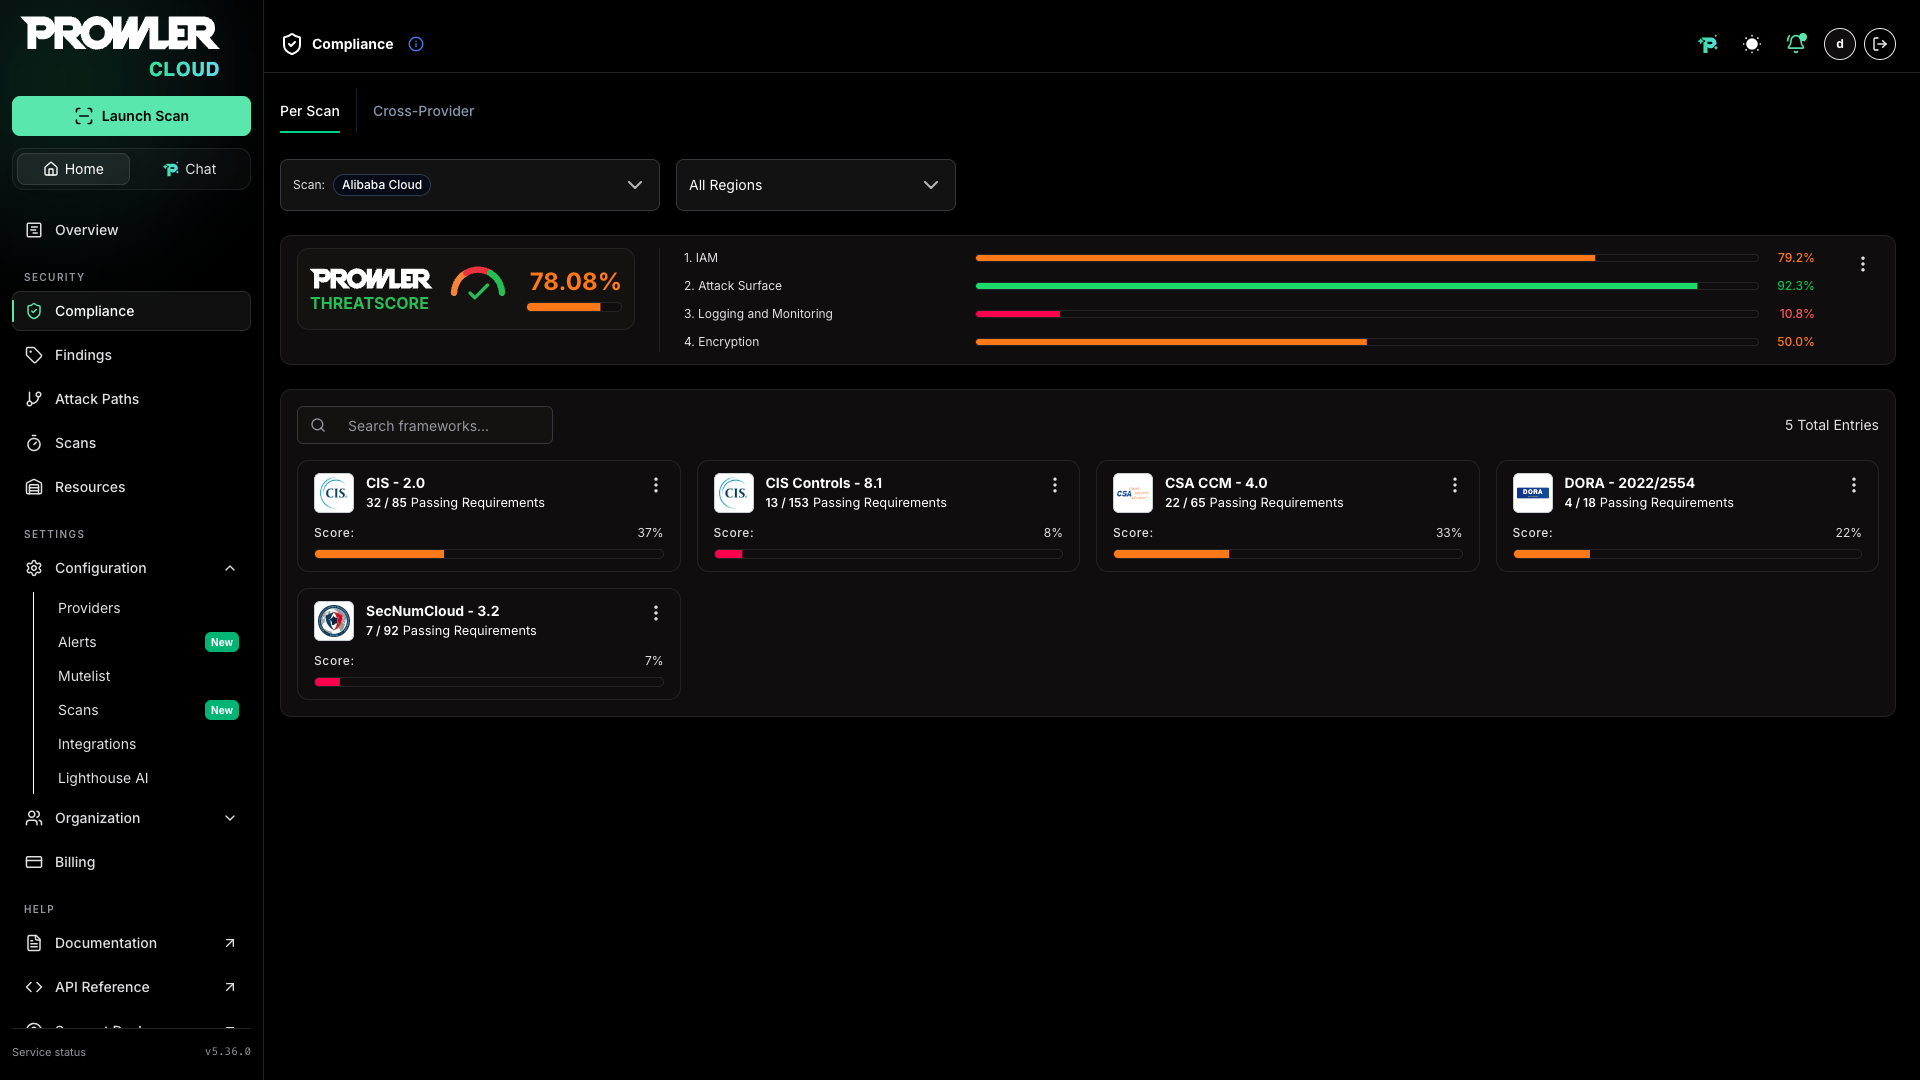
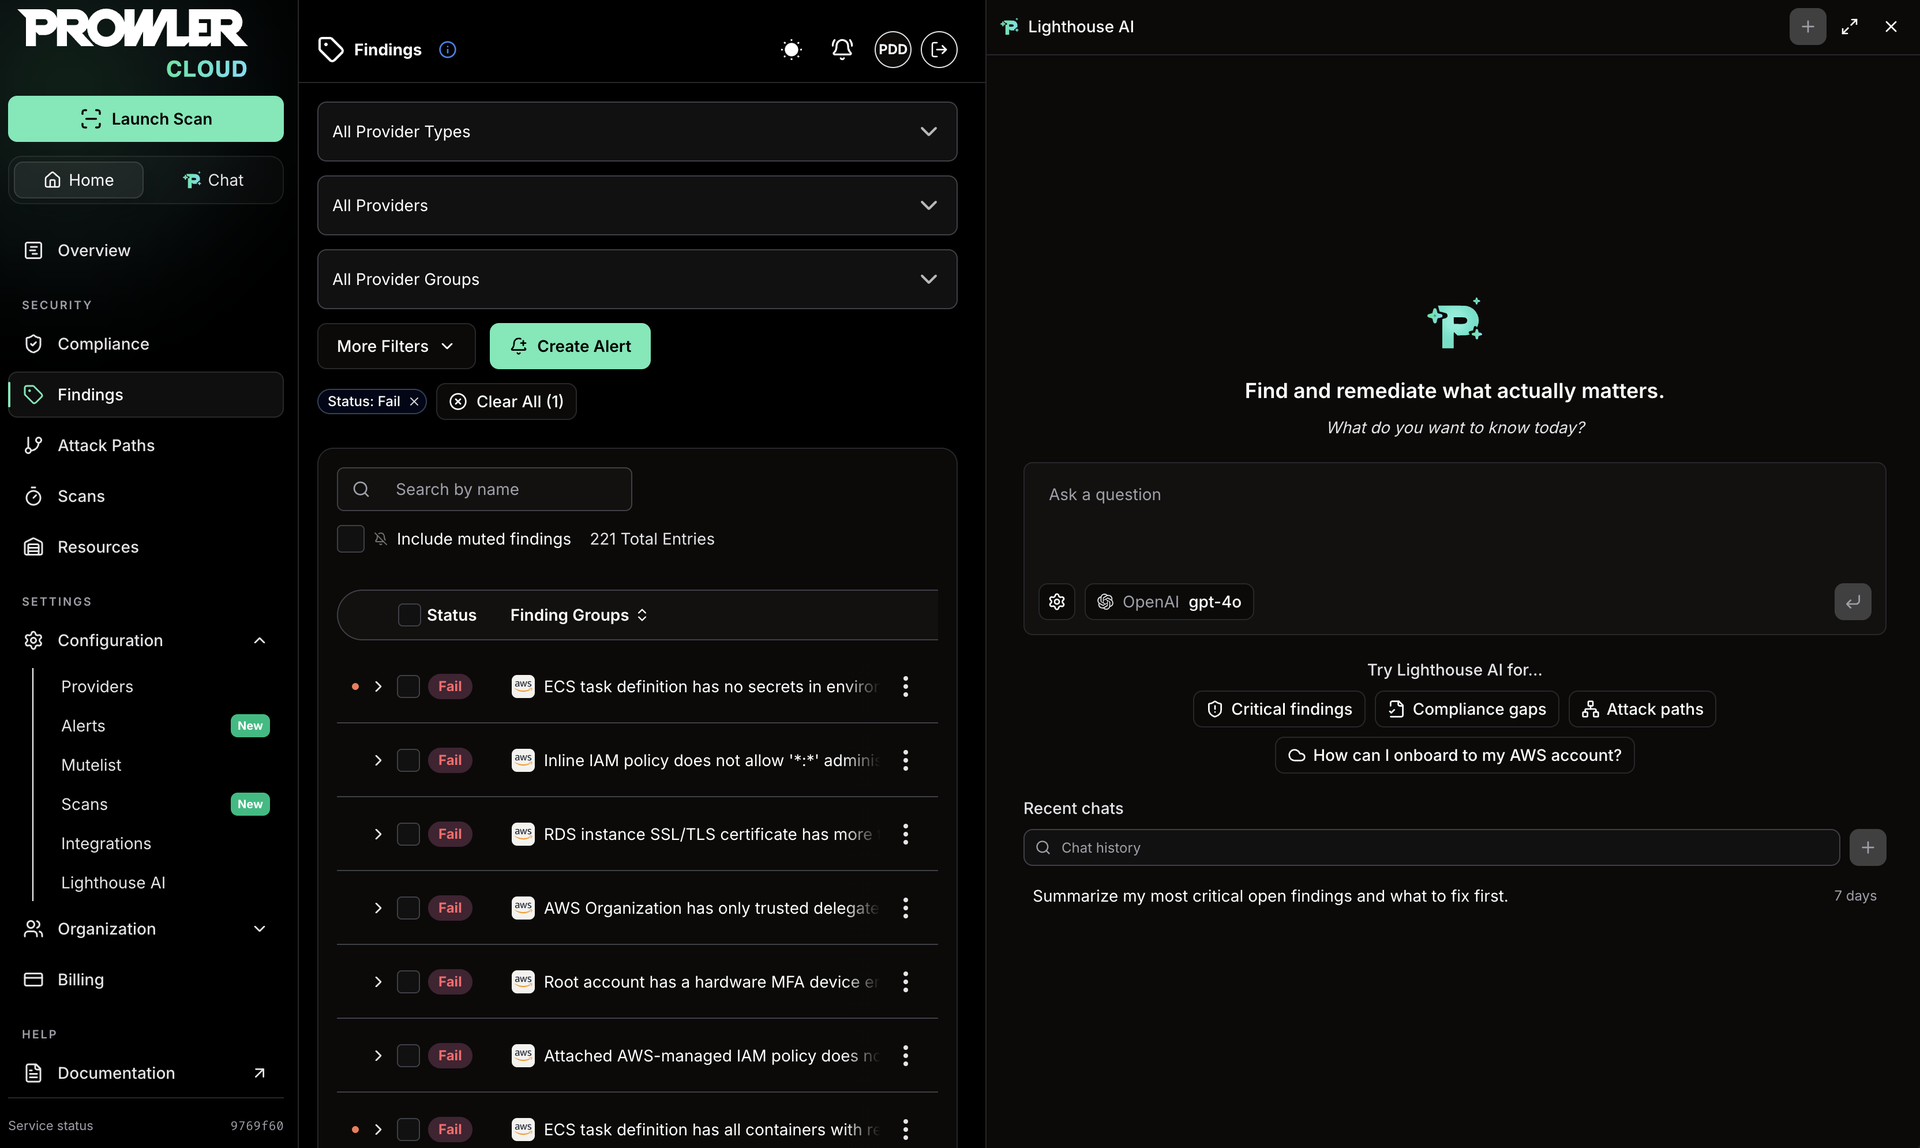
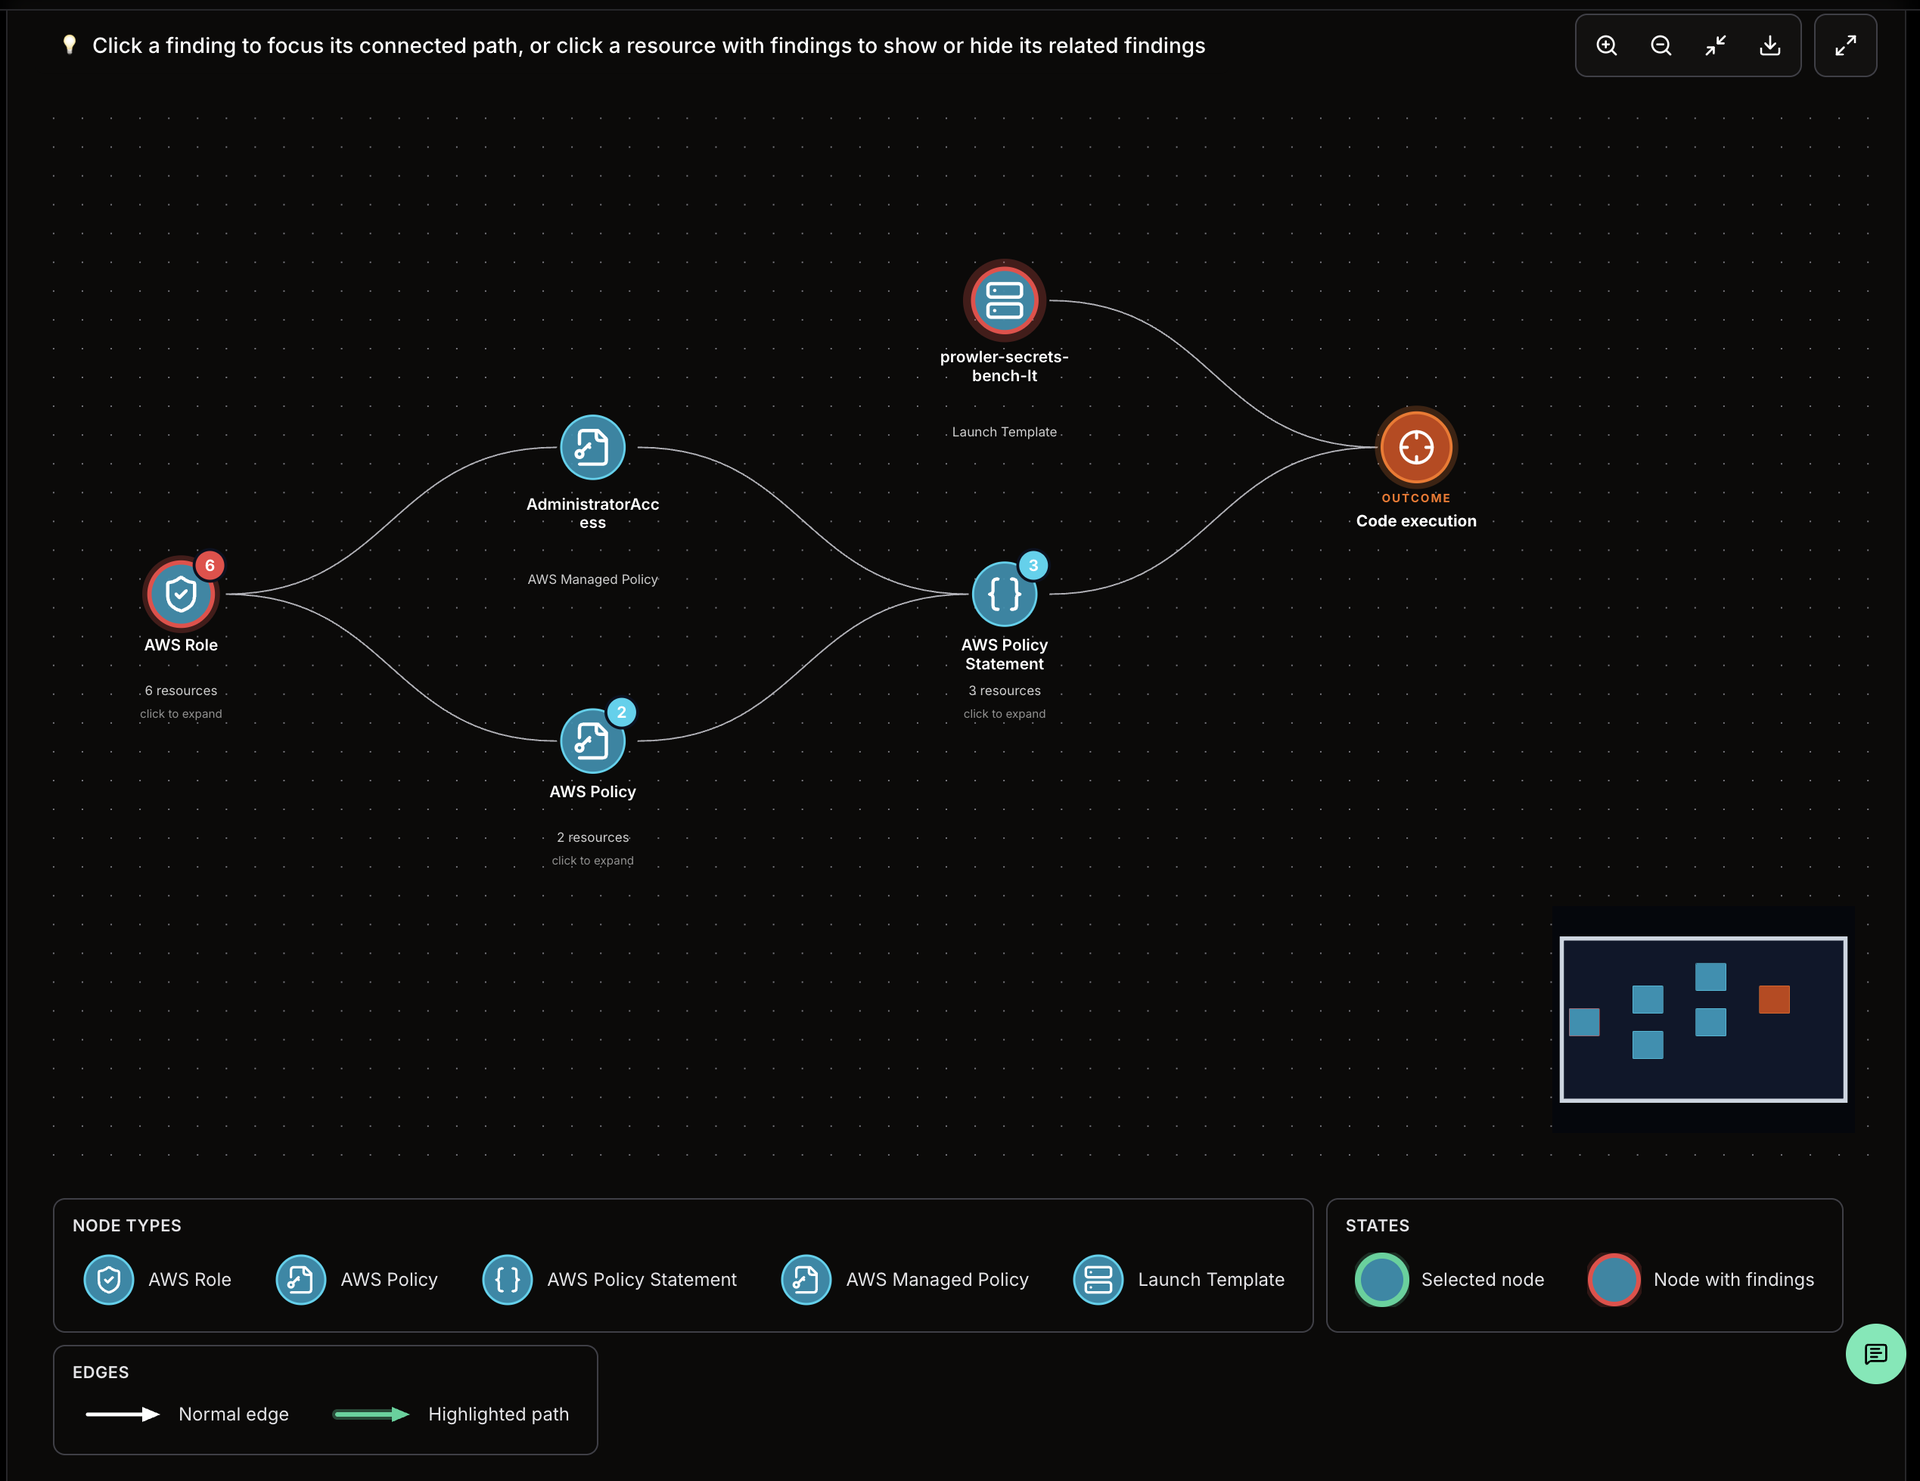
Point it at your cloud accounts and it returns a ranked list of what is misconfigured, mapped to the standards auditors ask about. Connect providers like AWS, Azure, Google Cloud, Kubernetes, Microsoft 365, and GitHub, launch a scan or schedule recurring ones, and read the results on an overview with a ThreatScore gauge, severity bars, and a resource inventory by category. The Findings page groups failed checks, expands each group into the affected resources, and lets teams mute noise, triage status, send groups to Jira, and create alerts that email or message people after each scan. Compliance pages score every framework from CIS and NIST to PCI DSS, SOC 2, HIPAA, GDPR, and ISO 27001, with a watchlist for the ones you care about and downloadable reports. Attack Paths draws a graph from IAM roles and policies to outcomes like code execution, using a Neo4j graph database filled by AWS scans. A built-in AI assistant answers questions about critical findings and compliance gaps with the model provider you configure. Organizations, roles, and API keys keep access tidy. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Benefits
- See Cloud Risk In One Score
- A ThreatScore gauge, severity breakdown, and resource inventory turn thousands of checks into a clear picture of which accounts and services need attention first.
- Answer Auditors With Evidence
- Every scan maps to frameworks like CIS, NIST, PCI DSS, SOC 2, HIPAA, and ISO 27001, so teams can show pass and fail status per requirement.
- Keep Findings Data Private
- Scan results, credentials, and graphs stay in your own database and server, which suits regulated teams that cannot send cloud inventory to outside services.
- Fix What Matters First
- Grouped findings, manual triage status, Jira hand-off, and attack path graphs help engineers pick the problems that actually open a route to sensitive resources.
Features
- Multi-Cloud Scan Engine
- Run checks across AWS, Azure, Google Cloud, Kubernetes, Microsoft 365, and GitHub, on demand or on a schedule, with remediation guidance for each failed check.
- Grouped Findings Table
- Expand each failed check to see impacted resources, filter by provider, region, and severity, mute findings, set triage status, and add notes.
- Compliance Dashboards
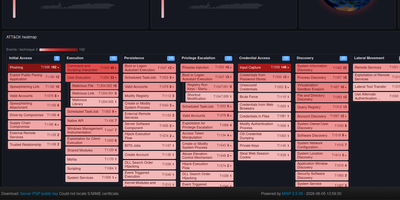
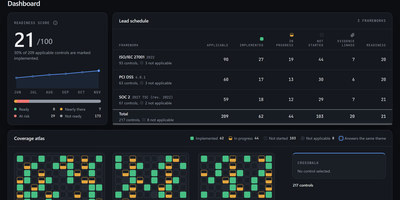
- Browse frameworks per scan or across providers, view ThreatScore pillars, pin favorites to a watchlist, and download CSV or PDF reports.
- Attack Path Graphs
- Select a query to visualize privilege escalation chains from roles and policies to outcomes, then zoom, expand nodes, and focus on connected findings.
- Alerts And Integrations
- Create alerts from filtered findings with email or channel destinations, and connect Jira, Slack, and S3 to route results into existing workflows.