tirreno
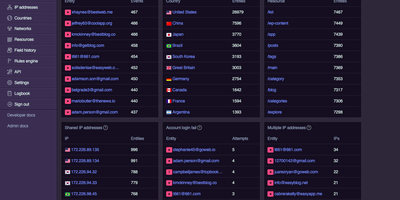
tirreno watches what accounts actually do inside your product, then surfaces the ones that look like account takeover, credential stuffing, fake signups, or insider abuse. Your backend reports events such as logins, registrations, page views, searches, email changes, and field edits through an SDK or one HTTP call, and a scheduled job turns them into per-user context: devices, IP addresses, sessions, and connected identities. Preset rules cover account takeover, credential stuffing, content spam, bot detection, multi-accounting, promo abuse, dormant accounts, API protection, and high-risk regions, and you can add rules of your own. Each rule adds to a risk score, and thresholds decide whether a user is flagged for manual review or suspended automatically. The review queue lists who needs a look, and the single user view shows behaviour patterns, risk scores, connected identities, and an activity timeline. A field audit trail records what changed and when, which supports compliance reviews, while the logbook lists every API request the instance received. Your application can ask a blacklist endpoint whether a user or IP should be blocked before it responds. An optional IP enrichment pack adds geolocation, ISP, and VPN or proxy detection. All event data stays on your own server. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Deploy