PentaGI
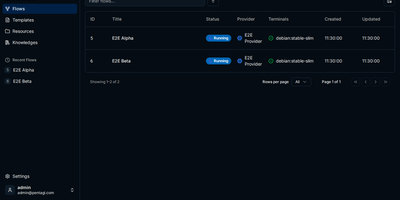
Autonomous red team execution without manual script coordination is what PentaGI delivers through a multi-agent penetration testing platform engineered for automated security assessments. Security engineers configure testing scopes, target IP ranges, domain lists, and rules of engagement through an interactive web console with real-time execution graphs. Autonomous agent personas break down high-level assessment goals into discrete tactical phases, orchestrating network port discovery, service banner fingerprinting, web application crawling, and CVE verification. Specialized agents query integrated Graphiti knowledge graphs and local vulnerability repositories to synthesize attack paths, validate exploitability, and confirm finding veracity before issuing alerts. Operators monitor live agent terminal streams, inspect sandboxed tool executions, and adjust active LLM provider routes across OpenAI, Anthropic, or local Ollama endpoints. The template editor allows red teams to compose reusable testing playbooks with customizable security prompt chains, safety constraints, and automated remediation reporting. Audit logs capture full command histories, raw tool outputs, and LLM reasoning steps to generate compliance-ready technical documentation. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
cvENGINE
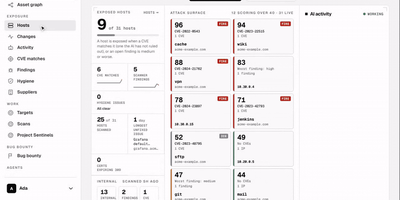
cvENGINE takes a domain name and returns a verdict on which of today's exploited vulnerabilities can actually reach you, with evidence attached. Continuous discovery builds a Shodan-style inventory of subdomains, IPs, ports, products, versions, certificates, and technologies, then rates every CVE as fire, smoke, or ice from real exploitation sources and scores each host from 0 to 100. Read-only validation reproduces a finding and records the exact command used. Optional AI triage sorts matches into confirmed, likely, or needs validation. A live dashboard, a change timeline with screenshot diffs, saved searches with alerts, and one-click PDF reports keep teams current. Sentinels run scans from other machines, including inside private networks, and an optional OpenVAS add-on extends coverage. Hygiene checks cover TLS, email and DNS records, exposed databases, cloud storage buckets, and WordPress sites. Organizations, roles, two-step sign-in, a REST API, and Slack, Discord, Telegram, and Lark alerts support shared use. A bug bounty workbench imports program scope and drafts reports. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL-3.0 licensed.
OpenCTI
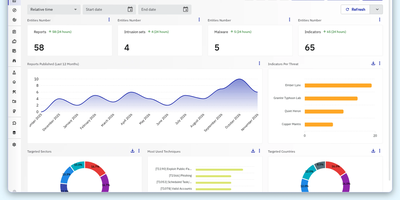
OpenCTI gives security teams one place to see which adversaries target their sector, how those groups operate, and which vulnerabilities they exploit. Reports, feeds, and analyst notes become linked STIX 2.1 entities such as intrusion sets, malware, ATT&CK techniques, vulnerabilities, and indicators, each carrying its source, confidence level, and TLP marking. Investigations start from a few entities and expand node by node, letting analysts pivot from an indicator to the campaign, malware family, and victim sector behind it. Threat pages show an ATT&CK matrix with the techniques in use highlighted, and custom dashboards chart any query as time series, distributions, or lists with one-click presets. Connectors import MITRE datasets, MISP, AlienVault, and CVE data, enrich observables through Shodan or DomainTools, and export STIX 2.1, CSV, or PDF files. TAXII collections, CSV feeds, and live streams publish selected knowledge to your SIEM or EDR, while RSS, CSV, JSON, and TAXII feeds pull outside intelligence in. Case management tracks incident responses, information requests, and takedown requests with assigned tasks and reusable task templates, and notification triggers alert analysts when watched entities change. A rules engine infers new relationships, decay rules age out stale indicators, and a GraphQL API with a Python client supports automation. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Domain Watchdog
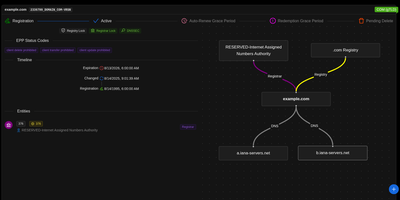
When the domain you want is already taken, Domain Watchdog tracks its history, warns you as it changes, and can try to register it as soon as it becomes available. Searching any domain returns its registrar, status, nameservers, and registration events from RDAP, the structured JSON successor to WHOIS. A timeline lays out the full lifecycle, from creation through renewals and transfers to final deletion, while deletion forecasting orders tracked domains by their expected drop window. Watchlists group domains with the events that matter, send alerts by email or as webhooks to Slack, Mattermost, or Discord, and publish an iCal feed plus RSS feeds for events and EPP status. Attach a connector for OVH, Gandi, Namecheap, AutoDNS, or Name.com, and an expired domain on the watchlist triggers an order attempt through that provider's API. The app also lists ICANN-accredited registrars and TLDs, and rate limiting with caching minimizes RDAP requests. Administrators can cap watchlists, domains per watchlist, and webhooks per watchlist, toggle public RDAP lookups, and add custom static content to the instance. Scripts can manage watchlists and connectors, search domains, and request user tokens through the documented REST API. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Velociraptor
Hunting for a suspicious file, process, or registry key across every endpoint becomes a single hunt in Velociraptor, an endpoint visibility and digital forensics platform. A web console sends tasks to clients on Windows, Linux, and macOS machines, which hold a persistent connection and run each task as soon as it is issued. A hunt runs a VQL artifact, one of more than 400 built in, across selected endpoints, picks up machines that reconnect later, and tracks which hosts have answered. Each hunt and collection opens into a notebook where markdown and live VQL cells group, filter, and timeline the results. A virtual file system browses a client's directories and fetches files through file, NTFS, and registry accessors, with hex and text viewers. Offline collectors bundle chosen artifacts into one binary that writes an optionally encrypted container for later import, suiting machines that never reach the server. Client event queries stream telemetry such as DNS lookups to the server, and server event queries can alert Slack, email, Elastic, or Splunk. Quarantine confines a host's network traffic to the Velociraptor server, and the Shell page runs commands on it. Sign-in works through Google, Azure, GitHub, OIDC, or SAML, with reader, analyst, investigator, and administrator roles. Responders reach for it during threat hunts, compromised host triage with KapeFiles targets, and dead disk image analysis. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
CISO Assistant
Compliance audits, risk registers, vendor reviews, and evidence usually sit in separate spreadsheets; CISO Assistant keeps them in one connected, self-hosted GRC platform. Run audits against more than 200 frameworks, including ISO 27001, NIST CSF, SOC 2, PCI DSS, NIS2, DORA, GDPR, and HIPAA, scoring each requirement and attaching evidence and applied controls. A mapping from the library projects a finished audit onto another framework, so the same questions are not answered twice. Risk assessments rate scenarios on configurable matrices, record current and residual levels, link the controls that treat them, and open matrix and action-plan views, plus EBIOS RM studies and quantitative analysis. Applied controls, policies, and recurring tasks carry owners and due dates, evidence attaches to them, and a month-by-month control plan shows what is outstanding. Third-party risk covers vendors, solutions, contracts, criticality tiers, and questionnaires that vendor representatives answer themselves. Assets, business impact analyses, incidents, and a GDPR register with DPIA screening share the same workspace. Analytics tabs list what needs attention, and a workflow builder can email scheduled digests or react to events. An MCP server with 139 tools lets Claude, ChatGPT, or LM Studio read and change records, and an optional chat assistant answers questions with a local or hosted model. SAML or OIDC single sign-on, MFA, a REST API, and a CLI cover access and automation. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Xalgorix
Xalgorix delivers AI-driven penetration testing that proves vulnerabilities exist rather than guessing, pairing an autonomous LLM agent with an independent exploit verifier that re-exploits every finding before it reaches your report. The 22-phase methodology mirrors how a skilled human pentester works through an engagement, covering reconnaissance, subdomain enumeration, port scanning, web crawling, parameter fuzzing, SQL injection testing, XSS detection, authentication bypass, API testing, and more. Select all phases or pick specific ones per target. The platform ships with 85+ offensive security tools preinstalled (nmap, nuclei, httpx, subfinder, katana, ffuf, gobuster, sqlmap, masscan, dalfox, feroxbuster) plus 14 built-in agent tools for browser automation, terminal execution, and note-taking. Connect your own LLM provider (OpenAI, Anthropic, DeepSeek, Gemini, Groq, Ollama, or MiniMax) so no scan data or target information leaves your infrastructure. The web dashboard on port 9137 provides live WebSocket telemetry showing tool calls, agent reasoning, and findings as scans progress. A findings index with CVSS scoring and severity filters organizes results, and branded PDF reports include your company name and logo. Wildcard and multi-target scans handle red team attack-surface mapping, while source-code scanning audits repositories directly without requiring a deployed target. A REST API enables scripted scans and SIEM pipeline integration, and webhooks push notifications to Discord or Telegram. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
CTFd
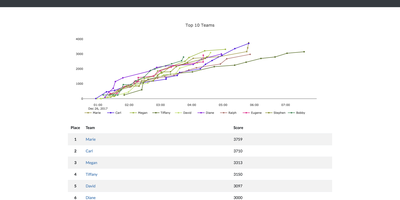
Starred by over 6,500 users on GitHub and trusted by organizations including Toyota, CTFd has been the leading open-source platform for hosting cybersecurity competitions since 2015, providing everything needed to run professional Capture The Flag events through a clean web-based administration panel without touching a database query. The framework supports both individual and team-based competitions with automatic tie resolution, configurable score freezing, and scoregraphs comparing the top teams with detailed progress tracking. Challenge creation offers static and regex-based flags, dynamic scoring that adjusts point values based on solve count, unlockable hints purchasable with points, file attachments uploaded to local storage or Amazon S3-compatible backends, and challenge attempt limits with automatic bruteforce protection. Version 3.8 introduced challenge logic fields controlling flag submission behavior with any, all, and team modes, integrated dynamic scoring into the standard challenge type, participant ratings and reviews on challenges, and admin-stored challenge solutions viewable after competition. The Markdown-based content management system enables custom pages for rules, FAQs, and resources, while SMTP and Mailgun integration handles email confirmation and password recovery. The plugin architecture supports custom challenge types, flag validators, and scoring algorithms, while the theme system provides complete visual customization. Import and export functionality preserves entire competition configurations for archival and reuse across events. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
OpenAEV
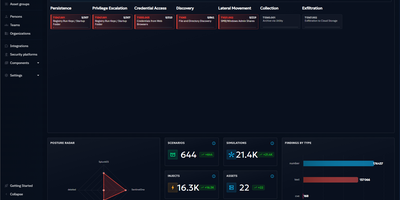
Before an attacker tests your defenses, OpenAEV lets you replay their techniques and see which ones your EDR, SIEM, and people actually catch. Scenarios sequence injects that mirror a threat actor's behavior, and simulations run them once or on a schedule against chosen endpoints, scoring prevention, detection, vulnerability, and human response. Atomic tests fire a single ATT&CK technique from the Threat Arsenal, such as an Nmap scan or a Nuclei CVE scan, and can repeat hourly, daily, weekly, or monthly. A lightweight agent for Windows, Linux, and macOS enrolls each endpoint for testing, while asset groups organize targets by filter. Collectors match EDR, XDR, and SIEM alerts to each inject, marking it prevented or detected, or missed when the expectation window expires. Findings collect scan results and CVE data for each asset, custom dashboards chart posture over time, and scheduled PDF or HTML reports reach stakeholders without platform access. Exercises can also target people through phishing campaigns with landing pages and email templates, SMS, media pressure articles, challenges, and post-run lesson surveys. Pre-built scenarios import from the XTM Hub, or OpenAEV can generate them from OpenCTI security coverage, and a REST API supports automation. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Flowsint
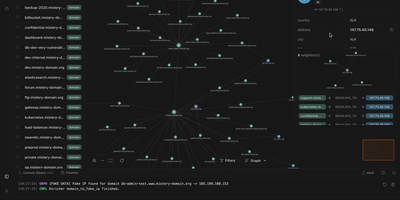
Flowsint turns scattered OSINT leads, like a domain, a username, an email, or a crypto wallet, into one interactive graph that you expand with a right click. Drop an entity on the canvas, run an enricher, and the results appear as new nodes with their relationships already drawn in. Over 30 built-in enrichers cover subdomain discovery, WHOIS and historical records, DNS and ASN lookups, IP geolocation, username searches with Maigret and Sherlock, breach checks for emails and phone numbers, Gravatar profiles, website crawling for contacts and tracking codes, and Ethereum wallet transactions and NFT transfers. Chain enrichers into flows so each output feeds the next step, then replay the same flow on any entity of that type. Missing a source? Write an enricher template in YAML, or describe the API in plain language and let the built-in AI draft it, with API keys kept in an encrypted vault instead of config files. Custom entity types, aliases, tags, JSON import and export, and basic role-based access control make it workable for small teams, and an n8n connector pipes findings into alerts and reports. Double-click the canvas to add items fast, or alt-drag between nodes to link them. Every graph stays on your own server, and no default accounts exist. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
OASM
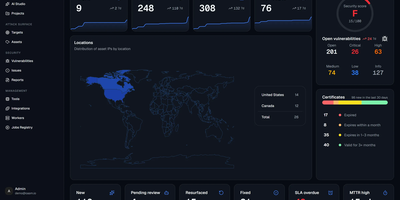
Know every internet-facing asset your team exposes, and which weakness to fix first, before an attacker maps them for you. Add domains, IP addresses, CIDR ranges, or Git organizations as targets, with internal or external scope, and OASM builds one searchable inventory of hosts, ports, services, technologies, URLs, TLS certificates, and screenshots, with a topology graph and CSV export. Scanners such as Nuclei, Nmap, OWASP ZAP, Nikto, WPScan, and Gitleaks install from a marketplace as isolated connector containers, and distributed workers run them on demand or on a schedule. Findings move through new, active, resurfaced, and fixed states with CVSS, EPSS, and SLA timers, and teams accept risk, dismiss, or open remediation issues with priority, assignee, and due date. Projects keep chosen assets scanned on a schedule, when new assets join, or when a vulnerability appears. AI Studio is a security agent that runs on the model you connect: it answers questions from workspace data, writes a plan for your approval, dispatches parallel subagents, runs commands on your workers, and drives a headless browser, filing its findings as proposals a reviewer must approve. An MCP server opens the same workspace data to Claude, Cursor, and VS Code with a workspace API key. Assets sync from AWS, Cloudflare, and Vercel, and alerts reach Slack, Discord, Telegram, or webhooks. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
BugTraceAI
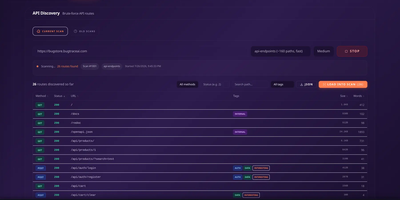
Point an AI pentesting crew at a web app you own and watch it hunt: BugTraceAI plans the checks, sends specialist agents after each weakness class, and brings back evidence you can inspect. A scan moves through six visible phases, from crawling and endpoint discovery through strategy, exploitation and validation, and ends in a findings table where every result carries a severity, a CVSS score and a confirmed status. The web dashboard follows the hunt live as a graph of specialists branching from a coordinating agent, and its API discovery workspace brute-forces routes and loads the interesting ones straight into a scan. Analysts get their own toolbox of more than twenty utilities for poking HTTP traffic by hand, an AI repeater for replaying requests, and ModelLab for comparing models on cost and results. Findings download as a ZIP with the full report, and a terminal workspace with pipeline, findings, agents, timeline and logs views suits keyboard-driven work. Bring your own model through OpenRouter, Anthropic, Z.ai or a local endpoint, and aim the whole suite at the bundled BugStore practice shop when you want to rehearse safely. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
MISP
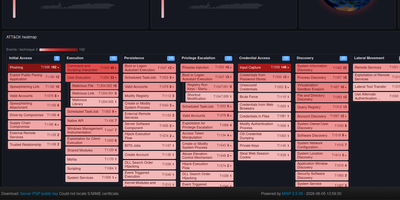
MISP is an open source threat intelligence platform where analysts log indicators and incidents, see how they connect, and share them with trusted organizations. Each case is an event holding attributes and structured objects such as files, network connections, and email messages, with Markdown reports beside the machine-readable data. A correlation engine links events that share values, including fuzzy-hash and CIDR matches, and warning lists flag benign values before they cause false positives. Taxonomies and galaxies tag events with TLP levels, threat actors, malware families, and MITRE ATT&CK techniques. Analysts explore relationships in an event graph and a correlation graph with a timeline, and build drag-and-drop dashboards with maps and ATT&CK heatmaps. Sharing groups control who sees which event, and instances synchronize with partner organizations with distribution settings down to a single attribute. Free-text, URL, bulk, and STIX imports fill the database, and exports reach Suricata, Snort, Zeek, OpenIOC, CSV, STIX 1 and 2, and RPZ zones. A REST API, the PyMISP library, expansion modules, and workflows enrich data and automate publishing. ZeroMQ and Kafka streams announce every change to connected tools. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
VoidAccess
VoidAccess is a self-hosted dark web OSINT platform that takes a single investigation question and returns a sourced report, a searchable relationship graph, and indicators you can load straight into your defenses. One query fans out in parallel to more than a dozen Tor search engines, code hosts, paste sites, security feeds, and curated onion seeds, then follows newly discovered onion links while mandatory safety gates drop prohibited queries, URLs, and content. A thirteen-step pipeline refines the question, collects across English, Russian, and Chinese sources, filters signal from duplicates and dead ends, enriches what survives, and extracts the entities that matter. It recognizes threat actors, ransomware groups, malware families, IP addresses, domains, onion addresses, file hashes, cryptocurrency wallets across seven chains, exposed credentials with secrets masked, messaging handles, CVEs, and MITRE ATT&CK techniques. Everything lands in an interactive graph with communities and infrastructure clusters, so you can start from one wallet or handle and walk the neighborhood it belongs to, cross-referenced against earlier investigations. Scheduled monitors watch for changes and send Telegram or email alerts when your targets move. Finished work exports as STIX 2.1, MISP events, Sigma and YARA rules, CSV, JSON, and bundled IOC packages, with multi-user access for a team. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Knock-Knock
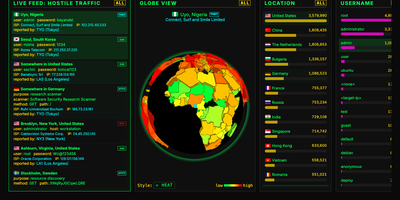
Bots that knock on your server's login ports are always turned away by Knock-Knock, a multi-protocol honeypot that shows every attempt on a live dashboard. Honeypots answer on the standard ports for SSH, Telnet, FTP, RDP, SMB, SIP, HTTP, and SMTP, with MQTT, Node-RED, Modbus, S7, and SNMP as optional extras. Authentication is always rejected, so no bot ever gets a shell. Who is knocking? The live feed shows each attempt's country, username, password, ISP, IP, and protocol. From where? A 3D globe marks the origin in one of six styles, including an extruded country heat map. Trying what? Leaderboards rank countries, usernames, passwords, ISPs, and IP addresses, and a trivia panel explains why bots favor certain credentials. A protocol filter re-slices the feed, globe, and leaderboards together; SIP shows dialed numbers and toll-call destinations, and RDP shows hostnames and accounts. Too fast? Press the space bar to pause, right-click any knock for details, or switch on a virtual Geiger counter that clicks as attacks arrive. Want to fight back? Download hourly 30-day and 365-day blocklists with recipes for CSF, CrowdSec, ipset, nftables, and pfSense, or query the optional API for any IP, CIDR range, or ASN. Several honeypot servers can stream into one aggregated dashboard. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Freki
When a suspicious executable lands in your inbox, Freki gives your team a private place to pull it apart before it touches the network. Upload a sample through the web interface and Freki extracts its fingerprints at once: MD5, SHA-1, SHA-256, SHA-384, and SHA-512 hashes, plus CRC32 and SSDEEP fuzzy hashes for spotting near-duplicate variants. Static analysis then dissects Windows PE files without running them, reporting headers, sections, imported libraries, embedded strings, and capabilities identified in the code. A YARA engine sweeps every sample against your rule sets, so signatures your analysts write flag matching files the moment they arrive. Connect a VirusTotal API key and each report gains antivirus detection results from dozens of engines, placed next to your local findings. The same analysis runs through a REST API, so intake pipelines, mail gateways, and triage scripts can submit files and read verdicts automatically. Analysts discuss findings in community comments attached to each sample, building a shared memory of what a file is and why it matters. Accounts control who may submit samples and call the API, and every analyzed sample stays downloadable for re-examination or sharing with trusted peers. Docker Compose brings the whole platform up behind Nginx with its MariaDB database, keeping live malware samples on your own hardware instead of a public service. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
PRISM
PRISM consolidates passive reconnaissance, credential leak detection, and network asset mapping into a unified operational dashboard to replace fragmented command-line security tools. Analysts can launch simultaneous multi-source investigations against domains, internet protocol addresses, email mailboxes, phone numbers, and online handles to uncover domain registrations, open network ports, cryptographic certificates, and historical web archives. The platform interrogates threat feeds and leak repositories to expose credential leaks, dark web mirrors, and email routing anomalies with automated SMTP mailbox verification. Cross-platform identity engines crawl thousands of social networks and public registries to correlate aliases, discover leaked commit identities, and trace digital footprints across the web. Discovered assets render into interactive entity relationship graphs alongside geographic internet protocol maps to help investigators visualize infrastructure clusters and ownership links. An automated operational security calculator evaluates exposure vulnerabilities across identity, web, and infrastructure vectors, producing an aggregated risk score with granular hardening recommendations. Scheduled watchlists continually monitor target infrastructure, dispatching webhook notifications to chat channels whenever new subdomains, ports, or credential leaks appear. Investigators can export comprehensive audit dossiers as self-contained HTML files, styled PDF documents, or structured spreadsheets. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.