Supabase
With over 107,000 GitHub stars and adoption by teams at Mozilla, 1Password, Peerlist, and thousands of startups, Supabase has become the most widely deployed open-source Firebase alternative — built entirely on PostgreSQL rather than a proprietary NoSQL store. Every project provisions a dedicated Postgres database with 40+ preinstalled extensions, auto-generating REST APIs via PostgREST, GraphQL via pg_graphql, and real-time change streams via an Elixir-based WebSocket engine that supports database change listeners, user presence tracking, and arbitrary broadcast messaging. Authentication covers email and password, phone OTP, magic links, and 20+ social providers including Google, GitHub, Apple, Azure, and SAML SSO, all enforced through Postgres Row Level Security policies that run inside the database itself. S3-compatible object storage delivers files through a CDN spanning 285+ cities with on-the-fly image transformations powered by imgproxy. Edge Functions run globally distributed TypeScript on the Deno runtime with Node.js compatibility and access to over two million NPM packages. The pgvector extension stores, indexes, and queries vector embeddings for AI-powered semantic search and retrieval-augmented generation workflows. Supabase Studio provides a browser-based dashboard with a table editor, SQL editor, schema visualizer, and log explorer. Official client SDKs ship for JavaScript, Python, Flutter, Swift, Kotlin, C#, Go, and Ruby. The self-hosted Docker Compose stack runs fourteen coordinated services including Kong API gateway, Supavisor connection pooler, and Logflare analytics. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Ory Hydra
Ory Hydra is an OpenID Certified OAuth 2.0 and OpenID Connect provider that plugs into any existing user database or authentication system through a headless consent and login bridge, letting you own your authorization infrastructure without rebuilding identity management from scratch. The Go binary ships at under 15MB with zero system dependencies and exposes two distinct API surfaces: a public endpoint on port 4444 handling authorization code flows, token exchanges, PKCE challenges, device authorization grants per RFC 8628, and OpenID Connect discovery, plus an admin endpoint on port 4445 managing client registration, token introspection, consent session lifecycle, and JWKS rotation. Access tokens can be issued as opaque reference tokens or signed JWTs for stateless validation at resource servers, while refresh token rotation, token revocation per RFC 7009, and pairwise subject identifiers provide granular security controls. Persistent storage spans PostgreSQL, MySQL, and CockroachDB with automatic schema migrations, and the architecture supports horizontal scaling behind load balancers with shared database state. Dynamic client registration per RFC 7591 enables automated provisioning, and the OAuth 2.0 Threat Model security considerations are implemented as default behaviors rather than optional add-ons. Trusted by OpenAI and other internet-scale platforms. Helm charts and Docker Compose quickstarts provide production-ready deployment paths alongside the broader Ory ecosystem including Kratos for identity management, Oathkeeper for zero-trust API proxying, and Keto for fine-grained permissions. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Ory Kratos
With 13,800 GitHub stars, adoption by OpenAI for ChatGPT's authentication infrastructure serving 800 million weekly active users, and governance under the Ory open-source ecosystem, Ory Kratos provides enterprise-grade identity management as a headless API server that separates authentication logic from user interface — enabling any frontend framework to consume standardized self-service flows for registration, login, recovery, verification, and profile management. Multi-factor authentication supports passkeys, WebAuthn security keys, TOTP authenticator apps, SMS one-time codes, email magic links, and backup recovery codes with configurable Authenticator Assurance Levels enforcing step-up authentication for sensitive operations. Social sign-in connects to any OpenID Connect provider including Google, GitHub, Apple, and Microsoft, plus enterprise SAML 2.0 federation for B2B single sign-on. Customizable identity schemas using JSON Schema define user profiles with flexible trait structures, while pre- and post-flow webhooks enable integration with CRMs, analytics, and compliance systems. The courier system handles email and SMS delivery for verification codes and password recovery links. Session management provides device tracking, forced logout, and configurable lifespans with privileged session elevation. Deploy alongside Ory Hydra for OAuth2/OIDC token issuance and Ory Keto for fine-grained permissions to build a complete identity platform. Docker Compose deployment with PostgreSQL. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Open Connector
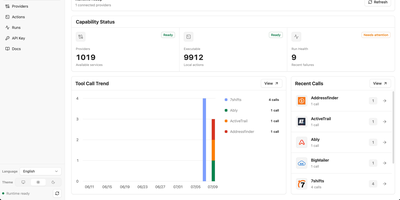
With over 5,000 GitHub stars since its June 2026 launch, OOMOL OpenConnector bridges the gap between AI agents and the real world by handling the authentication nightmare that stops LLMs from calling external APIs safely. The runtime connects to more than 1,000 SaaS providers — GitHub, Gmail, Notion, Slack, Microsoft, HubSpot, Google Workspace, and hundreds more — through 10,000+ prebuilt typed Actions that agents can discover and execute without ever touching raw credentials. OAuth2 flows, API key rotation, custom credentials, and no-auth providers are all managed centrally with AES-encrypted storage, scoped runtime tokens, and configurable action allowlists and blocklists that enforce least-privilege access. Agents interact through five access surfaces: the Model Context Protocol endpoint at /mcp for Claude and other MCP-capable hosts, a full REST API at /v1 for programmatic control, an auto-generated OpenAPI specification for code generation, a TypeScript SDK for application integration, and the oo CLI for local agent relay. The built-in Web Console provides browser-based administration for configuring OAuth apps, managing connections, inspecting action schemas, and reviewing execution logs with redacted inputs. Deploy via Docker Compose with SQLite for single-server setups, run from source on Node.js 22+, or push to Cloudflare Workers with D1 and R2 for edge deployment. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
DefGuard
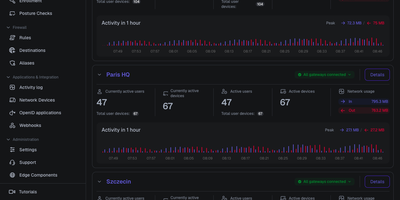
Behind one admin panel, DefGuard runs a WireGuard VPN, an identity provider, and multi-factor authentication, so every person and device proves who they are before reaching your private network. Administrators define VPN locations, assign which users and groups may enter each one, and enforce firewall rules that allow or deny traffic per location, with changes applied to gateways in real time. People enroll remotely through a guided self-service flow, register their own laptops and phones, and connect with desktop and mobile clients that show live connection statistics. Sign-in goes well beyond passwords, because the built-in OpenID Connect provider gives internal tools single sign-on, while TOTP codes, WebAuthn and FIDO2 keys, email tokens, and mobile biometrics gate each connection. Directory teams sync accounts from LDAP and Active Directory, or federate sign-in through Google, Microsoft, and custom OpenID providers, instead of maintaining a separate user list. Every authentication, enrollment, and policy change lands in a searchable activity log, and webhooks plus a REST API let surrounding systems react to access events automatically. Gateways keep enforcing access from a local cache when the control plane is unreachable, and several gateways can front the same location for failover. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Vaultwarden
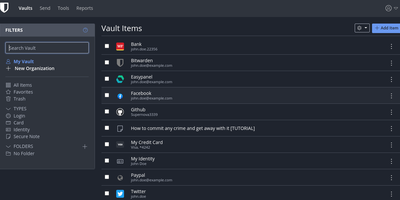
The Bitwarden server, reimplemented in Rust: Vaultwarden (formerly bitwarden_rs) is the unofficial lightweight edition. It speaks the same wire protocol as the official server, so every official Bitwarden client - browser extensions, iOS, Android, desktop, and the bw CLI - connects without modification, while the server itself runs as a single container against SQLite (or MySQL/MariaDB/PostgreSQL) instead of the official multi-container stack that wants gigabytes of RAM. Features Bitwarden gates behind paid tiers ship free: organizations with collections, groups, member roles, and policies; TOTP code storage; file attachments; Bitwarden Send; Emergency Access; event logs; and admin password reset. Two-factor options cover authenticator apps, email, FIDO2 WebAuthn, YubiKey, and Duo, and OIDC-based SSO landed natively in v1.35.0. Zero-knowledge encryption is unchanged - vault data is encrypted client-side and the master password never reaches the server. Attachments and Sends store on local disk or S3-compatible backends, an admin panel manages users and server settings, and backup is copying one data directory. Suited to individuals and teams up to roughly 50 users.
Nango
The integrations your SaaS product offers its own users - that is what Nango, an open-source product-integrations platform, exists to build. It solves the repetitive infrastructure work behind every third-party API connection: OAuth flows, API key handling, token refresh, encrypted credential storage, rate-limit backoff, retries, and multi-tenant connection management. It ships pre-built auth configurations for 800+ APIs. Your users connect their accounts through an embeddable, white-label Connect UI, and your backend then reads or writes data through Nango's proxy, SDKs, or REST API without ever touching raw credentials. Integration logic is written as TypeScript functions covering actions, scheduled data syncs, and webhook processing - all running on one runtime with retries, checkpointing, and per-connection logs built in. Syncs pull records incrementally on a schedule, one-way or two-way, which suits RAG pipelines, search indexing, and keeping local copies of external data current. Selected actions can also be exposed as tool schemas or through a built-in MCP server, so AI agents operate on user-connected accounts without ever handling provider credentials. Auth support spans OAuth 2.0, OAuth 1.0a, API keys, basic auth, and JWT, and observability - logs, metrics, failure detection, and a reconnect flow for expired credentials - is scoped per customer connection for easier support debugging. Works with any backend language. Self-hosting on RepoCloud keeps all customer credentials and synced data on infrastructure you control, which matters for data residency and compliance requirements.
PocketBase
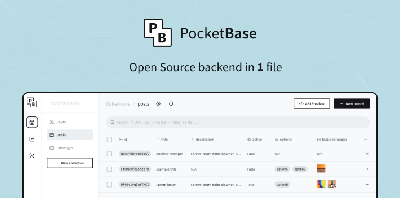
An entire backend in a single Go executable: PocketBase embeds SQLite with realtime subscriptions, authentication and user management, file storage, and an admin dashboard, all behind a REST-ish API. SQLite runs in WAL mode, which outperforms client-server databases for the read-heavy workloads typical of small and mid-sized apps. Authentication supports email/password, one-time passwords, and 15+ OAuth2 providers including Google, Apple, and GitHub, with stateless tokens. Clients subscribe to record changes over server-sent events, and official JavaScript and Dart SDKs cover web, mobile, and Flutter frontends. Collections, rules, and API access permissions are managed visually in the admin UI. When you need custom logic, extend it with JavaScript hooks running in the embedded JS VM of the prebuilt binary, or import PocketBase as a Go library and compile custom business logic into your own single-file backend. File storage attaches uploads to records with thumbnail generation for images and optional S3-compatible external storage. All state lives in one pb_data directory, so backup is a directory copy and upgrade is replacing a binary - one of the lowest-maintenance backends you can run. The contrast with Firebase is the point: where usage-based pricing scales with reads, writes, and bandwidth, PocketBase runs the entire backend at flat hosting cost, and the data is a plain SQLite file you can copy anywhere. MIT-licensed.
Kanidm
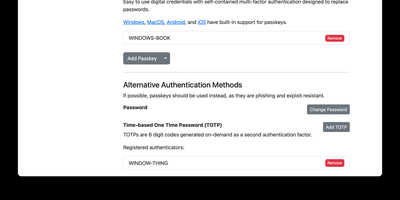
Every service you self-host wants its own account database, and Kanidm exists so they can all share one: one identity server where people sign in with passkeys and every application trusts the same login. Users register YubiKeys, Touch ID, Windows Hello, or TPM backed authenticators, and attested passkey policies let administrators restrict sign-in to specific authenticator models in high security environments. Applications connect as OAuth2 or OpenID Connect clients with authorization code, client credentials, PKCE, token exchange, and revocation supported, so your wiki, Git forge, and file sync all delegate sign-in instead of storing passwords. The application portal gives each person one page of tiles for every service they may open, and role based access control decides which groups see which applications and scopes. Older systems that only speak LDAP bind to the read-only LDAPS gateway, while Wi-Fi and VPN gear authenticates through the built-in RADIUS server with MS-CHAPv2 and EAP-TLS. Linux machines join through the Unix client for PAM and NSS authentication, cached offline credentials protected by the machine TPM, and SSH keys distributed from the server to every host. A second server replicates the whole database with strong eventual consistency, every node accepting writes without elections or quorums, so a failed machine never locks your users out of sign-in. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MPL-2.0 licensed.
Casdoor
With 13,800+ GitHub stars and active releases through 2026, Casdoor is the open-source identity platform that ships OAuth 2.0, OIDC, SAML 2.0, CAS, LDAP, SCIM 2.0, WebAuthn passkeys, TOTP multi-factor authentication, and Face ID biometric login in a single Go binary with a React web console — covering every authentication protocol your organization will ever need. Social login connects 50+ identity providers including Google, GitHub, Microsoft Azure AD, Facebook, WeChat, DingTalk, Apple, Twitter, and LinkedIn without custom code. The AI-first architecture includes a Model Context Protocol gateway for AI agent authentication and Agent-to-Agent protocol support for securing LLM-powered workflows. Built-in Casbin integration delivers authorization primitives beyond basic RBAC: attribute-based access control, relationship-based access control, and custom policy models through a unified engine. The organization-scoped multi-tenancy model isolates users, applications, and identity providers per tenant with customizable login pages, branding, and SMTP configuration. SCIM 2.0 endpoints automate user provisioning from HR systems and Active Directory. Official SDKs for Go, Java, Node.js, Python, and PHP accelerate application integration. The RESTful API exposes every resource for programmatic management. Comprehensive audit logs record authentication events and administrative actions. Deploy via Docker Compose with MySQL or PostgreSQL, the all-in-one SQLite Docker image for quick trials, or the official Kubernetes Helm chart for production clusters. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Logto
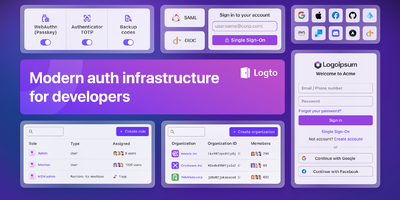
With over 14,000 GitHub stars, 1 million managed identities on Logto Cloud, and continuous releases through version 1.42.0 in July 2026, Logto has emerged as the most credible open-source alternative to Auth0, Clerk, and AWS Cognito by packaging OIDC, OAuth 2.1, enterprise SSO, multi-tenancy, and RBAC into a single MPL-2.0 codebase that self-hosts for free with no per-MAU pricing surprises. Every Logto tenant operates as a fully compliant OpenID Provider supporting PKCE-only public clients, DPoP token binding, and RFC 9068 JWT access tokens. Pre-built sign-in flows handle email, phone, social login via Google, Facebook, Azure AD, and dozens of connectors, passkey authentication, and multi-factor verification through TOTP and WebAuthn. Organizations enable first-class multi-tenancy where users belong to multiple tenants with per-organization RBAC scopes on API resources. Enterprise SSO connects to Okta, Entra ID, and any SAML or OIDC identity provider. SDKs for over 30 frameworks including React, Next.js, Angular, Vue, Flutter, Go, and Python integrate authentication into SPAs, web apps, mobile apps, APIs, machine-to-machine, and CLI tools. The admin console provides user management, audit logs, webhook event subscriptions, and custom domain configuration. Personal Access Tokens and token exchange support AI agent architectures and MCP server authentication. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MPL-2.0 licensed.
Appwrite
Backed by over 56,000 GitHub stars and a growing ecosystem of client and server SDKs covering Flutter, React Native, Swift, Kotlin, Python, Node.js, Deno, and more, Appwrite provides a complete backend platform that replaces Firebase and Supabase with a fully self-hostable architecture. The authentication module supports email and password, phone OTP, magic links, OAuth providers including Google, GitHub, Apple, and Facebook, anonymous sessions, and JWT token management with configurable session policies. The database service provides a document-oriented store with collections, indexes, query filters, pagination, and real-time subscriptions that push changes to connected clients instantly via WebSocket. The storage service handles file uploads with built-in image manipulation including cropping, resizing, format conversion, and compression, served through a CDN-ready URL structure. Serverless functions execute custom backend logic triggered by HTTP requests, scheduled cron jobs, or database events, with runtime support for Node.js, Python, PHP, Ruby, Dart, Swift, Kotlin, and Java. The messaging service enables push notifications, SMS, and email delivery through configurable providers including APNS, FCM, Twilio, Vonage, Mailgun, and Sendgrid. Team management with role-based permissions, webhook integrations, and health monitoring APIs complete the platform. The admin console provides a web-based dashboard for managing all services, monitoring usage metrics, and configuring project settings. Deployment runs via Docker Compose with MariaDB for metadata and configurable storage adapters. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. BSD 3-Clause licensed.
Hanko
Backed by 9,000+ GitHub stars and developed by a Germany-based team with deep FIDO2 expertise, Hanko delivers the open-source authentication platform that replaces Auth0, Clerk, and Firebase Auth with a passkey-first architecture built on phishing-resistant WebAuthn credentials. The Go backend exposes both public and administrative HTTP APIs handling passkey registration and login, password authentication, email passcodes, TOTP-based MFA, security key verification, server-side sessions with remote revocation, and JWT issuing with configurable expiry and refresh policies. OAuth SSO connects Apple, Google, GitHub, Microsoft, and custom OIDC providers, while SAML Enterprise SSO integrates corporate identity providers for single sign-on across the organization. Hanko Elements provides framework-agnostic web components that embed complete onboarding, login, and user profile flows into any application with two lines of code, fully customizable via CSS variables and supporting i18n with custom translations. The JavaScript frontend SDK handles API communication, credential management, and session state for teams building custom authentication UIs without the pre-built components. Webhooks notify external services of authentication events including user creation, login, email verification, and password changes. Privacy-first design principles enforce data minimalism with user-deletable passwords and configurable identifier strategies supporting email-only, username-only, or combined approaches. Docker deployment starts the backend with PostgreSQL or MySQL, serving both APIs on configurable ports. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 (backend) / MIT (frontend) licensed.
Supertokens Core
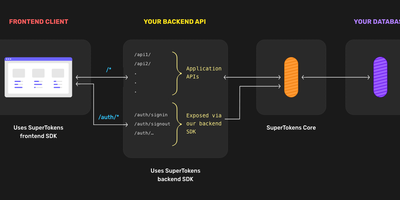
Authentication that lives inside your application rather than behind a redirect to an external identity provider - SuperTokens takes a fundamentally different architecture from Auth0 and AWS Cognito. Three tiers make that work - frontend SDKs (React, Angular, Vue, vanilla JS, React Native) render overridable login UI and manage tokens; backend SDKs (Node.js, Python, Go) expose auth endpoints on your own API domain; and SuperTokens Core, the piece you host here, is the stateless HTTP service handling core auth logic, password hashing, token signing, and database operations against PostgreSQL. The recipe system keeps features decoupled: use email/password, social login, passwordless (magic links, OTP), phone-password, multi-factor authentication (TOTP, WebAuthn), user roles, and microservice auth - individually or combined; you can even use SuperTokens purely for session management alongside another login provider. Sessions are where it shines: rotating refresh tokens with theft detection, automatic access-token refresh, CSRF protection, and secure cookie handling out of the box - the details that become vulnerabilities when hand-rolled. Verification happens locally in your backend via cached JWT signing keys, so the Core stays off the hot path. Self-hosted means no user limits, free forever, with all user data in your database. Apache-licensed.
Rauthy
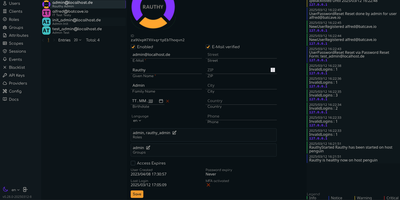
Every self-hosted app asking for its own password is a liability you keep re-creating. Rauthy is a lightweight single sign-on identity provider that gives your whole homelab or organization one secure login through OpenID Connect and OAuth 2, with passkeys at the center instead of passwords. Accounts can be fully passwordless: an email address plus a FIDO2 passkey with user verification, or a password backed by a security key, with magic links and upstream login providers also supported. The admin UI manages users, clients, roles, groups, sessions, API keys, blacklists, and per-client login branding with custom logos and colors, and events stream to email, Matrix, or Slack when something deserves attention. Login endpoints defend themselves with brute-force and credential-stuffing detection, automatic IP blacklisting, rate limiting, and optional geolocation blocking. Beyond web apps, a PAM and NSS module extends the same identities to Linux workstations and SSH logins with ephemeral passwords or public keys, and the OAuth device flow covers headless and IoT devices. It runs as a single efficient service on embedded Hiqlite or Postgres, clusters for high availability, needs only tens of megabytes of memory, and has passed an independent security audit. Dynamic client registration, SCIM provisioning, and DPoP tokens cover modern decentralized login flows. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Issuerd
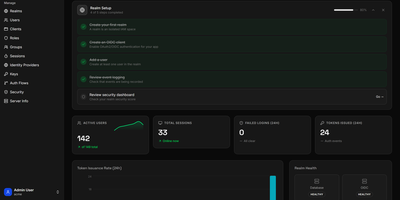
One login for every internal tool, without handing your users another password to forget: Issuerd is a Keycloak-compatible identity provider that runs single sign-on for your whole stack from a single binary. Administrators manage realms, users, groups, clients, roles, client scopes, and protocol mappers in an embedded admin console, while end users get their own account console for passwords, passkeys, and two-factor settings. Authentication flows cover MFA, social login, and themable, localized login pages with per-realm language and email templates, so each audience sees a sign-in that looks like your product. Federation connects Samba AD, OpenLDAP, and Active Directory with user and group sync, password validation and write-through, plus Kerberos and SPNEGO for desktop single sign-on. For modern clients it implements DPoP token binding so stolen access tokens are useless without the holder's key, CIBA for approvals that happen on a second device, and token exchange patterns aimed at AI agents calling downstream services. Declarative YAML provisioning, a full management API, OpenAPI export, Prometheus metrics, and health probes round out day-two operations, and nodes scale horizontally behind any load balancer with no sticky sessions. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
InsForge
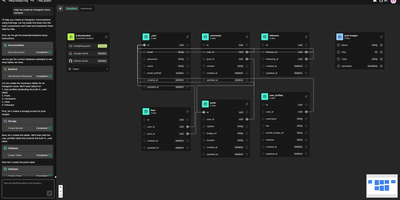
With 12,600 GitHub stars and 52 releases in under a year of development, InsForge is the fastest-growing open-source backend platform purpose-built for AI coding agents — giving Claude, Cursor, and any MCP-compatible tool direct access to database, authentication, storage, compute, and AI model infrastructure through a single self-hosted stack. The native MCP server exposes every InsForge operation as callable tools, letting coding agents autonomously create database tables, manage user authentication, upload files, deploy edge functions, and ship complete full-stack applications without human intervention. The Model Gateway provides an OpenAI-compatible API that routes requests across multiple LLM providers (OpenAI, Anthropic, Google, and open-source models) with unified billing, rate limiting, and fallback logic. PostgreSQL with pgvector handles both relational data and vector embeddings for RAG pipelines, while S3-compatible storage manages file uploads and static assets. Edge Functions run serverless TypeScript code on Deno with sub-millisecond cold starts for API endpoints, webhooks, and scheduled tasks. The authentication system provides user management, OAuth2 flows, sessions, and magic links with JWT token handling built in. Site Deployment builds and serves frontend applications with automatic SSL and custom domain configuration. The CLI paired with Agent Skills enables terminal-based workflows where agents invoke InsForge operations directly from the command line. Deploy via Docker with PostgreSQL as the only required external dependency. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
2FAuth
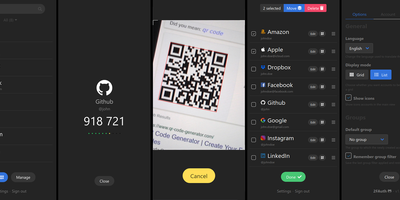
2FAuth generates TOTP, HOTP, and Steam Guard codes from any web browser, freeing your two-factor authentication from dependence on a single smartphone or app. Lose your phone, switch devices, or sit at a desktop computer, and your 2FA codes remain accessible through the web interface. The Laravel and Vue.js application stores account secrets in an encrypted SQLite database that backs up as a single file. Adding accounts works through camera-based QR scanning or manual secret key entry for services that only provide text codes. Group organization with drag-and-drop sorting keeps large collections navigable, categorized however you prefer. WebAuthn authentication with FIDO2 hardware keys protects vault access with phishing-resistant passwordless login, meaning the tool that secures your accounts is itself secured by the strongest available method. Automatic screen lock triggers after configurable idle time, and OTP obfuscation dots out generated codes until you tap to reveal them, preventing shoulder surfing in shared spaces. The REST API enables browser extensions and external applications to request codes programmatically. Import compatibility with Google Authenticator, Aegis, and 2FAS ensures painless migration without re-enrolling every account from scratch. PWA installation places 2FAuth on your device home screen for native-app-like instant access. Runs on a dedicated RepoCloud VPS with guaranteed resources and full root SSH access. AGPL-3.0 licensed.