Wag
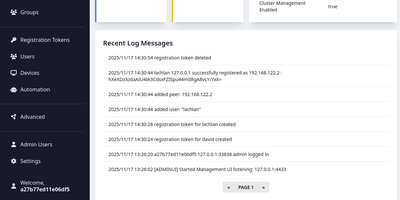
Wag is an authentication gateway for WireGuard that lets each device reach only the routes it should, and asks for a second factor before the sensitive ones open. Admins write access policies for everyone, groups, or single users, marking subnets, hosts, ports, and protocols as MFA-required, always allowed, or denied, and the most specific prefix wins, so one allowed address can sit inside a protected range. Devices join with a registration token, and the public endpoint answers with a finished WireGuard profile. Users then confirm a TOTP code, a WebAuthn security key, an OIDC single sign-on login that maps identity provider groups into Wag groups, or a PAM prompt, and repeated failures lock the account. Session lifetime and idle timeouts decide when they must prove themselves again. The browser portal lists users, devices, rules, registration tokens, and webhooks with real-time notifications, while a command line locks devices, resets MFA, and manages administrators. Webhooks turn JSON from an HR or identity system into new tokens or removed users and devices, and clients can fetch the list of guarded routes from a small API. Remote staff, contractors limited to one host, and homelabs are typical uses. When a server fails, the VPN remains reachable through clustering with witness nodes or an external etcd, and certificates arrive through ACME with HTTP-01 or Cloudflare DNS-01. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. BSD-3-Clause licensed.
Deploy