Open Kritt
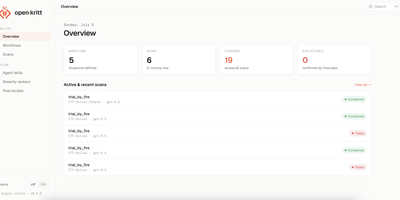
Big repositories, small questions: Open Kritt is a self-hosted platform that splits vulnerability research into focused tasks for AI agents and returns ranked, de-duplicated findings. Build a workflow as a tree of prompt steps, where each step declares the structured output it must produce and the next level launches one fresh agent per result. Scan remote or local repositories along with their dependencies, using Codex, Claude Code, or Grok Build as the harness. Every workflow ends in one fixed finding schema covering file, line, vulnerability type, trigger flow, and a malicious input example. Post-scripts then validate each finding, build a proof of concept, or write the report. Markdown severity rankers tell the model how to prioritize for your bounty program, and repeated findings collapse automatically. Model access comes from a Codex login or OpenAI, Anthropic, DeepSeek, OpenRouter, or xAI keys, with an Active switch to choose which accounts take new work. A dashboard tracks blueprints, scans, and findings, a headless command-line tool imports workflows and launches scans on servers without a browser, and finished scans export as one ZIP with a share-safe manifest. Built-in workflows, including an entry-point-driven hunt, give you a starting point. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Deploy