
Comp AI
Comp AI turns the months-long slog of SOC 2, ISO 27001, HIPAA, and GDPR certification into a largely automated process by connecting to your existing infrastructure and continuously collecting the evidence auditors actually ask for. Point it at your AWS account, Google Cloud project, GitHub organization, or any of 580+ supported integrations, and autonomous agents pull configuration snapshots, access logs, encryption status, and policy compliance data on a recurring schedule so your compliance posture reflects reality rather than last quarter's manual export. The AI policy engine analyzes your tech stack, team structure, and risk tolerance to generate organization-specific policies for information security, access control, incident response, data retention, and vendor management; no two companies get the same boilerplate. An open-source device agent runs on employee machines checking disk encryption, firewall status, screen lock settings, password length, and antivirus presence around the clock, flagging failures the moment they occur instead of surfacing them during an audit. Built-in penetration testing agents scan your codebase and API endpoints for vulnerabilities like SQL injection and output audit-ready reports. The vendor risk management module scores third-party services and surfaces compliance gaps before they become findings. A public trust center lets prospects verify your compliance status directly, eliminating security questionnaire bottlenecks. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Conformiti
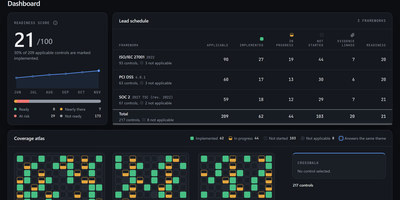
Audit season stops being a six week archaeology dig through shared drives when Conformiti keeps your whole compliance programme in one self-hosted system built for SOC 2, ISO/IEC 27001:2022, and PCI DSS v4.0.1. Its three complete control libraries hold 217 controls with a cross-framework crosswalk, so satisfying one requirement can answer its equivalents elsewhere instead of duplicating work. Evidence lives in a folder tree generated from those libraries, where every document declares which controls it satisfies and every control lists its documents, ending the hunt for proof at fieldwork time. Readiness is calculated rather than vibes: each control scores from implementation status, owner, evidence freshness, and testing, minus a penalty for open risks, and the dashboard tracks that score with daily snapshots. Documents carry review cadences with escalating email reminders before they expire, versions archive instead of overwriting, and uploads can pass through ClamAV scanning. A five by five risk register, vendor register with shared responsibility matrices, periodic access reviews, and a RACI matrix keep the rest of the programme beside the controls instead of in separate spreadsheets. When assessors arrive, you issue them a sealed, signed evidence package for a fixed window that verifies offline, rather than handing over drive access that outlives the engagement. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.