DodoGuard
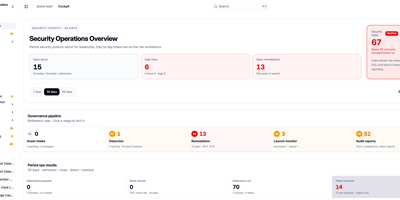
Before an AI agent meets real users, put it through a security checkup it cannot sweet-talk. DodoGuard is a web console and command line where teams register their agents, run evaluation and red-team tasks against them, and decide if each one is cleared for launch. The overview page shows a security index, open risks, remediation counts, and a pipeline that runs from asset intake through detection and remediation to launch monitoring and audit reports. An asset ledger lists every managed agent with its platform, environment, and risk level. A guided wizard creates assessment tasks that pick a test library for prompt injection, instruction leakage, tool misuse, and output risks, then runs black-box conversations against the agent. Evaluation configs cover prompts, providers, variable cases, and several assertion types, with OpenAI, Anthropic, Azure, Bedrock, Ollama, and any OpenAI-compatible endpoint supported. Findings land in a closed-loop board where owners confirm, fix, retest, and close each risk, and finished tasks export as reports for release evidence. Docker Compose with SQLite brings up the web UI on port 3000, and the same engine runs in continuous integration. Security teams use it for launch gates, platform owners use it for regression checks after prompt changes, and auditors use it for evidence. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Deploy