RedAmon
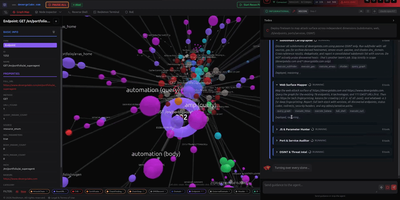
An AI agent that maps your attack surface, proves what is exploitable, and drafts the code fix: RedAmon is a red team for domains you are authorized to test. A six-phase recon pipeline runs subdomain, port, HTTP, and vulnerability scanners in parallel and merges every result into a Neo4j graph you can query in plain language. The agent works from a Kali sandbox with 100+ security tools, asks for human approval before risky steps, and can deploy a Fireteam of specialist sub-agents that investigate separate angles of one target at once. CypherFix triages each finding, then a code agent opens a GitHub pull request with the patch. AI Gauntlet attacks chatbots and LLM endpoints with prompt injection and jailbreak batteries, mapped to the OWASP LLM Top 10. TrafficMind records every HTTP request the tools send, with a searchable history the agent can replay. An Insights dashboard charts findings, CVE severity, and attack chains per project, and the settings page connects OpenAI, Anthropic, OpenRouter, Bedrock, or local Ollama and vLLM models. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Deploy