Unla
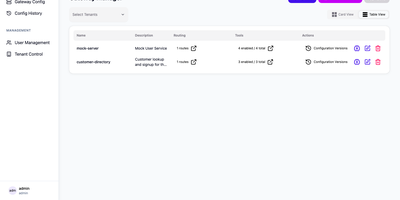
Unla puts a friendly front door on every API you already run, so AI clients can call it as an MCP server without anyone writing a line of glue code. Describe an endpoint in YAML or the form editor, name its arguments, choose where each one goes in the request, and the gateway exposes it as a tool over SSE or streamable HTTP. Import an OpenAPI file to generate a whole server at once, or proxy a third-party MCP server and route it under a prefix of your choice. The Gateway Manager shows every server as a card or table row with its routes, enabled tools, and tool counts. Every save creates a numbered config version with its author and timestamp, so changes are easy to audit and roll back. Tenants keep teams separate, user accounts carry roles, and CORS settings sit next to each route. Configuration hot reloads, syncs across replicas, and persists to disk, SQLite, PostgreSQL, or MySQL. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
AnythingMCP
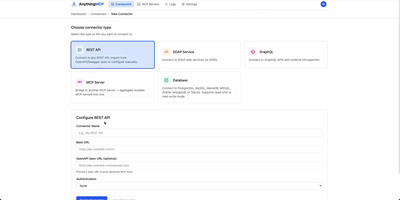
Connecting autonomous AI assistants to internal enterprise databases and legacy systems is streamlined by AnythingMCP, a visual Model Context Protocol gateway with automated knowledge graph generation and granular access controls. Engineers can import OpenAPI specifications, Postman collections, SOAP WSDL files, or raw database credentials to generate standardized Model Context Protocol tools in minutes without writing custom code. The built-in knowledge graph automatically maps entity relationships across disparate databases and software platforms, teaching agents how to correlate customer records in CRM tools with live order histories in enterprise resource planning software. System administrators can enforce fine-grained access policies by restricting tool execution permissions to specific roles and scoping database operations to read-only queries with strict row limits. An interactive web console provides real-time tool inspection, payload testing, request tracing, and comprehensive audit logs that capture every upstream invocation with full parameter visibility. Enterprise teams can integrate identity providers through OAuth2, SAML single sign-on, and SCIM automated user provisioning while protecting sensitive credentials using AES-256-GCM encryption at rest. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GNU AGPLv3 licensed.