Prismor
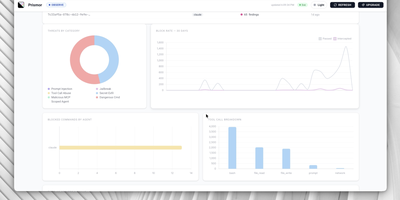
Prismor sits between your AI coding agents and the tools they want to use, judging every shell command, file read, and API call before it runs so a helpful agent cannot quietly become a destructive one. Run it in observe mode to watch what agents actually do across every workspace, then switch chosen rules to enforce and block secret leaks, prompt-injection pivots, privilege escalation, and risky package installs before execution. When a call is sensitive rather than forbidden, Prismor can pause it for human approval, letting a person decide instead of the model. Plain-language prompt guardrails such as never push to main are added to the agent context per agent and per session, and edits are picked up on the next prompt. Every action lands in a hash-chained, Ed25519-signed audit trail you can verify later, while the web dashboard breaks down sessions, findings, friction, and token spend so you can see where runs went wrong. Agents that cannot be hooked are still governed through the LLM proxy or the MCP gateway, which evaluates each tool call and scans responses for injected instructions before the model sees them. Honeytoken canary files trip a critical finding the moment an agent reads them, catching reconnaissance early. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Deploy