Krawl
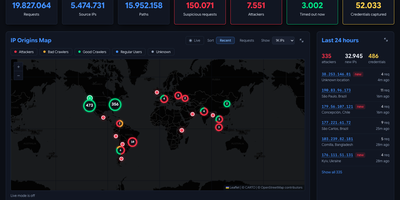
Leave a fake door unlocked and see who walks through: Krawl is a self-hosted honeypot that poses as a sloppy web server and records everything scanners and scrapers try. Fake WordPress, phpMyAdmin, and admin logins. Every attempt logged, every credential captured. A .env file leaking fake database strings, AWS keys, and Stripe secrets. SQL injection, XSS, path traversal, XXE, and command injection traps that answer with believable fake output. SQLMap gets a different database error on every request. Malicious crawlers wander an endless maze of random links. An optional tarpit adds delay and word salad that cost scrapers time, storage, and tokens. Optional AI-generated pages write a plausible decoy for any path an attacker requests. A hidden dashboard shows an attacker map, top IPs, captured credentials, and per-IP forensics. TLSH fuzzy hashing groups webshell variants into campaigns. A behavior score labels each IP attacker, bad crawler, good crawler, or regular user. Export bans as raw lists, iptables, or nftables rules, with guides for Fail2Ban, OPNsense, and RouterOS. A canary-token link in decoy pages emails you the IP and user agent of anyone who follows it. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Deploy