MISP
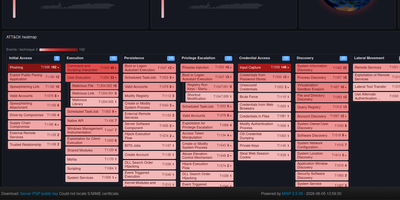
MISP is an open source threat intelligence platform where analysts log indicators and incidents, see how they connect, and share them with trusted organizations. Each case is an event holding attributes and structured objects such as files, network connections, and email messages, with Markdown reports beside the machine-readable data. A correlation engine links events that share values, including fuzzy-hash and CIDR matches, and warning lists flag benign values before they cause false positives. Taxonomies and galaxies tag events with TLP levels, threat actors, malware families, and MITRE ATT&CK techniques. Analysts explore relationships in an event graph and a correlation graph with a timeline, and build drag-and-drop dashboards with maps and ATT&CK heatmaps. Sharing groups control who sees which event, and instances synchronize with partner organizations with distribution settings down to a single attribute. Free-text, URL, bulk, and STIX imports fill the database, and exports reach Suricata, Snort, Zeek, OpenIOC, CSV, STIX 1 and 2, and RPZ zones. A REST API, the PyMISP library, expansion modules, and workflows enrich data and automate publishing. ZeroMQ and Kafka streams announce every change to connected tools. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Deploy