Spinifex
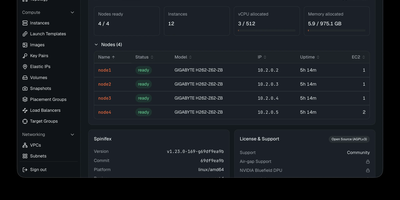
Spinifex rebuilds the AWS services your applications already call (EC2, EBS, S3, VPC, and IAM) on hardware you control, so workloads can leave the hyperscalers without a rewrite. An EC2 call boots a real KVM guest with spot instance and GPU passthrough options, attaches replicated block volumes, and places the machine inside an OVN virtual network guarded by security groups. S3 buckets land in erasure-coded object storage, container images live in a deduplicated registry, and managed Kubernetes clusters arrive with highly available control planes and node groups. Relational databases run as managed PostgreSQL or MariaDB with automated backups, load balancers terminate traffic at layer 4 or layer 7 with ACM certificates, and an authoritative DNS service manages hosted zones. Every request is authenticated with SigV4 at the gateway and routed to stateless service daemons, so capacity grows by starting more daemons on more nodes. Your existing AWS CLI profiles, SDK code, and Terraform plans point at the new endpoint and keep working, because 405 AWS API operations answer with the shapes your tooling expects. A built-in web console covers instances, volumes, buckets, networks, and IAM for operators who prefer clicks to commands. Clusters run on-premise, at air-gapped edge sites, or on GPU cloud capacity, and keep serving through disconnection because no external control plane exists. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Rancher
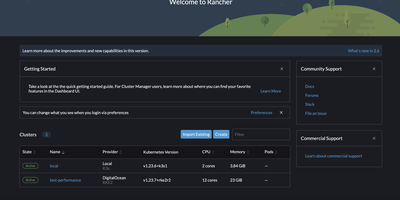
Used by over 30,000 teams and 650+ enterprise customers managing more than 5.2 million containers, Rancher has earned recognition as a Leader in the Gartner Magic Quadrant for Container Management and the Forrester Wave for Multicloud Container Platforms. The platform provides a single pane of glass for provisioning, upgrading, and securing Kubernetes clusters across Amazon EKS, Google GKE, Microsoft AKS, RKE2, K3s, and any CNCF-conformant distribution. Multi-Cluster Management enables centralized authentication via Active Directory, LDAP, SAML, GitHub, and OpenID Connect with granular role-based access control at the cluster, project, and namespace levels. Fleet, the built-in GitOps engine, delivers continuous deployment across hundreds of clusters simultaneously using Helm charts, Kustomize, or raw YAML manifests from any Git repository. The integrated app catalog provides one-click deployment of Prometheus monitoring, Grafana dashboards, Longhorn persistent storage, Istio service mesh, and hundreds of community Helm charts. Rancher supports air-gapped installations for disconnected environments, CIS benchmark scanning for security compliance, and automated backup and restoration of cluster configurations. The dashboard offers real-time workload monitoring, log aggregation, pod shell access, and namespace-scoped resource quotas. Cluster templates enforce organizational standards through Helm-based provisioning policies that ensure consistent configurations across environments. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.