mkcertWeb
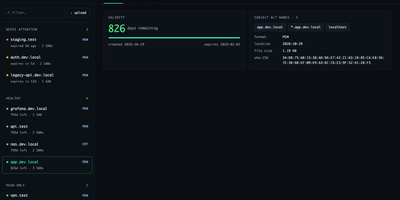
Your internal services deserve certificates your browsers actually trust, without a spreadsheet tracking when each one expires. mkcertWeb wraps the mkcert tool in a web interface where you generate certificates for any mix of hostnames, wildcards, and IP addresses, then download them as PEM, CRT, or PKCS#12 bundles for servers and client authentication. The certificate list groups everything by state, needs attention, healthy, read-only, or archived, showing days remaining, subject alternative names, and SHA-256 fingerprints at a glance. You can upload existing certificate and key files for viewing, attach a free-text note to each certificate, and archive or restore entries without ever overwriting a certificate of the same name. The root CA page offers downloads and install instructions for macOS, Linux, and Windows, and can generate a fresh CA for a new deployment. Devices enroll through the built-in SCEP server using one-time challenge passwords and templates, with an optional enterprise CA signing manual enrollments. A scheduled monitor checks expiry daily and sends alerts through SMTP email, ntfy, or an HTTP webhook, with test buttons for every channel. Settings save from the browser with secret masking, sign-in supports passwords or OpenID Connect single sign-on, and light and dark themes work down to phone width. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL-3.0 licensed.
Deploy