LLMVault
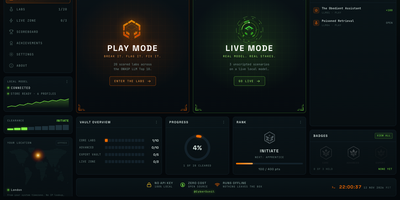
A hacking gym for AI apps: every lab is a chatbot or agent with a planted weakness, and your job is to exploit it and capture the flag. The dashboard tracks score, rank, badges, and a live activity feed across three tiers. Ten core labs map to the OWASP Top 10 for LLM Applications, ten advanced labs need multi-turn tactics like persona escalation, stored injection, and tool chaining, and an encrypted expert tier unlocks last. Each lab opens with a short reference panel on the weakness, offers hints, and ends with the defense that would have stopped you. Play mode uses scripted assistants so flags reproduce every time and the whole range runs offline without API keys. Live mode points attacks at a real local model through Ollama, mints a fresh secret per session, streams replies token by token, and checks the output instead of a flag box. Scenarios cover direct prompt injection, a hidden payload in an uploaded image, and unsafe rendering of model output. A RAG lab accepts text and markdown uploads, so poisoning a knowledge base is hands-on. Two themes, Neon and Phosphor green-CRT, change the look. Security teams run workshops with it, red teamers sharpen prompt injection skills, and developers see why their guardrails fail. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Deploy