Aegis
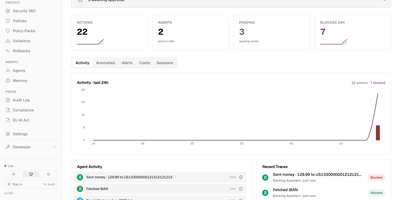
Put a checkpoint in front of every tool call your AI agents make, so a poisoned web page or file cannot quietly move money or send private data. Each call is classified and policy-checked before it executes, then allowed, blocked, or held for a person. Held calls land in an approvals queue that shows what the user asked, which passage the agent read, and the exact recipient or amount in question, with one-click block or allow. Instruction provenance flags destinations that appeared only in untrusted content, like an IBAN hidden in a file. The cockpit lists every run as a timeline of steps with verdicts, groups violations by the protection that caught them, and scores ten attack surfaces on a Security 360 page. An agent registry tracks owners, scope, and call counts. Budgets, anomaly alerts, and a kill switch cap runaway behavior. Sensitive values are redacted from traces, signed receipts prove a call was allowed, and exports produce PDF and CSV audit evidence. Python and TypeScript SDKs plug in with one line, or an LLM proxy catches calls with an environment variable. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Deploy