Spinifex
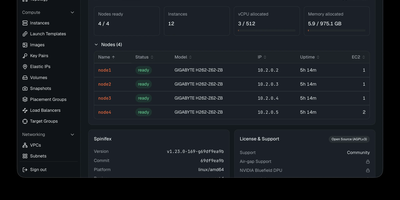
Spinifex rebuilds the AWS services your applications already call (EC2, EBS, S3, VPC, and IAM) on hardware you control, so workloads can leave the hyperscalers without a rewrite. An EC2 call boots a real KVM guest with spot instance and GPU passthrough options, attaches replicated block volumes, and places the machine inside an OVN virtual network guarded by security groups. S3 buckets land in erasure-coded object storage, container images live in a deduplicated registry, and managed Kubernetes clusters arrive with highly available control planes and node groups. Relational databases run as managed PostgreSQL or MariaDB with automated backups, load balancers terminate traffic at layer 4 or layer 7 with ACM certificates, and an authoritative DNS service manages hosted zones. Every request is authenticated with SigV4 at the gateway and routed to stateless service daemons, so capacity grows by starting more daemons on more nodes. Your existing AWS CLI profiles, SDK code, and Terraform plans point at the new endpoint and keep working, because 405 AWS API operations answer with the shapes your tooling expects. A built-in web console covers instances, volumes, buckets, networks, and IAM for operators who prefer clicks to commands. Clusters run on-premise, at air-gapped edge sites, or on GPU cloud capacity, and keep serving through disconnection because no external control plane exists. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Deploy