cvENGINE
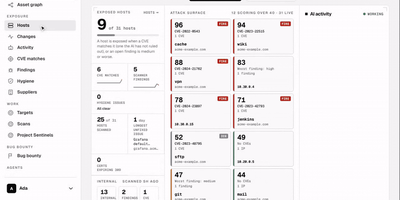
cvENGINE takes a domain name and returns a verdict on which of today's exploited vulnerabilities can actually reach you, with evidence attached. Continuous discovery builds a Shodan-style inventory of subdomains, IPs, ports, products, versions, certificates, and technologies, then rates every CVE as fire, smoke, or ice from real exploitation sources and scores each host from 0 to 100. Read-only validation reproduces a finding and records the exact command used. Optional AI triage sorts matches into confirmed, likely, or needs validation. A live dashboard, a change timeline with screenshot diffs, saved searches with alerts, and one-click PDF reports keep teams current. Sentinels run scans from other machines, including inside private networks, and an optional OpenVAS add-on extends coverage. Hygiene checks cover TLS, email and DNS records, exposed databases, cloud storage buckets, and WordPress sites. Organizations, roles, two-step sign-in, a REST API, and Slack, Discord, Telegram, and Lark alerts support shared use. A bug bounty workbench imports program scope and drafts reports. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. GPL-3.0 licensed.
Deploy