OpenCTI
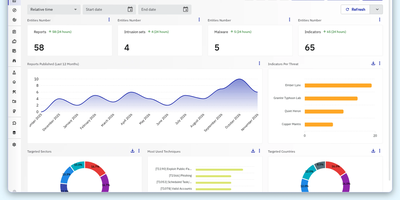
OpenCTI gives security teams one place to see which adversaries target their sector, how those groups operate, and which vulnerabilities they exploit. Reports, feeds, and analyst notes become linked STIX 2.1 entities such as intrusion sets, malware, ATT&CK techniques, vulnerabilities, and indicators, each carrying its source, confidence level, and TLP marking. Investigations start from a few entities and expand node by node, letting analysts pivot from an indicator to the campaign, malware family, and victim sector behind it. Threat pages show an ATT&CK matrix with the techniques in use highlighted, and custom dashboards chart any query as time series, distributions, or lists with one-click presets. Connectors import MITRE datasets, MISP, AlienVault, and CVE data, enrich observables through Shodan or DomainTools, and export STIX 2.1, CSV, or PDF files. TAXII collections, CSV feeds, and live streams publish selected knowledge to your SIEM or EDR, while RSS, CSV, JSON, and TAXII feeds pull outside intelligence in. Case management tracks incident responses, information requests, and takedown requests with assigned tasks and reusable task templates, and notification triggers alert analysts when watched entities change. A rules engine infers new relationships, decay rules age out stale indicators, and a GraphQL API with a Python client supports automation. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
OpenAEV
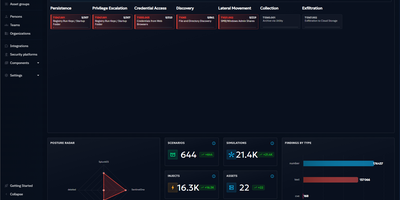
Before an attacker tests your defenses, OpenAEV lets you replay their techniques and see which ones your EDR, SIEM, and people actually catch. Scenarios sequence injects that mirror a threat actor's behavior, and simulations run them once or on a schedule against chosen endpoints, scoring prevention, detection, vulnerability, and human response. Atomic tests fire a single ATT&CK technique from the Threat Arsenal, such as an Nmap scan or a Nuclei CVE scan, and can repeat hourly, daily, weekly, or monthly. A lightweight agent for Windows, Linux, and macOS enrolls each endpoint for testing, while asset groups organize targets by filter. Collectors match EDR, XDR, and SIEM alerts to each inject, marking it prevented or detected, or missed when the expectation window expires. Findings collect scan results and CVE data for each asset, custom dashboards chart posture over time, and scheduled PDF or HTML reports reach stakeholders without platform access. Exercises can also target people through phishing campaigns with landing pages and email templates, SMS, media pressure articles, challenges, and post-run lesson surveys. Pre-built scenarios import from the XTM Hub, or OpenAEV can generate them from OpenCTI security coverage, and a REST API supports automation. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.