Categories
Knowledge Graph Cybersecurity Incident Response Threat Intelligence MITRE ATT&CK STIX TAXII SOCStars
Forks
Watchers
Developer links
OpenCTI
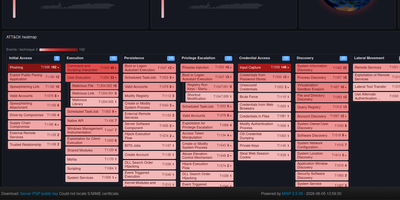
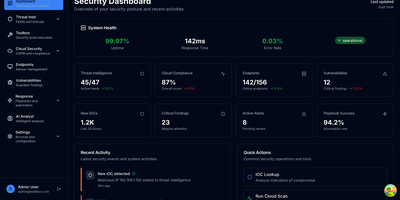
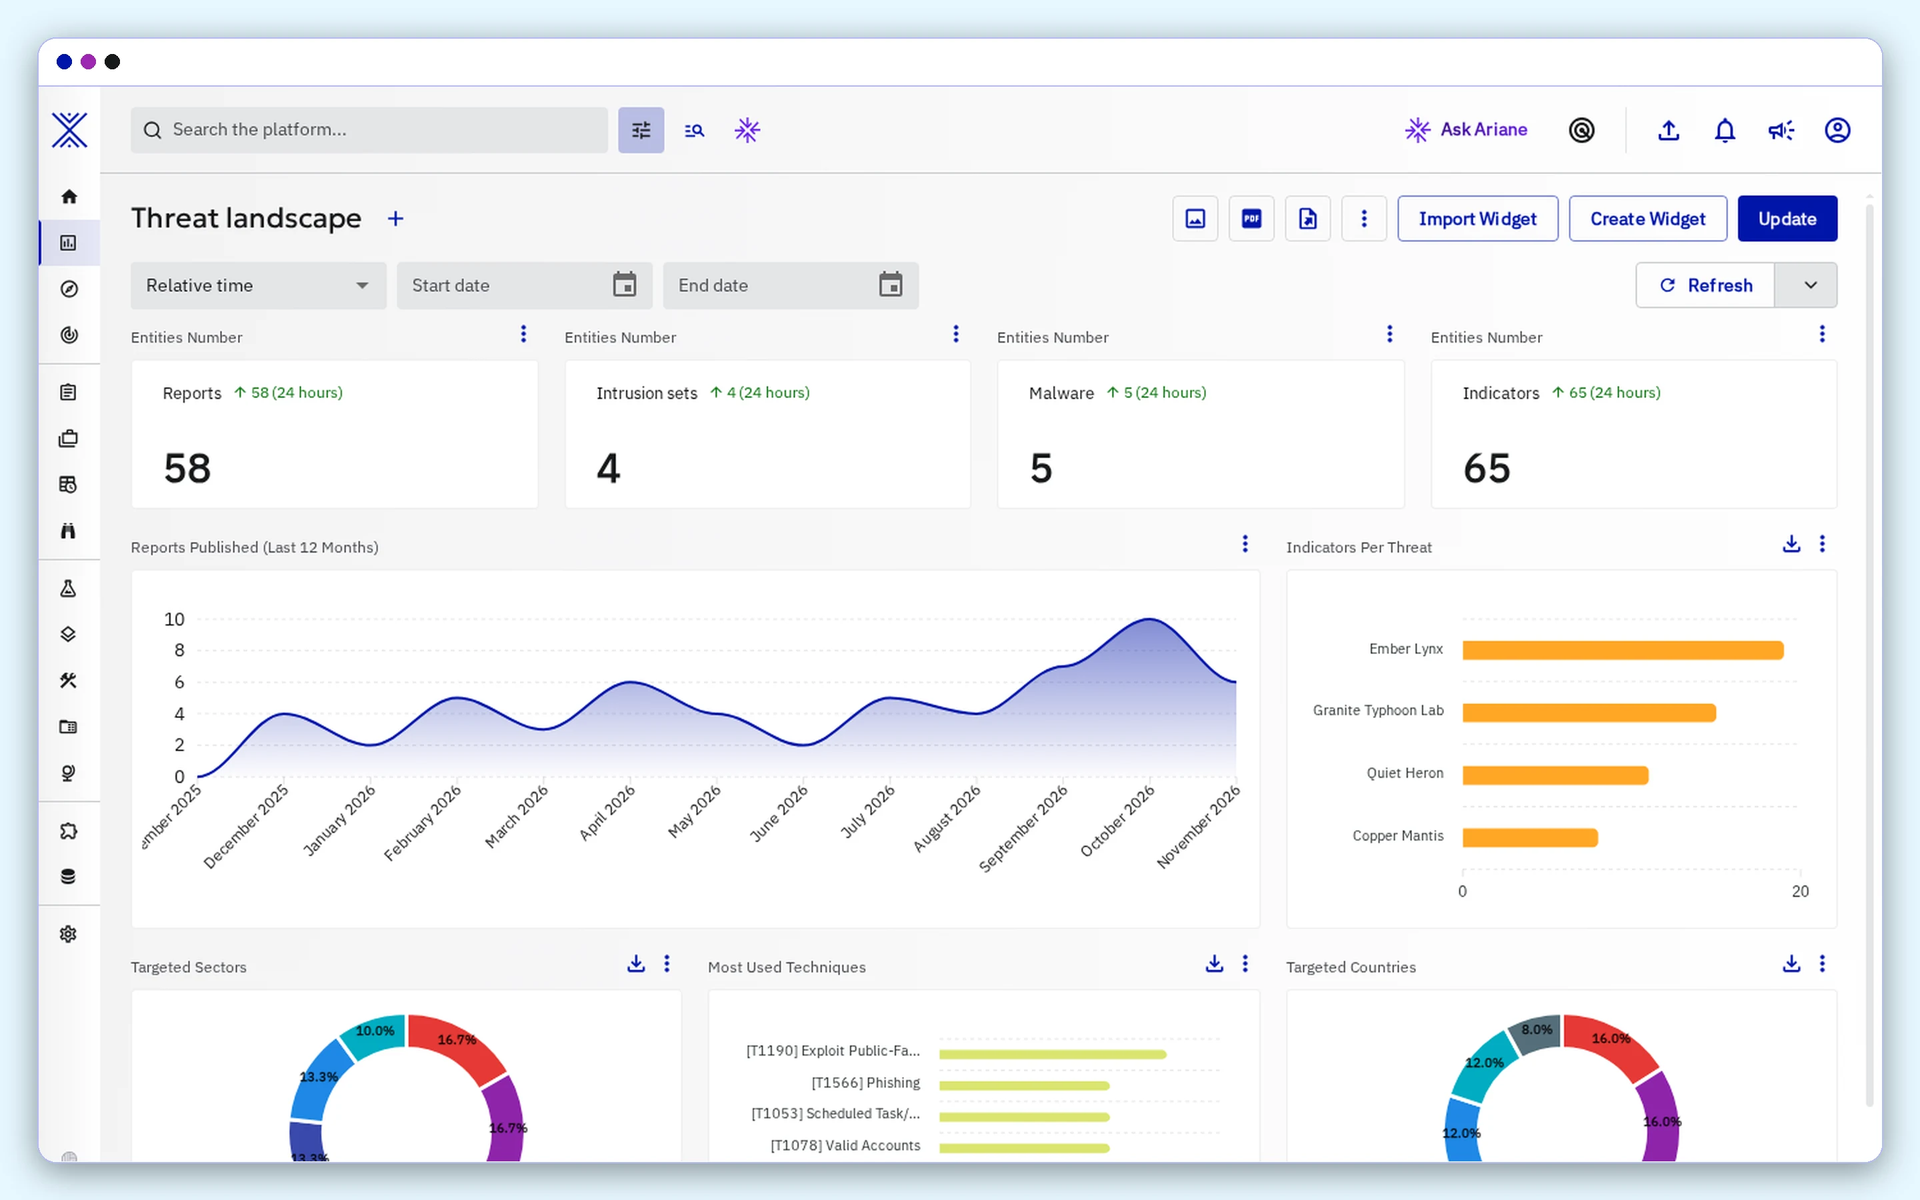
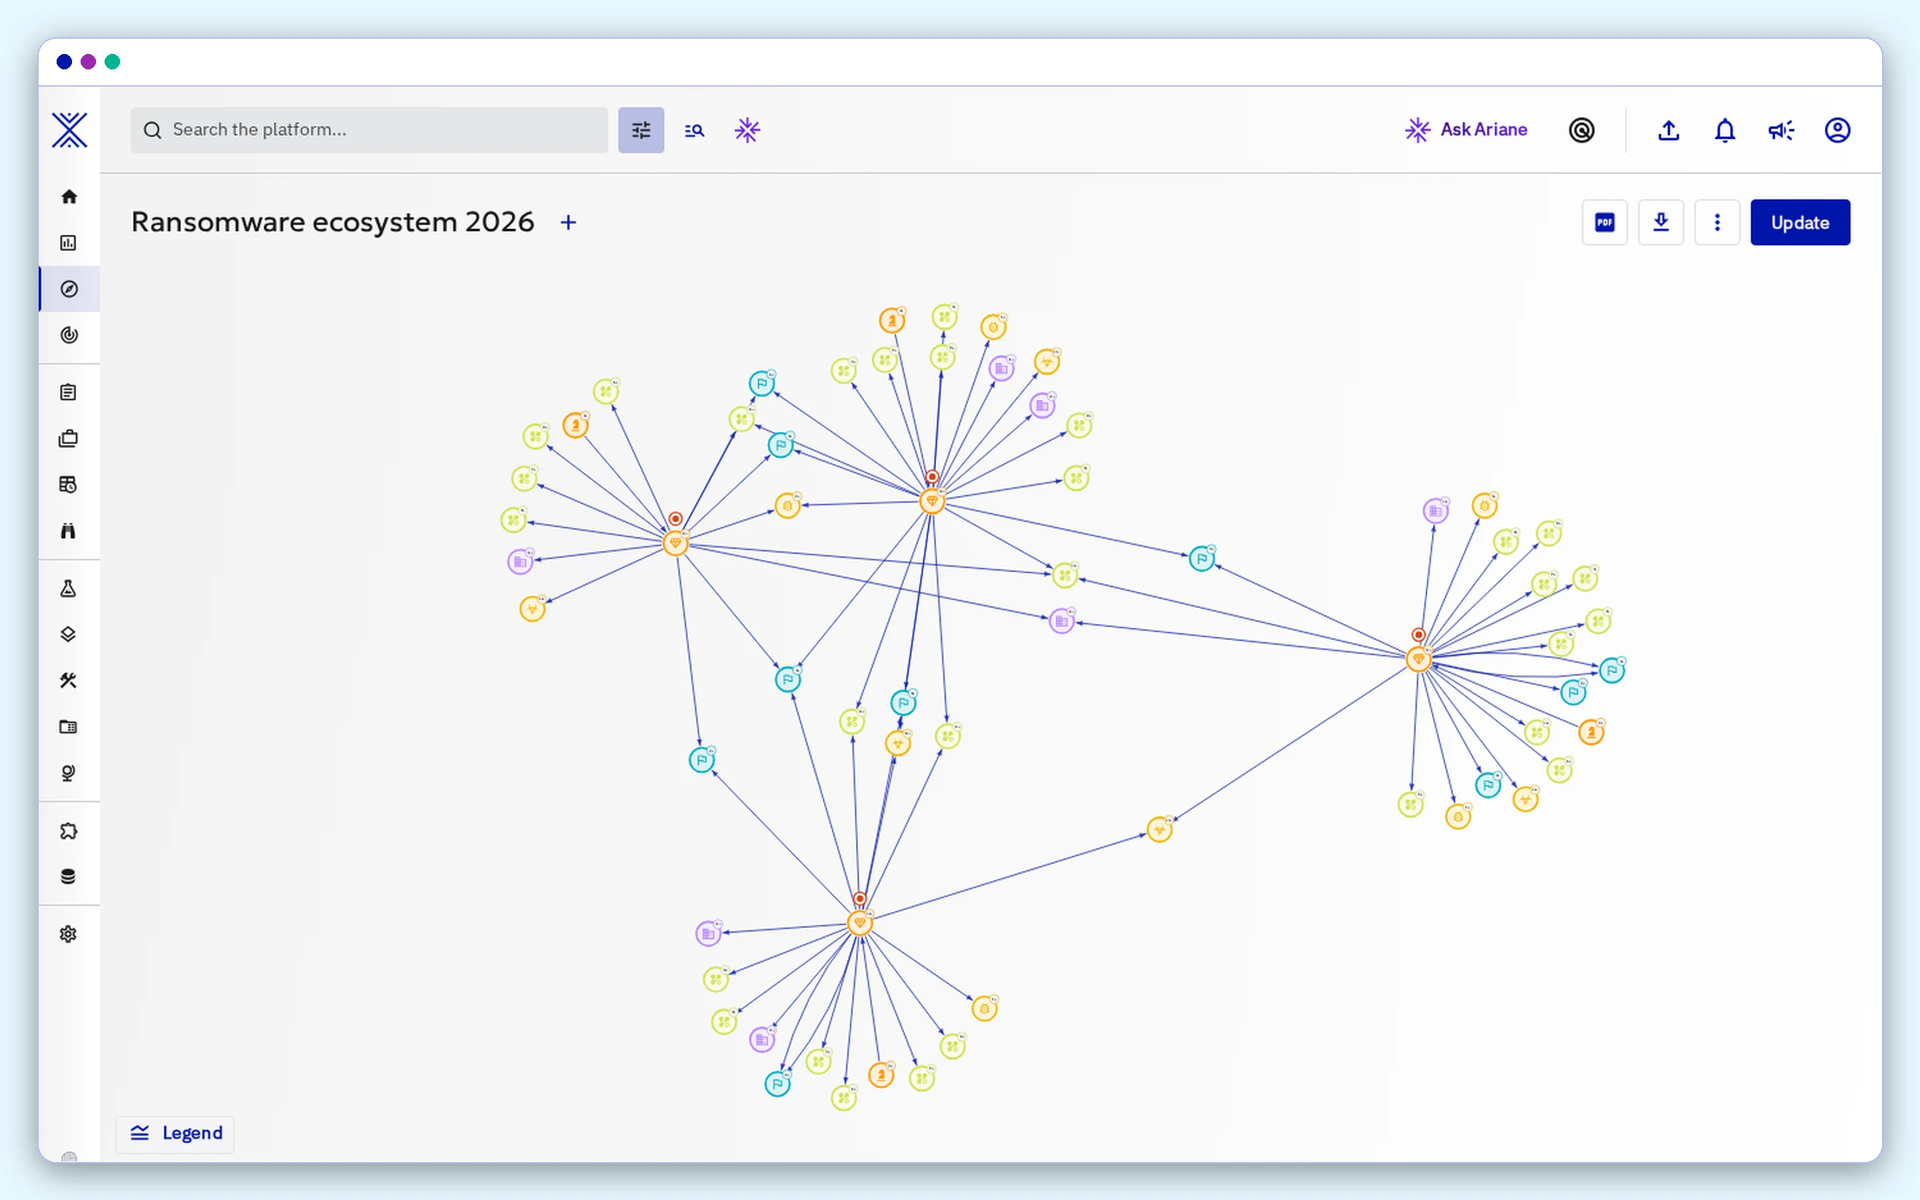
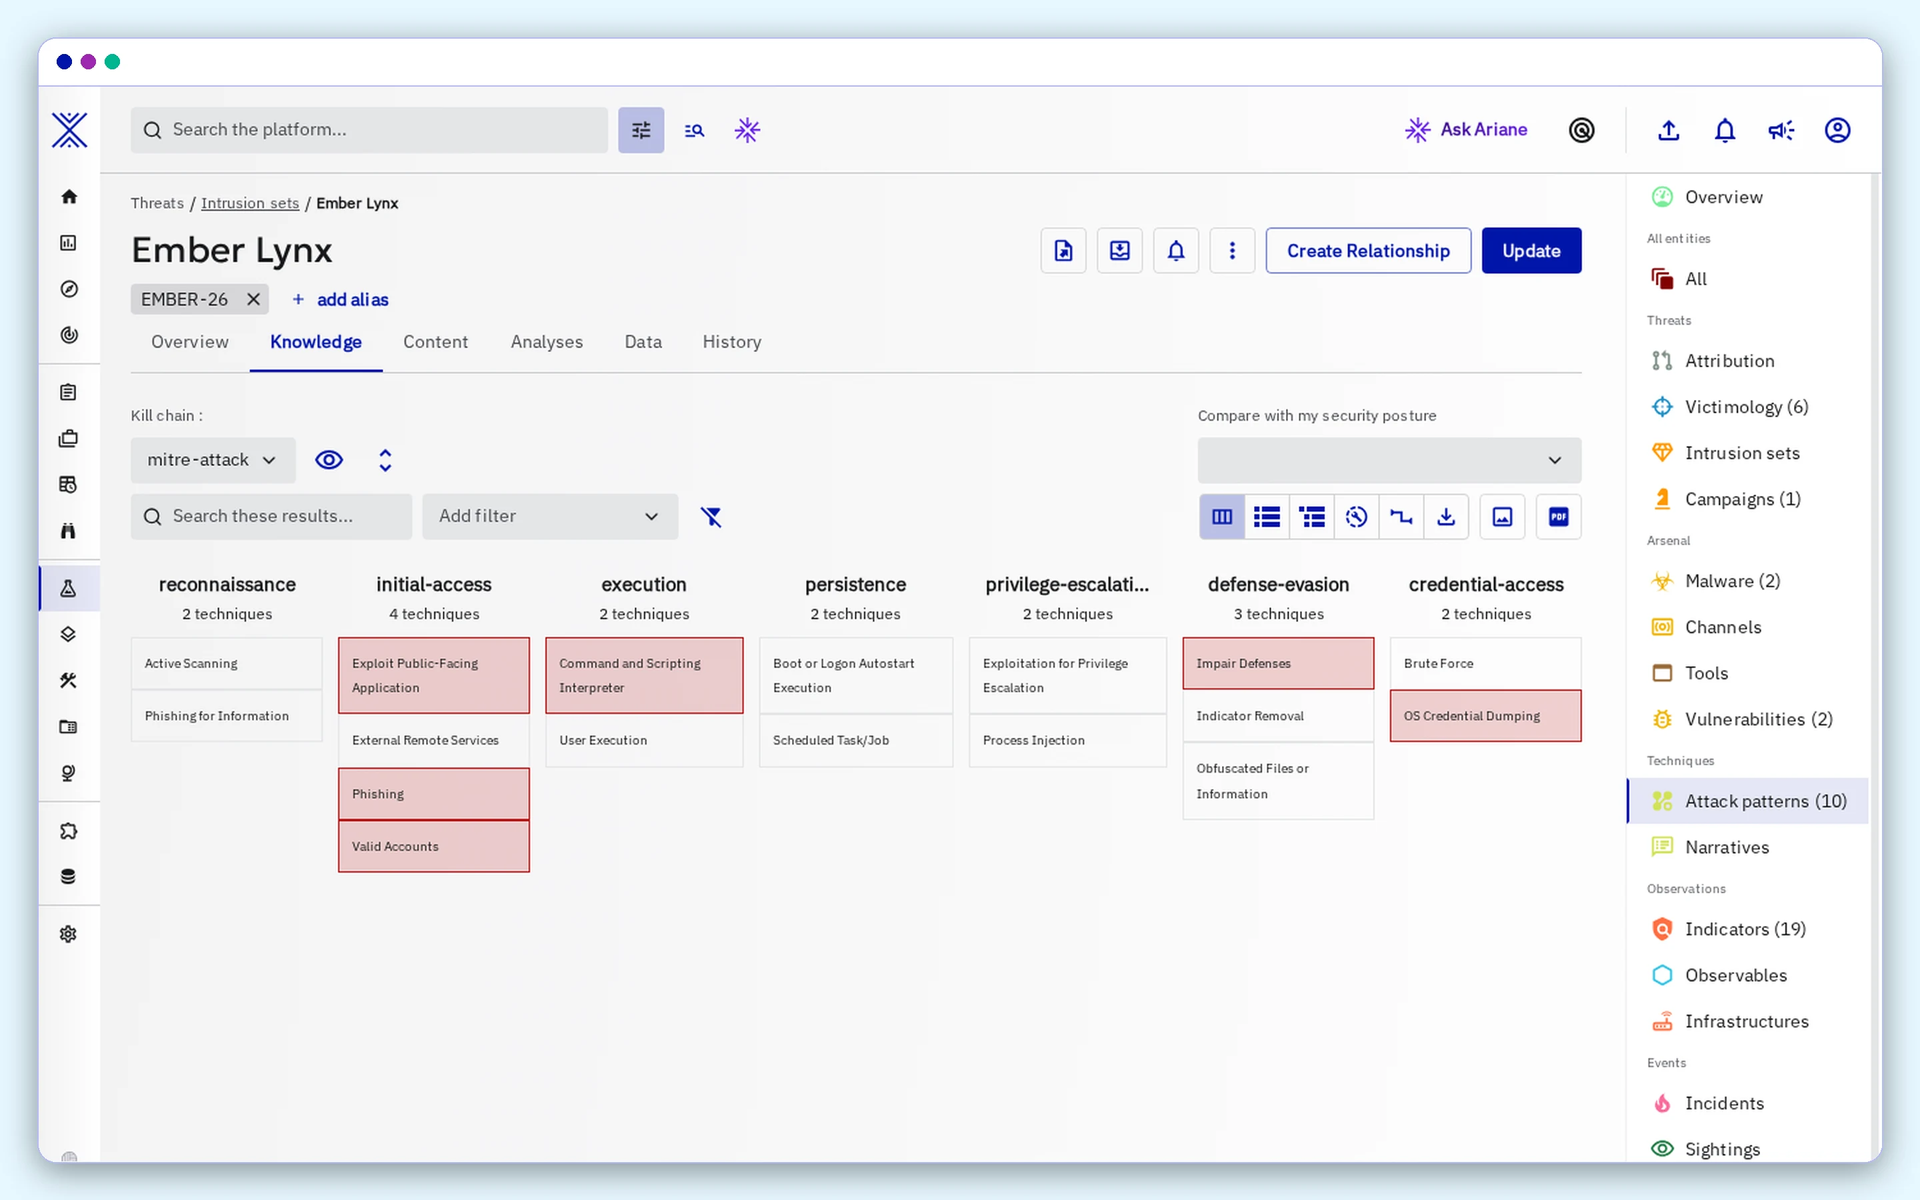
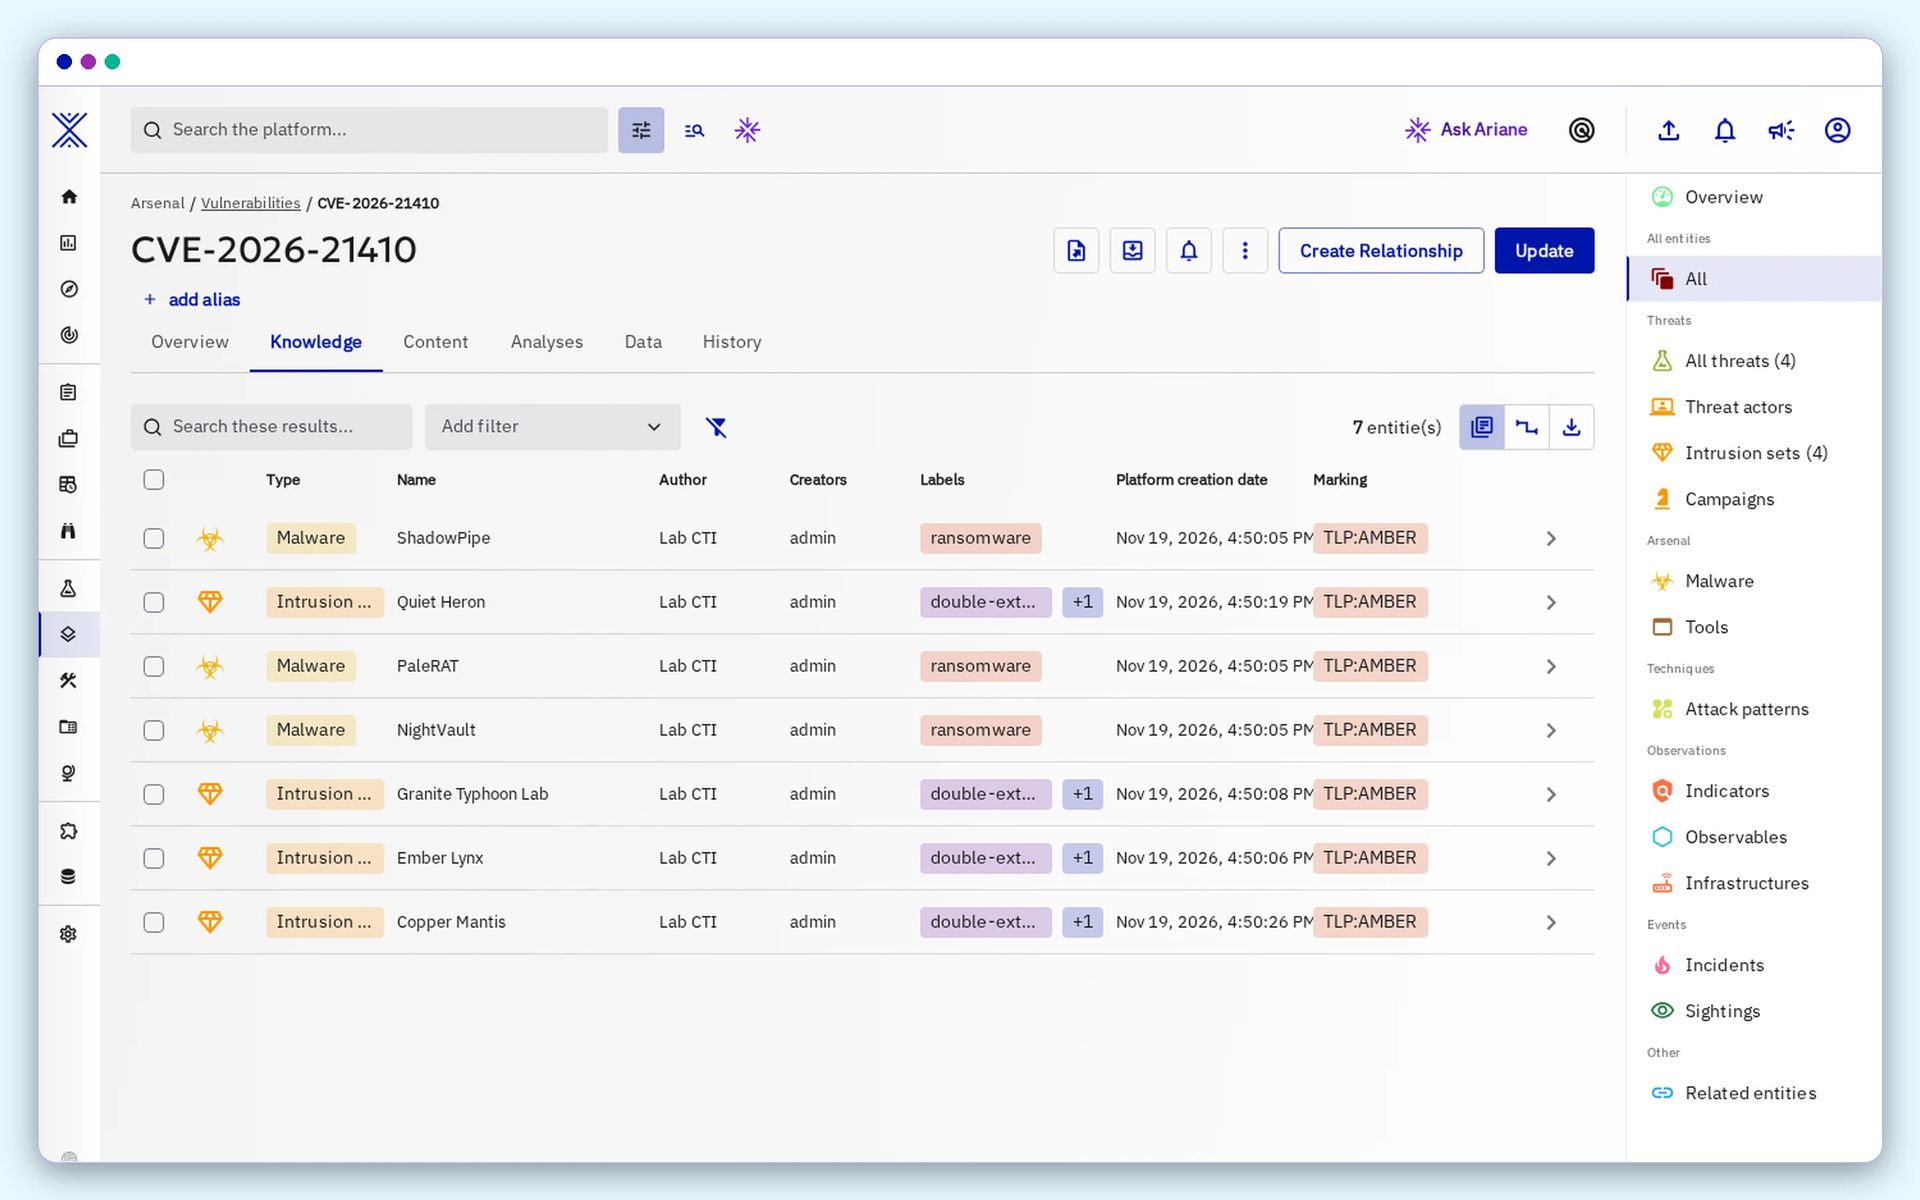
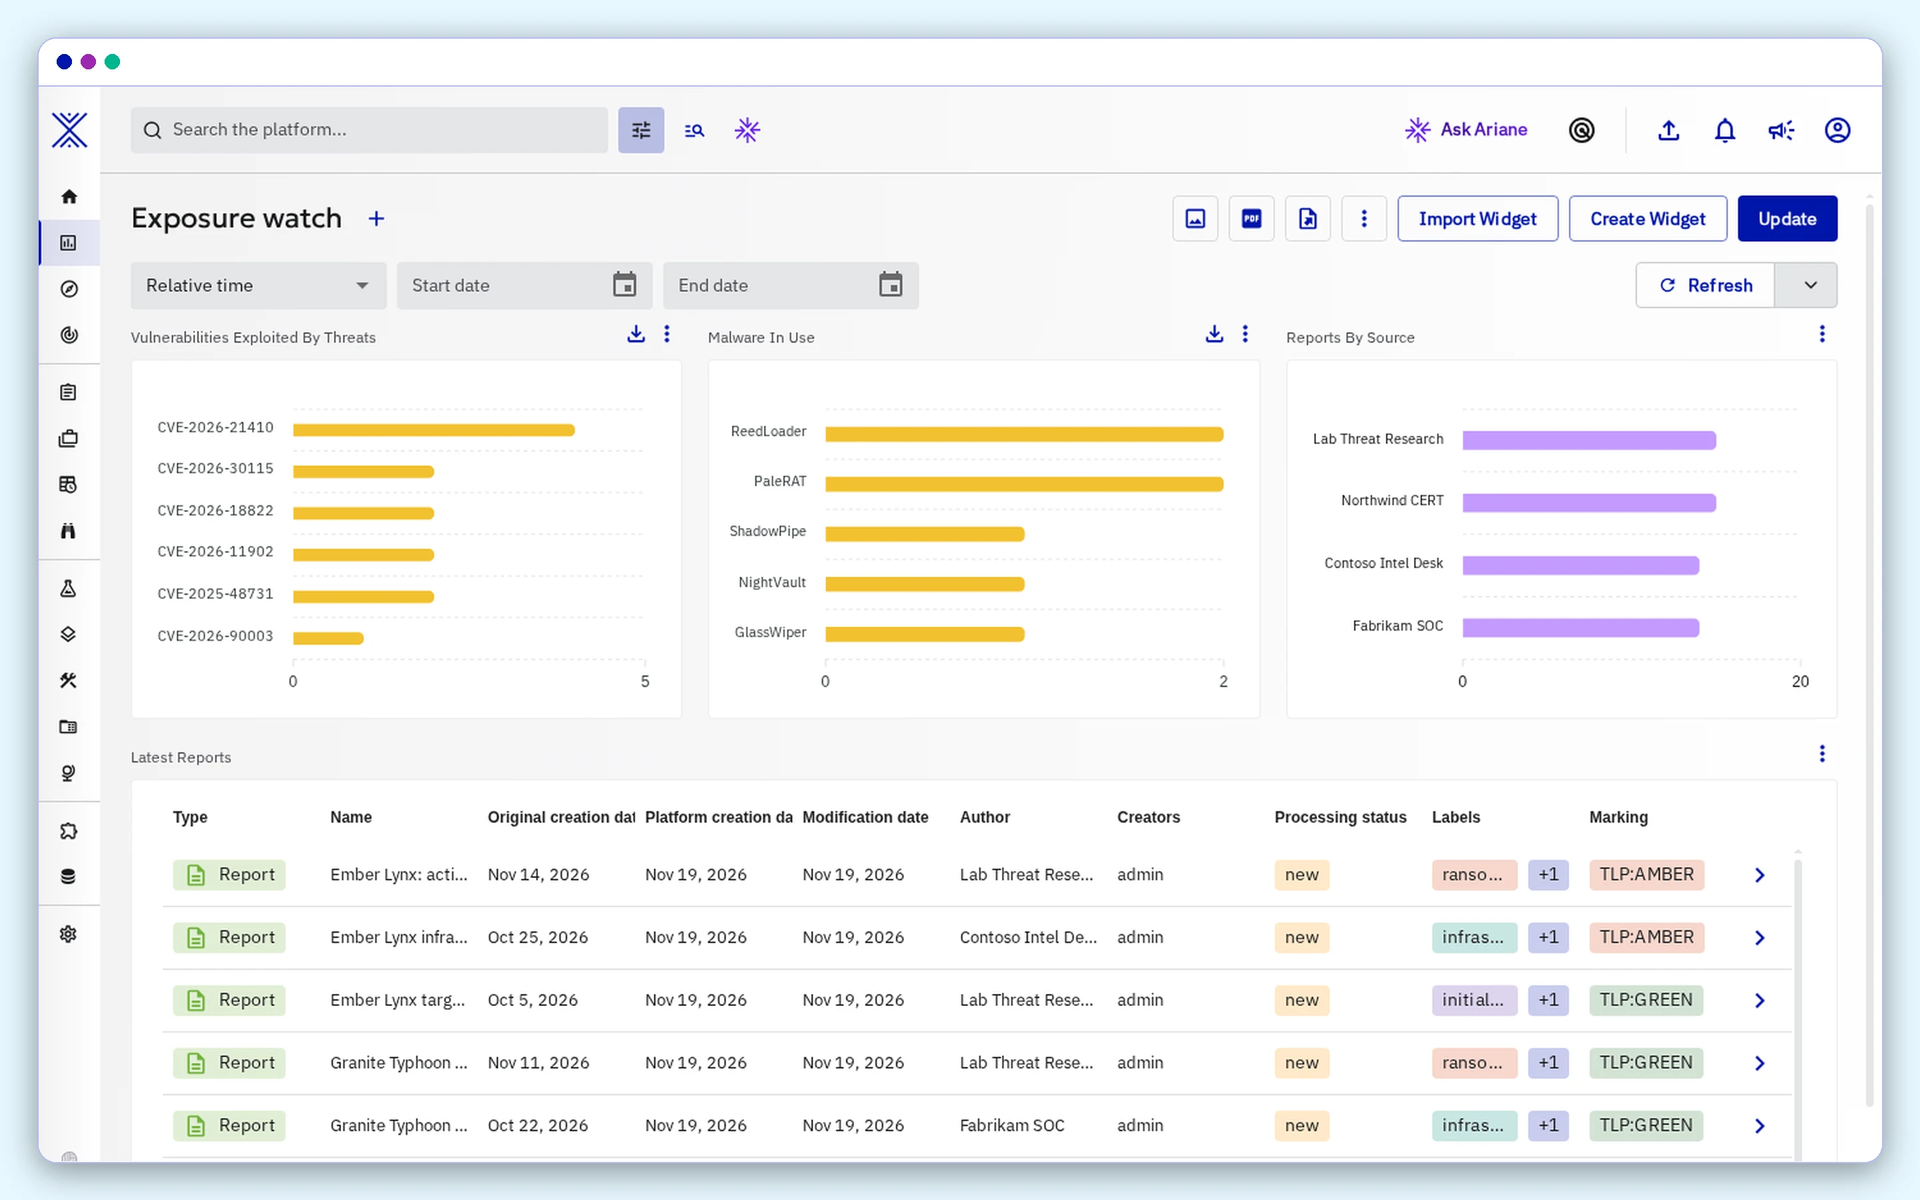
OpenCTI gives security teams one place to see which adversaries target their sector, how those groups operate, and which vulnerabilities they exploit. Reports, feeds, and analyst notes become linked STIX 2.1 entities such as intrusion sets, malware, ATT&CK techniques, vulnerabilities, and indicators, each carrying its source, confidence level, and TLP marking. Investigations start from a few entities and expand node by node, letting analysts pivot from an indicator to the campaign, malware family, and victim sector behind it. Threat pages show an ATT&CK matrix with the techniques in use highlighted, and custom dashboards chart any query as time series, distributions, or lists with one-click presets. Connectors import MITRE datasets, MISP, AlienVault, and CVE data, enrich observables through Shodan or DomainTools, and export STIX 2.1, CSV, or PDF files. TAXII collections, CSV feeds, and live streams publish selected knowledge to your SIEM or EDR, while RSS, CSV, JSON, and TAXII feeds pull outside intelligence in. Case management tracks incident responses, information requests, and takedown requests with assigned tasks and reusable task templates, and notification triggers alert analysts when watched entities change. A rules engine infers new relationships, decay rules age out stale indicators, and a GraphQL API with a Python client supports automation. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Benefits
- One graph for all threat intelligence
- Reports, indicators, actors, malware, and vulnerabilities share a single STIX 2.1 graph, so analysts follow relationships instead of searching spreadsheets, feed dashboards, and PDF folders one by one.
- Know which adversaries matter
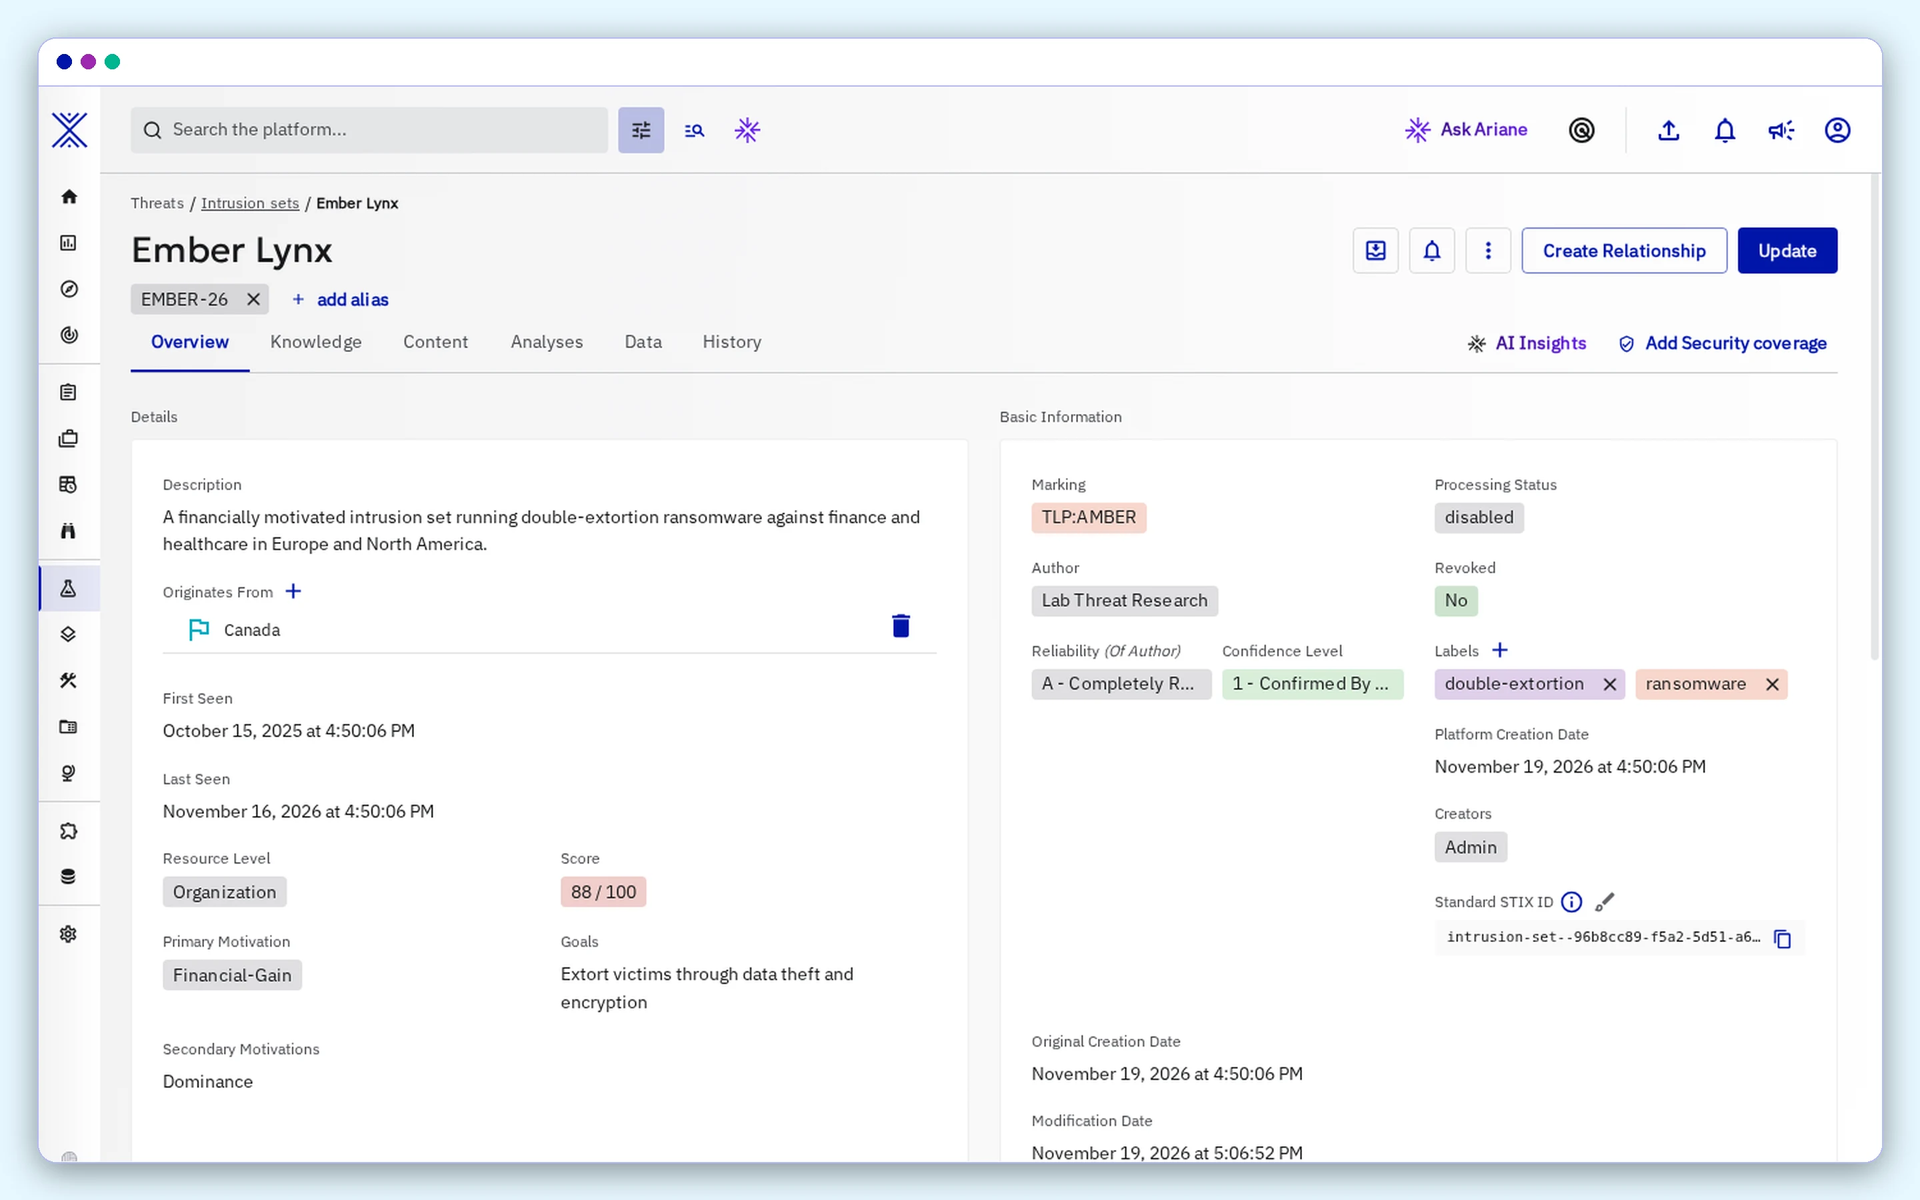
- Intrusion sets, targeted sectors, countries, and exploited vulnerabilities sit on each threat's page, so teams can judge which adversaries are relevant to their industry and which techniques to detect next.
- Feeds in, intelligence out
- Import connectors and TAXII, RSS, CSV, and JSON feeds fill the platform, while live streams, TAXII collections, and CSV feeds share curated indicators with your SIEM, EDR, or partner platforms.
- Sensitive intelligence stays under your control
- Incident notes and sector-specific intelligence stay on infrastructure you control, with TLP markings and per-user access levels on dashboards and investigations deciding who can view or edit what.
Features
- STIX 2.1 Knowledge Graph
- Threat actors, intrusion sets, campaigns, malware, tools, vulnerabilities, indicators, and observables are stored as STIX 2.1 objects and relationships with sources, confidence levels, and TLP markings.
- Investigations and ATT&CK Matrix
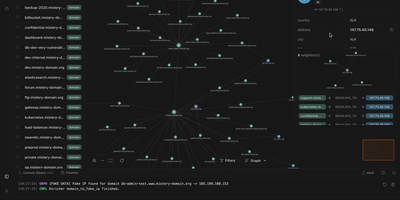
- Pivot and expand entities on an investigation graph, and open a MITRE ATT&CK matrix for any threat that highlights the techniques it uses.
- Custom Dashboards
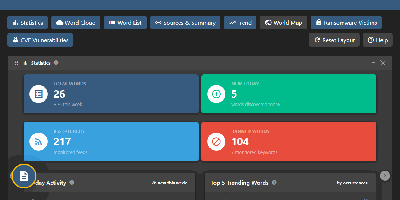
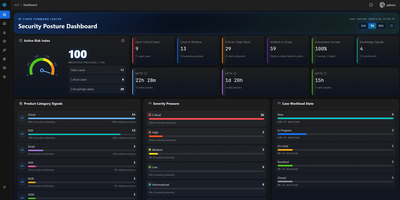
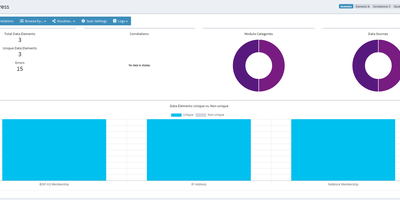
- Build dashboards from widgets such as counters, time series, distributions, and lists, set relative or fixed time ranges, and switch filters with variables and presets.
- Connectors and Feeds
- Import, enrichment, export, and stream connectors link MITRE datasets, MISP, Shodan, Splunk, and more, alongside TAXII, RSS, CSV, and JSON feeds and a GraphQL API.
- Case Management
- Handle incident responses, requests for information, and takedown requests as cases with assigned tasks, reusable task templates, notes, and the related entities and observables attached.
- Rules and Notifications
- A rules engine infers new relationships, decay rules age out indicators, and live or digest triggers notify users through chosen notifiers when watched events match their filters.