Supabase
With over 107,000 GitHub stars and adoption by teams at Mozilla, 1Password, Peerlist, and thousands of startups, Supabase has become the most widely deployed open-source Firebase alternative — built entirely on PostgreSQL rather than a proprietary NoSQL store. Every project provisions a dedicated Postgres database with 40+ preinstalled extensions, auto-generating REST APIs via PostgREST, GraphQL via pg_graphql, and real-time change streams via an Elixir-based WebSocket engine that supports database change listeners, user presence tracking, and arbitrary broadcast messaging. Authentication covers email and password, phone OTP, magic links, and 20+ social providers including Google, GitHub, Apple, Azure, and SAML SSO, all enforced through Postgres Row Level Security policies that run inside the database itself. S3-compatible object storage delivers files through a CDN spanning 285+ cities with on-the-fly image transformations powered by imgproxy. Edge Functions run globally distributed TypeScript on the Deno runtime with Node.js compatibility and access to over two million NPM packages. The pgvector extension stores, indexes, and queries vector embeddings for AI-powered semantic search and retrieval-augmented generation workflows. Supabase Studio provides a browser-based dashboard with a table editor, SQL editor, schema visualizer, and log explorer. Official client SDKs ship for JavaScript, Python, Flutter, Swift, Kotlin, C#, Go, and Ruby. The self-hosted Docker Compose stack runs fourteen coordinated services including Kong API gateway, Supavisor connection pooler, and Logflare analytics. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
OpenList
OpenList gathers every place your files live, local disks, S3 buckets, OneDrive, Google Drive, Dropbox, NAS shares, and forty-odd other services, into one browsable file list behind a single login. Mount each storage at its own path and the whole collection behaves like one tidy drive: documents open in the browser, whether PDF, Markdown, source code, or Office files, images get a gallery mode, and videos and audio play in place with subtitle and lyric support. Everyday file work happens in the same window: upload, delete, rename, move, and copy, including copying directly between two storages when you are migrating off a cloud plan. Offline download tasks let the server fetch links for you in the background, and multi-threaded acceleration squeezes speed out of sluggish single connections. Every folder can also be mounted as a real drive on your computer through the built-in WebDAV and FTP servers, with per-user permissions deciding who may read, upload, rename, or delete. Protected routes add passwords in front of sensitive shares, permalinks hand out direct download links, and granular user rules can hide files or open archive contents without extracting them. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Neon
Neon reimagines PostgreSQL with a serverless architecture that decouples storage from compute, enabling instant copy-on-write database branching, autoscaling under load, and scale-to-zero when idle with sub-second cold starts. The lakebase architecture distributes durability across three layers: stateless compute nodes running unmodified PostgreSQL, safekeepers providing Paxos-based WAL quorum replication, and a pageserver that materializes pages on demand while offloading immutable history to S3-compatible object storage via MinIO or AWS S3. Copy-on-write branching creates full database clones as metadata operations without duplicating data, enabling developers to spin up isolated test environments, run parallel CI/CD pipelines, or recover from data loss through point-in-time restore across the configurable history window. Autoscaling dynamically adjusts CPU and memory based on live traffic without manual capacity planning, while scale-to-zero ensures costs drop to storage-only during idle periods. Neon maintains 100% PostgreSQL compatibility with broad extension support including PostGIS, pg_cron, pgvector, pg_stat_statements, and hundreds more, so existing applications connect with standard PostgreSQL drivers and ORMs unchanged. The API-first control plane enables programmatic provisioning, branch management, and multi-tenant fleet operations for platform builders and AI agent integrations. Acquired by Databricks in May 2025 and backed by over 22,800 GitHub stars. Deploys via Docker Compose with pageserver, safekeepers, storage broker, and compute nodes backed by MinIO object storage. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Milvus
With over 45,000 GitHub stars and 100 million Docker pulls, Milvus is the most widely adopted open-source vector database, powering production AI systems at NVIDIA, Salesforce, eBay, Airbnb, and DoorDash. The distributed architecture separates compute and storage with stateless microservices on Kubernetes, horizontally scaling query nodes for read-heavy workloads and data nodes for write-heavy ingestion independently. Milvus 3.0 introduces lake-native retrieval that builds and serves indexes directly over vector data in object storage and open formats including Parquet, Lance, Iceberg, and Vortex without maintaining separate copies. Native hybrid search unifies lexical BM25 full-text retrieval and semantic vector search in a single engine with metadata filtering, eliminating the need for separate search infrastructure. Hardware-accelerated ANN indexing supports IVF, HNSW, DiskANN, and GPU-based indexes with BitQ 1-bit quantization cutting memory usage by 72 percent. SDKs for Python, Go, Node.js, and Java provide programmatic access, while Milvus Lite offers lightweight embedding for local development via pip install. Server-side aggregation, sorting, faceted search, StructArray for nested document structures, and ColBERT multi-vector scoring move ranking and result processing into the engine. The Path Index enables 100x faster JSON filtering with support for 100,000+ collections per cluster for multi-tenant deployments. Self-hosting deploys via Docker Standalone or Kubernetes with Helm charts using S3-compatible, GCS, or Azure Blob storage backends. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Mediary Scout
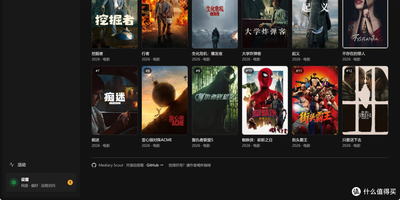
Mediary Scout puts an AI agent in charge of your cloud drive media library: name a movie, series, or anime and it finds a release, transfers it into your own drive, and checks that the files really arrived. Connect Quark, UC, 115, 123, GuangYaPan, and Tianyi, mostly with a QR code scan, and the agent probes live free space on every drive before each run, hard-blocking any that is full or over quota. It prefers a single drive that can cover every missing episode and combines drives only when none can, recording which drive holds each episode in one library. Search starts with the bundled PanSou for share links, optional Haisou and Prowlarr sources add more links and magnets, and transfers land in a staging folder first, where the agent inspects real file sizes, deletes ad files and lower-bitrate duplicates, then sorts episodes into Season folders. A daily patrol fills in missing episodes of tracked shows. Foreign titles that arrive without Chinese subtitles get matching .ass or .srt files from assrt.net, renamed to match the video. Unhappy with a file? Leave a plain-language note on the title, and the agent blacklists that source on every drive and fetches a replacement. A built-in HTTP API lets Claude Code, Codex, or OpenClaw queue titles and check progress, while multi-user mode gives family members separate accounts, drives, and libraries. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. 0BSD licensed.
Argo CD
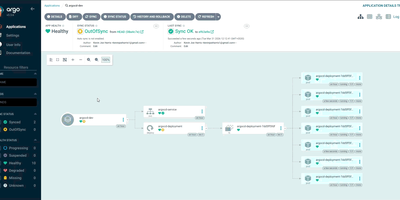
A CNCF Graduated project with over 23,700 GitHub stars and adoption by organizations including Intuit, Adobe, Capital One, and Red Hat, Argo CD has become the industry standard for GitOps-based Kubernetes deployments since its creation at Intuit in 2018, treating Git repositories as the single source of truth for application configurations and automatically reconciling live cluster state with declared desired state. The platform supports Helm charts including Helm 4, Kustomize overlays, Jsonnet, and plain Kubernetes YAML manifests, rendering templates and applying resources through configurable sync policies with automated or manual reconciliation, pruning of orphaned resources, and self-healing that reverts unauthorized cluster changes. ApplicationSets enable templated generation of applications across multiple clusters, environments, and Git repositories using generators for pull requests, Git directories, cluster lists, and merge strategies. The web UI provides a real-time application topology view with resource health status, sync state indicators, log streaming, and a network view supporting Gateway API and Ingress visualization. Version 3.5 introduced mTLS for internal component communication, graduated user impersonation and source hydrator to beta, added native ApplicationSet management with preview applications in the UI, and delivered source integrity validation. Multi-cluster management deploys applications across development, staging, and production environments from a single Argo CD instance with RBAC, SSO via OIDC and SAML, and audit logging. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Coder
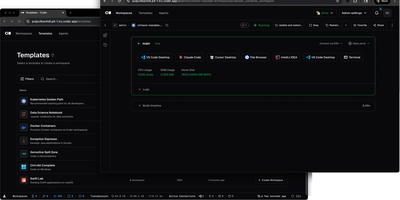
With over 14,000 GitHub stars and enterprise adoption by security-conscious organizations, Coder transforms how development teams provision, manage, and secure their coding environments. Every workspace is defined as a Terraform template, meaning infrastructure engineers can standardize development environments across EC2 instances, Kubernetes pods, Docker containers, or any combination, while developers get self-service provisioning that launches in seconds rather than days of manual setup. The WireGuard-based networking layer establishes encrypted tunnels between developer machines and remote workspaces, providing low-latency access without exposing ports or configuring VPN concentrators. Automatic idle detection shuts down unused workspaces after configurable periods, directly reducing cloud compute costs for organizations running hundreds of developer environments. The Coder Agents feature introduces native AI coding capabilities where the agent loop executes entirely within the control plane on self-hosted infrastructure, keeping LLM API credentials out of individual workspaces and eliminating credential exfiltration risks. Centralized model governance allows platform teams to approve specific AI providers and models, set per-user spend limits, and maintain complete audit logs of all prompts, tool calls, and agent activity. IDE integration supports VS Code through a dedicated extension, JetBrains IDEs via Gateway and Toolbox plugins, and browser-based code-server for web access. The template registry provides pre-built configurations for common development stacks. DevContainer support builds environments from standard devcontainer.json specifications. Deploy on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
FileGator
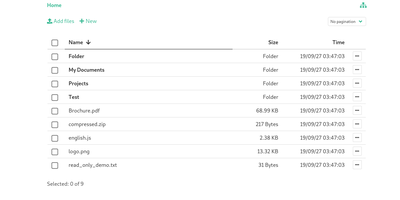
FileGator is a self-hosted, multi-user web file manager that gives your team a shared place to upload, organize, preview, and download files through the browser, with every person fenced into the folders they are allowed to touch. Create accounts for colleagues, students, or clients and give each one a home folder plus permissions that decide what they can read, write, rename, or delete. Everyone gets the full file toolkit: copy, move, rename, edit, create, delete, and preview, plus zip and unzip for bundling archives on the server. Select several files or folders and download them together, or zip a remote directory and pull it down in a single transfer. Uploads accept drag and drop with a live progress bar, and chunked transfers pause and resume, so a multi-gigabyte video survives an unstable connection. Point FileGator at a plain folder on the server disk or connect an Amazon S3 bucket as the storage adapter behind the same interface. Teachers collect assignments through it, field teams drop photos and documents from the road, and families share one photo archive without anyone installing an FTP client. Admins manage users, roles, and permissions from one panel, and the application runs on ordinary PHP hosting you already know how to operate. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
9Drive
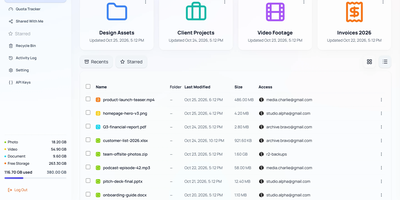
Four half-full cloud accounts become one big drive with a single search bar. Connect Google Drive accounts and S3-compatible buckets like Cloudflare R2, MinIO, Wasabi, or Backblaze B2, and the Quota Tracker shows total, used, and available space across all of them. Upload routing picks the destination by most free space, round-robin, or a custom priority order, and files stream straight through to storage without touching the server disk. The file manager offers nested virtual folders with custom colors and icons, list and grid views, filters for type, account, size, and date, previews for images, videos, PDFs, and Office files, a recycle bin, and a starred list. Public links open a built-in viewer with an embed mode, and invitations give other people viewer or editor access to a file or folder, tracked on a Shared page. An activity log records uploads, shares, and changes, and API keys with upload-only scope let scripts and CI jobs push files through a documented endpoint. Dark mode and a phone-friendly layout that installs as a PWA come built in. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Olares
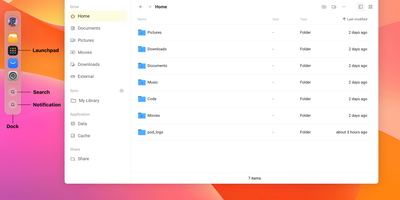
Your own hardware should be the cloud your AI lives in. Olares is an open-source personal cloud operating system that turns one machine, or a small cluster of them, into a private AI platform: run local large language models, keep always-on agents working on your files, and open a browser-based desktop of apps from any device. The built-in Lares assistant takes instructions in plain language and delegates research, file management, and routine automation to agents. The Model Console downloads and serves open models from a local catalog, with GPUs pooled across nodes and split by time or memory for AI, media, and gaming workloads. A one-click market installs self-hosted applications beside the system apps: Files browsing local folders, synced data, cloud storage, and SMB or NFS shares; Vault managing secrets; Dashboard watching the machine; and Control Hub administering it all. Networking stays private by design, with a built-in VPN, reverse proxy, and public, private, or internal entrances giving each app an HTTPS address without exposing individual ports. Backups protect the whole system, the desktop works from phone or browser anywhere, and your apps, storage, and accelerators behave like one coherent computer rather than a pile of containers. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Harbor
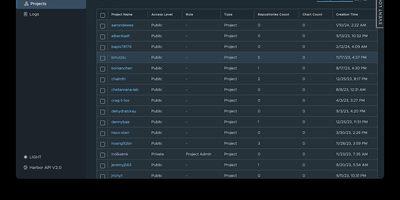
The first container registry to reach CNCF graduated status with over 29,000 GitHub stars since VMware open-sourced it in 2016, Harbor transforms the basic Docker Distribution into a hardened enterprise registry with vulnerability scanning, supply chain signing, multi-datacenter replication, and project-level access control out of the box. Trivy scans every pushed image against the NVD, GitHub Advisory Database, and distribution-specific vulnerability feeds, with scan-on-push policies that block deployment of images exceeding configurable severity thresholds. Artifact signing through Cosign keyless signatures and Notation enforces content trust policies ensuring only cryptographically verified images reach production clusters. Policy-based replication synchronizes images and Helm charts between Harbor instances across multiple datacenters using repository, tag, and label filters with automatic retry and bandwidth throttling — enabling hybrid-cloud and disaster-recovery topologies. The RBAC model isolates projects with per-project quotas, robot accounts for CI/CD automation, webhook notifications, and audit logging that tracks every pull, push, delete, and configuration change. LDAP, Active Directory, and OIDC authentication integrate with existing identity providers, while the proxy cache transparently caches images from Docker Hub, Quay, and other upstream registries to reduce pull latency and rate-limit exposure. The RESTful API with embedded Swagger UI, tag retention policies, garbage collection scheduling, and immutable artifact rules complete the lifecycle management. Deploy via Docker Compose or Helm Chart on Kubernetes. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
Higress
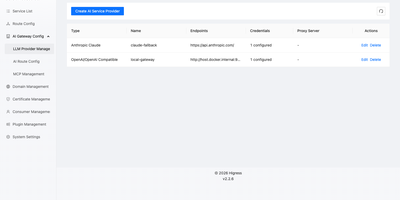
Send every AI request through one gateway that holds your model providers, API keys, and access rules. The web console starts with a first-run admin setup, then an LLM Provider page where OpenAI-compatible endpoints, Anthropic Claude, Azure OpenAI, Tongyi Qianwen, Moonshot, Zhipu, and other services are added with their tokens. AI Route Config maps path prefixes and model match rules to weighted target services, with token failover and first-packet timeouts to keep traffic moving when a key fails. Consumer Management issues key, OAuth2, and JWT credentials, and each route can limit access to named consumers. Plugin Management lists ready-made AI plugins for caching, context limits, data masking, prompt templates, prompt decorators, load balancing, and intent checks, plus traffic and security plugins that can be configured per route. MCP Management hosts MCP servers behind the same authentication and rate limits so agents call tools through one governed address. Service Sources import backends from Nacos, Zookeeper, Consul, Eureka, static addresses, or domains, and domain and certificate pages handle HTTPS, including free automatic certificates from Let's Encrypt. An LLM proxy for a product team, a shared model endpoint for several agents, or a replacement for an ingress controller all fit this console. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
CockroachDB
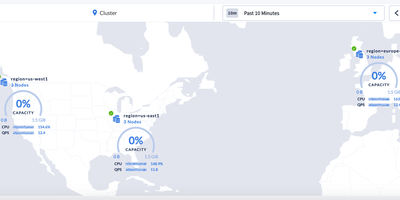
With over 32,000 GitHub stars and adoption by DoorDash, Netflix, and Bose, CockroachDB is the distributed SQL database designed to survive disk failures, machine outages, rack losses, and entire datacenter failures while maintaining strongly-consistent ACID transactions with serializable isolation by default. The architecture layers SQL on a transactional key-value store using the Raft consensus protocol for synchronous replication, automatically splitting data into ranges that distribute and rebalance without manual sharding. PostgreSQL wire protocol compatibility means existing drivers, ORMs, and tools including psycopg2, pgx, ActiveRecord, Django ORM, GORM, Hibernate, and Prisma work without modification. Multi-region capabilities include configurable survival goals at region or zone level, table-level locality settings for pinning data to specific geographies for GDPR compliance, and follower reads for low-latency global queries. The built-in DB Console provides cluster overview dashboards, node maps showing geographical distribution, SQL activity pages tracking statement fingerprints, transaction latency percentiles, session details, and real-time metrics for queries per second, storage capacity, and replication status. Change data capture streams row-level changes to Apache Kafka, Google Cloud Pub/Sub, or webhook endpoints for event-driven architectures. Online schema changes execute ALTER TABLE without locking or downtime, and distributed backup supports full and incremental snapshots to S3, GCS, Azure Blob, and NFS. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. CockroachDB Software License (source-available).
Puter
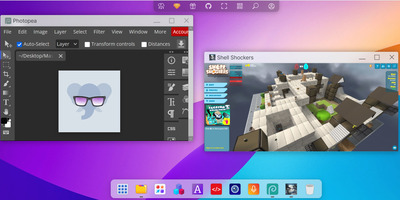
Puter delivers a complete cloud operating system that runs entirely in the browser — turning any device with internet access into a full-featured personal computer with desktop environment, file management, application hosting, and developer platform. The familiar desktop interface presents windows, taskbar, right-click menus, drag-and-drop, and multi-window management indistinguishable from native operating systems. The hierarchical filesystem supports file creation, uploads, sharing, permissions, and trash recovery with storage backends ranging from local SQLite for self-hosting to S3 and DynamoDB for production scale. Built-in AI integration provides access to GPT-4, Claude, and other models directly from the desktop for text generation, code assistance, and image creation. The developer platform offers a JavaScript SDK, REST APIs, cloud storage, key-value database, and serverless workers for building and hosting web applications without managing infrastructure. Sandboxed applications run in iframes with IPC communication and permission-based access to filesystem, AI, and system services. The app store enables publishing, discovering, and monetizing applications built on the Puter platform. Website hosting publishes static sites with custom domains directly from the file manager. Multi-user support provides individual accounts with authentication, resource isolation, and sharing capabilities. Deploy via Docker with a single command, Docker Compose for production, or npm for development — the one-line install script handles everything automatically on Linux, macOS, and Windows. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Filestash
Filestash puts a Dropbox-style web interface in front of the SFTP servers, S3 buckets, SMB shares, and WebDAV storage you already run, so no file has to move. Administrators enable each connector, including FTP, NFS, Git, Dropbox, Google Drive, Storj, IPFS, and Backblaze B2, from one admin console. Colleagues browse, rename, move, and upload in a single folder view, with resumable uploads for big transfers. Thumbnails cover JPEG, PNG, WebP, TIFF, HEIF, and RAW photos. Images open with an EXIF info panel, and PDFs, audio, video, and EPUB ebooks open right in the browser. A CodeMirror editor handles text and code, and HLS transcoding streams video on demand. Outside guests get a shared link instead of credentials, with an optional password, an expiry date, and read, write, or upload-only rights. Limit a link to one email address or a whole domain, or mount it as a network drive. A workflow engine chains emails and HTTP calls after file events, webhooks, or schedules. Flip one admin setting and Claude, ChatGPT, and Mistral Le Chat can use the connected storage as MCP tools. Downloadable file apps add Office documents, 3D models, and GIS maps. Runtime plugins are zip files dropped into the plugins folder. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.

CubeSandbox
CubeSandbox gives every AI agent its own hardware-isolated MicroVM with a dedicated Linux kernel — not a shared-kernel container but a true KVM virtual machine — booting in under 60ms with less than 5MB of memory overhead per instance, enabling thousands of concurrent sandboxes on a single server via kernel sharing and Copy-on-Write memory. The Rust-built CubeProxy exposes an E2B SDK-compatible REST API on Axum, so existing E2B Cloud applications switch by changing one environment variable with zero client code changes. CubeMaster orchestrates cluster-level scheduling in Go while Cubelet manages node-local sandbox lifecycles including create, run, pause, resume, snapshot, and destroy operations. CubeVS, the eBPF-powered network layer, enforces per-sandbox isolation with LPM trie-based egress policies entirely in kernel space — no userspace context switches — while CubeEgress provides an L7 security proxy with per-domain, per-path, and per-method allowlists plus automatic credential injection that keeps secrets invisible to sandbox code. Hundred-millisecond-granularity snapshots enable checkpoint, rollback, and parallel fork from any saved state. The volume framework supports E2B-compatible pluggable storage with independent lifecycle and cross-sandbox sharing. Production deployment uses Terraform on Tencent Cloud or Helm charts on Kubernetes, K3s, or TKE, with full ARM64 support alongside x86_64 and AutoPause/AutoResume for cost optimization. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.
QVMConsole
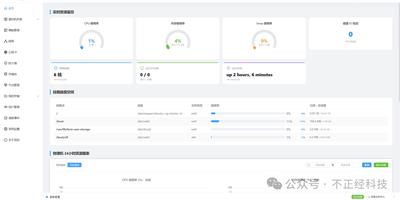
QVMConsole turns a KVM host into a small private cloud where tenants create, clone, snapshot, and console into their own virtual machines from one web panel without ever touching the hypervisor. Create machines from templates, linked clones, or ISO images across x86_64 and ARM hosts with BIOS or UEFI firmware, multiple disks, and multiple network cards, then manage power, reinstalls, imports, and exports from the same console. Each tenant receives an isolated VPC built on Open vSwitch with its own logical switch, VLAN, DHCP, NAT, and access control, plus cloud-style security groups, port forwarding with health checks, bandwidth limits, and monthly traffic quotas. Storage pools span host disks and LVM volumes, VM disks migrate between pools online, and snapshots carry their own quotas with restore and UEFI safeguards. Open any machine in the browser through the noVNC console, complete with shortcut keys and one-click password paste, and follow long operations in an asynchronous task center that streams progress live. Administrators enforce two-factor authentication, confirm sensitive actions a second time, and cap every tenant by CPU, memory, disk, VM count, public IPs, and runtime hours through fine-grained quotas or a lightweight cloud mode. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Kite
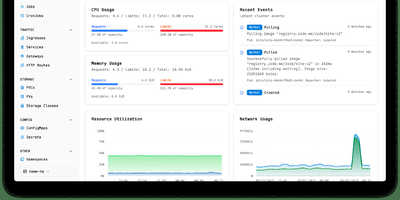
With nearly 3,000 GitHub stars and 14 releases since its June 2025 launch, Kite delivers a lightweight Kubernetes dashboard that replaces the fragmented workflow of switching between kubectl, Lens, and separate monitoring tools with a unified multi-cluster management platform. The dashboard automatically discovers clusters from kubeconfig files and supports independent Prometheus configurations per cluster, providing real-time CPU, memory, and network charts alongside live pod log streaming with filtering and search. A built-in web terminal opens shells directly into pods and nodes without kubectl port-forward, while the Monaco-based YAML editor offers syntax highlighting and validation for in-place resource editing. The integrated AI agent, powered by OpenAI or Anthropic models via native Go SDK integrations, translates natural language into precise client-go API calls — querying cluster health, analyzing pod logs, scaling deployments, patching resources, and cleaning up failed jobs — all operating strictly within the logged-in user's RBAC permissions. Enterprise governance includes OAuth 2.0 single sign-on, multi-factor authentication, FIDO2 passkeys, granular role-based access control with per-namespace permissions, and comprehensive audit logging. Helm chart management enables browsing, installing, and upgrading releases directly from the UI, while the Docker registry integration provides quick image tag selection. Deploy via a single Docker container with SQLite or use the official OCI Helm chart with PostgreSQL or MySQL for production. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache 2.0 licensed.