CrowdSec Web UI
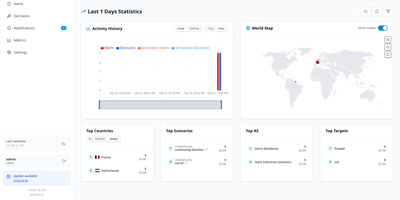
CrowdSec Web UI provides a centralized web console for monitoring intrusion detection telemetry, managing firewall remediation decisions, and auditing security events across multiple CrowdSec security engines. Administrators can connect several CrowdSec Local API endpoints simultaneously, aggregating threat intelligence and active bans into a unified visual interface. The dashboard displays geographic origins of attacking IP addresses, active remediation durations, and specific scenario triggers such as brute-force authentication attacks or web vulnerability probes. Operators can search through historical alert logs, inspect raw HTTP request details, and drill down into individual IP behaviors to differentiate authentic threats from false positives. Manual intervention tools let security teams enforce custom IP bans, adjust expiration timers, or immediately revoke erroneous bans across all connected bouncers with a single click. Integrated notification pipelines dispatch real-time security alerts to external destinations including ntfy, Gotify, and MQTT message brokers whenever critical thresholds are breached. Built-in Prometheus metrics dashboards visualize processing latencies, parser throughput, and decision counts over customizable time windows. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.
Fail2Ban UI
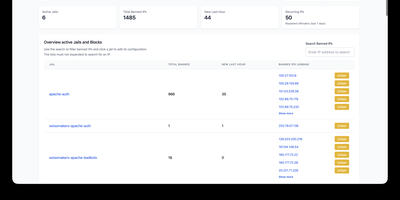
Manage Fail2Ban on every Linux server from one browser dashboard instead of logging into each host to check jails and unban addresses. The dashboard lists active jails and banned IPs and updates live as bans and unbans arrive, while one search box finds an address across every jail of every server so you can unban it in the right place. Servers connect through a local socket, key-based SSH, or a lightweight HTTP agent, and each one shows Healthy, Degraded, or Down status. Jails and filters are edited in the browser, with log path tests, a regex debugger that runs sample log lines through a filter, and a configuration check before Fail2Ban reloads. Ban Insights draws a zoomable ban and unban timeline, compares two incidents to expose repeat attackers, exports IP lists as CSV or JSON, and maps countries on an interactive 3D globe. Recurring offenders can be blocked permanently on MikroTik, pfSense, OPNsense, or UniFi Network firewalls. Alerts go out by email, webhook for ntfy, Slack, Mattermost, or Telegram, or Elasticsearch, filtered by country, and clicking any IP opens AbuseIPDB or AlienVault OTX reports. Sign-in works through Keycloak, Authentik, Pocket ID, or any OIDC provider, and the interface speaks nine languages. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. AGPL-3.0 licensed.