Argus Agentic SOC
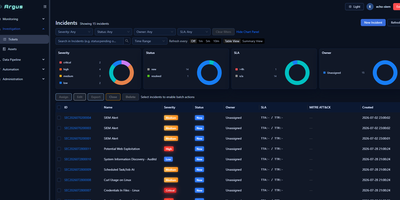
Every incident ticket in Argus, an open-source security operations center, comes with its own AI analyst, ready to explain the alert and suggest what to do next. Scheduled pipeline tasks pull alerts in from Elasticsearch and other sources, and tickets carry severity, owner, and SLA clocks that measure MTTA, MTTI, MTTC, and MTTR with color-coded buckets. Decision buttons walk each case from New through Acknowledged, Triaged, and Contained to Resolved. A War Room gathers analyst notes, system logs, files, pasted images, and extracted indicators. One click on Run AI Assistant returns a plain-language alert explanation, a suggested risk level, finished tasks, and next steps; scoped chat plus @ai and @playbook mentions keep the conversation inside the ticket. Built-in MCP tools look up CMDB assets, find similar past cases, and extract IPs, domains, and hashes, and you can register your own MCP servers and SKILL.md skills with usage monitors. A drag-and-drop workflow editor fires playbooks on new alerts, ticket changes, cron schedules, or webhooks. Detection engineers import Sigma rules from GitHub URLs or files, map fields to Splunk and Elastic ECS names, and review a publish history. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Deploy