OpenAEV
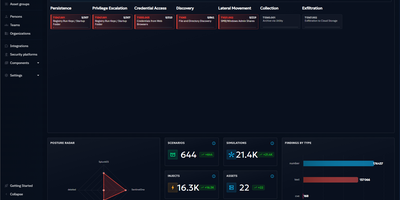
Before an attacker tests your defenses, OpenAEV lets you replay their techniques and see which ones your EDR, SIEM, and people actually catch. Scenarios sequence injects that mirror a threat actor's behavior, and simulations run them once or on a schedule against chosen endpoints, scoring prevention, detection, vulnerability, and human response. Atomic tests fire a single ATT&CK technique from the Threat Arsenal, such as an Nmap scan or a Nuclei CVE scan, and can repeat hourly, daily, weekly, or monthly. A lightweight agent for Windows, Linux, and macOS enrolls each endpoint for testing, while asset groups organize targets by filter. Collectors match EDR, XDR, and SIEM alerts to each inject, marking it prevented or detected, or missed when the expectation window expires. Findings collect scan results and CVE data for each asset, custom dashboards chart posture over time, and scheduled PDF or HTML reports reach stakeholders without platform access. Exercises can also target people through phishing campaigns with landing pages and email templates, SMS, media pressure articles, challenges, and post-run lesson surveys. Pre-built scenarios import from the XTM Hub, or OpenAEV can generate them from OpenCTI security coverage, and a REST API supports automation. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. Apache-2.0 licensed.
Deploy