Stars
Forks
Watchers
Developer links
sish
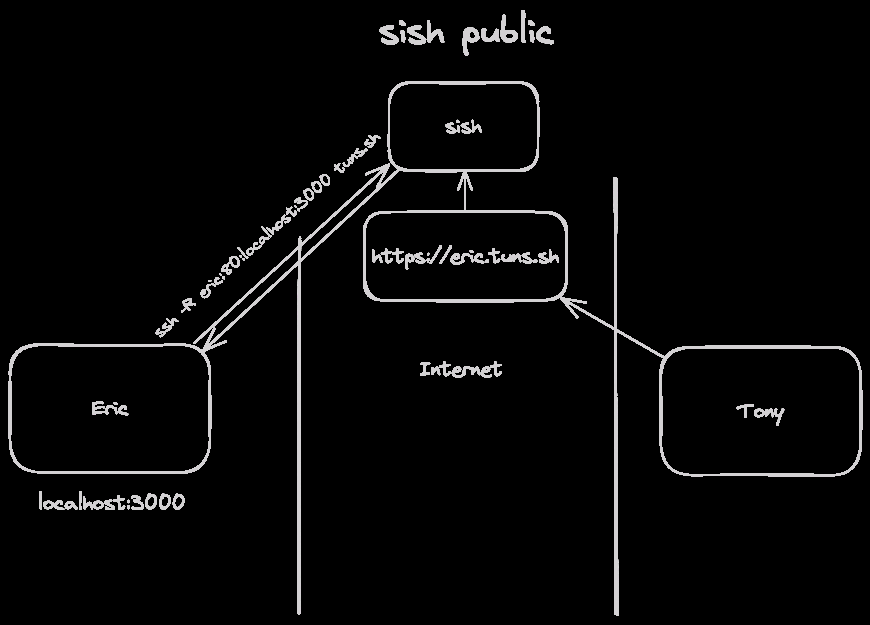
Private machines hide their services behind routers and firewalls; sish gives those services a public address, reached with nothing more exotic than the SSH client already on your laptop. Point a standard remote forward at the server and a local web app appears at its own subdomain over HTTPS, ready to share with testers, clients, or a webhook provider. Raw TCP forwards work the same way, publishing a database, a game server, or an SSH port on a fixed external port you choose. Private aliases keep sensitive services off the public internet entirely, reachable only through an authenticated SSH jump from another machine you control. SNI routing passes encrypted TLS connections to the right backend by hostname, so several services share one public endpoint without the tunnel terminating their encryption. Aliases can spread traffic across multiple backends with built-in load balancing modes, handy when several replicas sit behind one name. The service console lists live tunnels and inspects forwarded requests as they pass, turning tunnel debugging into reading a log instead of guessing. Access rests on SSH keys or passwords with hot-reloaded key directories, and binding policies cap which subdomains and ports each user may claim. Because clients need no agent software, locked-down laptops, CI runners, and embedded devices can open tunnels with the tools already installed. Running on a dedicated VPS on RepoCloud with guaranteed CPU, RAM, and SSD, full root SSH access, and a browser serial console. MIT licensed.
Benefits
- No Client To Install
- Every tunnel opens with the OpenSSH client shipped on macOS, Linux, and Windows. Teammates, CI systems, and appliances point a remote forward at your server and publish a service, with zero agents to distribute.
- Private Aliases Stay Hidden
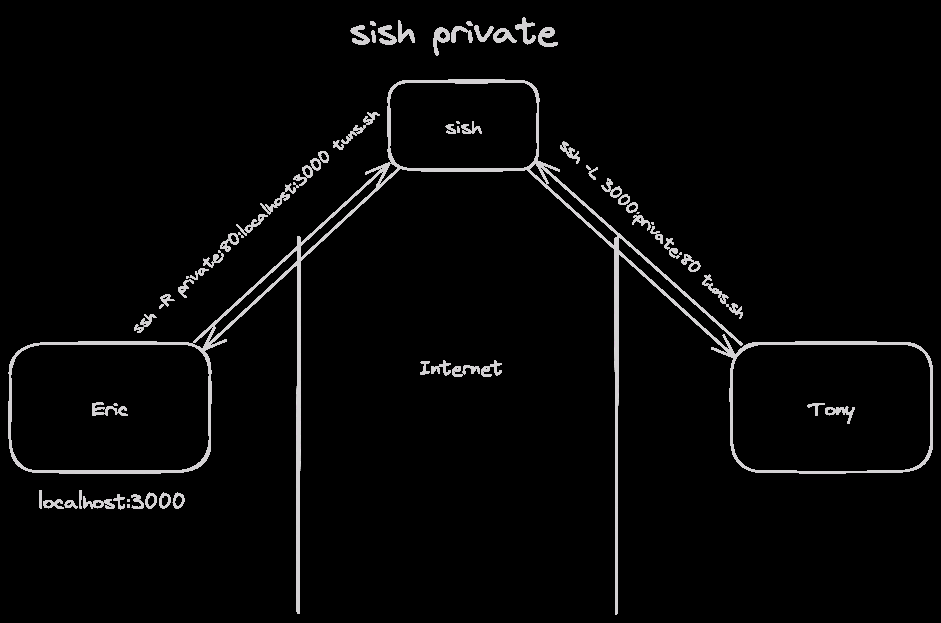
- Aliases expose a laptop or internal service only to clients who arrive through an authenticated SSH connection. The service never appears on a public port, so scans and strangers find nothing listening at all.
- One Endpoint Many Services
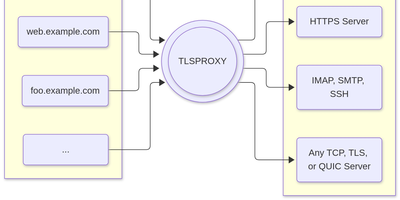
- SNI routing reads the hostname inside encrypted TLS handshakes and forwards each connection untouched to its backend. Many services share a single public address, and certificates stay under each backend's own control end to end.
- Console Shows Live Requests
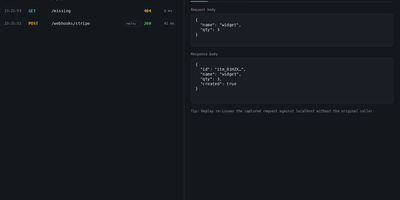
- The service console displays connected tunnels and the requests moving through them in real time. Watching an actual webhook arrive beats adding print statements and redeploying the receiver for every debugging round.
Features
- HTTP And TCP Forwarding
- Remote SSH forwards publish local HTTP, HTTPS, WebSocket, and raw TCP services at subdomains or external ports on the server, with random or fixed assignment.
- SNI TLS Routing
- The proxy inspects the Server Name Indication inside TLS handshakes and routes encrypted connections to matching backends without decrypting traffic at the tunnel layer.
- Private TCP Aliases
- Named aliases forward ports between authenticated clients through the server, so a database or SSH service stays reachable to teammates and invisible to the internet.
- Alias Load Balancing
- HTTP, TCP, and SNI aliases accept multiple backends and distribute new connections across them with selectable balancing modes for simple replicated services behind one name.
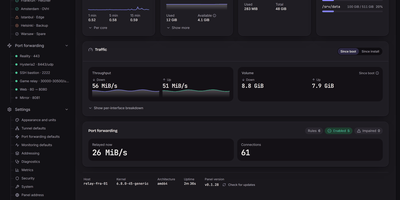
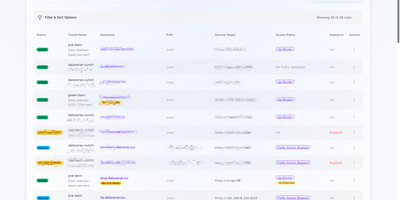
- Service Console Inspection
- A built-in console enumerates active tunnels and shows requests as they are forwarded, giving operators a live view of who is connected and what traffic flows.